A round-up of today’s digital forensics news and views:
Forensic Focus News
Semantics 21 Is Calling Time on Outdated Investigation Tools
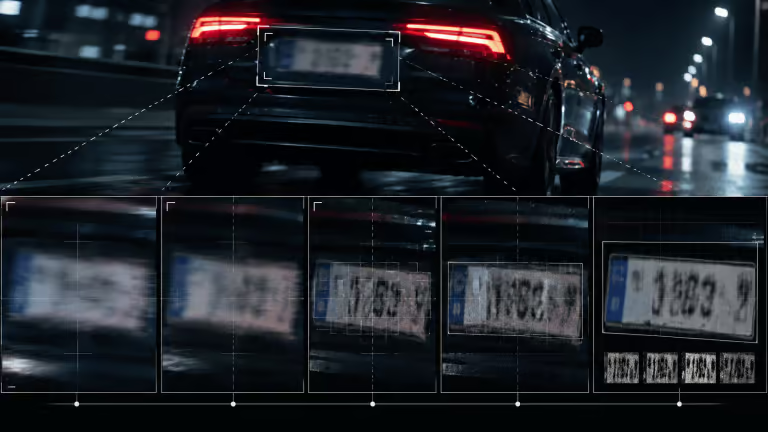
Digital evidence volumes have grown beyond the capacity of many legacy investigative tools, leaving analysts to compensate manually for limited visibility and fragmented workflows. Semantics 21 offers three connected tools, S21 VisionX for image and video analysis, S21 CCTV for time-critical footage review, and S21 Transcriber for converting spoken audio into searchable text, all designed to keep investigative judgement with trained professionals.
Research & Techniques
eBPF Rootkits Evade Linux EDR Sensor Visibility
eBPF-based rootkits such as LinkPro and VoidLink operate at the same kernel privilege level as EDR sensors, allowing them to suppress event visibility and actively detect analysis tools like bpftool and strace. Because live-host commands become unreliable under these conditions, acquiring a memory image before any reboot remains the most forensically sound method for identifying what the kernel actually loaded.
Tools & Software
Chainsaw v2.17.1 Fixes Sigma Translation Bugs
Chainsaw v2.17.1 is out, patching invalid rules, correcting Sigma regex translation errors, and fixing the lint command exit code. The release also adds initial support for Sigma’s windash modifier, expanding detection coverage for Windows event log analysis.
GLEAPP Triages Large Forensic Photo Datasets
GLEAPP is a forensic tool designed to organize and analyze large photo and media datasets, sorting images by categories such as faces, geolocation data, and known bad hashes. It generates detailed reports on image metadata and features identified during analysis, making it practical for examiners handling high-volume media collections.
Read more (matthewplascencia.substack.com)
Legal & Policy
Pegasus Lacked Full Operator Control, Experts Find
Polish internal security agency ABW experts found that Pegasus spyware could silently harvest SMS, email, VoIP calls, GPS data, and live audio/video from Android and iOS devices. CBA, the agency operating the system, lacked administrative credentials for key components, and intercepted data was routed through an anonymising server network outside Poland controlled by NSO Group. Experts confirmed the vendor had technical capability to access operational surveillance material during remote support sessions.
Training & Events
LOLBins Talk Targets Malware-Free Attack Forensics
Attackers abuse trusted Windows binaries like MSHTA, rundll32, and svchost to execute malicious activity without dropping traditional malware, complicating detection. Forensic differentiation relies on process ancestry, command-line arguments, execution context, and Windows artifact analysis rather than file-based indicators.
Industry News
Cuyahoga County Prosecutor Hiring ICAC Forensic Examiner
The Cuyahoga County Prosecutor’s Office is recruiting a Special Investigator and Forensic Examiner for its Internet Crimes Against Children Task Force unit in Cleveland, OH. Candidates with a background in computer forensics investigations are encouraged to apply directly through the office’s online portal.