This Week on Forensic Focus
From Hours To Minutes: Accelerating Digital Investigations With Detego Global In The City Of Johannesburg
Discover how the City of Johannesburg is using Detego’s digital forensics technology to accelerate evidence discovery, examine more devices, and streamline investigations without returning to the lab.
MD-LIVE: Mobile Forensic Triage Solution, From First Connection To Final Report
See how MD-LIVE takes investigators from first connection to a court-ready report at the scene, with Block Hash Scan, Auto Scroll Capture…
Analyzing Driver Behavior Using Vehicle Data
Can vehicle data reveal the difference between normal and reckless driving? Discover how iVe uses velocity logs, hard braking, and acceleration events…
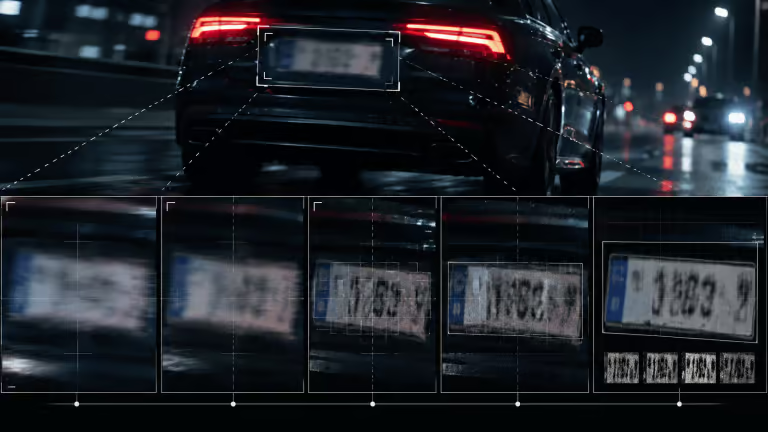
Beyond Blur: Decision-Making In Complex Licence Plate Examination And Enhancement Casework
Guocai Wang explores why “blurred” is not a diagnosis in forensic licence-plate analysis, and why the processing strategy should follow the material…
Magnet Autokey: Accelerating Your Vehicle Investigations
Jason Miranda and Evan Walker from Magnet Forensics show how Magnet Autokey pulls location history, connected devices and even text messages from…
Elsewhere in DFIR
- 1
VESTIGEX Beta Launches as Free DFIR Platform
VESTIGEX is a new free Windows desktop platform for digital forensics and incident response, supporting disk image formats (E01, raw, VHDX, VMDK, DMG), KAPE collections, memory forensics via Volatility 3, and mobile acquisition over ADB and iPhone encrypted backups. Artifact analysis spans Windows, macOS, Linux and mobile sources, with a unified super-timeline, 2,400+ Sigma rules mapped to MITRE ATT&CK, and a local AI assistant powered by Ollama that keeps all evidence on-device. Currently in beta (v1.1.1), the tool generates hash-chained audit logs and chain-of-custody reports in HTML, PDF, Word and Excel. Read more (vestigex.app)
- 2
Open-Source Tools Extract Files from NTFS Disk Images
Two open-source command-line tools, ntfsfind and ntfsdump, allow DFIR practitioners to search and extract files directly from Windows disk images without mounting them. Built on direct MFT parsing, ntfsfind supports regex path search with metadata filters including timestamps, file attributes, deleted entries, and ADS records, while ntfsdump recreates directory structures from dd, E01, VHD, VHDX, and VMDK formats including VMware snapshot chains and Hyper-V differencing disks. Read more (sumeshi.github.io)
- 3
VLEAPP Doubles Artifacts, Major LEAPP Updates
VLEAPP has grown from 103 to 202 artifacts on its main branch, adding support for Ford SYNC, GM OnStar, GM Bosch HMI, Nissan 08IT, BMW MGU, and SiriusXM infotainment systems. Companion tools DLEAPP, iLEAPP, and ALEAPP received 65, 11, and 9 new artifacts respectively, and raw images can now surface free space and deleted flash files as artifacts. Read more (leapps.org)
- 4
DFRWS Report: Making AI Defensible in Casework
DFRWS has published practitioner perspectives from its 2026 Americas conference on responsible AI use in digital forensics casework, covering performance evaluation, appropriate use, and engineering guardrails. Panelists stressed that AI outputs must be auditable and traceable to source data, treating AI tools with the same scrutiny as conventional forensic tooling. A key finding is that guidance aimed only at practitioners fails to reach investigators and attorneys, making direct examiner engagement with legal stakeholders essential. Read more (dfrws.org)
- 5
Windows Event Log Analysis Guide for IR
A detailed incident response guide covers Windows Event Log investigation methodology, from evidence preservation and scoping to key Event IDs for logon analysis, lateral movement detection, and Kerberos/NTLM authentication tracing. Logon Type definitions, failure reason codes, and RDP session artifacts are mapped to specific event channels, giving practitioners a structured starting point for triage. Guidance on AI-assisted analysis includes clear warnings about hallucination risks and data privacy when handling sensitive log content. Read more (sumeshi.github.io)