This Week on Forensic Focus
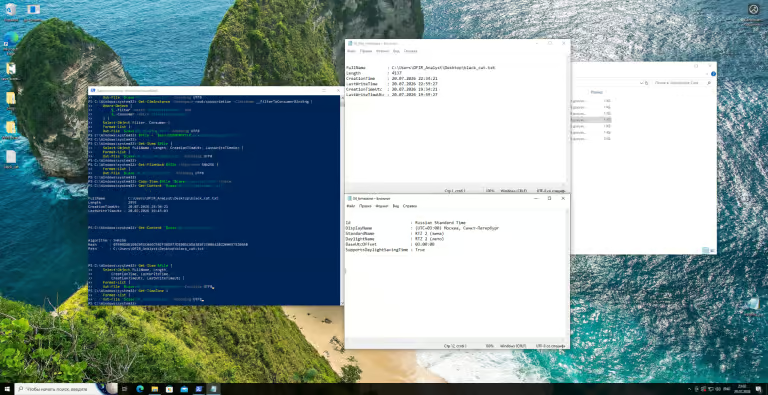
Investigating WMI Permanent Event Subscription Persistence
Vitalii offers a hands-on DFIR deep dive into WMI ActiveScriptEventConsumer persistence, from registration and execution to memory artifacts, Sigma detection, and cleanup.
MD-RED v4: AI-Powered Mobile Forensic Analysis, From Raw Evidence To Case Insight
See how MD-RED v4 handles growing evidence volumes with AI-based media analysis, malware scanning, CDR correlation and PC messenger data in one…
Amped Podcast Episode 4 – User Needs, Forensic Minds: How New Features Are Born
Sam Abbot, Emi Polito and Andrea Frisina go behind the scenes to show how your feedback becomes new features in Amped FIVE,…
Cellebrite Genesis vs. ChatGPT: Why You Need Purpose-Built Investigative AI
What sets purpose-built investigative AI apart from general-purpose LLMs? Discover how Cellebrite Genesis helps investigators analyze digital evidence with traceable findings, warrant-bound…
Elsewhere in DFIR
- 1
Free 720-Page Incident Response Book Available
SANS Faculty Fellow Joshua Wright released Dynamic Incident Response, a 720-page incident response book, free to the community. Wright is distributing signed print copies at the DFIR Summit in Arlington, with the full text available as a free download for those not attending. Read more (dynamicincidentresponse.com)
- 2
Europol Maps EU Digital Forensics Capability Gaps
The European Commission and Europol have published a gap and needs analysis identifying critical shortfalls in digital forensic capabilities across EU member states. Key problem areas include cloud, IoT, and vehicle forensics, unaffordable commercial tools, and insufficient cross-border expertise sharing. Findings will shape future EU funding under the Internal Security Fund and guide development of shared forensic solutions. Read more (eureporter.co)
- 3
Open-Source Tool Extracts WhatsApp Web Browser Data
WhatsApp Web Extractor is a new open-source forensic tool that parses Chrome, Edge, Brave, and Firefox browser profiles to recover WhatsApp Web chats, media, and metadata without launching a browser. It reads IndexedDB and localStorage directly, supports three decryption modes, and outputs both readable JSON and an Android-format msgstore.db compatible with existing WhatsApp forensic suites. A GUI and CLI are available for Windows, with a Linux binary also provided. Read more (linkedin.com)
- 4
New Research Targets OneDrive Forensic Artifacts
Brian Maloney's research on OneDrive forensic artifacts, presented at the SANS DFIR Summit, covers the evolution of OneDrive and its implications for casework. A companion tool accompanies the findings, giving examiners practical support for cloud storage investigations. Read more (malwaremaloney.blogspot.com)
- 5
ORISA Tool Recovers Deleted AI Chats from Android Memory
Georgia Tech researchers have built ORISA, a memory forensics tool that recovers deleted conversations from locally running AI assistants on Android devices, even after users delete them. Tested across 10 apps, three AI models, and 60 configurations, the tool reconstructs recoverable fragments into functional AI sessions, surfacing data the original session had already stopped actively using. Presented at the 2026 IEEE Symposium on Security and Privacy, the research opens a new artifact category for mobile forensic examiners investigating AI assistant activity. Read more (newswise.com)