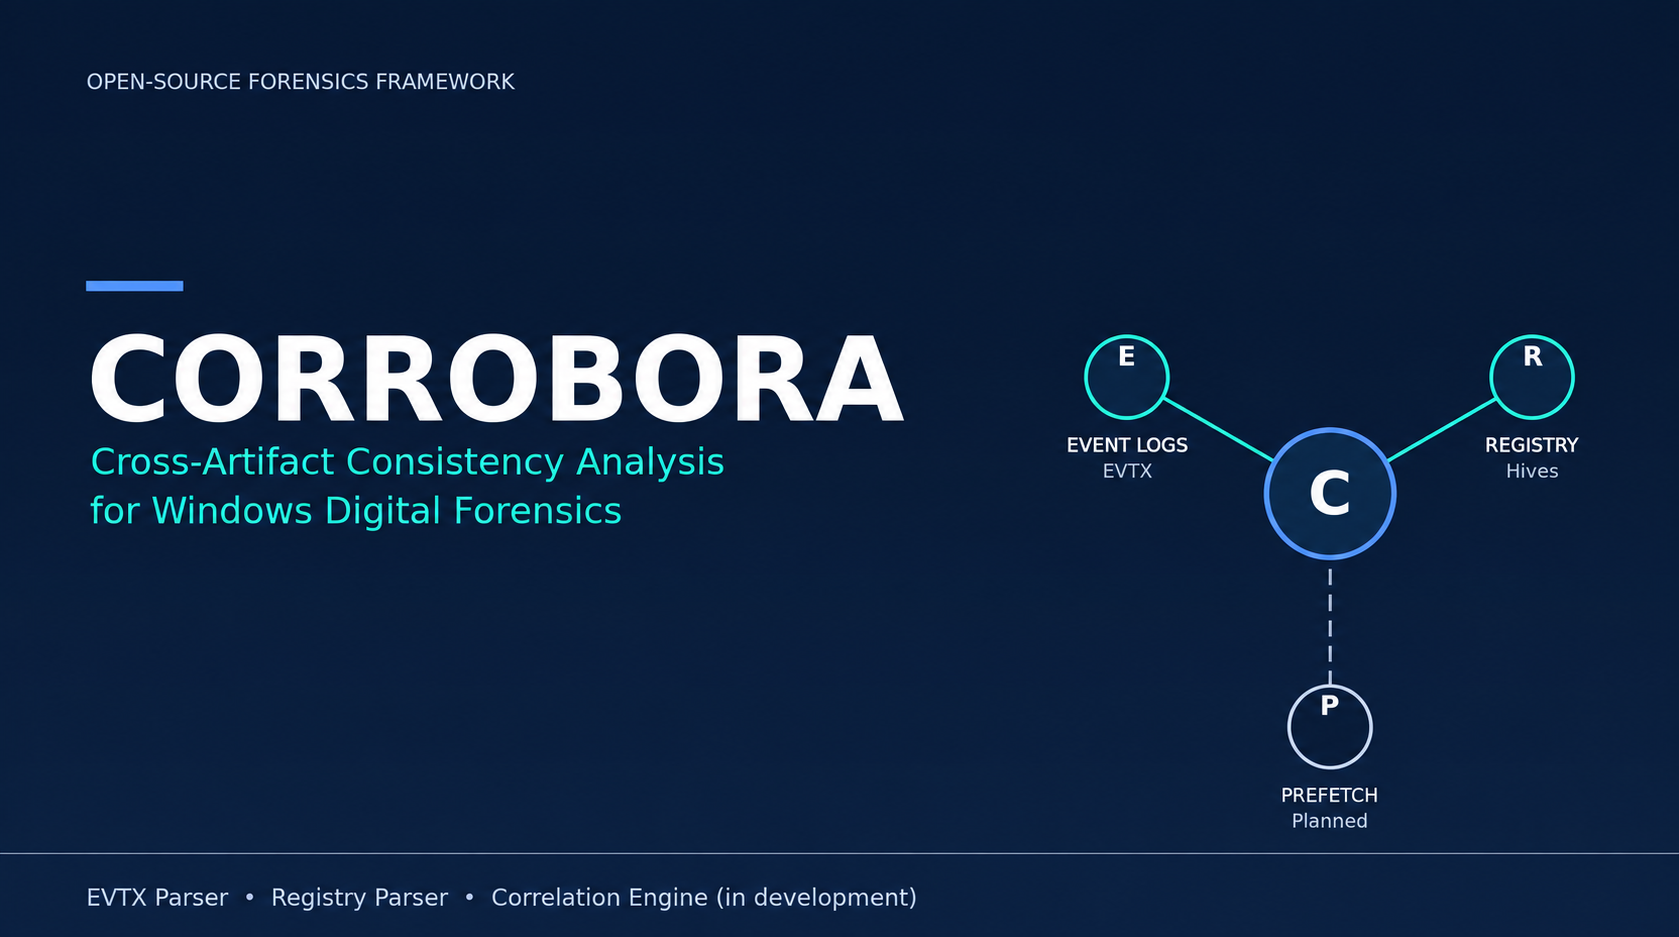
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

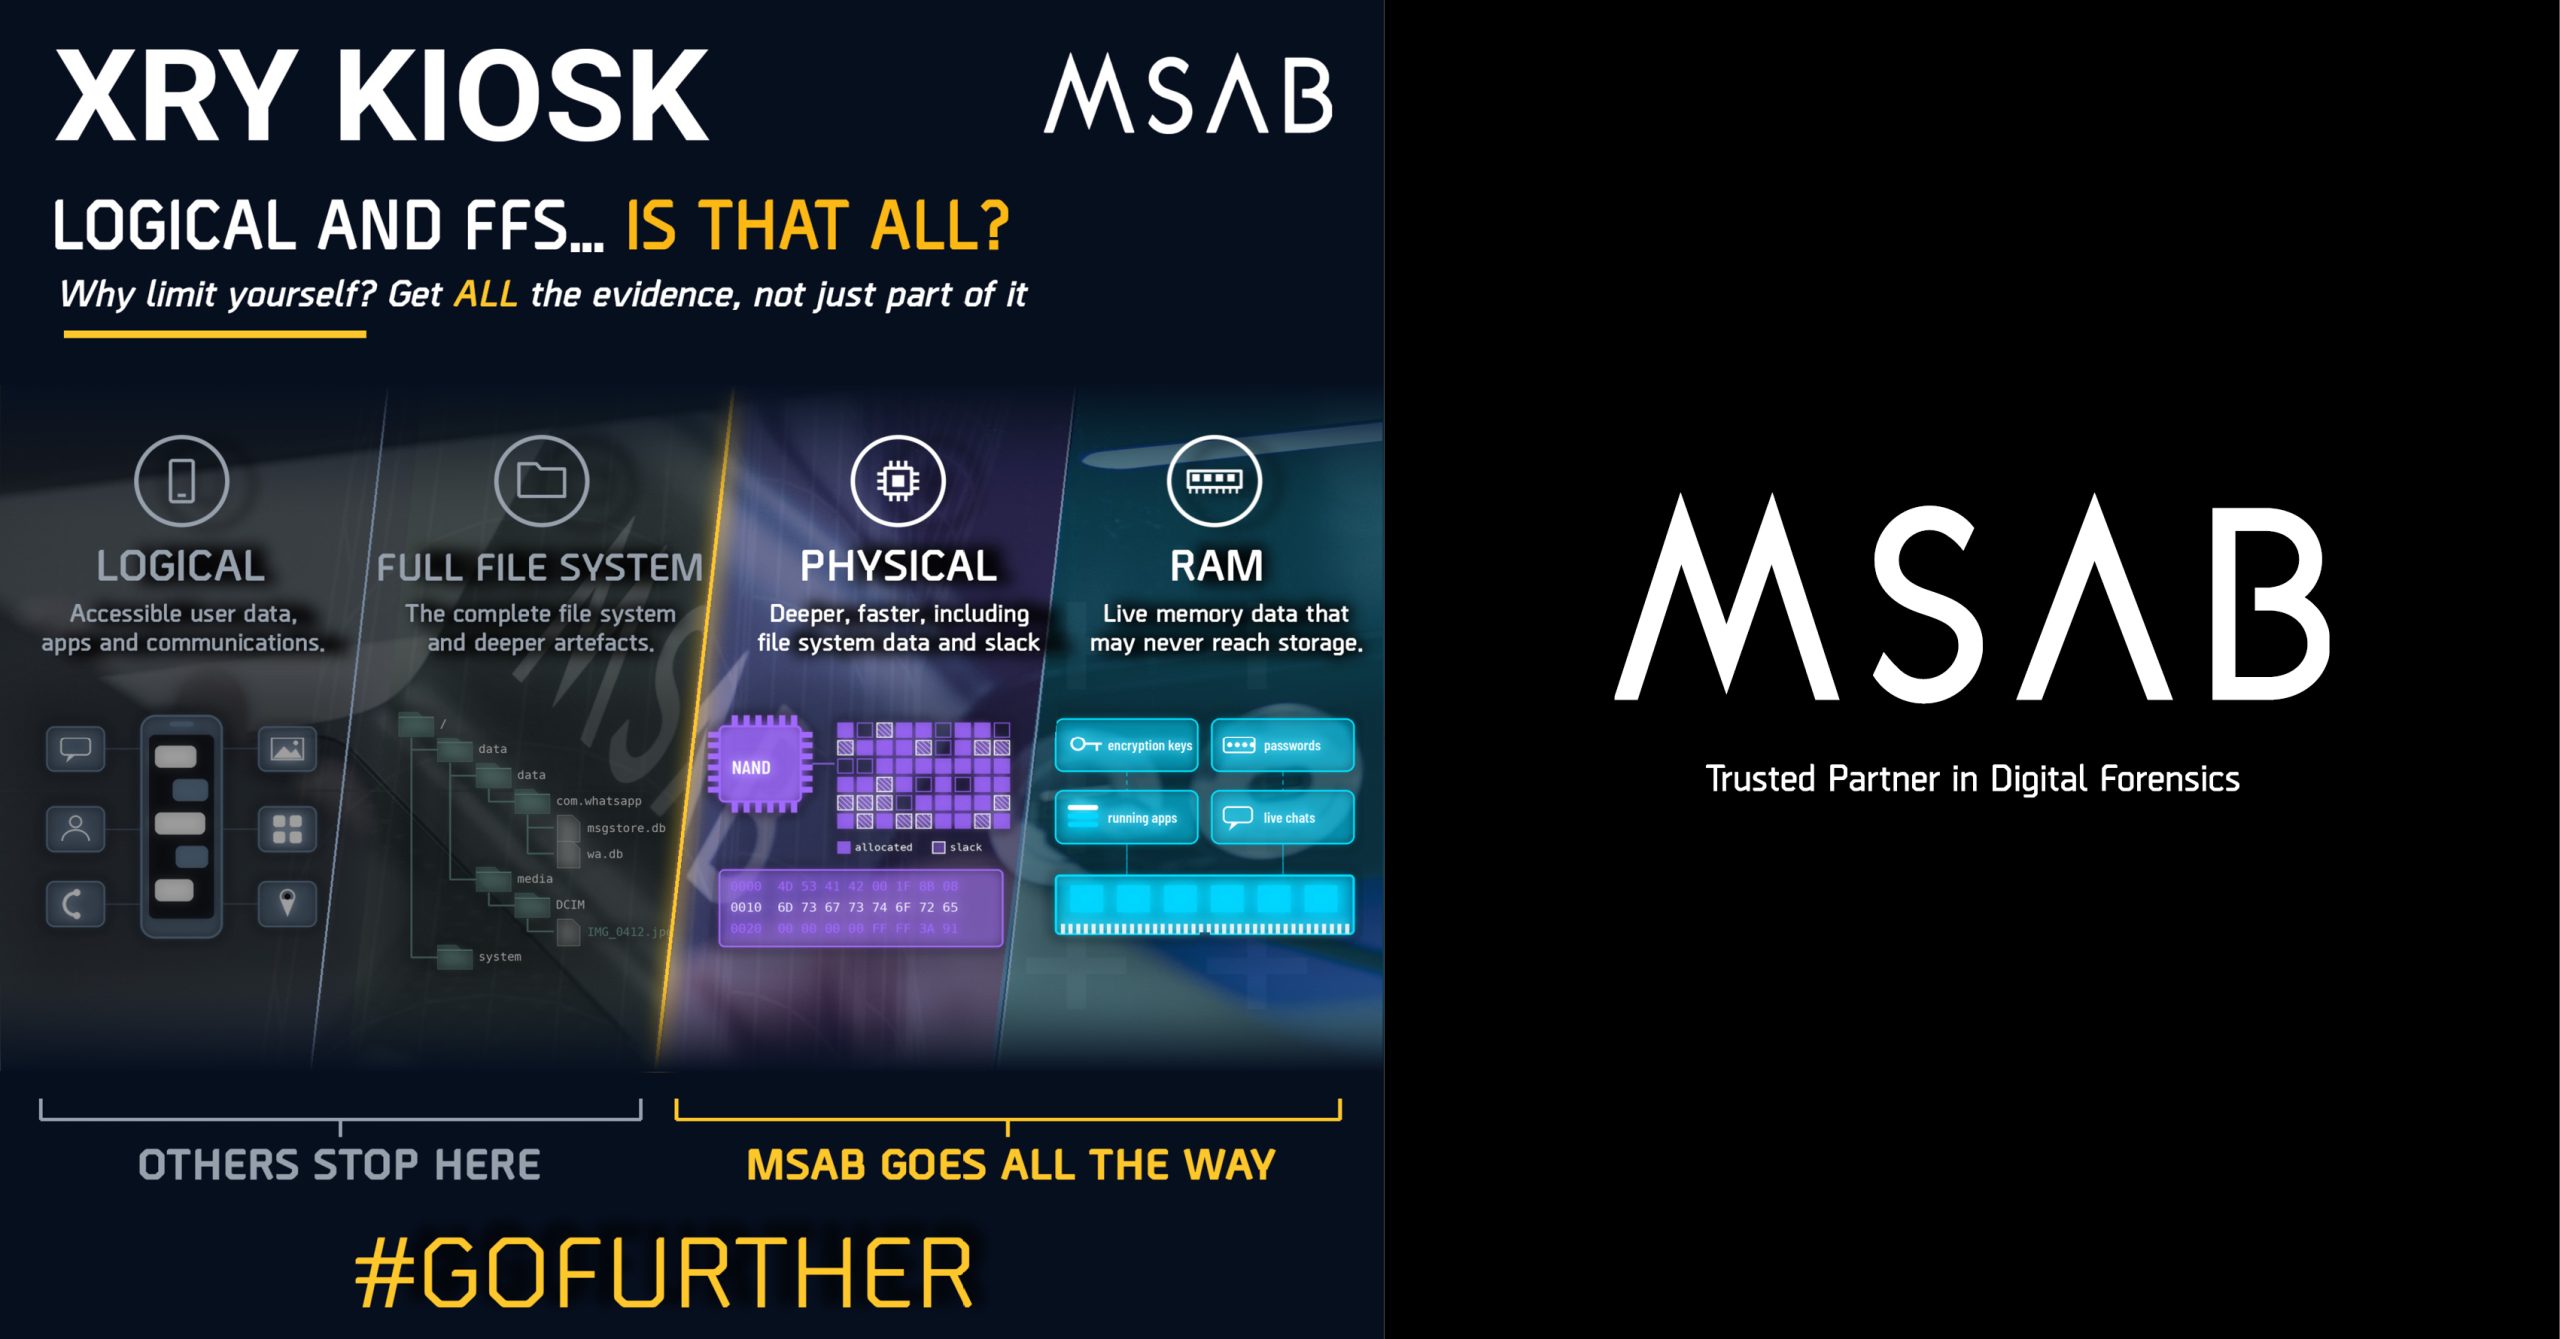
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Western Digital’s Advanced Format

“What is it? In a nutshell, it’s replacing the traditional 512 byte hard drive sector with a 4 kilobyte (4,096B) hard drive sector for a number of practical and technological reasons. The move to 4K-sectors has been some 10 years

Into The Boxes Issue 0×0

Into The Boxes is an e-magazine covering issues concerning Digital Forensics and Incident Response. The first issue contains four specific articles that cover a variety of digital forensic and incident response issues… More (Into the Boxes)

Adroit Photo Forensics review

A review of Adroit Photo Forensics is now online here with follow up discussion available here. Many thanks to Austin Troxell for the review.

Secret mobile phone codes cracked

A German computer scientist has published details of the secret code used to protect the conversations of more than 4bn mobile phone users. Karsten Nohl, working with other experts, has spent the past five months cracking the algorithm used to

Digital Forensics Research Challenge Results Released

The results and winners of the 2009 Digital Forensics Research (DFRWS2009) Challenge were announced at the 9th Annual DFRWS Conference. This challenge delves into gaming consoles from a forensic perspective, combining UNIX file system forensics, memory forensics, and network forensics.

More on DECAF

DECAF takes an interesting turn at decafme.org plus Cyberspeak interview at http://cyberspeak.libsyn.com/index.php?post_id=561335

IntaForensics launches hunt for next generation of computer forensics experts

With the demand rising rapidly for computer forensics, Nuneaton-based computer forensics firm IntaForensics has enjoyed rapid growth. Now, the firm is launching a free 5-day intensive training course to attract the interest of local graduates…In recent years, as computers and

Protect yourself from COFEE with some DECAF

In response to Microsoft’s Computer Online Forensic Evidence Extractor (COFEE), which helps law enforcement officials grab data from password protected or encrypted sources, two developers have created “Detect and Eliminate Computer Assisted Forensics” (DECAF), a counter intelligence tool designed to

Experimental Validation Tool For Cell Phone Forensics Developed

Viewers of TV dramas don’t focus on the technology behind how a forensics crime team tracks a terrorist or drug ring using cell phone data, but scientists at the National Institute of Standards and Technology (NIST) do. NIST researchers have

Paraben’s Chat Examiner v2.0 Released

Paraben has announced the release of Chat Examiner v2.0. If your subscription is current, you can download the new version from your registration site account at http://register.paraben-forensics.com. If your subscription is not current, you can update it from your registration

viaForensics announces Android Forensics training course

viaForensics has announced their Android Forensics training course which will prepare examiners with the tools, techniques and analysis methods to investigate an Android device. This training course is for law enforcement or government employees only and coincides with the DoD

Interview with Russell May, 4N6 Investigation

An interview with Russell May of 4N6 Investigation is now online at http://www.forensicfocus.com/russell-may-interview-101209. Russell is a well known figure in the computer forensics world with a reputation for providing some of the best training courses available. Enjoy the interview!

SC Suite v3.9 Released.

A new version of SC Suite is available, version 3.9 now includes more tools to analyse and extract information from a variety of file types and utilities to assist in every day tasks. Continuing user feedback has resulted in the

HBGary Launches HBGary Federal

HBGary, Inc. today announced the spin-off of its U.S. government cybersecurity services group. The new company, known as HBGary Federal, will focus on delivering HBGary’s malware analysis and incident response products and expert classified services to the Department of Defense,

Forensic Computing PhD, UK

There is a PhD position available at the Centre for Forensic Computing, Cranfield University, UK. The broad area for the research is the investigation of the digital evidence left on hard disks by users who have communicated via the Internet.