Belkasoft, a global provider of digital forensics and incident response (DFIR) software, announced the release of Belkasoft X version 2.13. The company’s fourth release of the year equips BelkaGPT, its offline AI assistant, with document summarization, topic detection across more types of communication, and chain of thought in answers. Version 2.13 also adds support for the major AI assistant apps and introduces deleted file analysis based on NTFS Master File Table (MFT) records.
A More Transparent and Versatile AI Assistant
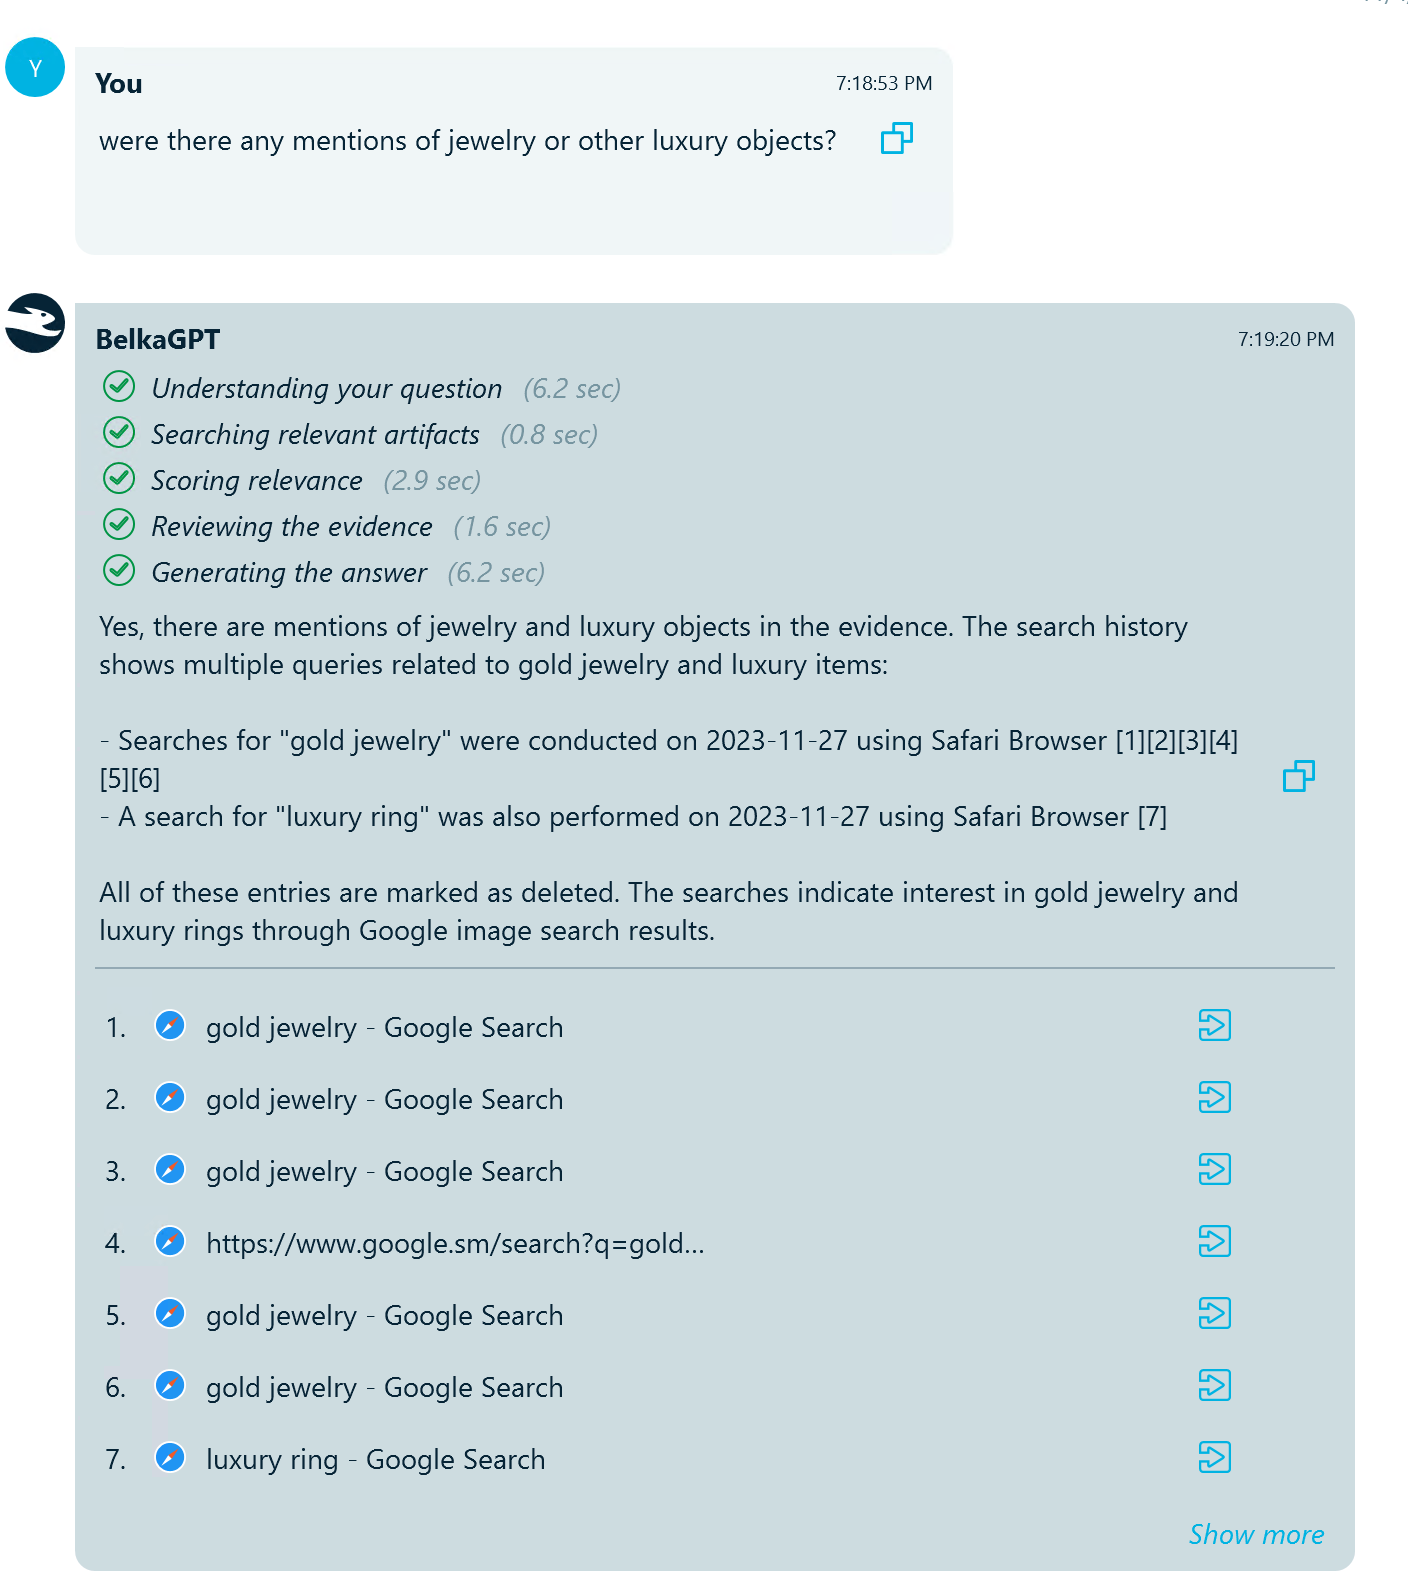
A key addition in version 2.13 is a chain of thought in BelkaGPT answers. While generating a response, BelkaGPT now displays the steps it takes to answer the investigator’s question, along with the time each step took. Combined with references to the underlying artifacts, which BelkaGPT already provides, this lets investigators see not only what evidence an answer relies on, but also how the answer was reached, making AI-assisted findings easier to assess and stand behind.
BelkaGPT also gains document summarization. You can summarize word processor files, PDFs, spreadsheets, slide decks, and plain-text logs to quickly understand what each document contains and decide whether it deserves closer examination. A quick summary covers the first 500 words of a document, while a full summary processes up to 25,000 words. Summaries are written in the language the investigator selects, regardless of the document’s original language.
Topic detection, introduced in version 2.11 for chats, now extends to emails and SMS messages. The same predefined detectors, covering categories such as money, drugs, operational coordination, and account access, as well as investigator-defined custom detectors, now work across all three communication types.
The release also makes BelkaGPT more accessible on modest hardware. A new fast answer mode automatically adapts answer generation to the available hardware, cutting response times on computers without a compatible GPU to about 1 to 3 minutes, down from 12 to 15. The BelkaGPT Q&A chat can now also run on BelkaGPT Hub, offloading answer generation to shared infrastructure within the investigator’s own network, and a built-in tutorial helps new users get started with BelkaGPT features.
“We keep bringing BelkaGPT to the areas where investigators need it most: the tasks that eat up hours of manual review. But in digital forensics, speed is only valuable if you can trust the result. That’s why reliability and transparency guide every BelkaGPT feature we build, just as much as capability does.”
Yuri Gubanov, CEO of Belkasoft
When AI Is the Evidence
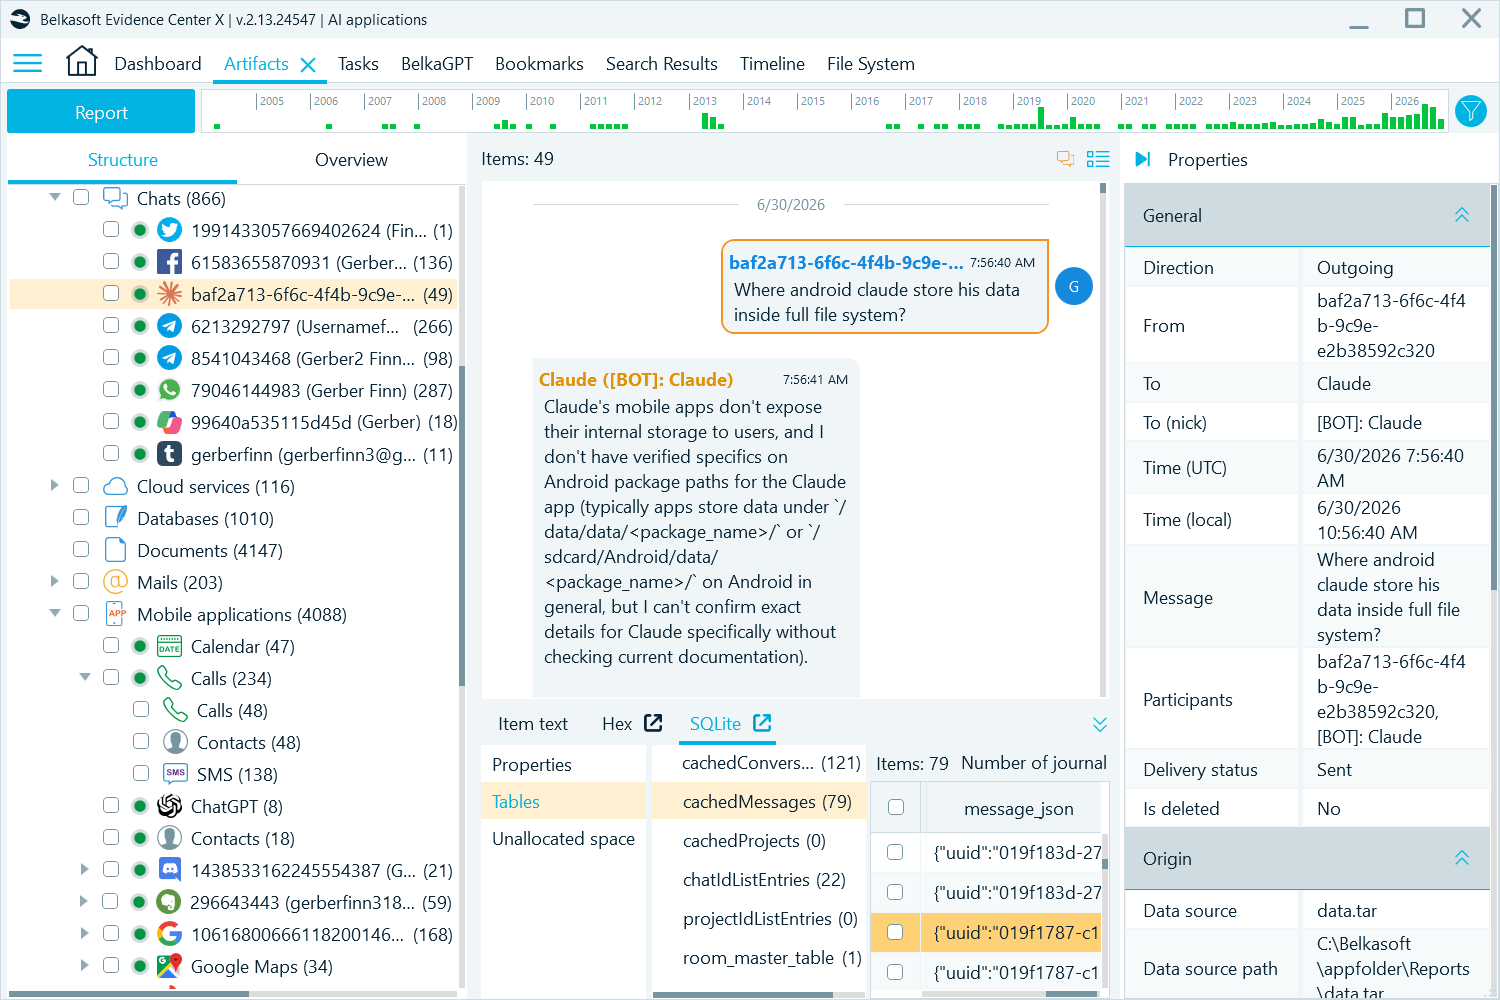
As AI chatbots become part of everyday life, conversations with them are increasingly relevant to investigations. Belkasoft X v2.13 adds artifact extraction for Claude AI and Copilot on both Android and iOS, and for ChatGPT on Android, alongside updated support for the latest ChatGPT version on iOS. Data from these apps is presented in Belkasoft X together with messages, documents, browser history, and other evidence, ready to be searched, analyzed, and reported.
Recovering Deleted Files from the MFT
Deleting a file rarely erases every trace of it. Belkasoft X v2.13 puts those traces to work: it reconstructs records of deleted files and folders from the NTFS Master File Table, bringing evidence that no longer appears in the regular folder structure back into the case, including from volume shadow copies.
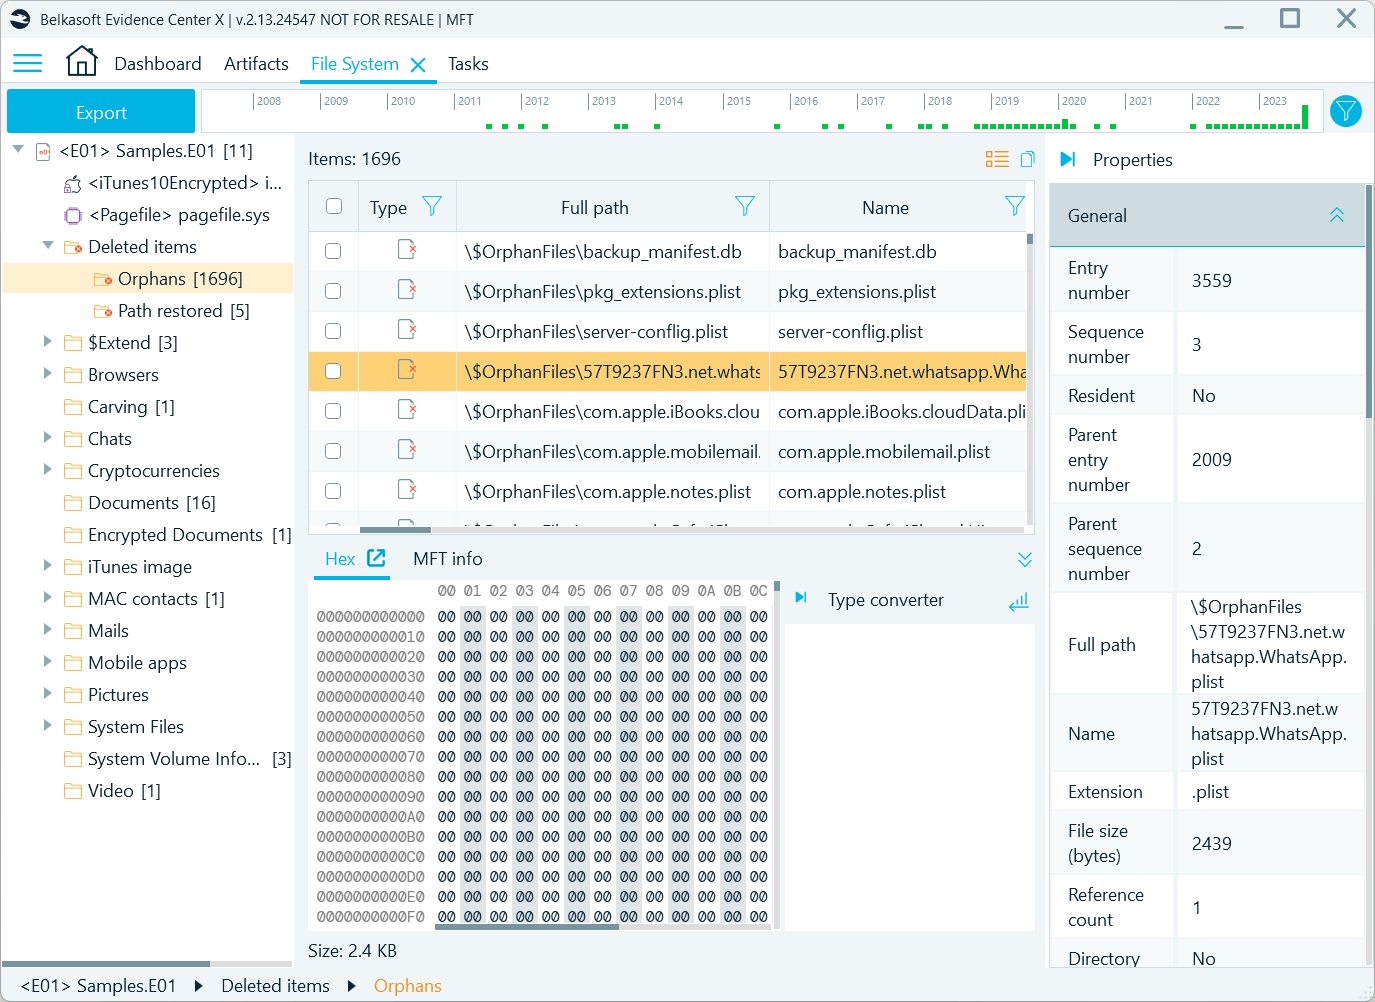
Investigators can quickly zero in on the deleted files that matter, establish what was stored on a volume and when, and recover files whose data is still on the disk, all within the same environment where they review the rest of the evidence.
Stronger Acquisition Across Mobile and Cloud Sources
The release continues to refine the MediaTek (MTK) acquisition workflow redesigned in version 2.12. Belkasoft X now correctly handles dumps from devices that use file-based encryption without metadata encryption, accepts MTK dump.bin files as mobile images, and provides clearer task statuses and logs for brute-force and decryption. A new utility, available on request from Belkasoft support, enables decryption of dumps acquired with MTKClient.
On the cloud side, Google Cloud acquisition now falls back to signing in through a browser window when the initial sign-in attempt fails, keeping acquisition stable as Google changes its authentication protocols. Browser sign-in works across all supported Google services, including Drive, Gmail, Keep, My Activity, and Sync, and supports two-factor authentication.
Expanded Artifact Coverage and Reporting
Beyond AI assistants, version 2.13 adds support for Google Files, Google Messages, Google Photos, Samsung Gallery Trash, and Samsung My Files on Android, and improves extraction from Telegram, TikTok, Viber, Discord, Gmail, X (formerly Twitter), and other apps. Reports on mobile app and SMS artifacts can now be split by contact or conversation, including in RSMF (Relativity Short Message Format), making large volumes of communications easier to review and share selectively.
Availability
Belkasoft X v2.13 is available now. Upgrading from previous versions is free for all customers with an active Software Maintenance and Support (SMS) contract.
To explore all new features and download the latest version, visit the Belkasoft X release page: https://belkasoft.com/whats-new-in-belkax-2-13
About Belkasoft

Belkasoft is a global provider of digital forensics and incident response solutions trusted by law enforcement agencies, government bodies, and corporate security teams worldwide. Through ongoing investment in AI-powered capabilities, Belkasoft is committed to equipping the DFIR community with tools that match the pace and complexity of modern investigations.