Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

Data-Driven Approach For Automatic Telephony Threat Analysis

ElMouatez Billa Karbab discusses his work at DFRWS EU 2018. Elmouatez: Hello back. Yeah. I’m here the second author, and the first one couldn’t make it. This is why I’m presenting. Thank you. This work is entitled ‘Data-Driven Approach for

Register For Webinar: Valuable New Capabilities of the Tableau TX1

The latest free update for the OpenTextâ„¢ Tableau TX1 Forensic Imager provides several exciting new features and enhancements guaranteed to improve data acquisition capabilities. Join OpenText on January 29 at 11 am CST for a live webinar, Valuable New Capabilities

OpenForensics: A Digital Forensics GPU Pattern Matching Approach

Ethan Bayne discusses his research at DFRWS EU 2018. Ethan: Hello, everyone. I understand I am the last talk separating you between coffee, so I’ll try to keep it brief. So, my name is Ethan Bayne, I’m coming today from

Digital Forensics News January 2019

OpenText have released EnCase Forensic 8.08, with new cloud and encryption capabilities. There’s only one week left to submit your proposals for DFRWS US 2019, which takes place in Portland, OR in July. The latest version of BlackLight from BlackBag

Forensic Focus Forum Round-Up

Welcome to this month’s round-up of recent posts to the Forensic Focus forums. What are your current best practices when you encounter a device that’s full disk encrypted? Would you be interested in attending a forensics get-together in the US

How Trustworthy Is Digital Evidence?

Leonhard Hosch shares his research at DFRWS EU 2018. Leonhard: Thank you. I’ll be presenting the paper ‘Controlled Experiments in Digital Evidence Tampering, or How Trustworthy is Digital Evidence?’ I’m Leonhard Hosch, I’m with Felix Freiling, I’m currently doing my

How Trustworthy Is Digital Evidence?

Leonhard Hosch shares his research at DFRWS EU 2018. Leonhard: So, thank you. I’ll be presenting the paper ‘Controlled Experiments in Digital Evidence Tampering, or How Trustworthy is Digital Evidence?’ I’m Leonhard Hosch, I’m with Felix Freiling, I’m currently doing

Dissecting Malicious Network Traffic To Identify Botnet Communication

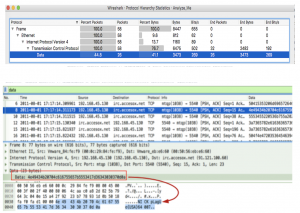
by Swasti Bhushan Deb Botnets are well-known in the domains of information security, digital forensics and incident response for hosting illegal data, launching DDOS attacks, stealing information, spamming, bitcoin mining, spreading ransomware, launching brute force attacks, managing remote access to

Dissecting Malicious Network Traffic To Identify Botnet Communication

by Swasti Bhushan Deb Botnets are well-known in the domains of information security, digital forensics and incident response for hosting illegal data, launching DDOS attacks, stealing information, spamming, bitcoin mining, spreading ransomware, launching brute force attacks, managing remote access to

Scene Of The Crime: You’ve Found A Drone. What Do You Do?

by Lee Reiber, COO, Oxygen Forensics, Inc. The proliferation of recreational drones and their impact on digital incident response has dramatically increased during the last several years. In January 2018, Nextgov stated the U.S. Federal Aviation Administration (FAA) reported over