Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

How Detego Global’s AI Technology Is Transforming Child Abuse Investigations

Hero Image

Discover how AI-powered digital forensics is helping investigators accelerate child abuse investigations, identify critical evidence faster, safeguard victims, and reduce exposure to distressing content with Detego Global’s advanced technology....
Today's headlines 2 Nov 2026

AI For Investigations: 5 Myths, Debunked

AI For Investigations: 5 Myths, Debunked

Discover the truth behind five common myths about AI in investigations, with real-world insights from investigators using Cellebrite Genesis....read more
Forensic Focus Digest, 30 Oct 2026

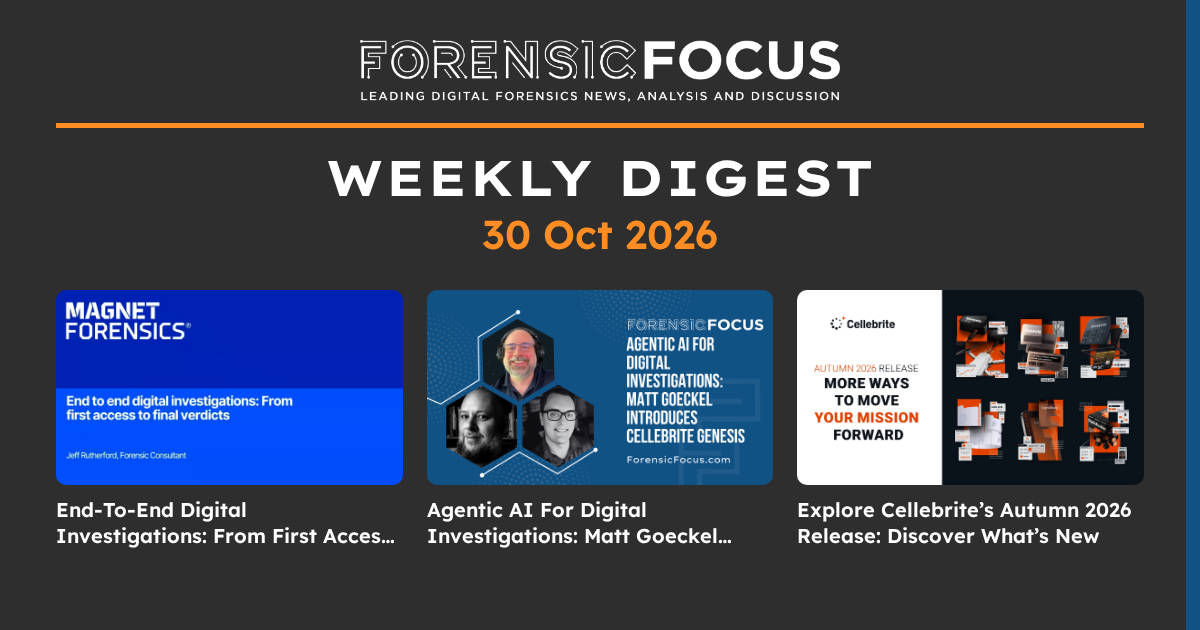
Forensic Focus Digest, 30 Oct 2026

Discover what’s new on Forensic Focus: explore end-to-end digital investigations with Magnet Forensics, meet Matt Goeckel, AI researcher at Cellebrite, learn about the Cellebrite Autumn 2026 Release, and more....read more
How A MacBook With A Broken Screen Helped Convict A UK Property Fraudster: Belkasoft X Case Study

How A MacBook With A Broken Screen Helped Convict A UK Property Fraudster: Belkasoft X Case Study

A broken MacBook, an iPhone, and a £113,000 fraud case - discover how Belkasoft X helped uncover crucial digital evidence that brought a UK property fraudster to justice....read more

Computer Monitoring: Software vs. Hardware Keyloggers

First published November 2006 Stephen Allen, Allen Concepts Inc., Chandler, AZ July 2006 www.keykatcher.com ABSTRACT John has been at his computer for hours, but his productivity has fallen lately. Is he emailing buddies, busy in chat rooms, or reading internet

The need for effective event management

First published November 2006 courtesy of GFI Software – www.gfi.com Introduction Underrated, undervalued and underutilized; events management is most often rated as a tedious and ungrateful task. System administrators shy away from event logs and the events contained within, citing

How Digital Detectives Deciphered Stuxnet

In June 2009, someone had silently unleashed a sophisticated and destructive digital worm that had been slithering its way through computers in Iran with just one aim — to sabotage the country’s uranium enrichment program and prevent President Mahmoud Ahmadinejad

Reflections on a first computer forensic investigation

First published October 2006 by Brian Marofsky What follows is a synopsis of the experience I had of conducting my first computer forensic investigation. It was my no means a text book investigation. I made my share of mistakes but

Examining Wireless Access Points and Associated Devices

First published October 2006 Sgt. Christopher Then, CISSP, EnCE September 17, 2006 Computer Crimes Unit Morris County Prosecutor’s Office Morristown, NJ 07963 [email protected] Wireless access for the home has become the preferred choice of connecting computers to the Internet. As

Dissecting NTFS Hidden Streams

First published July 2006 by Chetan Gupta NII Consulting, Mumbai www.niiconsulting.com   Cyber Forensics is all about finding data where it is not supposed to exist. It is about keeping the mind open, thinking like the evil attacker and following

VMWare as a forensic tool

First published May 2006 Brett Shavers May 2006 VMWare Workstation is one of the most up and coming software applications in both the corporate environment and in the computer forensic community. This paper will not detail the inner workings of

The Farmer’s Boot CD

First published May 2006 Preview Data in Under Twenty Minutes by Thomas Rude THE FARMER’S BOOT CD Preview Data in Under Twenty Minutes On January 1, 2006, THE FARMER’S BOOT CD, or FBCD for short, was officially released to the

Forensic Analysis of the Windows Registry

First published April 2006 Lih Wern Wong School of Computer and Information Science, Edith Cowan University [email protected] Abstract Windows registry contains lots of information that are of potential evidential value or helpful in aiding forensic examiners on other aspects of

Evidentiary Value of Link Files

First published March 2006 by Nathan Weilbacher I have been reading the posts in Forensic Focus for about a year now and on many occasions I have followed with great interest the threads of discussion on many topics. There are

Are non technical juries keeping criminals at large?

First published February 2006 by Carrie Moss, Marketing Assistant, CY4OR www.CY4OR.co.uk In England and Wales the only qualifications required of a jury member to be eligible to appear in a court of law are that they are registered on the

Analysis of hidden data in the NTFS file system

First published January 2006 Cheong Kai Wee Edith Cowan University [email protected] Abstract Criminals with sensitive information such as crime records tend to hide/encrypt this information so that even if their computers are collected by police department, there is no evidence