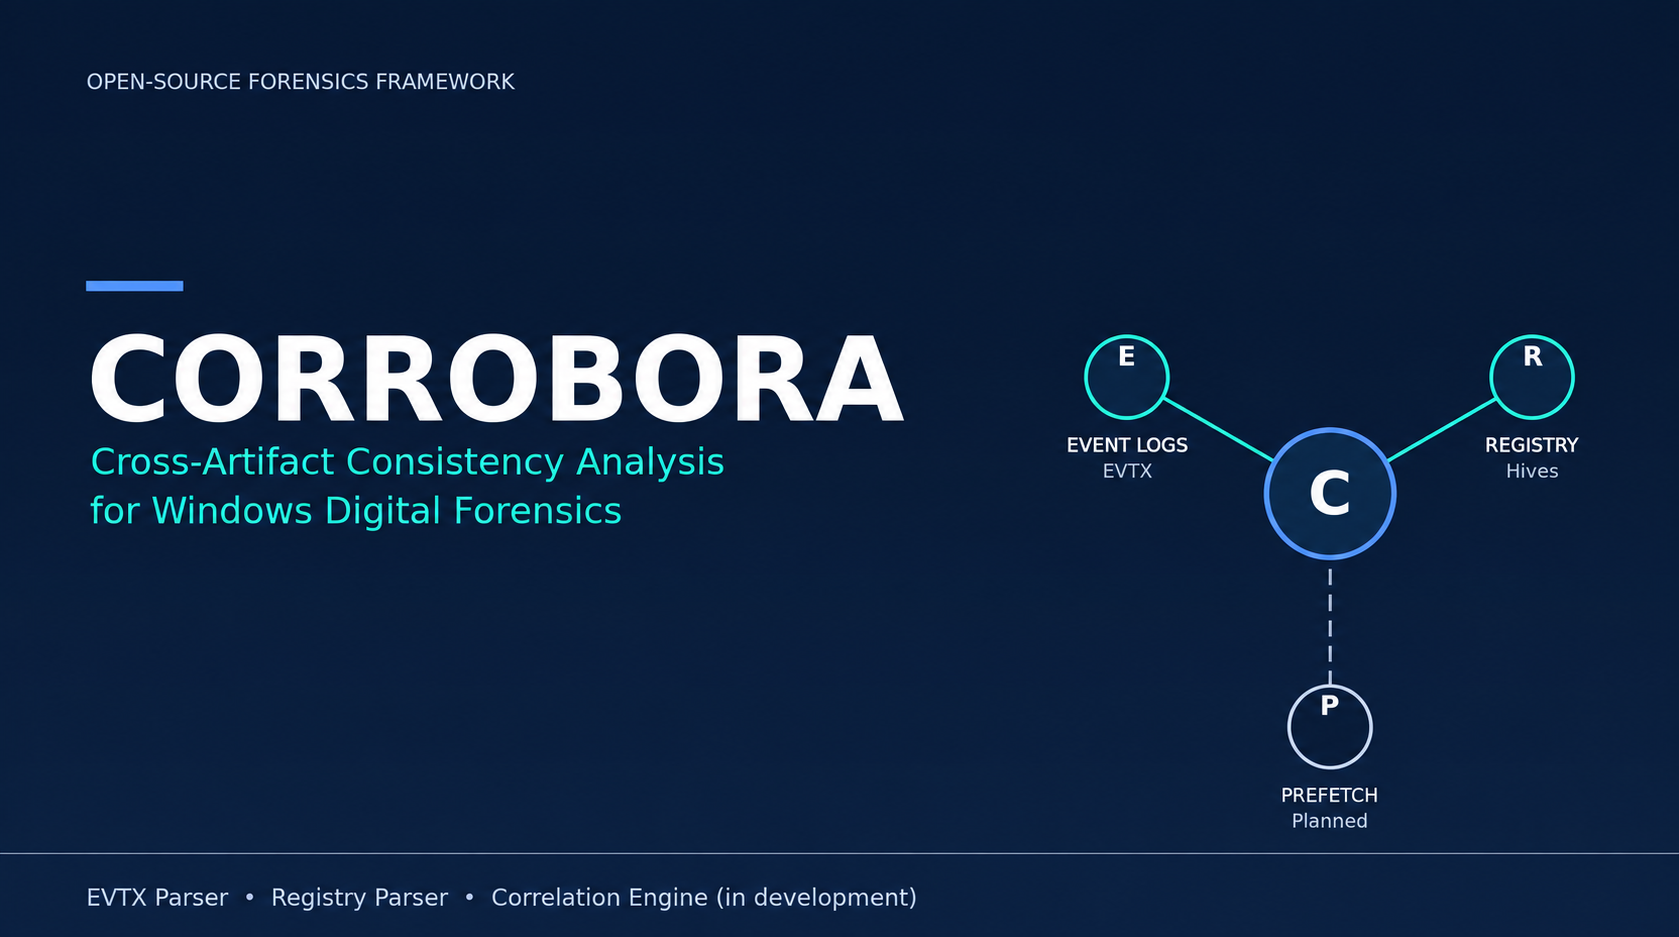
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

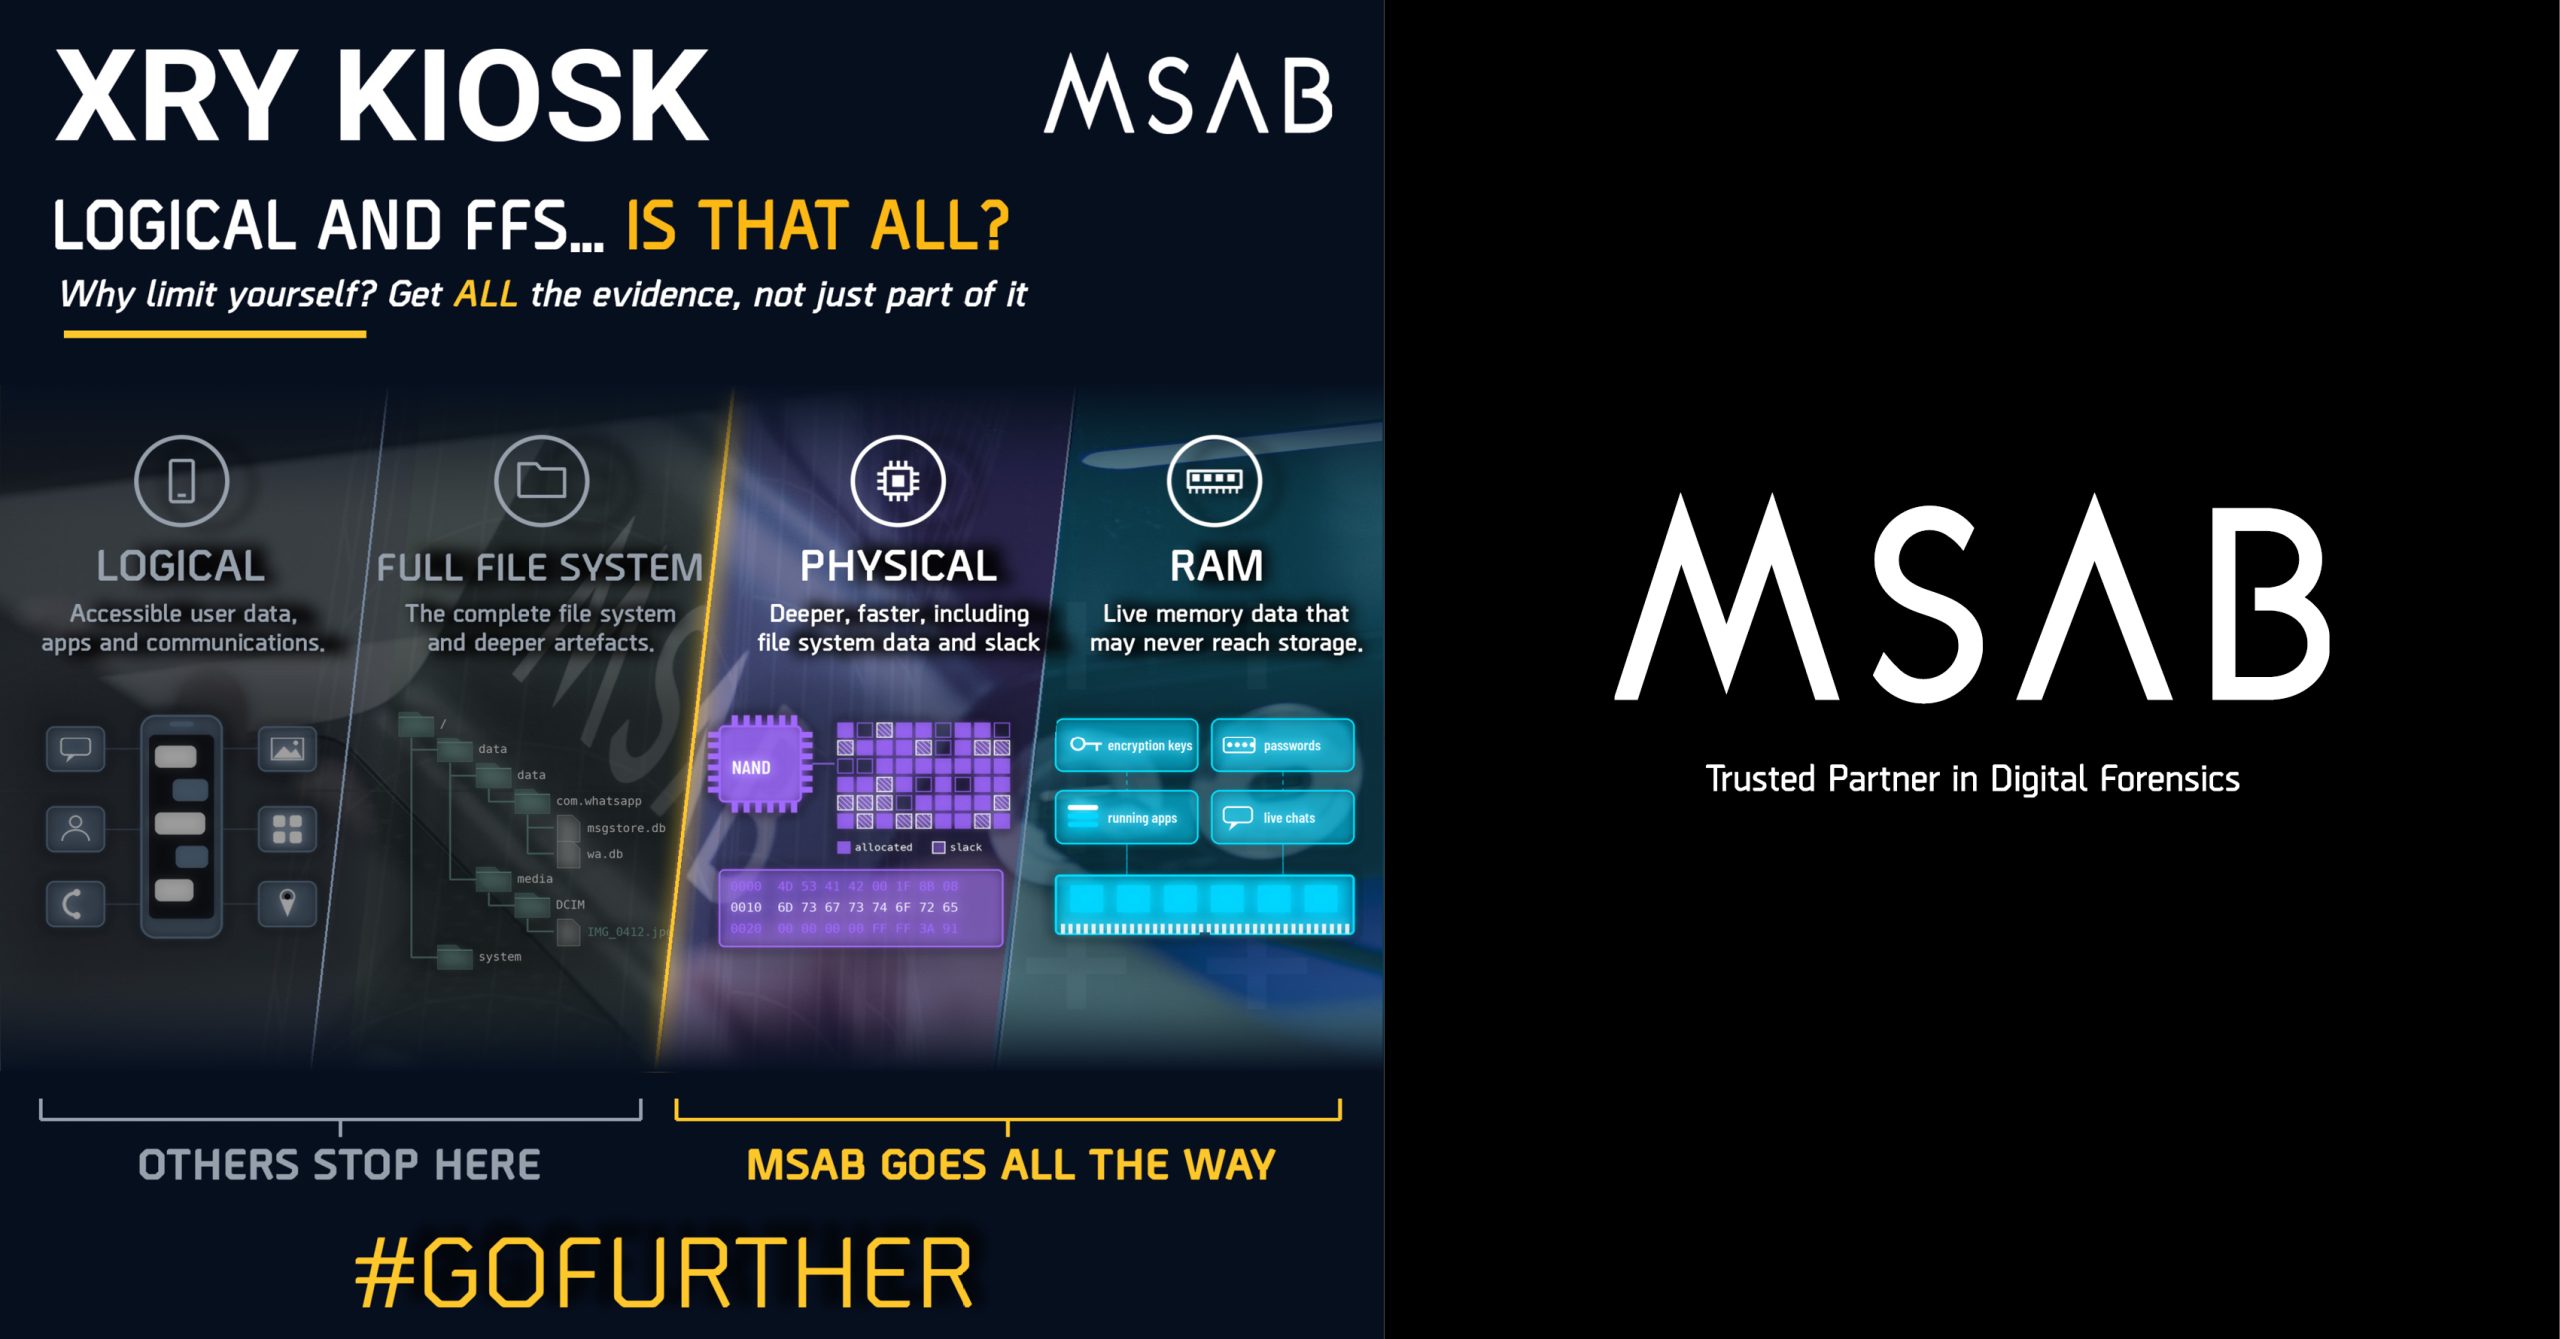
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
What’s Happening In Forensics – Jan 29, 2020

Errata Security discuss how to decrypt WhatsApp end-to-end media files. The HTCIA 2020 call for presentations is now open. Linux Security Labs share a review of GRR Rapid Response. Rick Holland recaps the SANS Cyber Threat Intelligence Summit 2020.

Amped Authenticate Update 15518: Customizable Reporting, Sun Position And More

Amped Software just released another update to Amped Authenticate, the leading forensic software for digital forensic experts to exploit the data behind digital images, allowing analysis of image integrity, authenticity, metadata, source and history, and detection of tampering prior to

What’s Happening In Forensics – Jan 28, 2020

Andrea Fortuna shares some thoughts on the Jeff Bezos phone hack data. Ciarán O’Brien provides a triage script to help with retrieving artifacts from compromised Citrix hosts. Magnet discuss how their new AXIOM Cyber tool can help with employee misconduct

What’s Happening In Forensics – Jan 27, 2020

Adam Harrison discusses evidence of program execution on different Windows OS versions. Magnet release AXIOM Cyber for remote acquisitions. Foxton Forensics discover some differences between Chromium and Edge Chromium artifacts. Andrew Hoog unpicks NavdDoomConductor, which tracks precise geolocation and time

Forensic Focus Forum Round-Up

Welcome to this month’s round-up of recent posts to the Forensic Focus forums. Forum members discuss IPv6 to IPv4 conversion in response to a warrant request. Can you explain why this prefetch folder is empty? How would you respond to

What’s Happening In Forensics – Jan 24, 2020

Steve Anson’s new book, Applied Incident Response, is now available on Amazon. Ciarán O’Brien has been working on a Jupyter notebook to help automate the process of pulling IOCs from artifacts recovered from compromised Citrix Netscalers. Heather Mahalik instigates a

Industry Roundup: Cloud Forensics

by Christa Miller Only a few short years ago, the idea of recovering forensic data from the cloud seemed like either troubling overreach, or unnecessarily redundant given the availability of evidence from mobile devices. As encryption became more prevalent on

Industry Roundup: Cloud Forensics

by Christa Miller Only a few short years ago, the idea of recovering forensic data from the cloud seemed like either troubling overreach, or unnecessarily redundant given the availability of evidence from mobile devices. As encryption became more prevalent on

What’s Happening In Forensics – Jan 23, 2020

Ryan Benson shows how Google search URLs can be a great source of digital forensic information. Magnet’s Jamie McQuaid discusses how deduplication can help your forensic analysis. Paraben’s Amber Schroader talks about getting started in digital forensics. Cellebrite share a

The iPhone Health App: A Forensic Perspective

Jan Peter van Zandwijk discusses his research at DFRWS EU 2019. Hello, my name is Jen Peter van Zandwijk. I work with the Netherlands Forensic Institute. And in this half-hour I will tell you about some research that they did

What’s Happening In Forensics – Jan 22, 2020

DFRWS announce a Women in Forensic Computing Workshop and Digital Forensics Bootcamp as part of this year’s EU conference. Mattia Epifani presents the CASE Ontology to the European Commission in Brussels. Mike Art Rebultan shares his route to a DFIR

Review: AccessData Enterprise From AccessData

by Jade James AccessData Enterprise enables investigators to forensically image and analyse devices. It also provides a means of workflow analysis and documentation, as well as a level of staff management. The inclusion of FTK means that examiners can conduct

What’s Happening In Forensics – Jan 21, 2020

Jessica Hyde shares a list of resources to help you keep up-to-date with mobile forensics. 13Cubed talk about CVEs in Windows event logs. Belkasoft discuss what’s new in Belkasoft Evidence Center v9.9.

The iPhone Health App: A Forensic Perspective

Jan Peter van Zandwijk discusses his research at DFRWS EU 2019.Hello, my name is Jen Peter van Zandwijk. I work with the Netherlands Forensic Institute. And in this half-hour I will tell you about some research that they did on