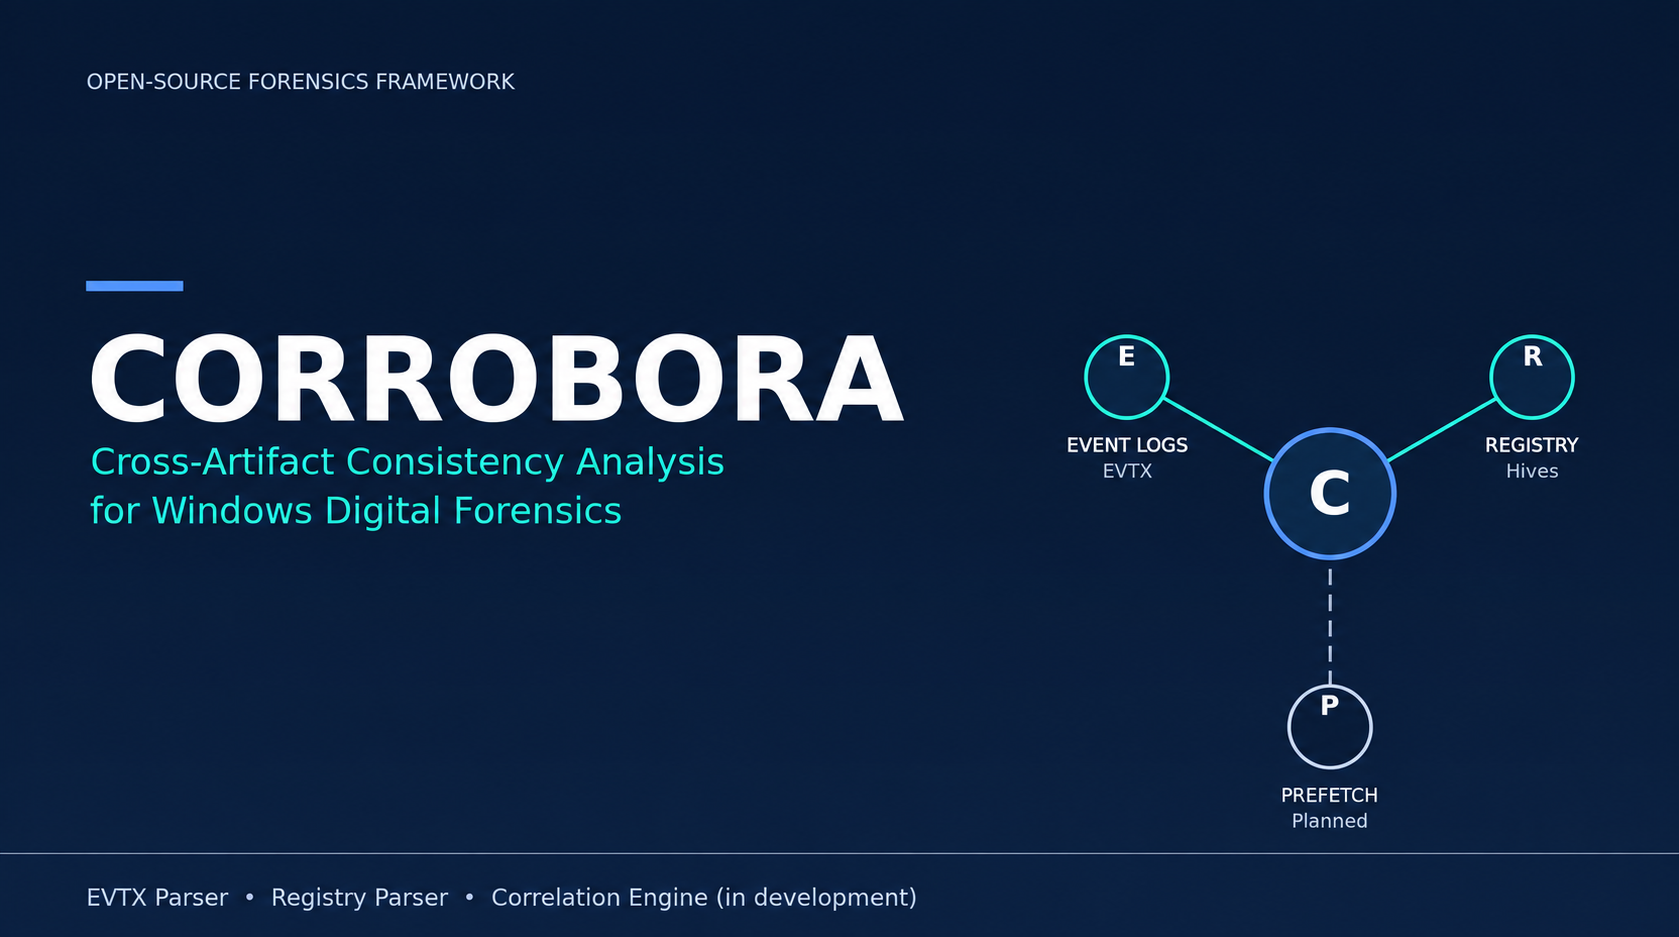
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

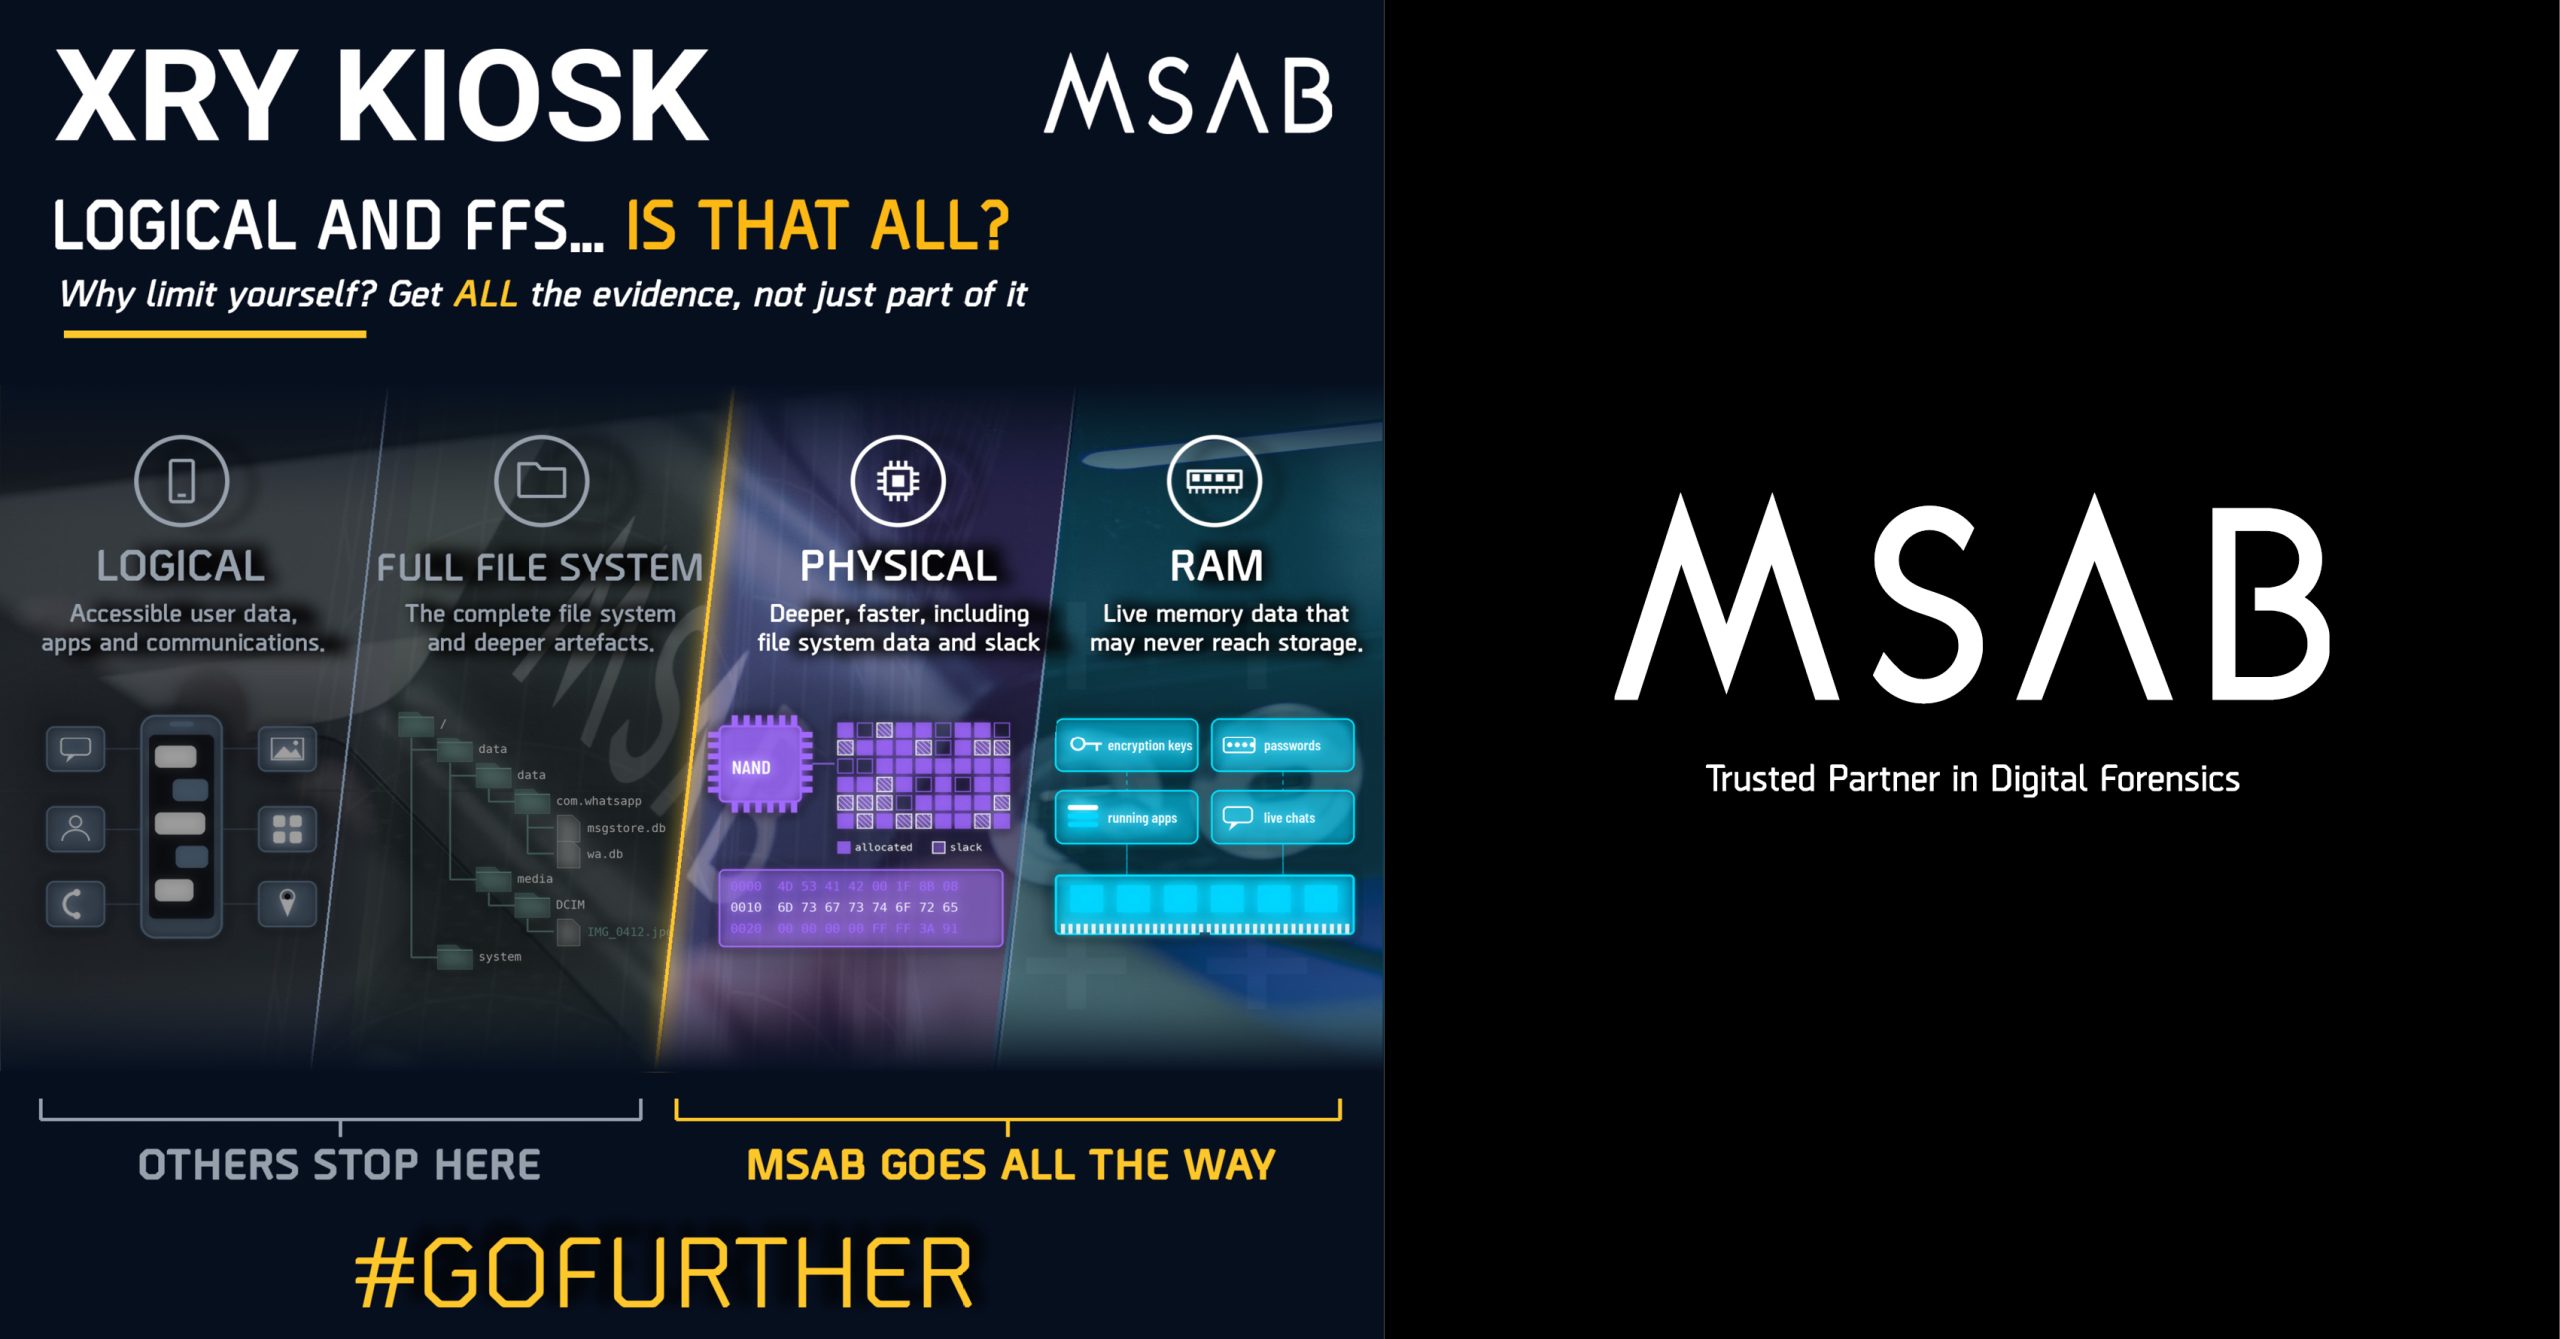
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Passware Kit 2019v4: Instantly Decrypts Symantec EPE & Is Faster For VeraCrypt

WHAT’S NEW Instant decryption of Symantec Endpoint Encryption disks via live memory analysis Support for additional VeraCrypt encryption algorithms Optimized password recovery for TrueCrypt/VeraCrypt Support for EnCase EX01 image files format Export and import of dictionaries Saving MS Office encryption

Investigating Kik Messenger In Oxygen Forensic® Detective

Kik is a free instant messaging app, which works on iPhones, Androids and Kindles. As of May 2016, Kik Messenger had approximately 300 million registered users, and was used by approximately 40% of United States teenagers. Of its 15 million

Now Released: XRY 8.1, XAMN 4.4 and XEC 5.2

With significant advances in extraction and decoding speeds, first-to-market support for the official iOS 13 release, new mobile app extraction capabilities and much more. Today’s release of new versions of XRY, XAMN and XEC gives mobile forensic examiners, investigators and

Forensic Focus Forum Round-Up

Welcome to this month’s round-up of recent posts to the Forensic Focus forums. Forum members help a student with ISO 17025 data sets. Why do some files have Last Accessed metadata, but no other metadata? Can you explain why a

What’s Happening In Forensics – Sep 26, 2019

Andrea Fortuna talks about analysing Windows recycle bin artifacts. Cerbero release Cerbero Suite 3.4. Lenny Zeltzer discusses malware analysis on the SANS blog. Cellebrite’s Joanna Shemesh talks about how their tools solve encryption challenges on Apple and Android devices.

Brett Shavers: I Took Belkasoft Evidence Center For A Spin Around the Block

Brett Shavers from DFIR.training reviewed Belkasoft Evidence Center (BEC). The review was dedicated to the latest version of BEC as an all-in-one digital forensic solution, which supports mobile and computer forensics as well as memory, cloud, and remote investigations. Among

Kathy Helenek, Senior Forensic Examiner, Gillware

Kathy, you're a Senior Forensic Examiner and eDiscovery Specialist at Gillware. Tell us more about your role – what does a typical day look like for you? Each day I’m interacting with clients, whether it be scoping for a new

What’s New In BlackBag’s Latest Release Of BlackLight 2019 R2

BlackLight 2019 R2 is packed full of powerful features you need to complete your investigations more quickly. This release includes new methods to find and export data how and where you need it. From partnerships to connect BlackLight with other

Interview With Guillermo Román Ferrero, Incident Response Expert

Guillermo, how did you become interested in digital forensics? I started studying digital forensics when I was still at university with a specific course on the matter. I found it very interesting to be able to investigate what an attacker

Guillermo Román Ferrero, Incident Response Expert

Guillermo Román Ferrero works as an Incident Response Expert for a Computer Security Incident Response Team. He is also a prolific author with his Follow the White Rabbit blog. Mr. Ferrero tried Belkasoft's digital forensics solutions recently and kindly agreed

What’s Happening In Forensics – Sep 23, 2019

Antonio Sanz provides a writeup of Defcon DFIR CTF: Memory Forensics. Salt4n6 talks about the forensic implications of Swipe to Type. Devon Ackerman reports how 281 people have been arrested for their participation in Business Email Compromise schemes. Cellebrite’s Shahar