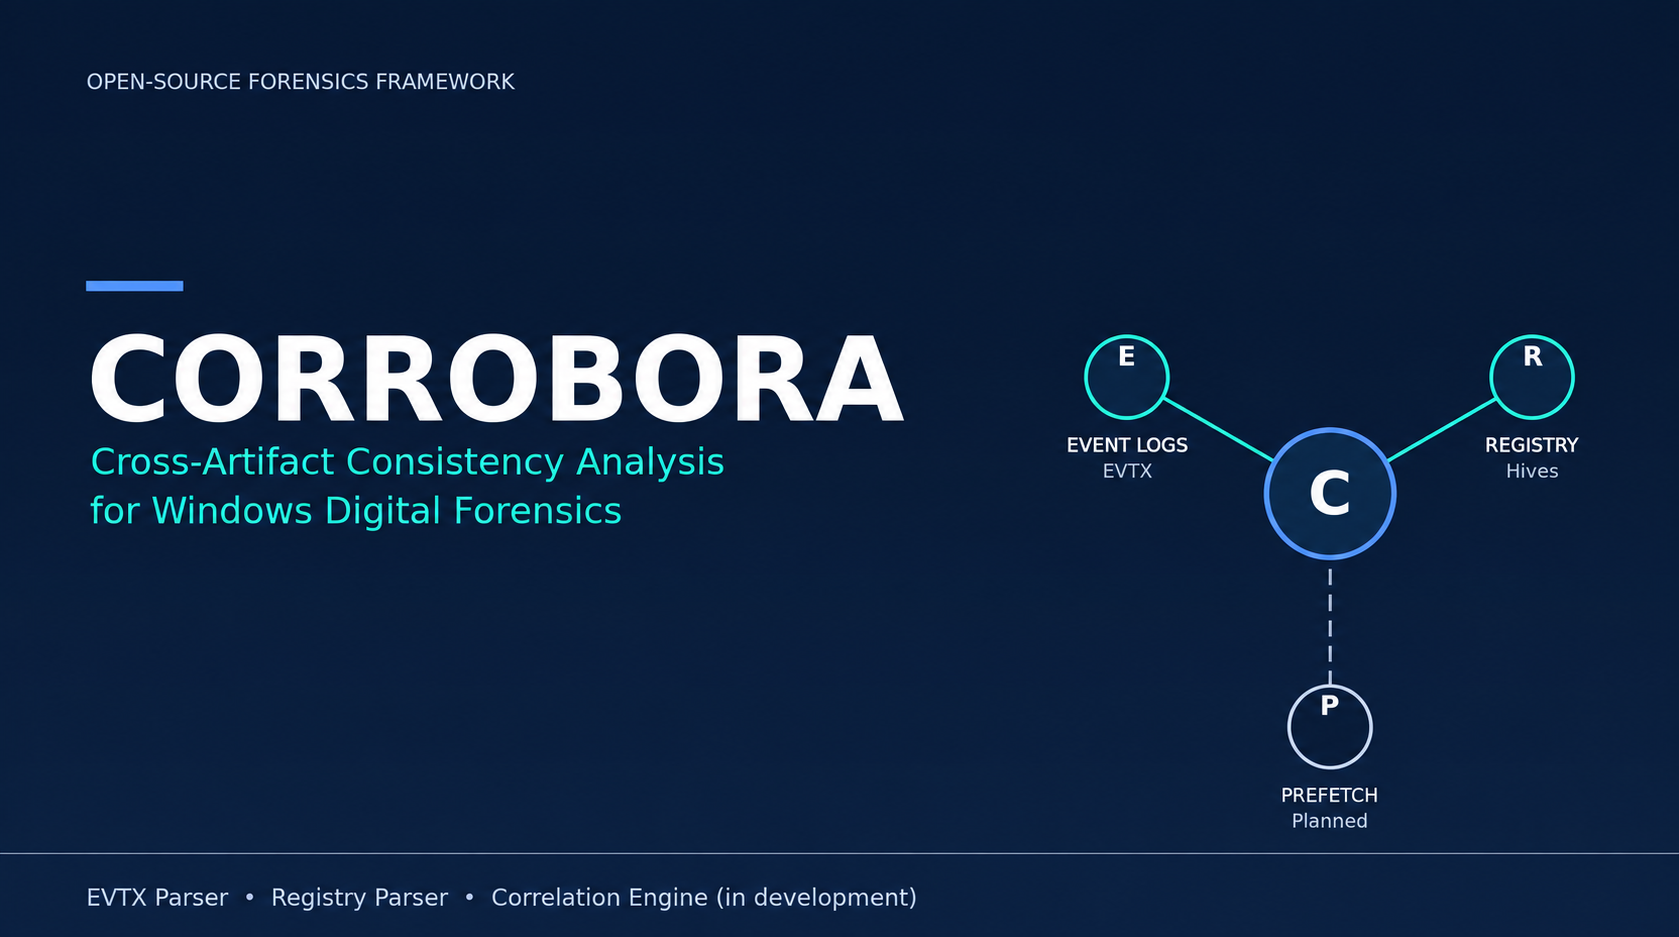
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

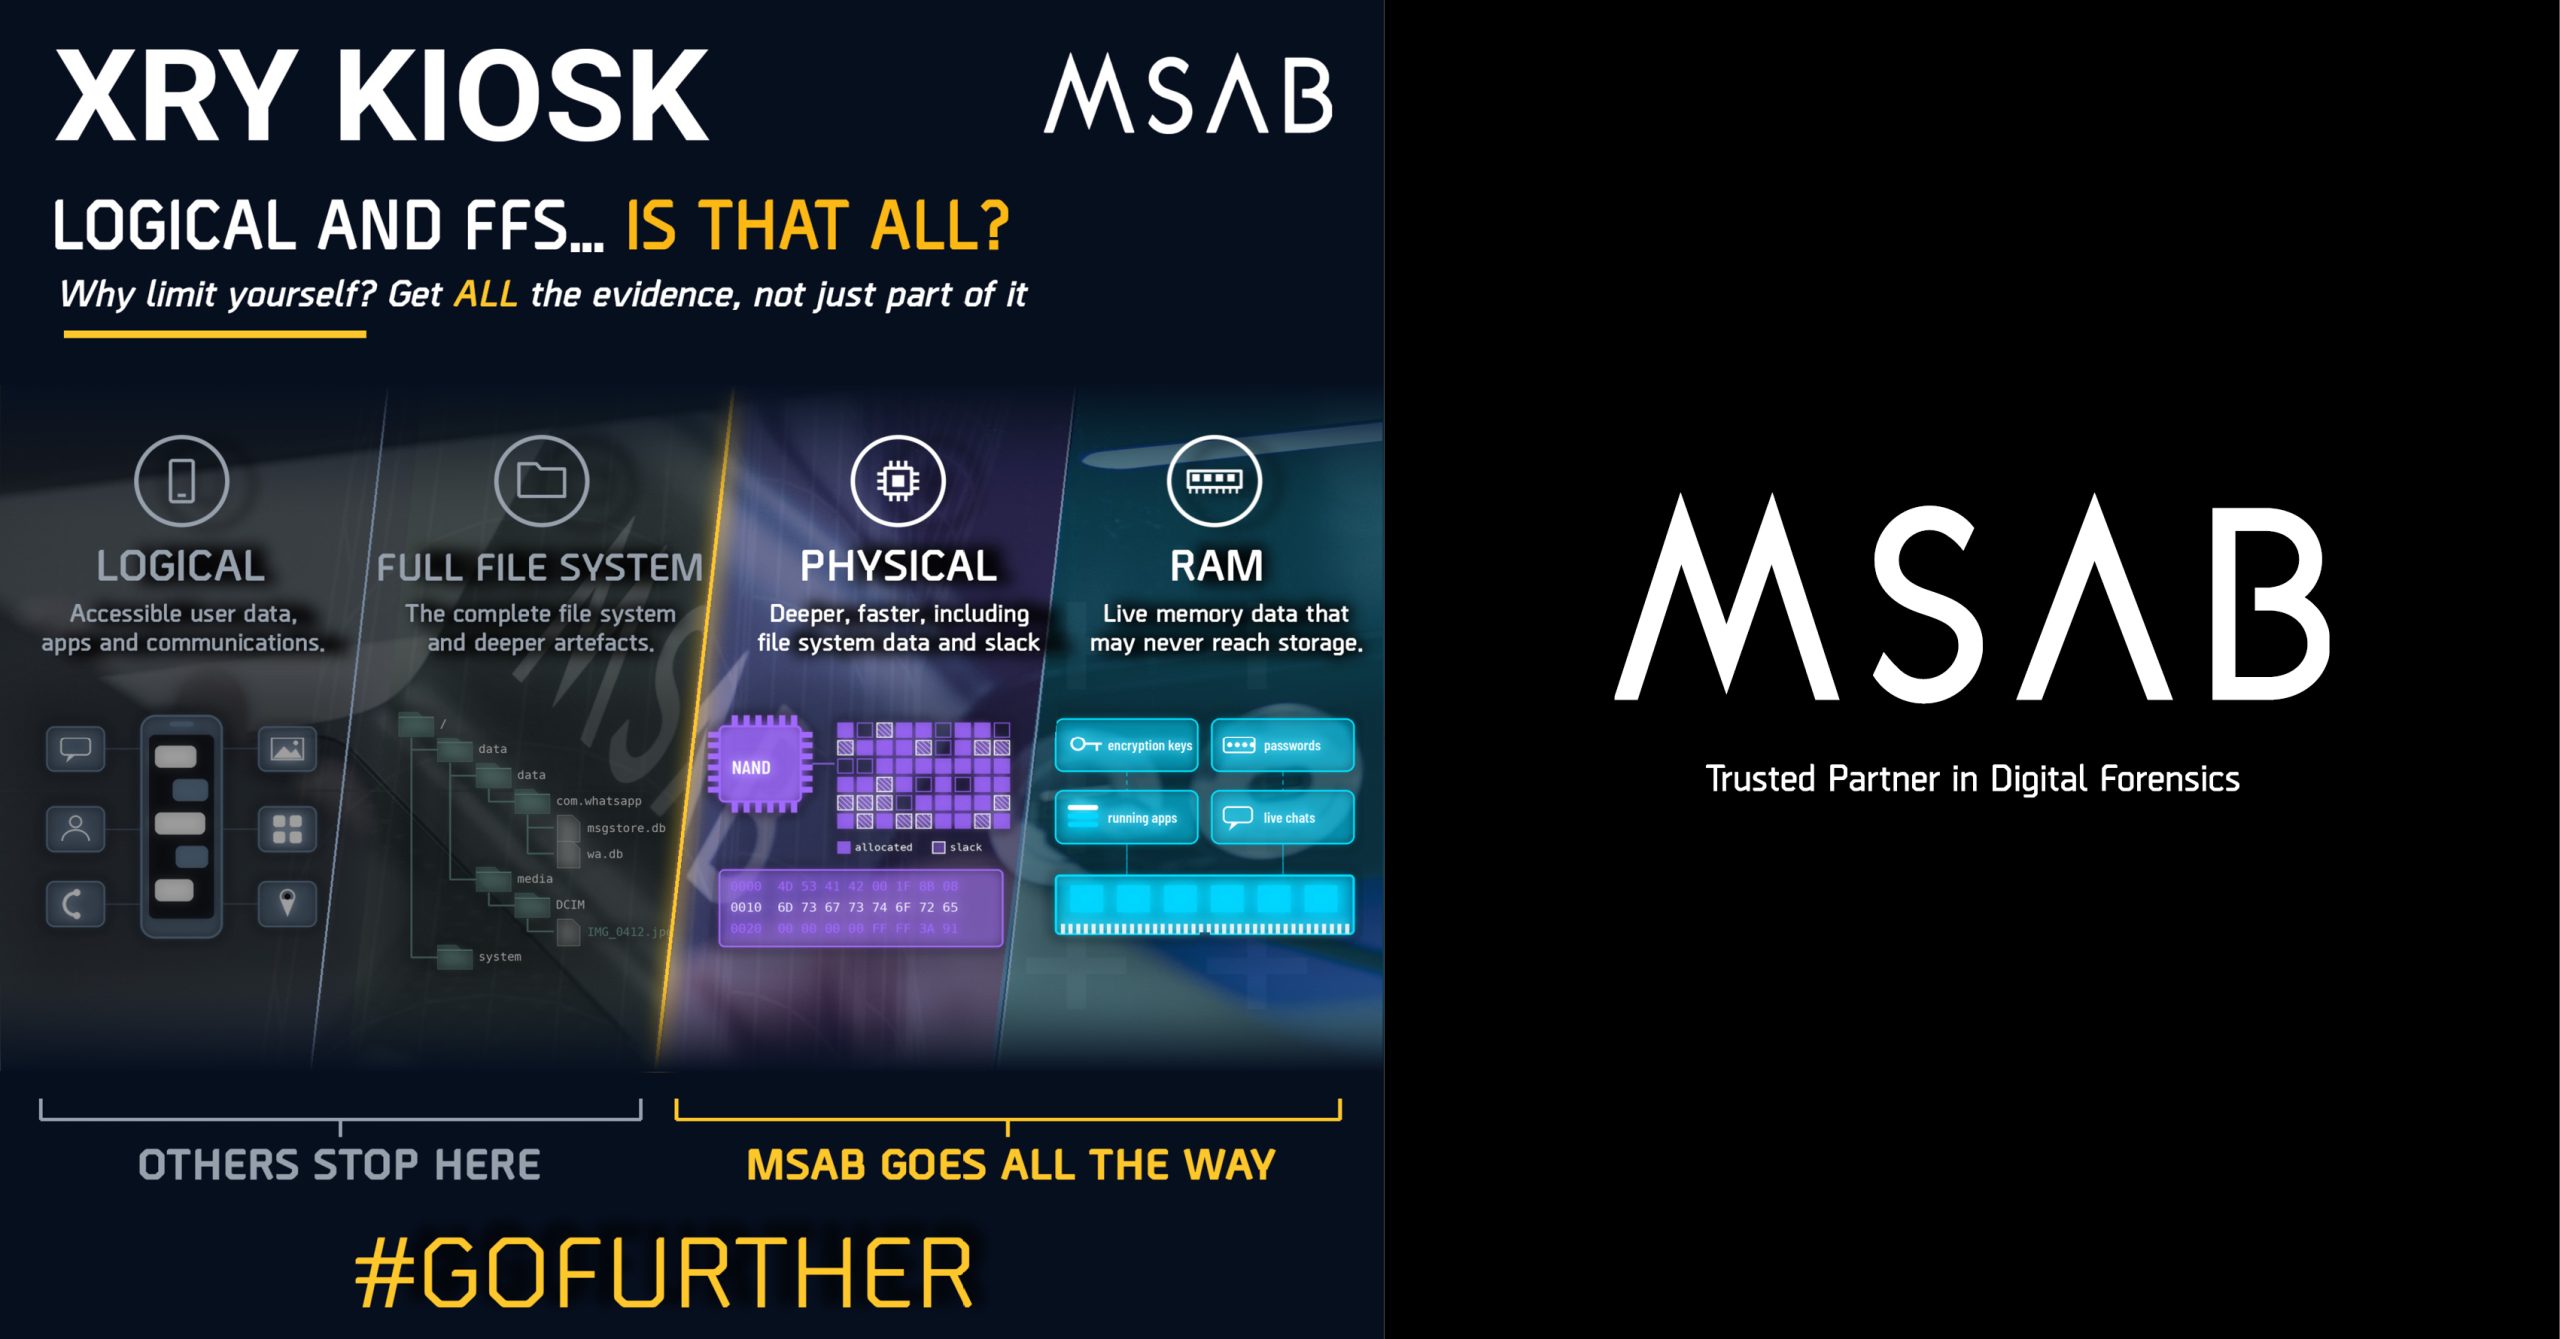
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Dealing With Teen Apps In Digital Forensics

Join the forum discussion here. View the webinar on YouTube here. Read a full transcript of the webinar here.Welcome to Paraben’s webinar on smartphone evidence, [teens] and their apps that they use. I’m Amber Schroader at Paraben Corporation and I’m

Griffeye x BlueBear – A Partnership Driven By Our User Community

Integrating BlueBear’s LACE carver into the Griffeye Analyze platform puts a great solution in the hands of users. It also shows the value of working together to solve problems and being guided all the way by what our users tell

Forensic Analysis Of The μTorrent Peer-to-Peer Client In Windows

by Michael R. Godfrey The μTorrent software client is the most popular BitTorrent peer-to-peer software application worldwide. Contraband files such as copyrighted movies and music, child pornography and pirated content, are frequently acquired through the peer-to-peer (P2P) file sharing protocol

Forensic Analysis Of The μTorrent Peer-to-Peer Client In Windows

by Michael R. Godfrey The μTorrent software client is the most popular BitTorrent peer-to-peer software application worldwide [1]. Contraband files such as copyrighted movies and music, child pornography and pirated content, are frequently acquired through the peer-to-peer (P2P) file sharing

Paraben Launches The E3 Platform Version 2.0

Providing a better solution for all types of digital evidence, E3 Platform is a comprehensive digital forensic tool designed to handle more data, effectively and efficiently. The version 2.0 of the E3 Platform has only enhanced these capabilities with key

Nugget: A Digital Forensics Language

Vassil Roussev discusses Christopher Stelly's research at DFRWS EU 2018. One of the long-standing conceptual problems in digital forensics is the dichotomy between the imperative for verifiable and reproducible forensic computations, and the lack of adequate mechanisms to accomplish these

Nugget: A Digital Forensics Language

Vassil Roussev discusses Christopher Stelly’s research at DFRWS EU 2018. Transcript Vassil: Thank you, everyone. We’re behind schedule, so we’ll try to rush through it … maybe you won’t notice the details. And before we start, since we mentioned that

Review Of AXIOM 2.5 From Magnet Forensics

Magnet AXIOM is an all-in-one digital forensics tool that lets examiners analyse evidence from both computer and mobile devices in the same case. Some of the latest features, along with points of comparison with Magnet’s Internet Evidence Finder, are outlined

AXIOM 2.5 From Magnet Forensics

Reviewed by Scar de Courcier Magnet AXIOM is an all-in-one digital forensics tool that lets examiners analyse evidence from both computer and mobile devices in the same case. Some of the latest features, along with points of comparison with Magnet’s

Randy Whitcroft Joins MSAB To Lead Sales In Canada

MSAB today announced the appointment of Randy Whitcroft to lead its sales efforts in Canada. “I am excited to represent MSAB in Canada. My role will be to help current and future MSAB customers improve their mobile forensic operations and

AccessData Strengthens Worldwide Team With Three New Hires

AccessData Group today announced that three industry veterans have joined the company in various client services leadership positions to assist customers in both the public and private sectors. “We pride ourselves on being able to deliver what our clients need.

Add Increased Pincode/Passcode Breaking Capabilities To Your Lab

Susteen is proud to announce that our Burner Breaker pincode/passcode/pattern breaking system, which achieved Popular Science’s “Best of What’s New” award in the category of Innovations in Security now includes our cutting edge field acquisition device. The Burner Breaker continues

Digital Forensics News October 2018

It’s the last week of submissions for the DFRWS EU 2019 call for papers. The Passware Kit Forensic tool from Passware has introduced the ability to recover Bitcoin wallet passwords. A post on Initialization Vectors demonstrates how to perform digital

Mobilyze 2018 R2 Now Available

BlackBag Technologies is proud to release Mobilyze 2018 R2 with additional iOS and Android support. Mobilyze makes triaging mobile devices easy with an interface that lets you go straight from acquisition to a well-formatted report. Sometimes small adjustments need to

Forensic Focus Forum Round-Up

Welcome to this month’s round-up of recent posts to the Forensic Focus forums. What is anti-forensics, how can we prove its relevance to an investigation, and how much of a challenge is it to the industry? Add your thoughts in