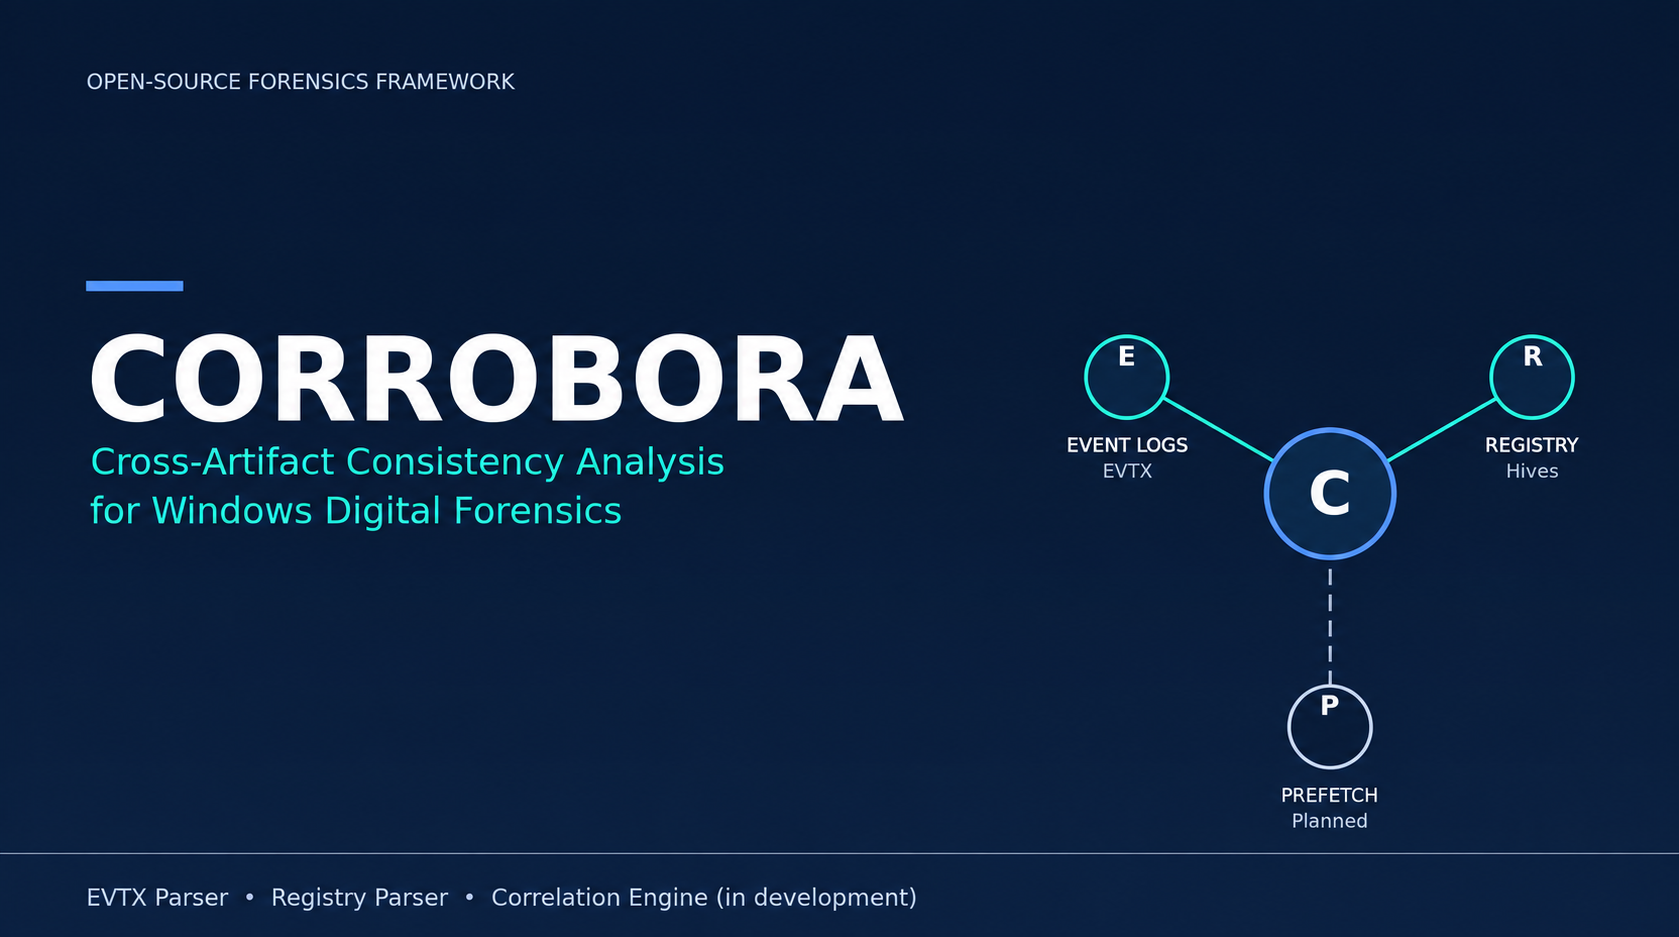
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

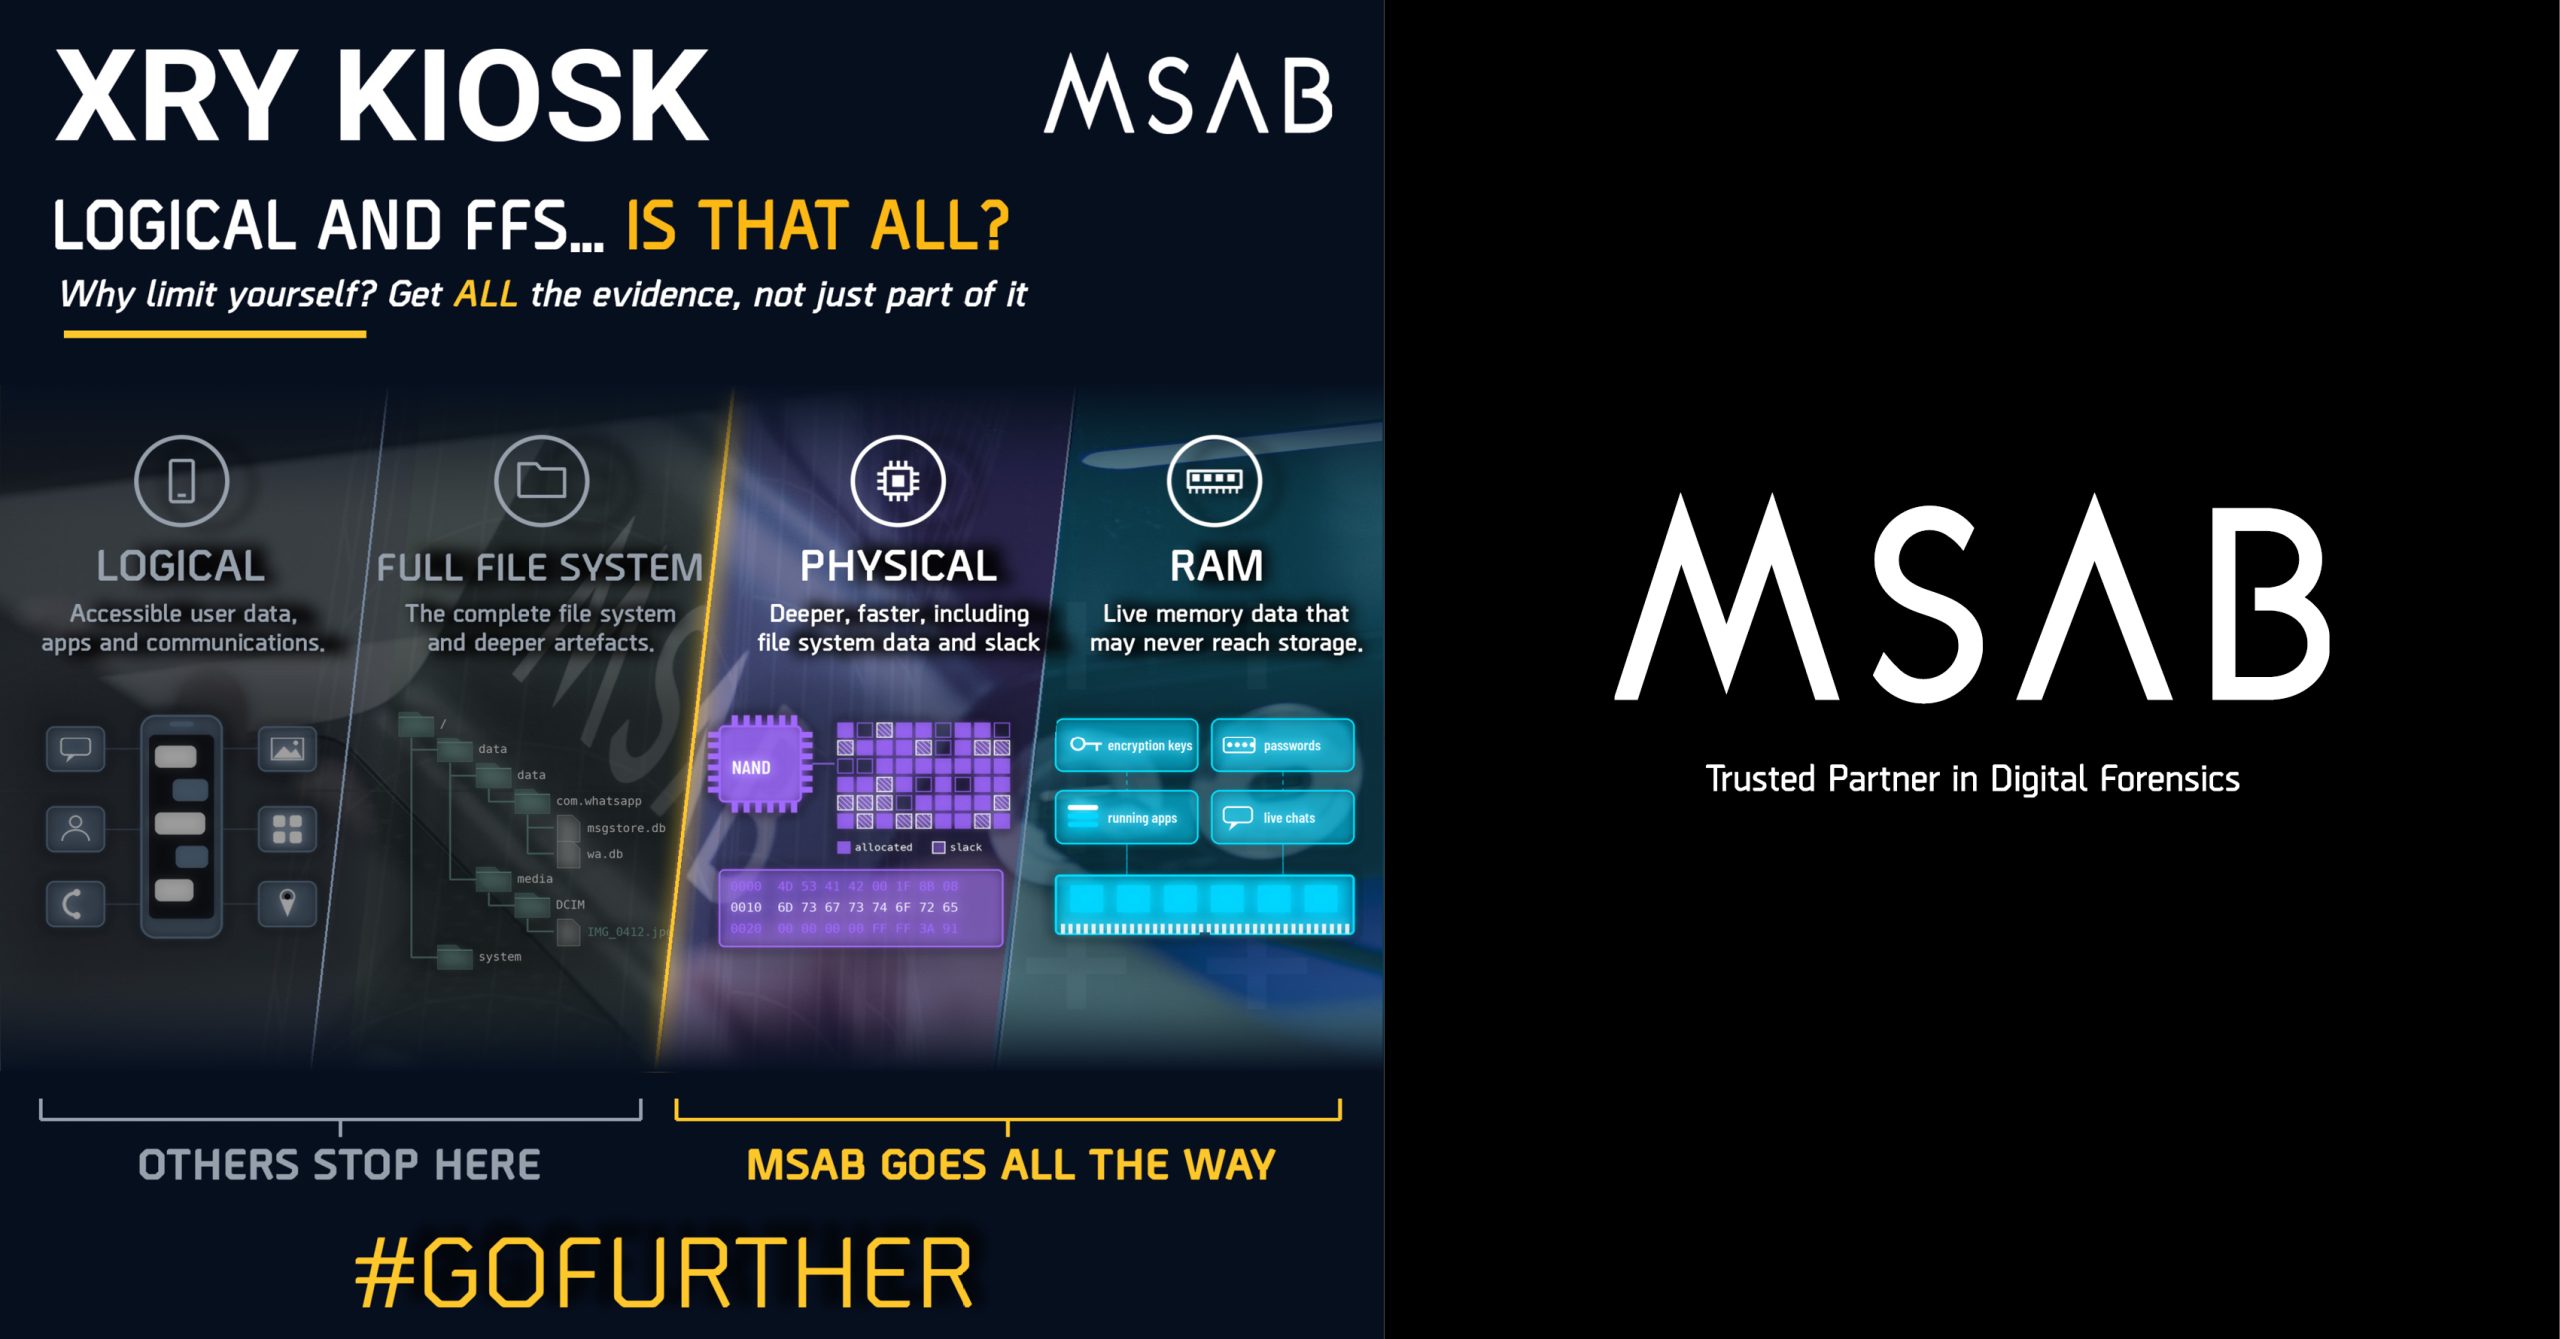
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

5 Steps to Ensure Your Cloud Provider Is Ready for Ediscovery

Identifying, retrieving, and producing electronically stored information (ESI) in response to a subpoena can be a time-consuming and costly business. Processing just one gigabyte of data in response to an electronic discovery (ediscovery) request can cost at least $30,000, according

Cyber forensics to the fore

The goal of computer forensics is to examine digital media in a forensically sound manner with the aim of identifying, preserving, recovering, analysing and presenting facts and opinions about the information. Most often associated with the investigation of a wide

Fighting crime in the computer age

Technology is changing at a dizzying pace, and law enforcement officers are having trouble keeping up. New smartphones are being released constantly. Tablets like the iPad are replacing laptop computers. Almost everybody – including those who break the law –

XRY v6.3.2 released

Micro Systemation just released XRY v6.3.2 This version includes: – The ability to bypass a complex passcode on some iOS devices– Full support for the new Apple operating system iOS6– A new RAM disk extraction method for iOS devices– Logical

Philip Anderson, Northumbria University

Philip, can you tell us something about your background and why you decided to teach digital forensics? I graduated from Northumbria University with a BSc (Hons) in Business Information Technology in 1997 and gained an MSc in Distance Education with

Android Forensics

Smartphones are changing the IT and Communication landscape vastly.  A Smartphone can do almost every good thing a computer can do. Today most of the corporate employee access and manage their official emails through the e-mail client installed on their

Collecting and Processing Bloomberg Data

A few years ago, Bloomberg data may have been relatively unusual, however today we see Bloomberg chat and email data being collected quite frequently. Not a surprise really considering some of the headlines relating to certain Banks and Financial institutions

IEF Adds Webpage Re-building and Support for iOS Backups in Latest Upgrade

With a strong commitment to helping thousands of its customers in the world’s top law enforcement, military, government and corporate organizations retrieve Internet-related communications from a broad range of artifacts, Magnet Forensics (formerly JADsoftware) has unveiled v5.6 of its industry-leading

Digital forensics: proactive or reactive?

For a number of years digital forensics has referred to ‘the application of computer investigation and analysis techniques to gather evidence suitable for presentation in a court of law’. While collecting this digital evidence, to be used retrospectively in subsequent

IPOD – Timestamps secrets

ABSTRACT This is a description how the Apple Ipod/Iphone stores the timestamps into their plist files. After an experiment we tried to order the various ways that Apple Idevices manage and store these data. We found the timestamps into PlayCounts.plist

PFIC Registration Open – The Mountains are Calling!

Paraben's Forensic Innovations Conference is being held in Park City, Utah November 3-6. Join us for bootcamps, lectures, and labs from the industry’s top experts and learn the latest innovations in digital forensics. Whether you are just getting started in

Windows 8 Forensics webinar – alternative URL

Sincere apologies to anyone having difficulty connecting to the Meetingburner service to view the Windows 8 Forensics presentation – please try the following URL on YouTube instead: http://youtu.be/uhCooEz9FQs Josh is available in the webinars forum to answer any questions. Please

Webinar: Windows 8 Forensics – last chance to register

There are currently just over 30 places left before we reach our maximum of 1000 attendees for Josh Brunty’s Windows 8 Forensics webinar. Please register now at http://forensicfocus.enterthemeeting.com/m/JXI8IWVX if you wish to attend. Date: TodayTime: 11AM EDT US / 4PM

New Linux Distro for Mobile Security, Malware Analysis, and Forensics

by Jay Turla, a contributor to InfoSec Resources. A new GNU/Linux distribution or distro designed for helping you in every aspect of your mobile forensics, mobile malware analysis, reverse engineering and security testing needs and experience has just been released