Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

How A MacBook With A Broken Screen Helped Convict A UK Property Fraudster: Belkasoft X Case Study

Hero Image

A broken MacBook, an iPhone, and a £113,000 fraud case - discover how Belkasoft X helped uncover crucial digital evidence that brought a UK property fraudster to justice....
Today's headlines 30 Oct 2026

Forensic Focus Digest, 30 Oct 2026

Forensic Focus Digest, 30 Oct 2026

Discover what’s new on Forensic Focus: explore end-to-end digital investigations with Magnet Forensics, meet Matt Goeckel, AI researcher at Cellebrite, learn about the Cellebrite Autumn 2026 Release, and more....read more
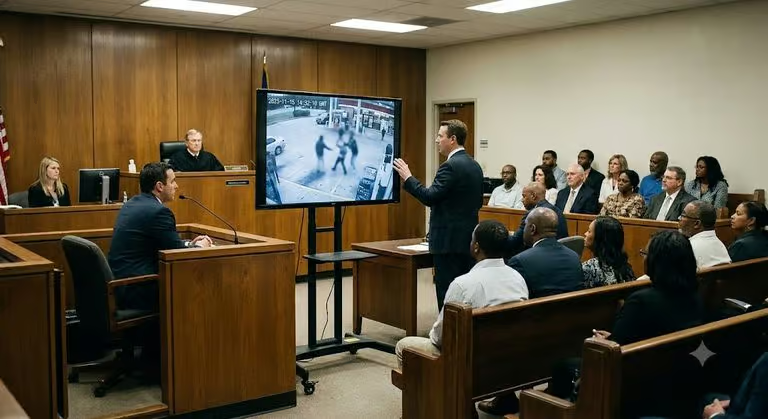
Preparing Digital Multimedia Evidence For Court: What To Consider Before Presentation

Preparing Digital Multimedia Evidence For Court: What To Consider Before Presentation

Effective courtroom presentation starts with careful preparation - discover how Amped Replay helps forensic professionals prepare clear, accurate and properly documented digital multimedia evidence for court....read more
Explore Cellebrite’s Autumn 2026 Release: Discover What’s New

Explore Cellebrite’s Autumn 2026 Release: Discover What’s New

Discover how the Cellebrite Autumn 2026 Release is transforming digital investigations with faster access to evidence, AI-powered insights and seamless collaboration....read more

Forensic Examination of FrostWire version 5

Introduction As digital forensic practitioners, we are faced regularly  with users utilizing the internet to swop and download copyrighted and contraband material. Peer to peer (P2P) applications are commonly used for this purpose, and like any software application, they is

Firefox Forensics

I was showing someone a trick to export Firefox SQLite tables to a spread sheet, and while she is a forensics person, she had never ever heard of this trick. It is neat enough to know when working off an

Retrieving Digital Evidence: Methods, Techniques and Issues

This article describes the various types of digital forensic evidence available on users’ PC and laptop computers, and discusses methods of retrieving such evidence. A recent research conducted by Berkeley scientists concluded that up to 93% of all information never

Authenticating Internet Web Pages as Evidence: a New Approach

By John Patzakis [1] and Brent Botta [2] Previously, in Forensic Focus, we addressed the issue of evidentiary authentication of social media data (see previous entries here and here). General Internet site data available through standard web browsing, instead of

Parallels hard drive image converting for analysis

The other day, talking to one of the analysts in Dallas, a question emerged about analyzing Parallels’ virtual machine hard drives. To my surprise, I did not find many help on this issue on-line and did not find tools that

Retrieving Digital Evidence: Methods, Techniques and Issues

by Yuri Gubanov [email protected] Belkasoft Ltd. http://belkasoft.com Abstract This article describes the various types of digital forensic evidence available on users’ PC and laptop computers, and discusses methods of retrieving such evidence. Download article in PDF format Introduction A recent 

A Quick Look at Exchange Forensics

A growing number of enterprises—and their IT staffs—are becoming increasingly concerned about the range of threats posed by electronic attack. Couple that with the high incidence of business litigation, and the high regulatory barriers, present in the US and EU,

Computer crime given low priority by Irish firms

Irish firms are failing to treat the threat of computer crime as seriously as they should, a new survey has revealed, with a lack of funding in information security and insufficient employee awareness of threats identified. According to the survey

Belkasoft releases Evidence Center v4.1 featuring deeper EnCase integration

Belkasoft releases Belkasoft Evidence Center 2012 version 4.1 featuring deeper EnCase v7 integration and more than 210 supported artifact types. The company’s flagship forensic tool, Belkasoft Evidence Center, now supports new EnCase v7 EX01 evidence files as well as E01,

Interview with John H. Riley, Bloomsburg University of Pennsylvania

John, can you tell us something about your background and why you decided to teach digital forensics? First, thanks for the opportunity to discuss our program. We’re really proud of what we’ve accomplished here and believe we’re contributing to the

Parallels hard drive image converting for analysis

Abstract The other day, talking to one of the analysts in Dallas, a question emerged about analyzing Parallels’ virtual machine hard drives.  To my surprise, I did not find many help on this issue on-line and did not find tools