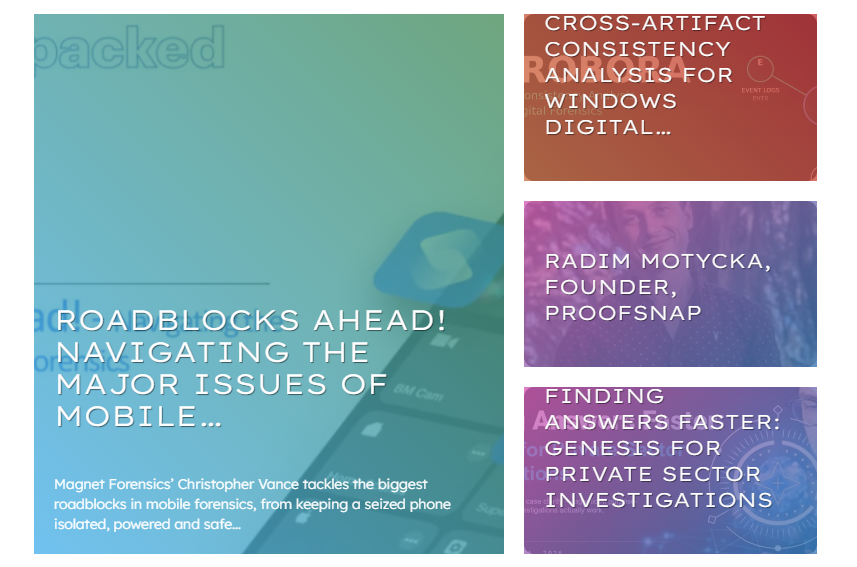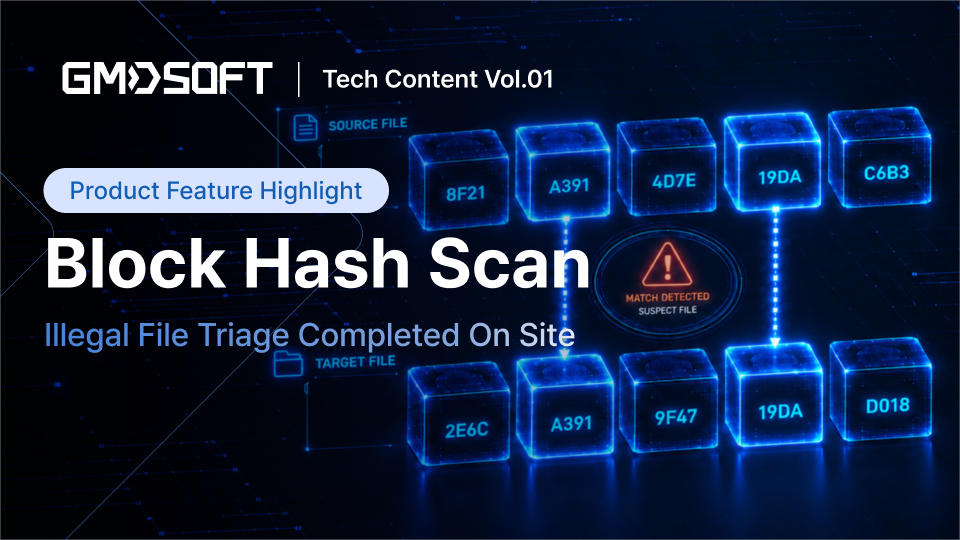
Block Hash Scan: Illegal File Triage Completed On Site

Hero Image

See how MD-LIVE’s Block Hash Scan helps investigators identify known target files on-site without reading every file in full, and what a zero-detection result really means....

Today's headlines 2 Oct 2026

Forensic Focus Digest, October 02 2026

Forensic Focus Digest, October 02 2026

Discover what’s new on Forensic Focus – explore the biggest challenges in mobile forensics with Magnet Forensics, discover faster investigative workflows with Cellebrite Genesis, meet Radim Motycka, founder of Proofsnap, and more....read more
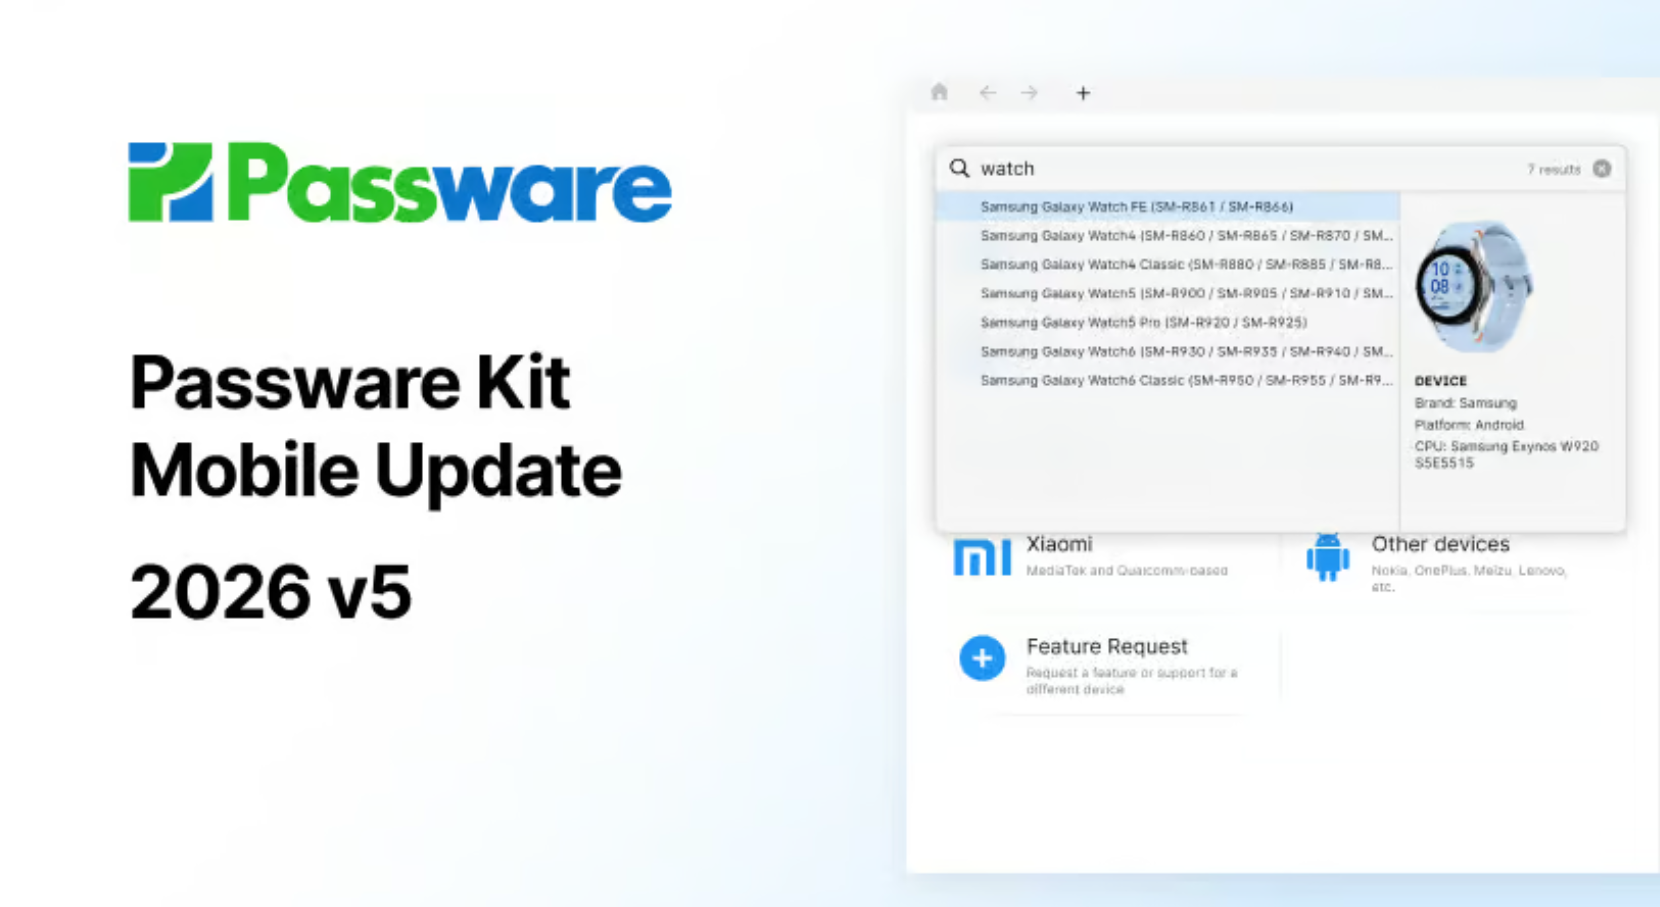
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 expands mobile forensics with Samsung Galaxy Watch 4/5/6 passcode recovery and data extraction, new Samsung and Unisoc device support, Enpass for Android decryption, and faster workflows with immediate passcode recovery....read more
Trust Is Not A Feature. It Is The Foundation.

Trust Is Not A Feature. It Is The Foundation.

Discover what agencies should expect from a digital forensics partner and how MSAB puts transparency, accountability and long-term commitment at the heart of its work....read more

NYU-Poly CSAW High School Forensics Competition

High School Cyber Forensics Challengehttp://www.poly.edu/csaw2011/csaw-forensicsPolytechnic Institute of New York UniversityRegistration is now OPENChallenge Begins: Wednesday September 21, 2011Challenge Submission Deadline: Monday October 24, 2011 @ 5:00PM ESTFinalists announced: Friday, October 28, 2011Finals in NYC: Thursday November 10-11, 2011Tonight, the cast

Integreon Announces Enhanced Seek & Collect v2.0 E-discovery Appliances

Integreon today announced an enhanced version of its Seek & Collect service and appliances. Seek & Collect efficiently captures electronically stored information (ESI) from remote locations in a forensically sound manner without the need for physical collection by forensic experts.

Paraben Device Seizure v4.5 Released

Paraben has released Device Seizure v4.5. This new version adds support for new models including the latest versions of iOS and Android phones. What’s New: * Added support for iOS 4.3.3 and 4.3.5 * Added support for 35 new phones

Google History Forensics

by Craig Ball In my last Forensic Focus column, I touched on migration to handhelds and the cloud, mushrooming drive capacities and encryption-by-default as just some of the factors auguring the eventual extinction of conventional digital forensics. But an end

Time and Forensics

by Simon Biles Time fascinates me, it has an amazing history and it has some great “toys”. One of my favourite quotes of all time is from Groucho Marx: “Time flies like an arrow, fruit flies like a banana.” I

Belkasoft Evidence Center 3.0

Belkasoft announces a major upgrade to its flagship forensic product, Belkasoft Evidence Center. The new version 3.0 adds picture and video support, enabling forensic investigators to run automated searches for images and video footage containing people’s faces or pornographic content.

Thomas Cannon and Jonathan Zdziarski join viaForensics

viaForensics, a firm providing expert services and products for mobile security and forensics, has announced that it has named US iPhone expert Jonathan Zdziarski and UK Android expert Thomas Cannon to its research and development arm. Both researchers are respected

Digital forensics: The inside story

Jelle Niemantsverdriet is the Principal Consultant, Forensics and Investigative Response EMEA, Verizon Business Security Solutions. In this interview he introduces the reader to the world of digital forensics and talks about computer forensics tools, privacy concerns, the fundamental differences in

Obtaining Information from Mobile Devices in Criminal Investigations

by David W. Bennett "Mobile device forensics has expanded significantly over the past few years. Older model mobile phones could store a limited amount of data that could be easily obtained by the forensics investigator. With the development of the

The cold boot attack: Can it be used for forensic memory acquisition?

by Richard Carbone "The purpose of this technical memorandum is to examine the technical characteristics behind the cold boot attack technique and to understand when and how this technique should be applied to the field of computer forensic investigations. Upon

DFCB Announces September 2nd Application Deadline for DFCP Designation

The Digital Forensics Certification Board (DFCB), an independent certifications organization for digital evidence examiners, today announced that its next application deadline for its Digital Forensics Certified Practitioner (DFCP) designation is September 2, 2011. The DFCB currently accepts applications four times

Mobile Forensics Training Session by viaForensics

viaForensics will hold five mobile forensics training sessions covering Linux use in forensics, iPhone forensics, Android forensics, advanced mobile forensics, and advanced file carving. The sessions will be held at the Peel Police Department in Mississauga, Ontario, October 3-7, 2011.

Jeffrey “Skunk” Baxter Announced as PFIC 2011 Keynote Speaker

PFIC – Paraben’s Forensic Innovation Conference – is pleased to have Jeffrey “Skunk” Baxter as our keynote this year. Not only is he one of the world’s leading guitarists, but he is one of the top innovators in the world

Google History Forensics

by Craig Ball "In my last Forensic Focus column, I touched on migration to handhelds and the cloud, mushrooming drive capacities and encryption-by-default as just some of the factors auguring the eventual extinction of conventional digital forensics. But an end