A round-up of today’s digital forensics news and views:
Forensic Focus News
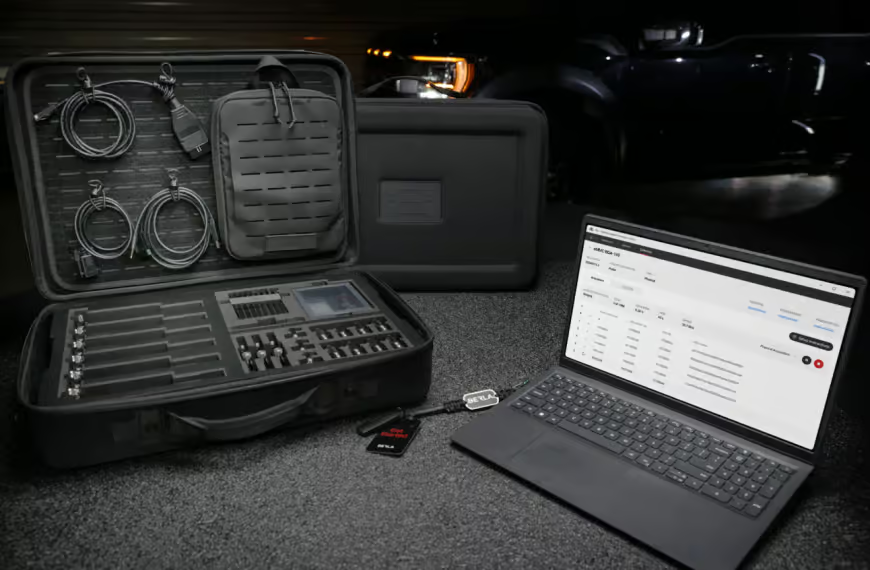
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch
Passware Kit Mobile 2026 v5 recovers passcodes and extracts data from 24 Samsung Galaxy Watch 4, 5, and 6 models by exploiting a vulnerability in the Exynos W920 and W930 SoCs, requiring physical connection to USB test pads on the board. Support also extends to five Exynos 1280-based Galaxy handsets, 19 Unisoc T760/T770/T820 devices, and Enpass for Android password extraction. Recovery on a single NVIDIA GeForce RTX 4070 Ti exceeds 14,500 passwords per second across multiple device families.
Trust Is Not A Feature. It Is The Foundation.
Transparency in ownership, development location and governance are foundational criteria agencies should apply when selecting a digital forensics partner. MSAB, listed on Nasdaq Stockholm and developing its technology in Sweden, serves law enforcement, defense and government clients in over 100 countries exclusively. The company is offering direct support to agencies needing to transition tools quickly amid recent industry disruption.
Research & Techniques
Field Notes: Reconstructing Attacker LSASS Dumps
A practitioner field note documents TrickDump, a technique used to dump LSASS memory for credential theft, observed during a real-world engagement. Investigators reconstructed the attacker’s dump process, providing methodology and artifacts directly applicable to similar incident response cases.
Industry News
Android Advanced Protection Adds Forensic Logging Feature
Google has introduced Intrusion Logging to Android’s Advanced Protection suite, a mobile-industry first that stores end-to-end encrypted security and network events in the cloud for up to 12 months, enabling forensic investigation of suspected device compromises. Additional features include USB Protection against juice-jacking and hardware attacks, Accessibility Protection restricting API abuse, and Failed Authentication Lock to counter brute-force attempts on seized devices.
Tools & Software
MFTGuard Detects NTFS Timestomping via MFT Analysis
MFTGuard, a new open-source DFIR tool written in C, parses the entire Master File Table to detect timestomping attacks using rule-based logic. Released as its first stable version, it flags potential NTFS timestamp manipulation and outputs results in JSON format.
Case Studies
Mobile Forensics Cross-Examination Lessons from Gatlin Case
A forensic analysis of the Ahmed Gatlin case examines how mobile phone evidence, cloud storage, and app-specific location permissions were challenged during cross-examination. Gaps in phone activity data do not independently confirm whether a device was off, idle, or simply not logging, a distinction courts increasingly scrutinize. Expert witnesses should bring reports to court and understand the legal basis for device access before testifying.
Training & Events
Free Narcos DFIR Training Dataset on Digital Corpora
A realistic forensic training scenario called Narcos, built in 2019 at WelTec, is freely available on Digital Corpora for anyone learning or teaching digital forensics. Practitioners can download disk images and memory dumps from three Windows 10 machines, simulating a Customs investigation into drug smuggling. The project site has been refreshed and explains both the case scenario and its construction methodology.
Read more (dfirsleuths.github.io)
Course Adds DJI Flight Log XOR Obfuscation Analysis
An updated drone forensics course now covers XOR obfuscation techniques found in early DJI aircraft flight logs, teaching examiners how record-specific keys derived from log data are used to encode payloads. Students learn to decode binary structures, validate tool output, and interpret artifacts that commercial software may not support, building a defensible forensic methodology for UAS evidence.