A round-up of today’s digital forensics news and views:
Forensic Focus News
Semantics 21’s CCTV Review Tool Is Built For Footage That Cannot Wait
S21 CCTV, from Semantics 21, provides frontline and specialist investigators with an offline workflow covering video review, enhancement, redaction, and reporting in a single environment. Designed for time-critical cases, it aims to reduce the friction between captured footage and usable evidence without requiring complex setup or switching between tools.
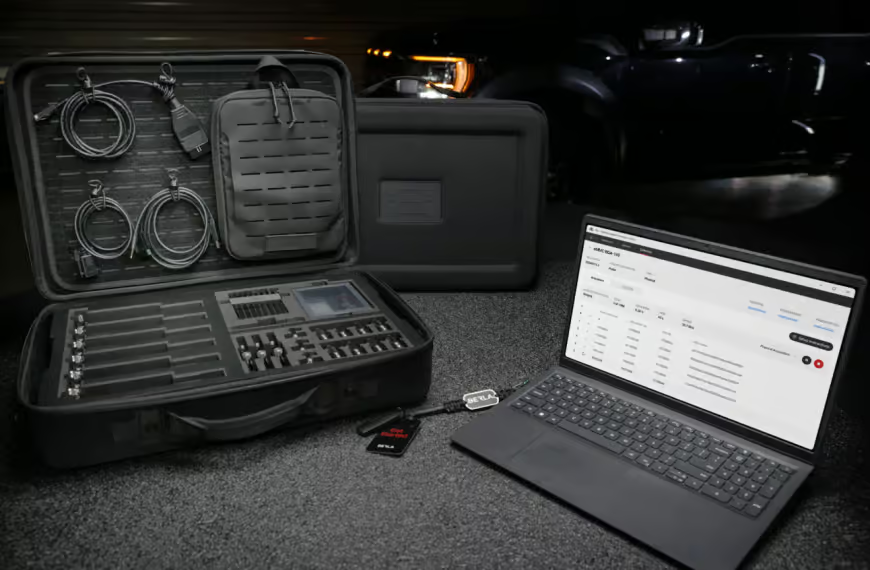
Berla Introduces iVe 5.0, Adding Support For More Than 38,500 Additional Vehicles
Berla Corporation has released iVe Generation 5, expanding vehicle forensics coverage to more than 38,500 additional vehicles globally and adding support for 388 infotainment and telematics systems. New modular hardware, including a non-destructive Probe Kit, gives investigators flexible lab and field deployment options. A new Collection Manager consolidates acquisition profiles, connection testing, and collection controls into a single workflow.
Tools & Software
AI Forensic Hackathon Yields Open-Source SIFT Tools
A SANS Institute hackathon challenged 4,413 entrants to build autonomous agents capable of working real forensic cases without fabricating evidence, with 90 practicing incident responders stress-testing finalists using tampering, path traversal, and command injection scenarios. Five winning open-source harnesses emerged, including Mulder and TRUDI, both now integrated into the SIFT Workstation.
Research & Techniques
Console-Pipe Injection Evades Classic EDR Detection
Console-pipe injection uses redirected stdin on benign child processes like nslookup.exe to write shellcode without VirtualAllocEx or WriteProcessMemory, bypassing EDR detections that rely on the classic allocation-write pair. Defenders should validate whether their stack correlates remote VirtualProtectEx calls on console children with subsequent thread-context redirects into newly executable pages. The forensic signal lies in the parent-child-protect-hijack sequence, not the utility names involved.
Steam VR Chaperone Data Reveals User Height
Chaperone boundary data stored in Steam VR frames can be analysed to extrapolate a user’s physical height, presenting a previously undocumented forensic artifact. This technique could support user attribution in investigations involving VR-capable devices, though further testing is noted as ongoing.
Training & Events
13Cubed Linux Forensics Course Reviewed
A new review of 13Cubed’s $895 Investigating Linux Devices course highlights its hands-on coverage of Linux logs, file systems, persistence, live response, disk analysis and memory forensics using open-source tools. The practical, open-book certification exam was passed on the first attempt with a 94/100 score, with the course described as particularly useful for SOC analysts seeking stronger Linux forensics skills.