Belkasoft X 2.12 advances several areas that continue to shape the product: AI-assisted investigations, access to more evidence through acquisition and artifact extraction, and secure, practical workflows for forensic labs and corporate investigation teams.
Key updates include offline evidence translation and SQLite database classification through BelkaGPT, along with redesigned Android acquisition workflows and broader artifact support across Android, iOS, and Windows. The release also strengthens offline operation with the Belkasoft Offline Map Server and BelkaGPT Hub, helping laboratories keep both geolocation analysis and AI-assisted processing within their own infrastructure.
Offline Evidence Translation
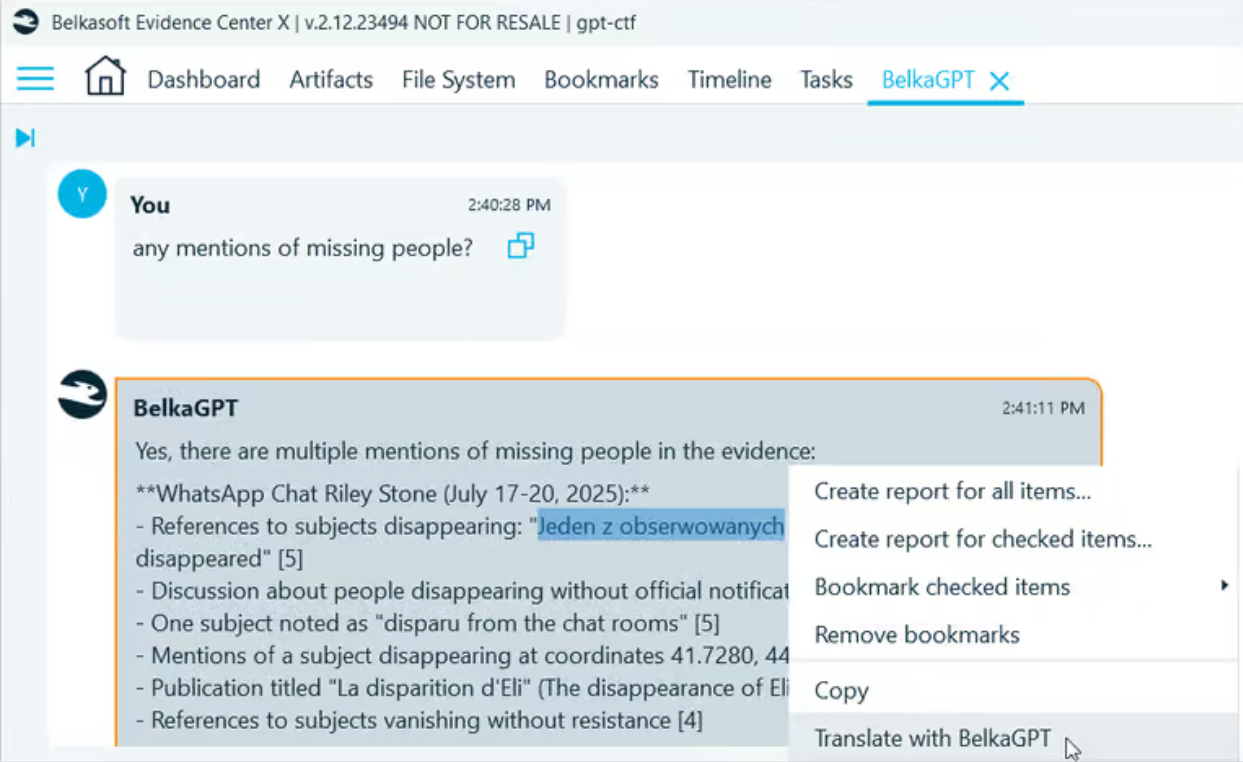
Foreign-language evidence slows investigations down. Online translation services are not an option for sensitive case data. Belkasoft X v2.12 solves both problems with offline evidence translation through BelkaGPT. All processing runs locally, so evidence stays inside the forensic environment.
BelkaGPT detects the source language automatically. It translates from more than 200 languages and dialects into over 100 target languages. You can translate a single chat message, a full conversation, or thousands of messages at once. Translated messages are searchable and can go straight into reports. BelkaGPT can also translate text from any other artifact without leaving the review workflow.
Belkasoft published a detailed preview of the feature on Forensic Focus ahead of the release.
Making Sense of Unsupported Applications
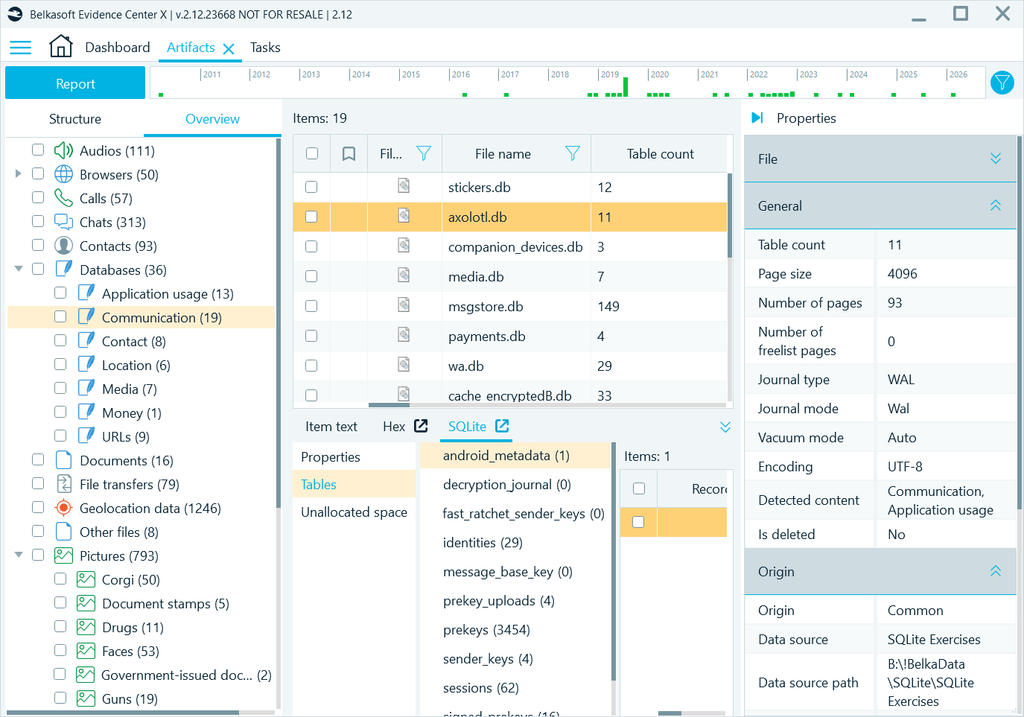
Many applications store data in SQLite databases that forensic tools do not parse automatically. A single data source can contain hundreds of such databases, and examiners often have no quick way to tell which ones matter. Version 2.12 helps with both tasks: deciding which databases to examine and turning their contents into evidence.
You can now use BelkaGPT to classify SQLite databases by content. BelkaGPT sorts the databases into categories such as communications, locations, financial information, credentials, and other predefined classes. You can also create custom categories to identify the databases with data of the most interest for a particular case. Instead of opening every unknown database by hand, they can start with the databases most likely to matter.
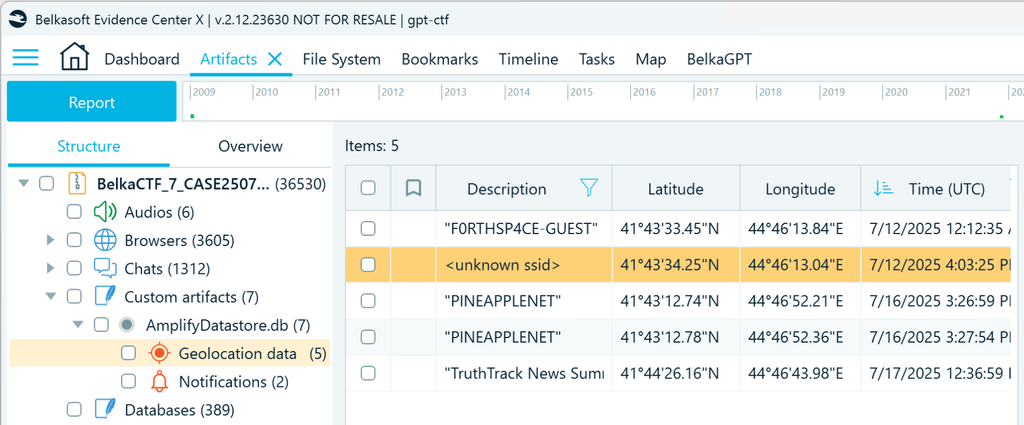
Once investigators find a relevant database, custom SQLite artifacts let them map its tables and columns to standard Belkasoft X artifact fields. These fields include timestamps, participants, message text, and geolocation. The mapped data then works like any other artifact in Belkasoft X: investigators can search, filter, and include it in reports.
“SQLite is everywhere in digital investigations—mobile apps, desktop applications, and countless tools that are not yet covered by automatic artifact extraction all rely on it to store data. With version 2.12, we brought together two complementary approaches to SQLite forensics: use AI to help investigators identify which databases are most likely to matter, and give them conventional forensic tools to structure, examine, and report on the relevant data. We believe this combination of AI-assisted prioritization and investigator-controlled analysis is a powerful way to make SQLite evidence more accessible without sacrificing transparency or control.”
— Yuri Gubanov, CEO of Belkasoft
More Flexible Android Acquisition
The redesigned MediaTek workflow separates acquisition from decryption. Investigators can acquire a dump first and decide how to access the encrypted user data afterward: decrypt it once the passcode is known, or run a brute-force attack. This approach is particularly helpful when working with damaged or non-booting phones, where little is known about the device before acquisition: you can revisit the same dump later, or try a different strategy.
MTK passcode brute-force is now more flexible. The brute-force attack works with unknown passcode lengths and supports dictionary attacks on alphanumeric passwords. Once passcode properties have been recovered from the device data, this approach allows you to perform the attack more efficiently.
Agent-based Android acquisition is more reliable on recent Android versions and now collects SMS messages and call history. Because the agent can save data to a USB flash drive or other external storage, investigators can collect evidence in the field without a forensic workstation.
New Evidence Sources for Mobile and Windows Investigations
On Android, new parsers cover Burner, FairEmail, Google Voice, GroupMe, Life360, Mastodon, MeWe, Microsoft Teams, TeleGuard, Waze, Wire, and other applications.
On iOS, Belkasoft X now extracts ChatGPT data, and updated parsers extract more data from Telegram, WhatsApp, X (formerly Twitter), Facebook, Instagram, Viber, and WeChat.
On Windows, Belkasoft X v2.12 adds three artifacts that show what happened on a computer:
- BAM and DAM records show program execution, with paths and timestamps.
- System Resource Usage Monitor (SRUM) data shows which applications used the network and when.
- Remote Desktop cache reconstruction rebuilds screen fragments into images. It shows what a user saw during a remote session, even if the remote host no longer exists.
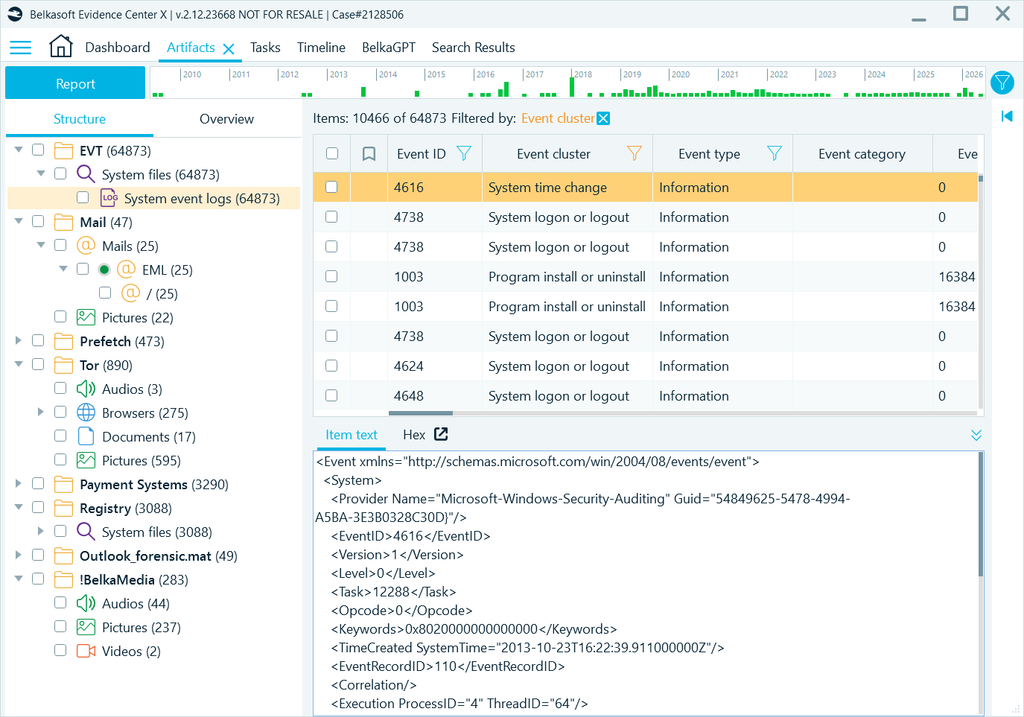
Windows event logs are also easier to review. The new Event cluster property groups events by activity, such as logons, software installations, remote access, and Wi-Fi connections. A single activity, such as a logon, can produce events with several different Event IDs. With clusters, investigators see all related events together and do not need to know which Event IDs to search for.
For legal review, Belkasoft X now supports Relativity Short Message Format (RSMF) 2.0. It can also split large exports by item count or file size for platforms such as Relativity.
Secure and Cost-Efficient Deployment
Belkasoft Offline Map Server lets air-gapped labs review geolocation evidence on maps without online mapping services. Coordinates from evidence stay inside the lab.
A new Windows installer for BelkaGPT Hub makes shared AI processing easier to deploy. Labs can install the hub on GPU-equipped workstations or a dedicated server. Examiners then send AI processing tasks to the hub from their regular computers, so the lab does not need to upgrade every machine. The Forensic Focus webinar Practical AI in Digital Forensics: Running Offline AI on Your Own Evidence with BelkaGPT explains how the deployment works.
Digital Forensics for Law Enforcement and Corporate Investigations
With version 2.12, Belkasoft X helps law enforcement and corporate forensic teams work with more data sources and spend less time on manual review. Sensitive evidence stays under their control.
The update is free for customers with an active Software Maintenance and Support contract. The trial version includes BelkaGPT. For more information about Belkasoft X v2.12, visit the Belkasoft X website.
About Belkasoft

Belkasoft is a global provider of digital forensics and incident response software. Law enforcement agencies, government bodies, and corporate security teams around the world use Belkasoft products to acquire, analyze, and report on digital evidence.