A round-up of today’s digital forensics news and views:
Forensic Focus News
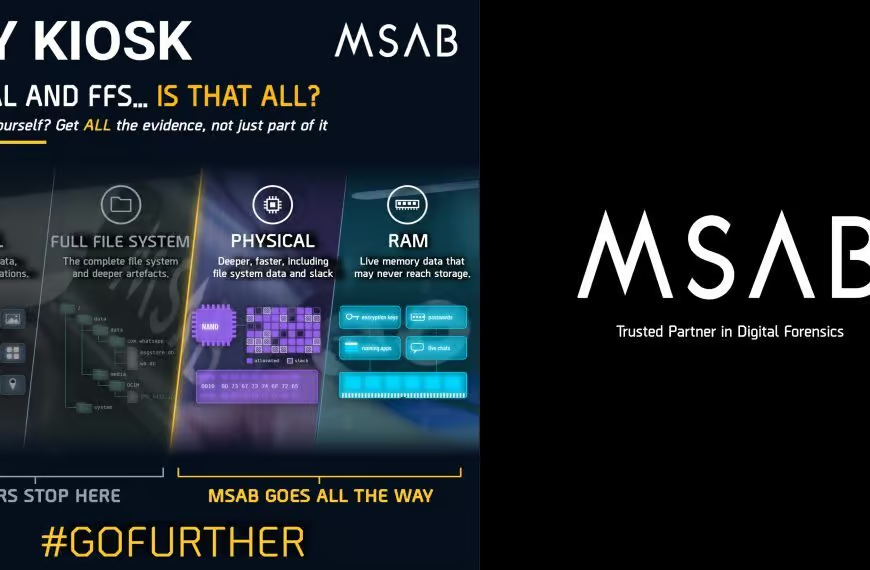
Go Beyond The Basics With XRY Kiosk From MSAB
Go beyond the basics with XRY Kiosk – extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics.
Research & Techniques
M365 Audit Log May Miss File Exfiltration Events
Microsoft 365 Unified Audit Log can record successful file acquisition as FileAccessed rather than FileDownloaded, a gap validated through controlled DFIR testing. Threat actors using Microsoft Graph API, Python scripts, or PowerShell can retrieve file content without triggering the expected FileDownloaded telemetry, misleading exposure assessments. Investigators should weigh access method, user agent strings, volume, and velocity when evaluating FileAccessed events during suspected unauthorized access.
Apple Unified Log Coverage Validation Explained
Empty search results in the Apple Unified Log can indicate either an absence of activity or a gap in archive coverage, and distinguishing between the two requires explicit methodology. Archive metadata, including reported start dates and class markers, cannot reliably define coverage boundaries, as reference iPhone data showed a 1970 epoch start date and markers that shifted independently of actual log data. Acquisition choices, such as setting a start date in UFADE, silently truncate archives without leaving any trace in the archive itself.
Windows Event Log Investigation Guide for IR
Effective event log investigation means building and verifying attacker hypotheses across multiple evidence sources, not just flagging suspicious Event IDs. Security logs can overwrite within hours, so preservation must precede analysis, with scope defined by host, timeframe, and behavior.
AI Agent Workflow Tips for Malware Analysts
Lenny Zeltser’s cheat sheet outlines how malware analysts can integrate AI agents into their workflow while maintaining analytical control, covering lab isolation, task delegation, and claim verification. Recommended integrations include GhidrAssistMCP for code review, ProcmonMCP for behavior analysis, and x64dbg Automate MCP for debugging, with REMnux and FLARE-VM as suggested lab environments. Analysts are warned against accepting agent conclusions uncritically, particularly around threat intel and common code patterns like packing.
Tools & Software
GLEAPP Triages Images and Video for DFIR
GLEAPP is a forensic media triage tool that processes folders, file system extractions, and E01 or raw disk images across NTFS, APFS, HFS+, ext, F2FS, and FAT formats. It supports deleted media recovery via MFT and FAT carving, MD5/SHA-1/SHA-256 and perceptual hashing, exact and visual deduplication, EXIF and GPS extraction, and known-hash matching against Project VIC, CAID-style databases, and the NSRL RDS. Output formats include HTML contact sheets, CSV, JSON, KMZ, and LAVA project files, with categorization decisions left entirely to the examiner.
Unfurl v2026.09 Adds Major Platform Parsers
Unfurl v2026.09 ships new parsers for Gmail, Safe Links, Facebook, Instagram, and GitHub, expanding its URL decomposition coverage across platforms investigators frequently encounter. Improved timestamp decoding in tokens and IDs strengthens artefact analysis, while new Tree and Text views in the web UI improve readability of results.
Training & Events
SANS Summit Case Study: Marshal Framing Investigation
A former Deputy U.S. Marshal used VPNs, encrypted messaging apps, and wiped devices to frame his ex-fiancée, but digital evidence secured his conviction anyway. At the SANS DFIR Summit in Arlington on October 15, 16, forensic investigator Jason Higley will detail how examiners reconstructed the scheme from fragmented artifacts across multiple service providers, with no single smoking gun.