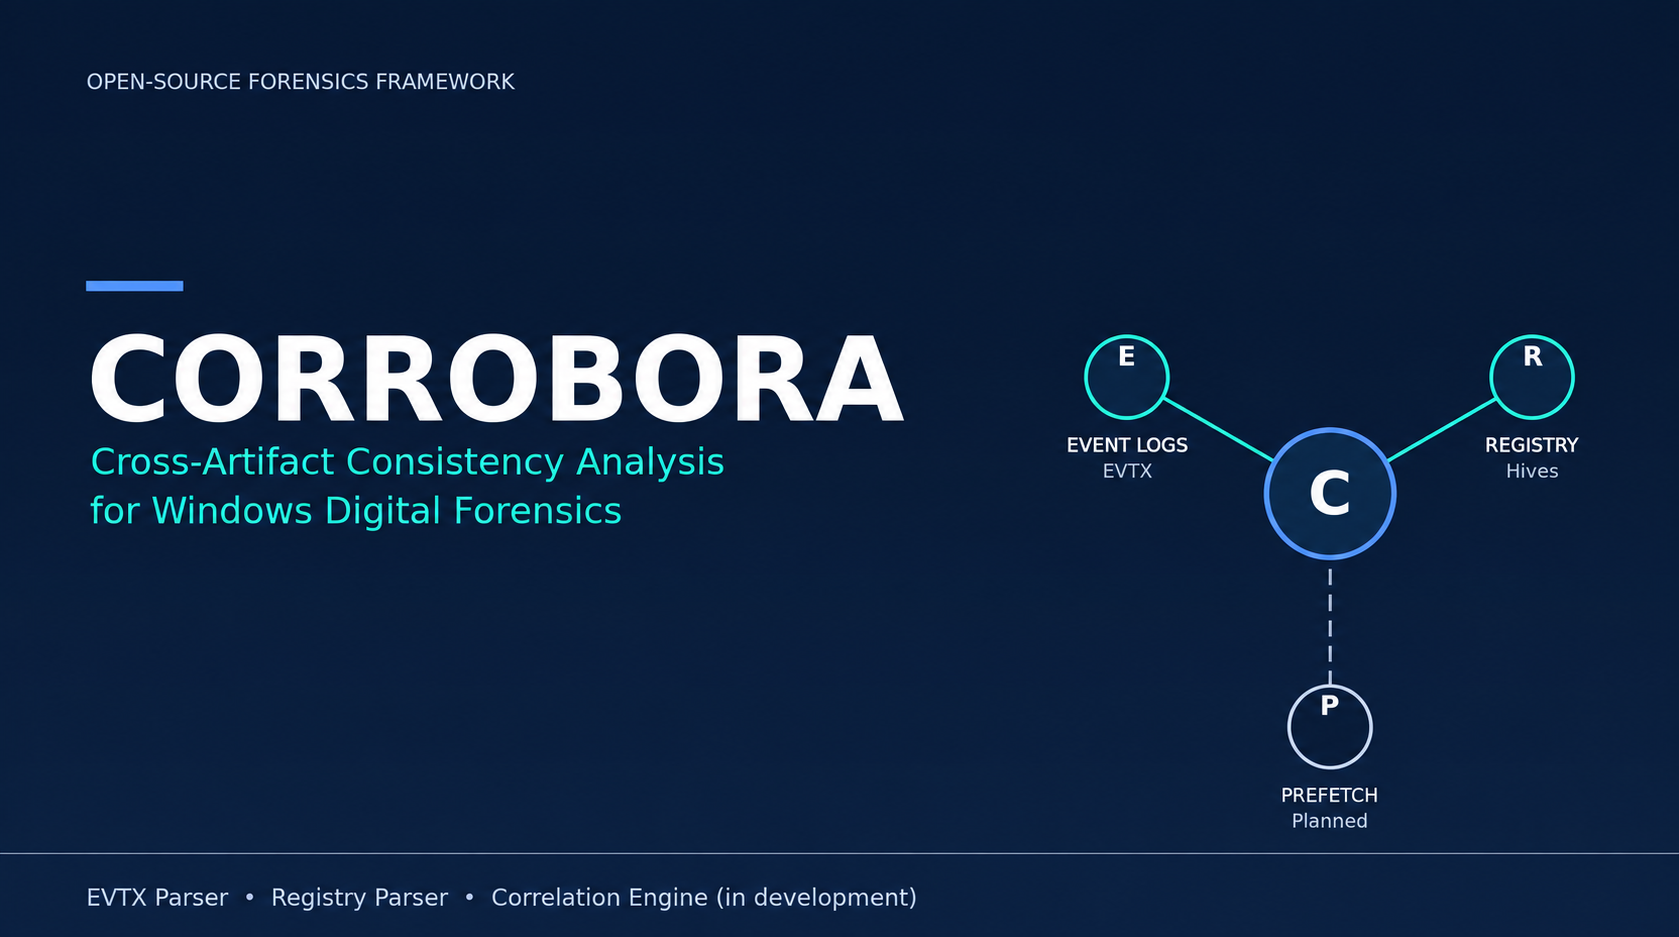
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Publication: an ethical dilemma for digital forensics research?

First published June 2010 by Dr Chris Hargreaves, lecturer at the Centre for Forensic Computing at Cranfield University in Shrivenham, UK Ethical issues in science are commonplace; examples such as cloning, climate change and genetic engineering are all subject to

Flash drives and acquisition

First published June 2010 by Dominik Weber, Senior Software Architect for Guidance Software, Inc. “Take a look at this”. It started simply with that.A co-worker was looking into some strange issue with an acquisition of a flash drive. It seemed

Unusual devices

First published June 2010 by Sean McLinden In 2007, New Jersey Governor Jon Corzine made the news twice for a single event. The first time was the report of a car accident on the Garden State Parkway in which he

Digital forensic sampling

The application of statistical sampling in digital forensics Authors: Robert-Jan Mora and Bas Kloet Company: Hoffmann Investigations, Almere, The Netherlands URL: http://en.hoffmannbv.nl Date: 27th March 2010 Version:1.0 Table of contents 1 Introduction 2 Sampling basics 2.1 The necessity for sampling

EnCase file copying and Windows Short File Names

First published May 2010 By Lee Hui Jing, EnCe Edited by Sarah Khadijah Taylor ABSTRACT A couple of months ago, one of my clients, an Investigating Officer from a Law Enforcement Agency, had requested me to extract some of the

The (Nearly) Perfect Forensic Boot CD – Windows Forensic Environment

by Brett Shavers   Introduction Figure 1: WWW.FORENSICS-INTL.COM As a quick introduction to the Windows Forensics Environment (WinFE); it is a bootable CD, based on the Windows Pre-Installed Environment (PE), with a few changes to create a forensically sound boot

Are users getting smarter?

First published February 2010 by Darren Ilston of MelBek Technology www.melbek.co.uk There is no doubt in my mind that computer users in general think they are becoming smarter when it comes to covering their tracks.The usual suspects of deleting browser

Timeline Analysis – A One Page Guide

First published February 2010 by Darren Quick Comments and suggestions may be sent to [email protected] Prepare The scope of the request determines the data to be collected, such as within a specific timeframe, and data of relevance such as specific

Casey Anthony Trial – Valid conclusions?

"Recently, the Casey Anthony trial in the USA has been a source of discussion in many fora, but most recently a bit of a “spat” seems to be in danger of breaking out between the developers of two of the

The darker side of computer forensics

First published January 2010 by John Irvine http://johnjustinirvine.com http://twitter.com/John_Irvine For the better part of the past thirteen (thirteen?!) years, I have been a computer forensic examiner. Sure, the title varies by job and location — digital forensic analyst, media exploiter,

Serving search warrants in Spain

First published January 2010 The expert witness perspective by Joaquim Anguas Abstract This article describes the most common schema and basic procedure in which search warrants related to computer evidence are served in Spain from the expert witness perspective, and

Computer incident response – DO NOT PANIC

First published January 2010 by Karl Obayi – Solicitor http://www.itevidence.co.uk This article seeks to advance some basic steps to be adopted in case you are confronted with a computer incident that calls for appropriate response. The incident in question could

Shrinking the gap: carving NTFS-compressed files

First published October 2009 Recovering deleted NTFS-compressed files By Joachim Metz Hoffmann Investigations www.hoffmannbv.nl 1.0 Joachim Metz September 2, 2009 Initial version. Summary An important part of digital forensic investigation is the recovery of data, particulary files. The recovery of

The Importance of Memory Search and Analysis

First published October 2009 by Access Data www.accessdata.com Introduction Historically, criminal or corporate investigations involving computer equipment began by immediately disconnecting any compromised machines from the network, powering them down, and securing them in a proper environment where they would

Simple Steganography on NTFS when using the NSRL

First published October 2009 Adam Hurwitz [email protected] Business Intelligence Associates, Inc. 39 Broadway, NYC, NY 10006 Abstract NTFS is structured so that there can be a physical separation of the data that comprises a file and the properties or metadata

Linux for computer forensic investigators: «pitfalls» of mounting file systems

First published October 2009 by Suhanov Maxim ITDefence.Ru Introduction Forensic Linux distribution is a customized Linux distribution that is commonly used to complete different tasks during computer forensics investigations. These distributions are often used to complete the following tasks: –