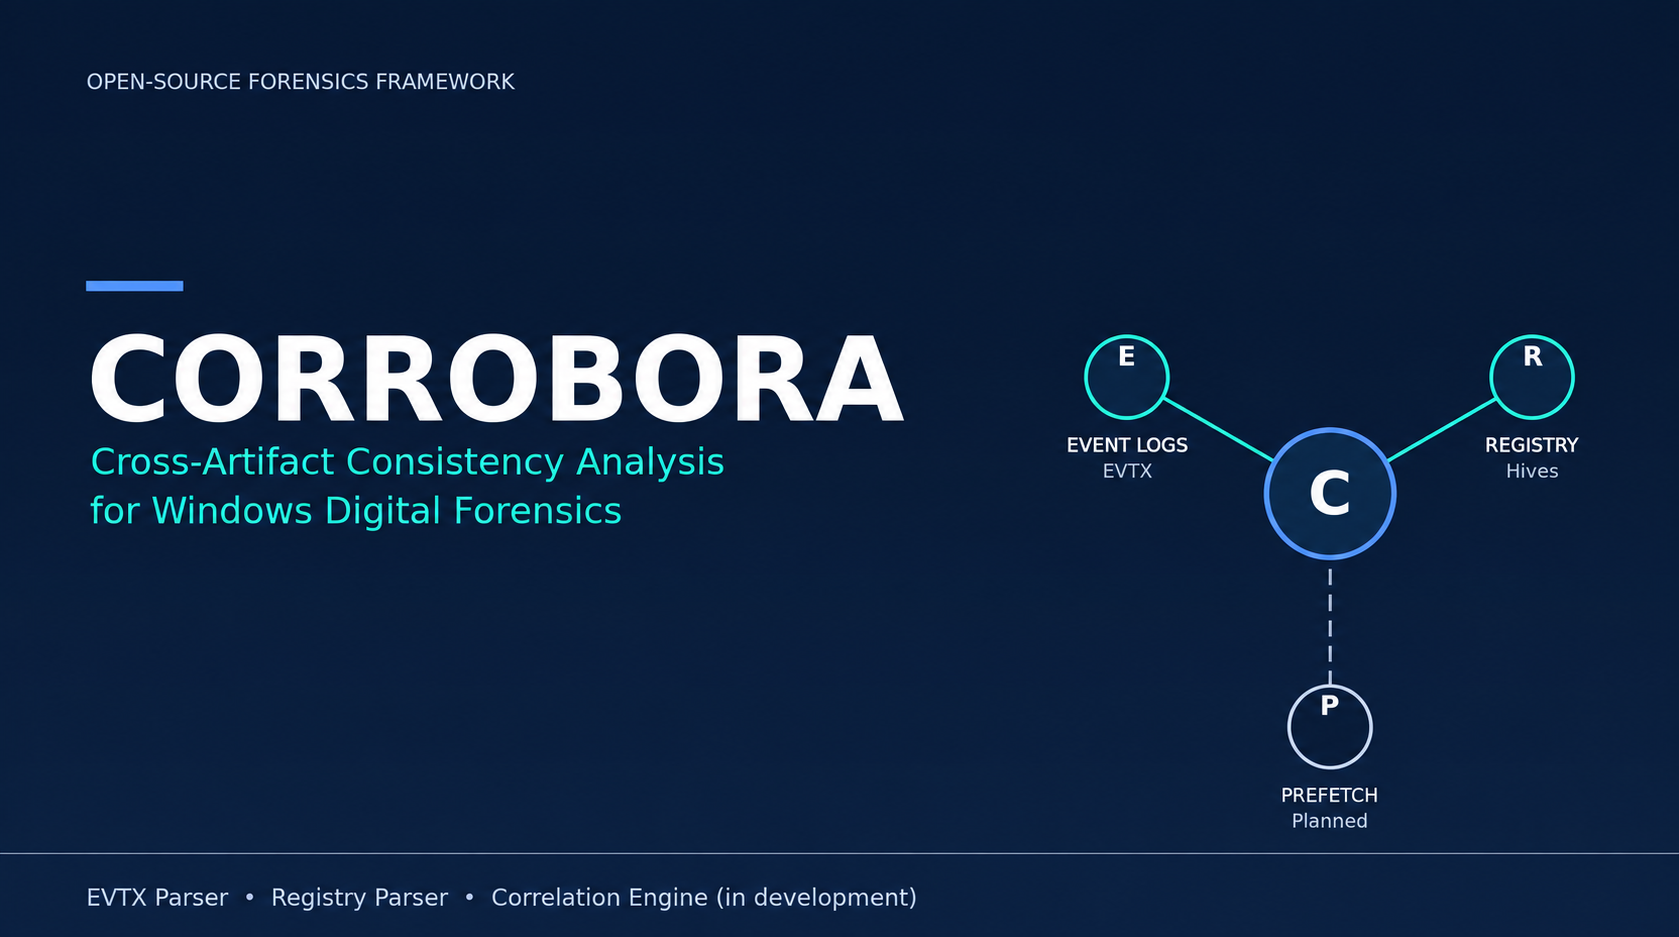
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

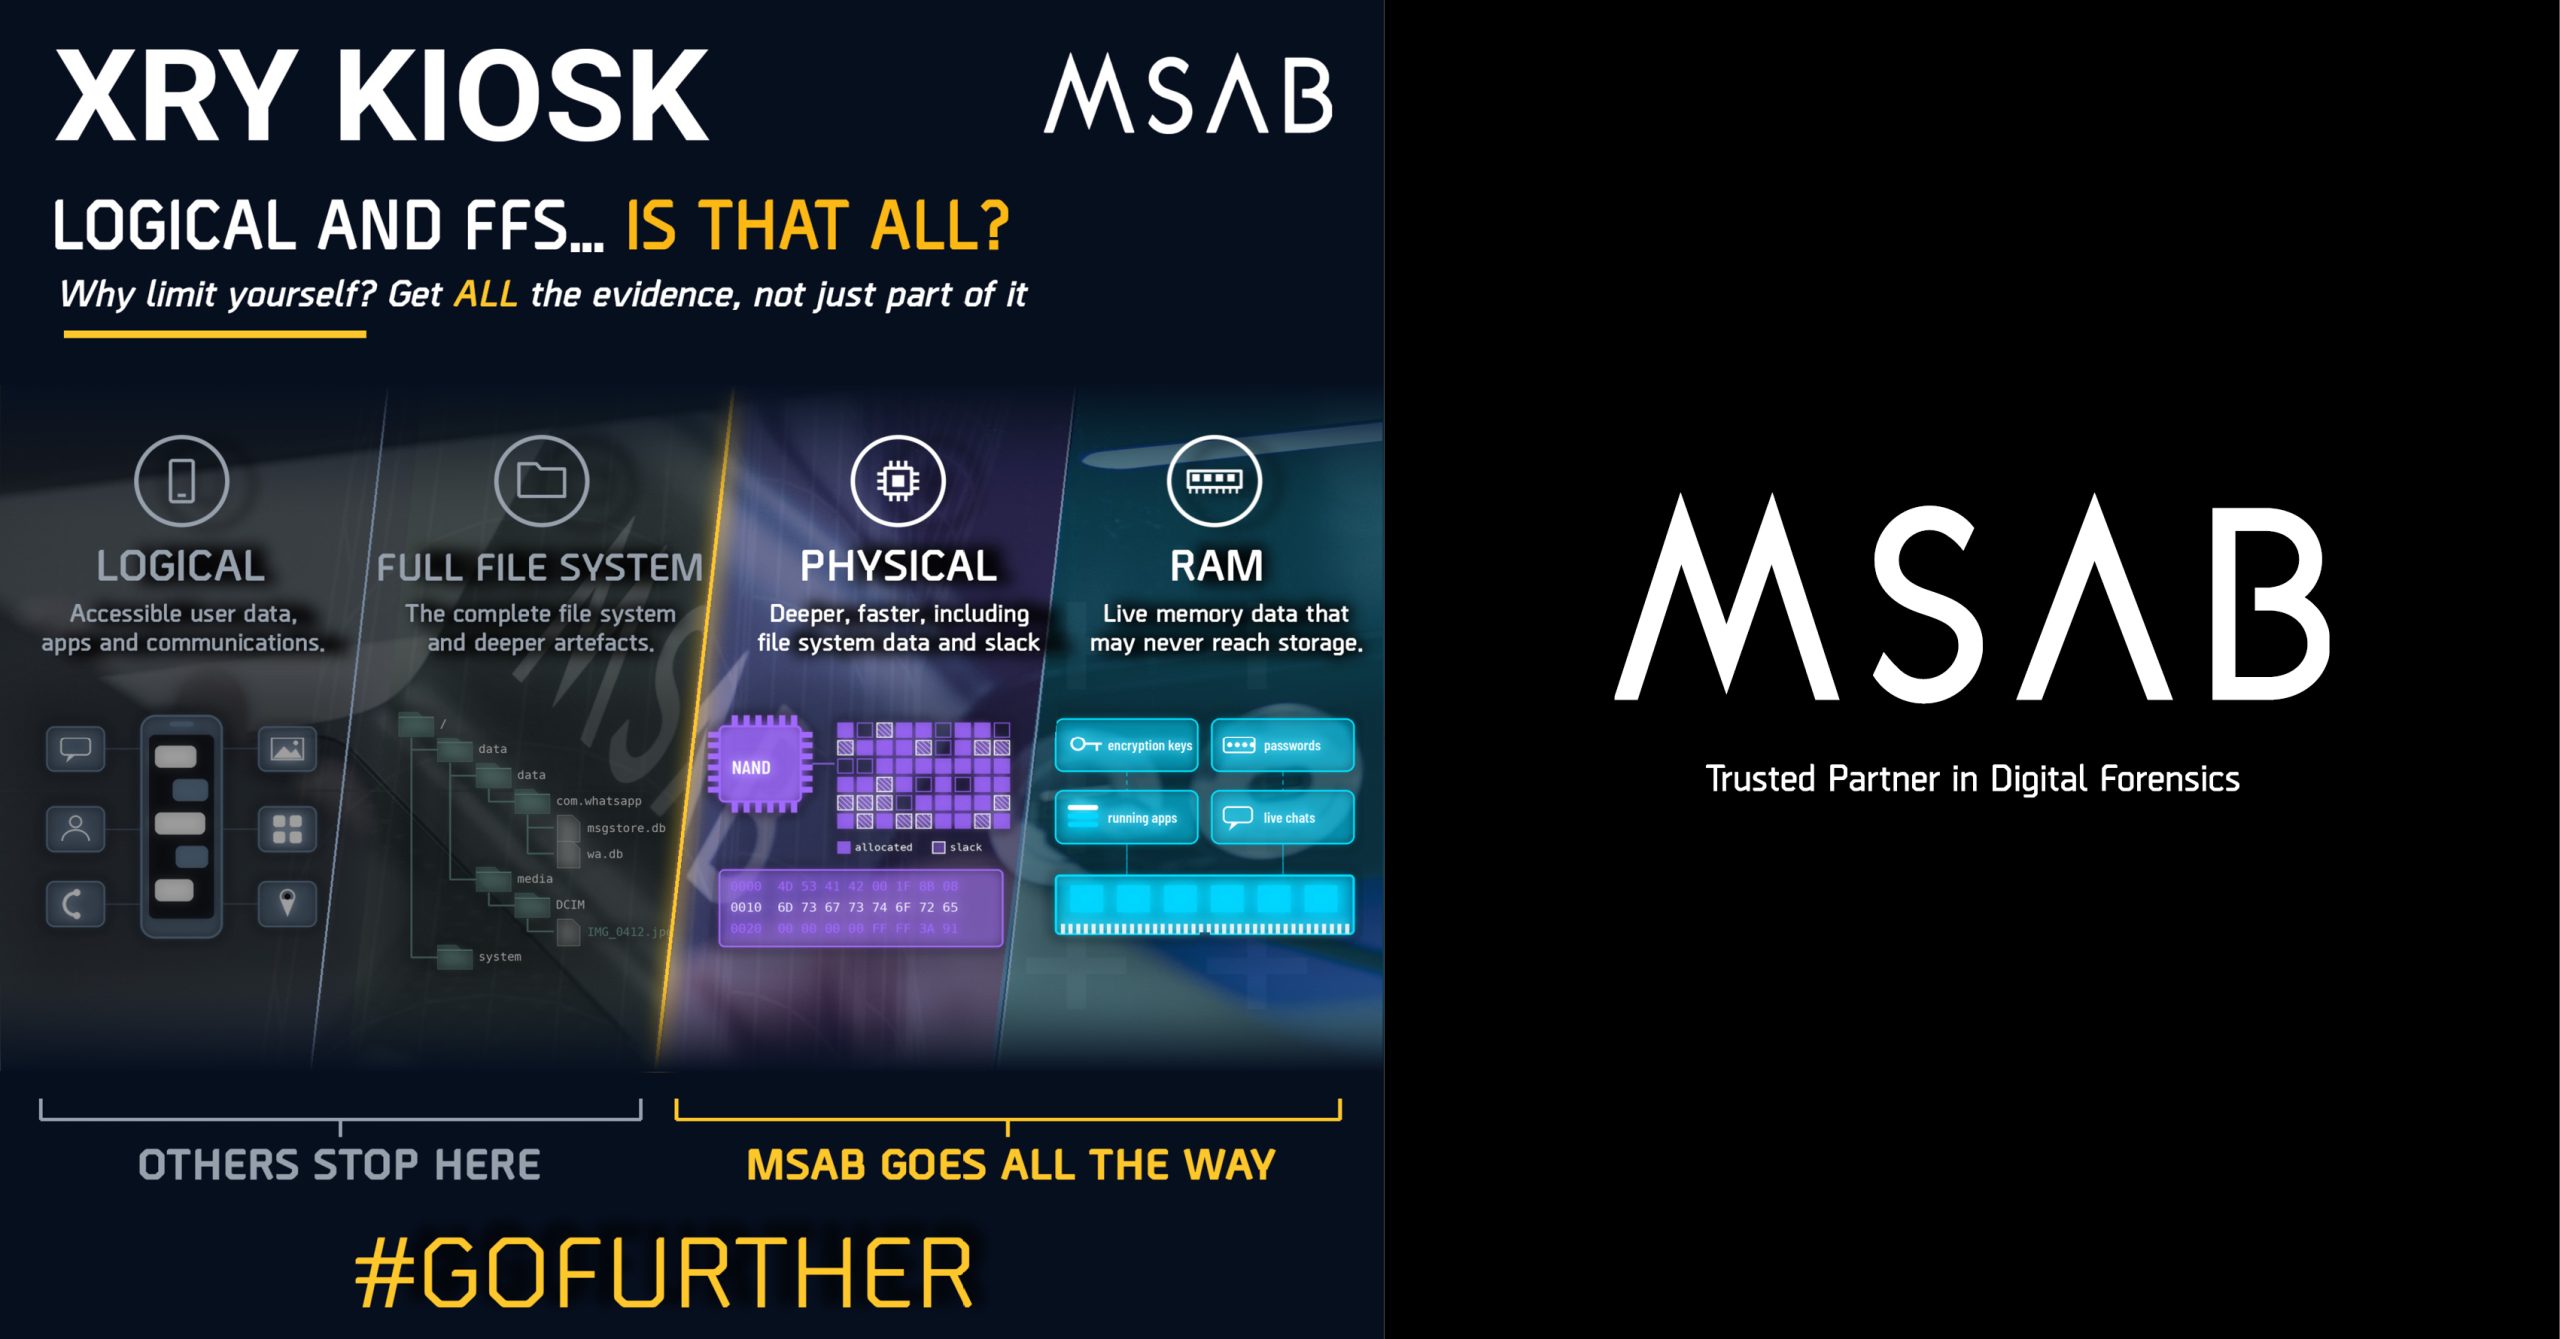
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Passive Network Security Analysis with NetworkMiner

First published January 2009 by Erik Hjelmvik networkminer.sourceforge.net It is disturbing how often networks are not properly documented in terms of IP plans, network segmentations and network security. Having a good view of the network is essential when performing a

A Discussion of Virtual Machines Related to Forensics Analysis

First published November 2008 by Brett Shavers (PDF version here) The Virtual Machine (VM)Description of the Virtual Machine The Virtual Machine Concept in Brief Virtual machines are not new and have been in use for well over a half century.

Email Evidence – Now You See it, Now You Don’t!

First published October 2008 By Sandy Boucher and Barry Kuang, Intelysis Corp. Background With the ever increasing role of computers and electronic communications in both our business and personal lives, emails have taken on a key evidentiary role in many

Linux ‘dd’ basics

First published March 2008 Linux dd can be a powerful and flexible tool to have in your box.You will find it installed by default on the majority of Linux distributions available today and it can be used for a multitude

The International Society of Forensic Computer Examiners (ISFCE)

by Joleyn Smithing, ISFCE The International Society of Forensic Computer Examiners (ISFCE)is dedicated to the advancement of the science of forensic computer examinations. Established in 2002, the ISFCE began as a result of the efforts of Mr. John Mellon. A

Computer Evidence in the Casey Anthony Trial – A Post Mortem

"In the recent case of the State of Florida vs. Casey Anthony, a recovered Firefox 2 history from Unallocated Space became the focal point of the State's case surrounding arguments of "premeditation". During the course of the trial, two different

Looking Forward To A Career In Digital Forensics

First published January 2008 by James Hooker I am rapidly approaching my final year of University, studying for a Forensic Computing degree, and like all students across the globe on a similar course, I am on a mission to find

Potential Impacts of Windows Vista on Digital Investigations

First published December 2007 by Christopher Hargreaves and Howard Chivers Paper received 30th April, 2007. C.J.Hargreaves, Cranfield University, Defence Academy of the United Kingdom, Shrivenham, SN6 8SW (+44 (0)1793 785753; e-mail: [email protected]).H.Chivers, Cranfield University, Defence Academy of the United Kingdom,

A Forensic Analysis Of The Windows Registry

First published November 2007 Derrick J. Farmer Champlain College Burlington, Vermont [email protected] (click here for a revised, quick reference PDF version of this paper) AbstractThis paper will introduce the Microsoft Windows Registry database and explain how critically important a registry

Corporate Investigations and the UK Data Protection Act

First published September 2007 by Rowenna Fielding INTRODUCTION A number of requirements of the Data Protection Act apply to workplace monitoring. While the DPA does not prohibit employee monitoring and investigation, any such activity must conform to the requirements of

Windows Vista – notes for forensic examiners (part two)

This article was first published in 2007 at http://www.securityfocus.com/infocus/1890 and is reprinted with permission by Jamie Morris Forensic Focus (www.forensicfocus.com) Intro In part one of this series [ref 1] we looked at the different editions of Vista available and discussed

Windows Vista – notes for forensic examiners (part one)

This article was first published in 2007 at http://www.securityfocus.com/infocus/1889 and is reprinted with permission by Jamie Morris Forensic Focus (www.forensicfocus.com) Intro While the fundamental principles of computer forensics remain largely unchallenged, the landscape upon which investigators operate is constantly changing.

F3 – The First Forensic Forum

‘F3 – The First Forensic Forum’, founded in the late 1990’s when forensic computing was still in its infancy, is a non-profit organisation with one specific goal which is reflected in our mission statement – “F3 exists to provide an