Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

How Detego Global’s AI Technology Is Transforming Child Abuse Investigations

Hero Image

Discover how AI-powered digital forensics is helping investigators accelerate child abuse investigations, identify critical evidence faster, safeguard victims, and reduce exposure to distressing content with Detego Global’s advanced technology....
Today's headlines 2 Nov 2026

AI For Investigations: 5 Myths, Debunked

AI For Investigations: 5 Myths, Debunked

Discover the truth behind five common myths about AI in investigations, with real-world insights from investigators using Cellebrite Genesis....read more
Forensic Focus Digest, 30 Oct 2026

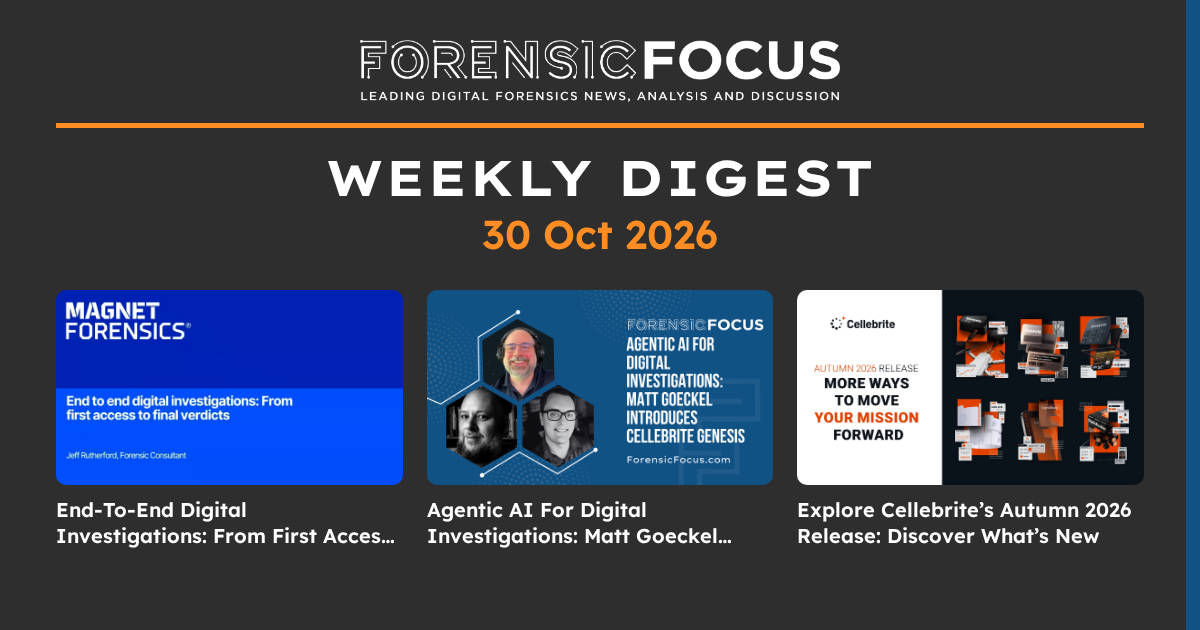
Forensic Focus Digest, 30 Oct 2026

Discover what’s new on Forensic Focus: explore end-to-end digital investigations with Magnet Forensics, meet Matt Goeckel, AI researcher at Cellebrite, learn about the Cellebrite Autumn 2026 Release, and more....read more
How A MacBook With A Broken Screen Helped Convict A UK Property Fraudster: Belkasoft X Case Study

How A MacBook With A Broken Screen Helped Convict A UK Property Fraudster: Belkasoft X Case Study

A broken MacBook, an iPhone, and a £113,000 fraud case - discover how Belkasoft X helped uncover crucial digital evidence that brought a UK property fraudster to justice....read more

The (Nearly) Perfect Forensic Boot CD – Windows Forensic Environment

by Brett Shavers   Introduction Figure 1: WWW.FORENSICS-INTL.COM As a quick introduction to the Windows Forensics Environment (WinFE); it is a bootable CD, based on the Windows Pre-Installed Environment (PE), with a few changes to create a forensically sound boot

Are users getting smarter?

First published February 2010 by Darren Ilston of MelBek Technology www.melbek.co.uk There is no doubt in my mind that computer users in general think they are becoming smarter when it comes to covering their tracks.The usual suspects of deleting browser

Timeline Analysis – A One Page Guide

First published February 2010 by Darren Quick Comments and suggestions may be sent to [email protected] Prepare The scope of the request determines the data to be collected, such as within a specific timeframe, and data of relevance such as specific

Casey Anthony Trial – Valid conclusions?

"Recently, the Casey Anthony trial in the USA has been a source of discussion in many fora, but most recently a bit of a “spat” seems to be in danger of breaking out between the developers of two of the

The darker side of computer forensics

First published January 2010 by John Irvine http://johnjustinirvine.com http://twitter.com/John_Irvine For the better part of the past thirteen (thirteen?!) years, I have been a computer forensic examiner. Sure, the title varies by job and location — digital forensic analyst, media exploiter,

Serving search warrants in Spain

First published January 2010 The expert witness perspective by Joaquim Anguas Abstract This article describes the most common schema and basic procedure in which search warrants related to computer evidence are served in Spain from the expert witness perspective, and

Computer incident response – DO NOT PANIC

First published January 2010 by Karl Obayi – Solicitor http://www.itevidence.co.uk This article seeks to advance some basic steps to be adopted in case you are confronted with a computer incident that calls for appropriate response. The incident in question could

Shrinking the gap: carving NTFS-compressed files

First published October 2009 Recovering deleted NTFS-compressed files By Joachim Metz Hoffmann Investigations www.hoffmannbv.nl 1.0 Joachim Metz September 2, 2009 Initial version. Summary An important part of digital forensic investigation is the recovery of data, particulary files. The recovery of

The Importance of Memory Search and Analysis

First published October 2009 by Access Data www.accessdata.com Introduction Historically, criminal or corporate investigations involving computer equipment began by immediately disconnecting any compromised machines from the network, powering them down, and securing them in a proper environment where they would

Simple Steganography on NTFS when using the NSRL

First published October 2009 Adam Hurwitz [email protected] Business Intelligence Associates, Inc. 39 Broadway, NYC, NY 10006 Abstract NTFS is structured so that there can be a physical separation of the data that comprises a file and the properties or metadata

Linux for computer forensic investigators: «pitfalls» of mounting file systems

First published October 2009 by Suhanov Maxim ITDefence.Ru Introduction Forensic Linux distribution is a customized Linux distribution that is commonly used to complete different tasks during computer forensics investigations. These distributions are often used to complete the following tasks: –

E-mail and appointment falsification analysis

First published September 2009 Analysis of e-mail and appointment falsification on Microsoft Outlook/Exchange By Joachim Metz Hoffmann Investigations www.hoffmannbv.nl Version: 1.0 Joachim Metz August 17, 2009 Initial version. Summary In digital forensic analysis it is sometimes required to be able

Experiences as a recent graduate

First published September 2009 Name withheld After graduating in the Summer of 2009, I knew that it would not be easy to find employment in a Computer Forensic related role. More specifically, I knew that the state of the UK’s

Alternatives to Helix3

First published August 2009 by BJ Gleason Author’s note: The article you are about to read was originally written in March 2009. The kind people at Linux+DVD magazine have allowed us to make my articles available after the printed version

Graduates: produce an excellent CV

First published July 2009 In this short article, David Sullivan of www.appointments-uk.co.uk, a specialist computer forensics recruiter, looks at how graduates can increase your chances of being selected for interview by improving your CV. David can be contacted at: [email protected]