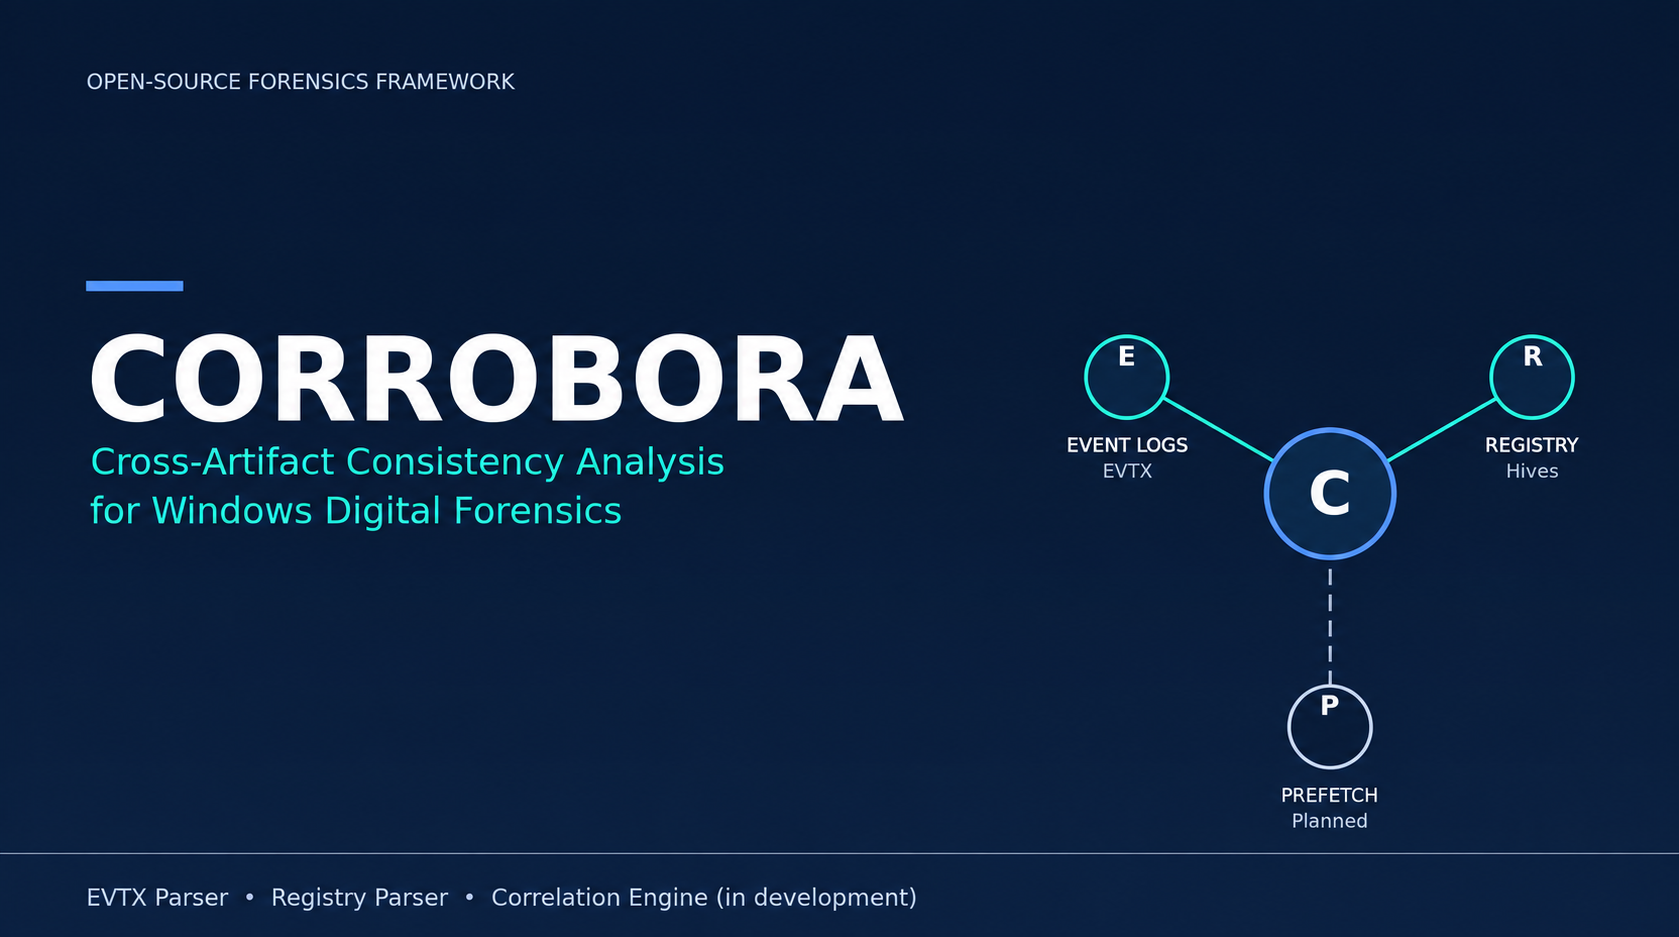
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

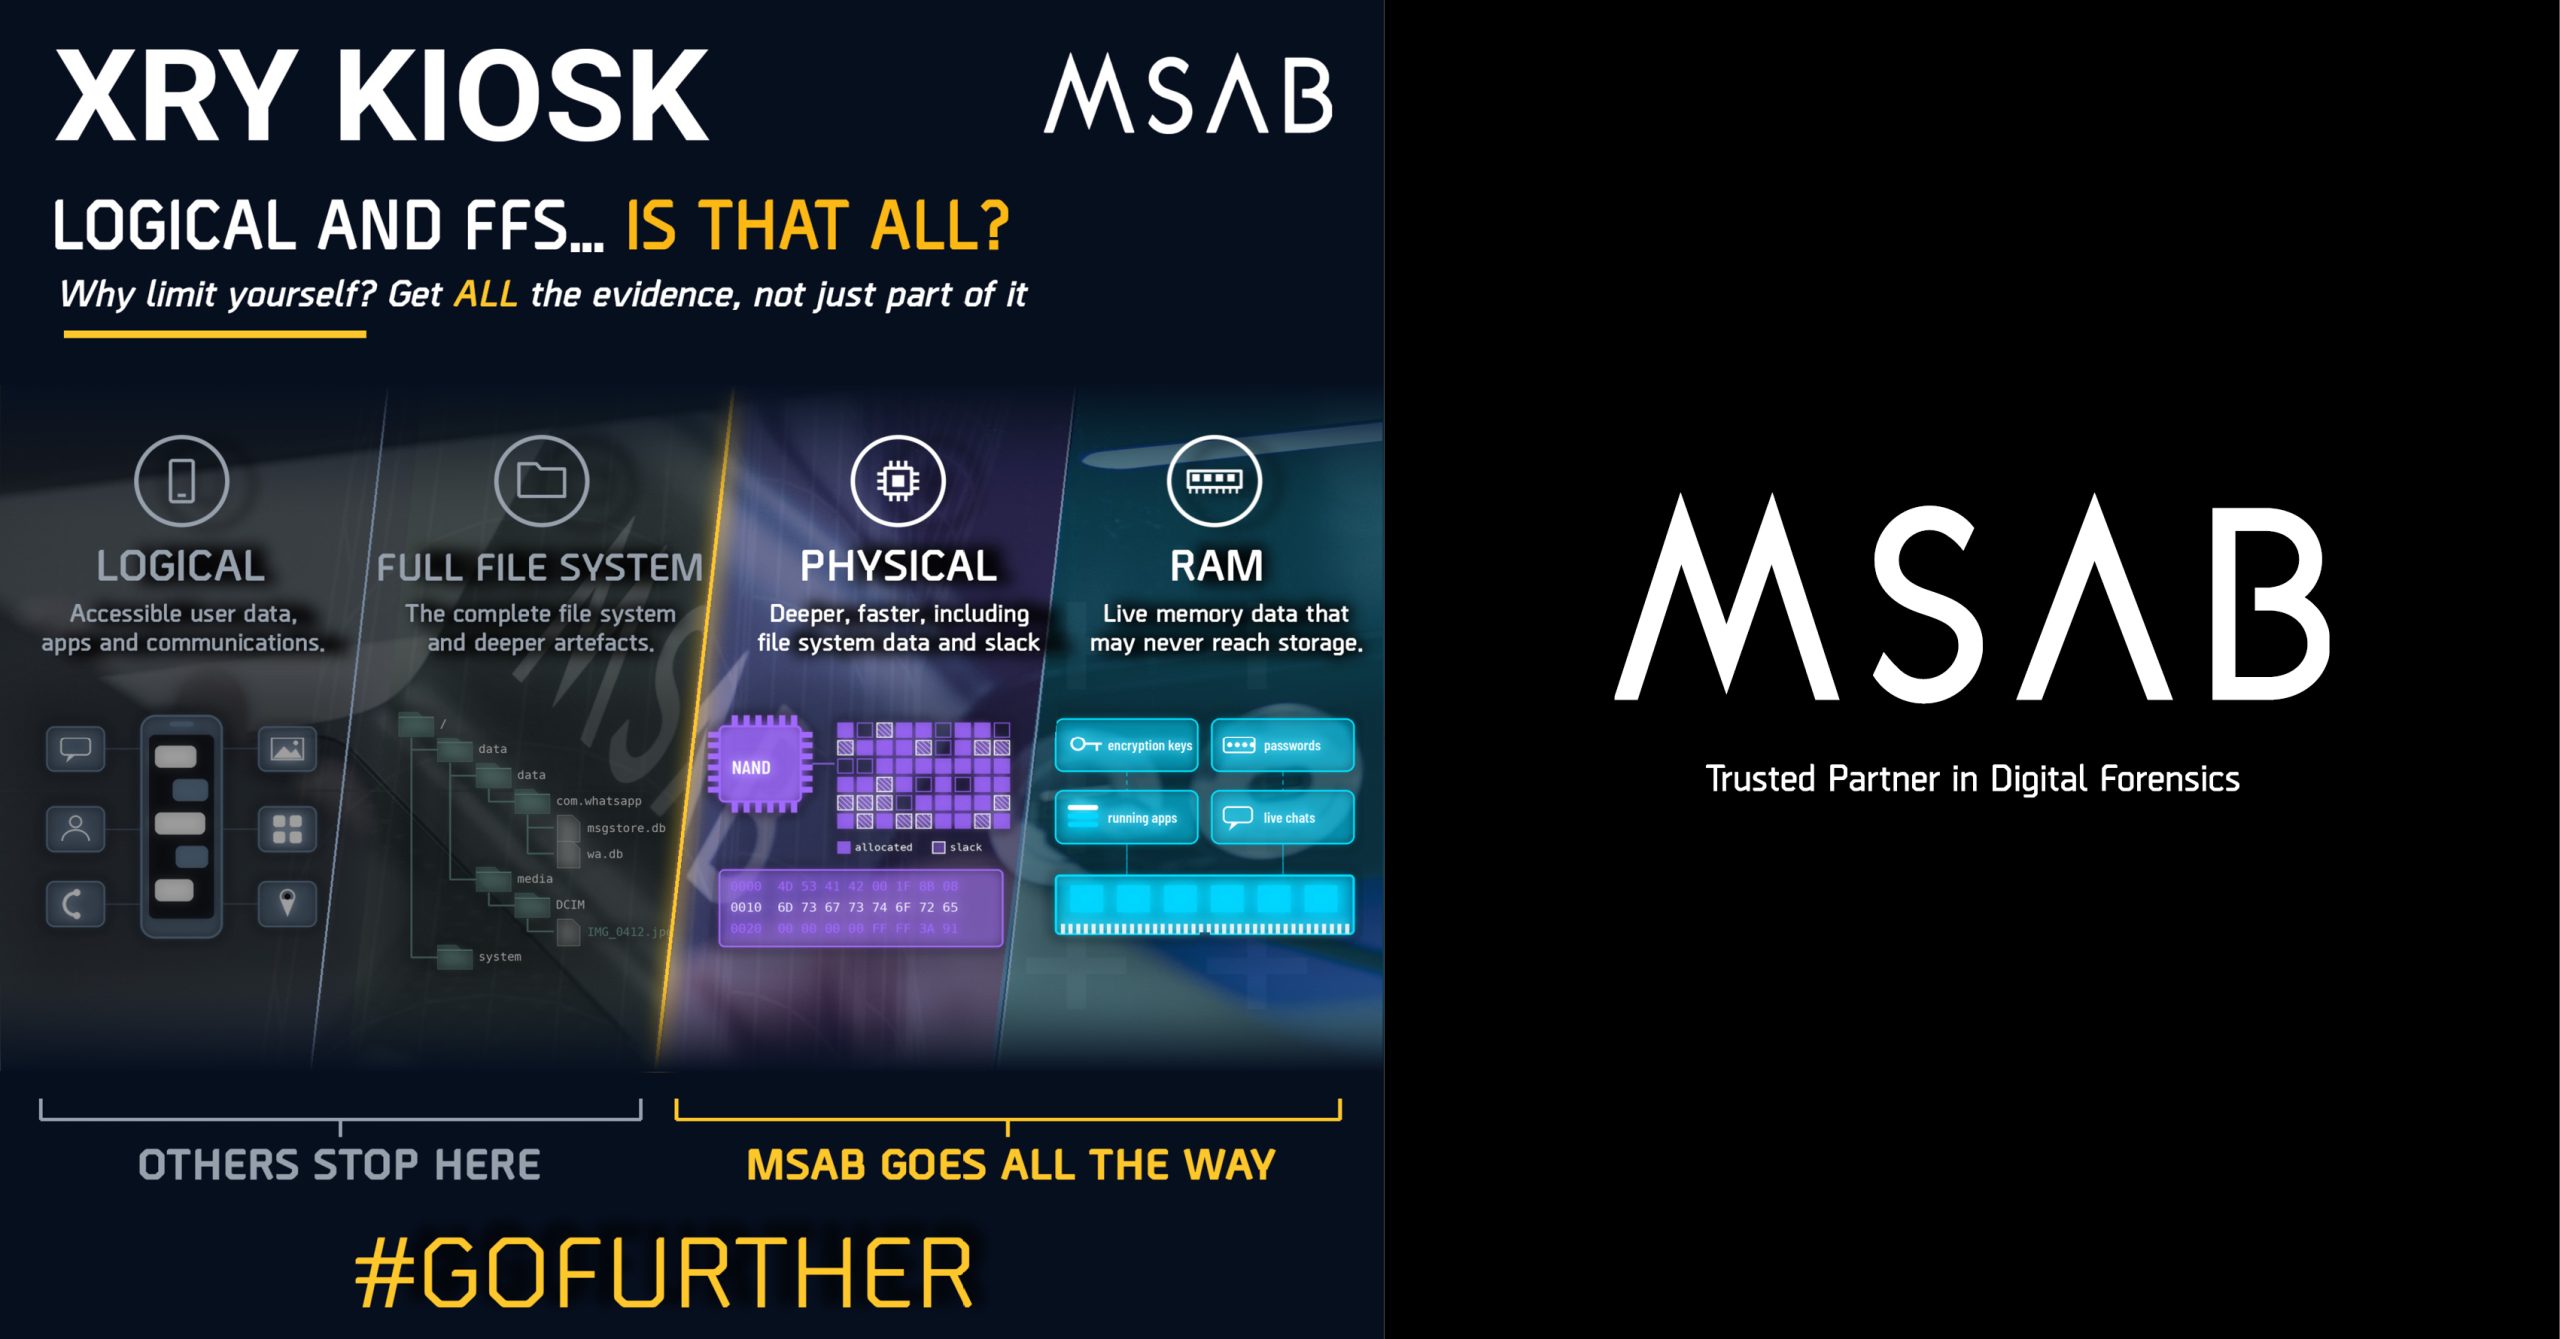
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Is Sarah Palin a Computer Criminal?

If Palin and her ghostwriter are in fact violating Facebook’s terms of use, that probably doesn’t seem like a big deal to most people. Just by surfing around the internet, we “agree” to dozens of website terms of use every

Oxygen Forensic Suite 2010 adds support for iTunes 10

The new 2.8.2 release of Oxygen Forensic Suite 2010 adds support for iTunes 10 as well as newest Blackberry and Samsung devices. All registered customers may download the new version immediately from their personal pages, a trial version is available

Please support David Benford running for the Cystinosis Foundation

David Benford from Blackstage Forensics is raising money for the Cystinosis Foundation by running in the Amsterdam Mizuno half marathon on the 17th of October. David’s daughter suffers from Cystinosis, a very rare and serious condition which is as yet

E-Mail Isn’t as Ethereal as You Might Think

At first blush, message headers seem esoteric. Why should a lawyer care about the alphanumeric ID assigned to a message, the message’s offset from Greenwich Mean Time or the names of the servers it traversed before delivery? The answer lies

Computer Forensics Experts, Who’s Your Daddy?

As computer forensics has become increasingly important to civil and criminal trials, certification for computer experts has been a growing business. Today there are a handful of nonprofit and for-profit organizations that offer computer forensic certification programs. However, no one

CSI SQL Server – Methods for collecting digital evidence

Forensic analysis of database systems is very specific and demanding task, and it was the main inspiration for writing this article. In this article you will find information about what digital forensic is and what kind of methods you can

Intro to Report Writing for Digital Forensics

So you’ve just completed your forensic examination and found that forensic gem or smoking gun in your case, so how do you proceed? Depending on where you fall as a forensicator (e.g., law enforcement, intelligence, criminal defense work, incident response,

Insiders Doubt 2008 Pentagon Hack Was Foreign Spy Attack

In the fall of 2008, a variant of a three year-old, relatively-benign worm began winding its way through the U.S. military’s networks, spread by troops using thumb drives and other removable storage media…”Some guys wanted to reach out and touch

High tech crime fighters in Garfield County Sheriff’s Office

When a detective with the Garfield County Sheriff’s Office collects a computer, cell phone, digital camera, thumb drive, or any other technological device that potentially holds evidence pertaining to a case, they take it to one person — Detective Cpl.

‘Web 2.0’ as evidence

by Sean McLinden "In a recent intellectual property case for which we were retained, among the electronically stored information (ESI) that the plaintiff sought for production were internal company blogs and wikis used by the defendant’s developers to discuss new

HBGary Unveils Freeware Tool for Incident Responders, Forensic Practitioners

HBGary has released a new freeware tool, FGET, a network-capable forensic data acquisition tool. FGET simplifies the process of acquiring forensically sound copies of key data on the hard drive, including the prefetch directory, system32\config directory, and all user’s NTUSER.DAT

Scalability: A Big Headache

by Dominik Weber"Scalability is simply the ability of our forensic tools and processes to perform on larger data sets. We have all witnessed the power of Moore's law. Hard drives are getting bigger and bigger. A 2 TB SATA hard

Single Sign On

by Si Biles"Calling something a “Holy Grail” is an interesting term – the intended meaning is well known to most of us – i.e. something miraculous that will solve all of your problems. However given that it’s supposedly a cup,