A round-up of today’s digital forensics news and views:
Forensic Focus News
How Semantics 21 Is Changing The Way Investigators Work With Digital Evidence
Semantics 21 develops forensic intelligence tools designed to reduce manual investigative work across image, video and audio evidence. S21 VisionX handles large-scale image and video analysis, similarity grouping and victim identification, S21 CCTV accelerates video evidence review, and S21 Transcriber makes spoken content searchable. All three tools support offline operation for secure environments.
Passware Kit 2026 v4 Simplifies BitLocker Decryption And Adds E01 Export
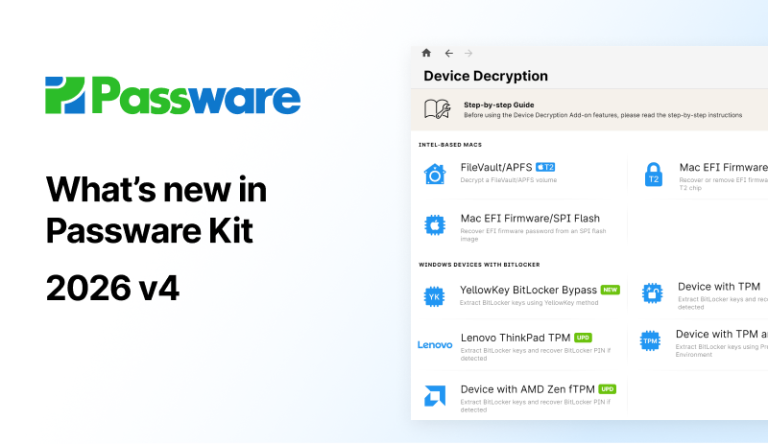
Passware Kit 2026 v4 expands BitLocker decryption support to additional AMD Zen/Zen+ devices and Lenovo hardware, and introduces the YellowKey method for PIN-free recovery on supported Windows systems. Decrypted disk images can now be exported directly in E01 format for analysis in standard forensic tools, and eCryptfs-encrypted Linux home folders are also now supported.
Case Studies
Qilin Ransomware Exploits Hypervisor Layer, Bypasses EDR
Qilin and INC ransomware operators are exploiting PAN-OS GlobalProtect CVE-2026-0257 to open MFA-free VPN sessions, moving directly from the gateway to vCenter without triggering endpoint detection. By disabling execInstalledOnly on ESXi hosts and extracting credentials from a domain controller’s virtual disk offline, attackers leave no process artifacts for EDR to catch. Responders should pull vCenter and ESXi logs for host security changes, hunt for fake MAC addresses and hard-coded OS strings at the gateway, and treat any confirmed compromise as requiring full credential reset including krbtgt.
Research & Techniques
PHP RCE Artifacts and Detection Queries for Responders
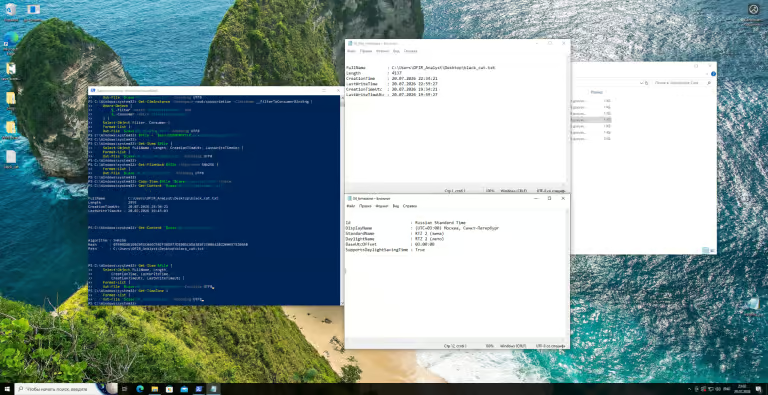
Two critical PHP remote code execution vulnerabilities (CVSS 9.2) are prompting incident responders to prepare for post-exploitation activity across php-fpm, php-cgi, and web-server worker processes. Key artifacts include shell spawning from web workers, modified PHP files in webroots, outbound connections to unexpected IPs, and php-fpm SIGSEGV crashes. Detection query starters are available for Microsoft Defender KQL, Splunk, Sigma, auditd, and Velociraptor, with guidance on preserving memory, logs, and webroot snapshots before patching.
Tools & Software
Birdbrain Captures Tamper-Proof Web Evidence Free
Birdbrain is a free, open-source desktop app and Chrome extension designed to capture web pages as tamper-proof evidence for investigations. It automatically extracts indicators such as emails, domains, and cryptocurrency wallet addresses from captured pages.
Training & Events
Advanced Drone Forensics Course Targets Investigators
Spyder Forensics and the European Digital Forensics Training Alliance are offering an advanced drone forensic analysis course covering forensically sound acquisition, flight log and telemetry analysis, and geospatial reconstruction across DJI, ArduPilot, PX4, and FPV ecosystems. Attendees will gain end-to-end examination skills for aircraft, controllers, and mobile devices using repeatable, defensible methodologies, and will receive the Spyder Forensics UAV Flight Log Analysis Tool Suite.