A round-up of today’s digital forensics news and views:
Forensic Focus News
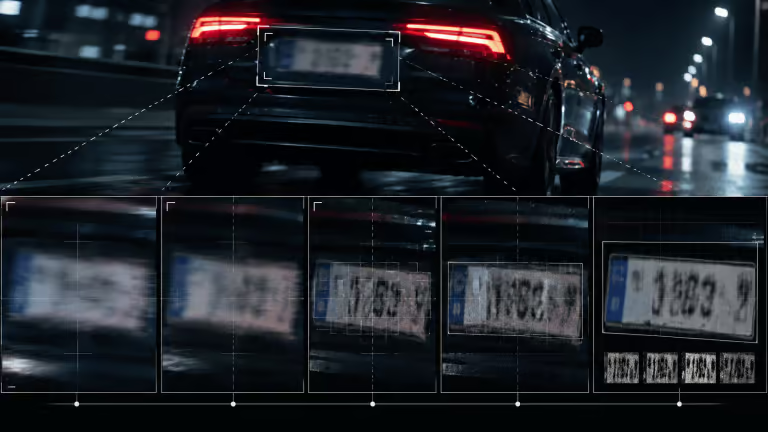
Beyond Blur: Decision-Making In Complex Licence Plate Examination And Enhancement Casework
Describing a licence plate as blurred is a visual observation, not a technical diagnosis, and different degradation factors require different processing strategies. Across four real casework examples, analyst Guocai Wang of Third Engine SL demonstrates how temporal sequences, frame registration, occlusion changes, processing order, and candidate-level interpretation each demand distinct decisions. The goal is not always a complete plate reading; some material can support only partial characters or multiple plausible candidates, and forcing a definitive conclusion can exceed what the source evidence allows.
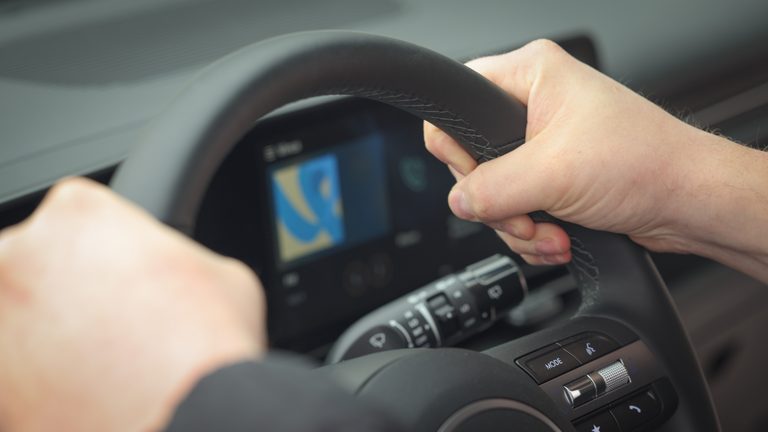
Analyzing Driver Behavior Using Vehicle Data
Velocity logs, hard braking, and hard acceleration events recorded by vehicle infotainment systems can distinguish intentional from accidental driving behavior, a distinction that proved critical in a UK murder case involving an Amazon delivery driver. Using iVe, analysts compared two trips along the same route in a 2026 Hyundai Kona, finding Trip 2 included speeds up to 22 mph over the limit and 23 hard acceleration events versus 8 in Trip 1. Repeated acceleration while already exceeding speed limits can indicate reckless or deliberate conduct rather than isolated error.
Tools & Software
Autorunsc 14.3 Regression Hides Persistence Entries
A behavioral change in Autorunsc 14.3 alters how launcher targets are resolved, causing signed launchers to mask unsigned persistence entries that earlier versions surfaced correctly. Examiners relying on signature filtering to triage autoruns output may miss active persistence mechanisms introduced after this version change.
Read more (digitaldefenseinstitute.com)
Hayabusa-Bulk-Runner Automates Multi-Host KAPE Triage
Hayabusa-Bulk-Runner is a new open-source tool that automates running Hayabusa across multiple KAPE collections, mounting disk images read-only and hashing them before and after processing. Each host gets its own Hayabusa report, and results are rolled into a single cross-host triage dashboard, eliminating manual stitching between runs.
EvidenceForge 2.2.0a2 Adds Linux ARM Support
Cisco Talos has released EvidenceForge 2.2.0a2, a pre-release update that extends Linux support to both ARM and x86_64 architectures. EvidenceForge Studio is now available on Linux alongside a streamlined workflow, broadening deployment options for DFIR practitioners across platforms.
GLEAPP Triages Large Image Datasets Fast
GLEAPP is an open-source tool built for rapidly triaging and analyzing large media datasets, carving images and extracting metadata including GPS location data visualized on offline maps. It supports hash sets, ICAC-specific data, and facial analysis, making it particularly relevant for investigators handling large volumes of image evidence.
Industry News
Flax Typhoon Hunt Behaviors Beyond Domain Seizure
FBI and partner agencies seized seven domains tied to China’s Integrity Technology Group, but domain takedowns leave persistent footholds untouched. SoftEther VPN clients masquerading as conhost.exe, EWS mailbox bots, password spraying across multiple Exchange endpoints, and DCSync requests from non-DC hosts are the behaviors worth hunting. Scope the full compromise first, then evict in a single coordinated action using CISA’s Eviction Strategies Tool.
DigitalCorpora Seeks New Steward After 20 Years
DigitalCorpora, a free 19TB open dataset underpinning digital forensics and security research worldwide, is seeking a new steward after two decades under its current maintainer. The resource hosts foundational data used by researchers and practitioners globally, and its continuity depends on finding a qualified individual, group, or institution willing to take over operations.
Read more (osdfir.blogspot.com)
Research & Techniques
Python ._pth File Hides Loader From Process Telemetry
Attackers abused a legitimate, PSF-signed Python interpreter dropped in a user’s Downloads folder, exploiting CPython’s path configuration file (._pth) to execute a malicious payload with no command-line arguments visible in process telemetry. Sysmon Event ID 15, not the more commonly collected Event ID 11, is required to capture the file’s contents and reveal the attack chain. The technique renders standard command-line argument hunting ineffective, requiring defenders to monitor ._pth file creation outside known Python install paths.
Read more (activesoc.blackhillsinfosec.com)
VeraKey Acquisition Resets FSEvents on iPhones
FSEvents logs may be absent from VeraKey full file system extractions not because they never existed, but because the acquisition process resets the fseventsd-uuid and clears history. Testing across two iPhones and eight prior extractions confirmed the issue, raising serious evidence integrity concerns. Magnet has confirmed a hotfix is in development.
Training & Events
ICAC Investigator Quick Reference Guide Launches
A new two-page quick reference guide for ICAC investigators compiles clickable links to free resources spanning digital forensics, mobile forensics, legal guidance, victim support, and training. Designed for investigators who lack access to formal ICAC training, it organises resources around common investigative needs. Volume 2 is already planned, with a focus on mental wellness and grant funding opportunities.