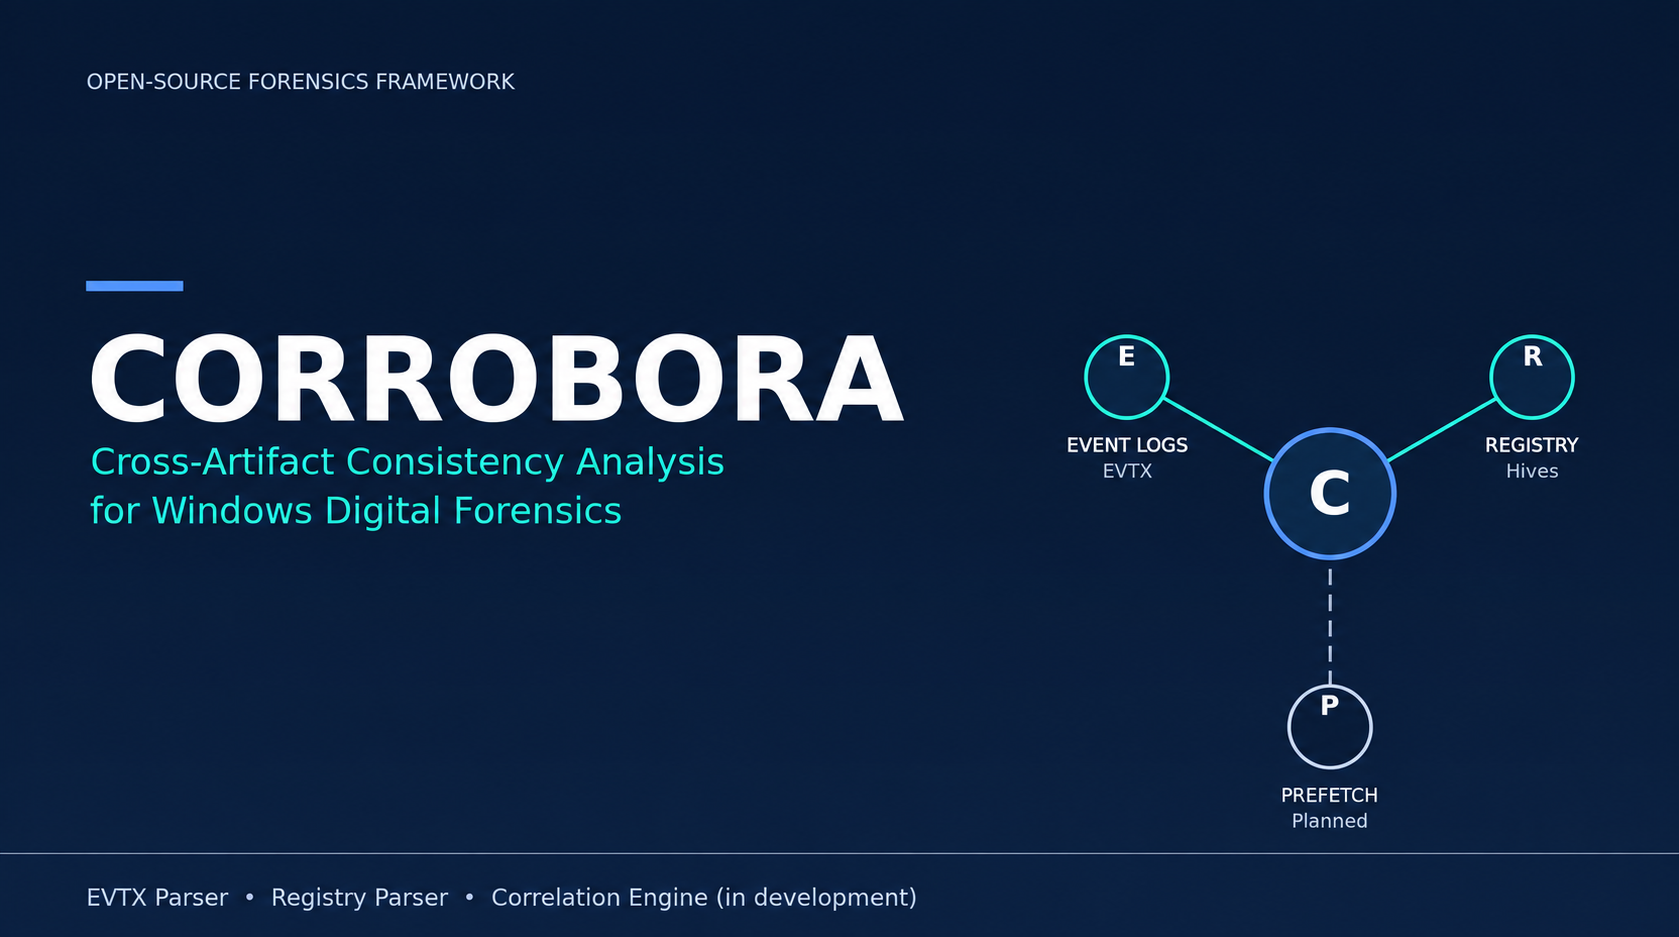
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
Radim Motycka, Founder, Proofsnap

Radim Motycka, Founder, Proofsnap

Why screenshots alone may not be enough: ProofSnap founder Radim Motycka explains how hashes, timestamps, WARC, network artefacts and independent verification can strengthen the preservation of web evidence....read more

How To Use The Updated Oxygen Forensic SQLite Viewer

Amanda: Hey everyone, It’s Amanda Mahan with Oxygen Forensics’ training team. Welcome back to Oxygen Forensic Detective’s weekly knowledge nuggets. This one’s going to be on our SQLite database viewer and our query builder that’s built into the tool.  Hey

2021 2Q MD-Series Release Note Highlights

MD-NEXT v1.89.19~v1.90.02  Samsung Full Filesystem Extraction for Android 11 – Supports 20 models of Galaxy S10, Galaxy Note10 Series with Exynos Chipset. Huawei Kirin 970/980/990/9905G Chipset Full Filesystem extraction – Supports 32 models including Honor Note 10, P20, P20 Pro,

Key Benefit Of Binalyze Forensic Features For SIEM Solutions

Due to the increase of cyber malicious activities and the need for companies to react as fast as possible to these incidents every organization needs proactive solutions for protecting its sensitive data and detecting suspicious activities in real-time.  Having a

Release The DRONE! : Meet Your 24/7 Available DFIR Expert

The first innovation of Binalyze was decreasing the evidence collection time to minutes from hours, if not days. The second one was making the overall acquisition process a fully automated workflow.  Both of these innovations are delivered by our TACTICAL

Automating And Sharing Digital Forensics Knowledge Through Hansken

What if you could automate digital forensics processes, centralize them, and then offer them at scale through the internet? Researchers at the Netherlands Forensic Institute (NFI) set out to answer the first question—then took the path through the second and

Exterro Participates In Gen CybHER Camp At Dakota State University

It was exciting to be in person at the annual GenCybHER Girls in Cybersecurity Camp at Dakota State University, June 20-24, 2021. This year, 66 girls in grades 6 through 9 attended from 5 states (SD, ND, MN, IA, NE). Our hands-on lab,

FTK Feature Focus: Optimizing Processing Options Part 2

Justin Tolman: Episode five, and we’re already doing a sequel. We’re taking another look at optimizing our processing in FTK Feature Focus. Welcome back. This is episode five of Feature Focus. I’m Justin Tolman. I’m the Director of Training over

Grayshift Virtual Briefing Room – July 8th

Join our upcoming Grayshift Briefing Room Mobile devices are a major source of evidence but obtaining that evidence can be challenging. There are instances where the suspect, victim, or witness is reluctant to release their device, which can result in