Block Hash Scan: Illegal File Triage Completed On Site

Hero Image

See how MD-LIVE’s Block Hash Scan helps investigators identify known target files on-site without reading every file in full, and what a zero-detection result really means....

Today's headlines 2 Oct 2026

Forensic Focus Digest, October 02 2026

Forensic Focus Digest, October 02 2026

Discover what’s new on Forensic Focus – explore the biggest challenges in mobile forensics with Magnet Forensics, discover faster investigative workflows with Cellebrite Genesis, meet Radim Motycka, founder of Proofsnap, and more....read more
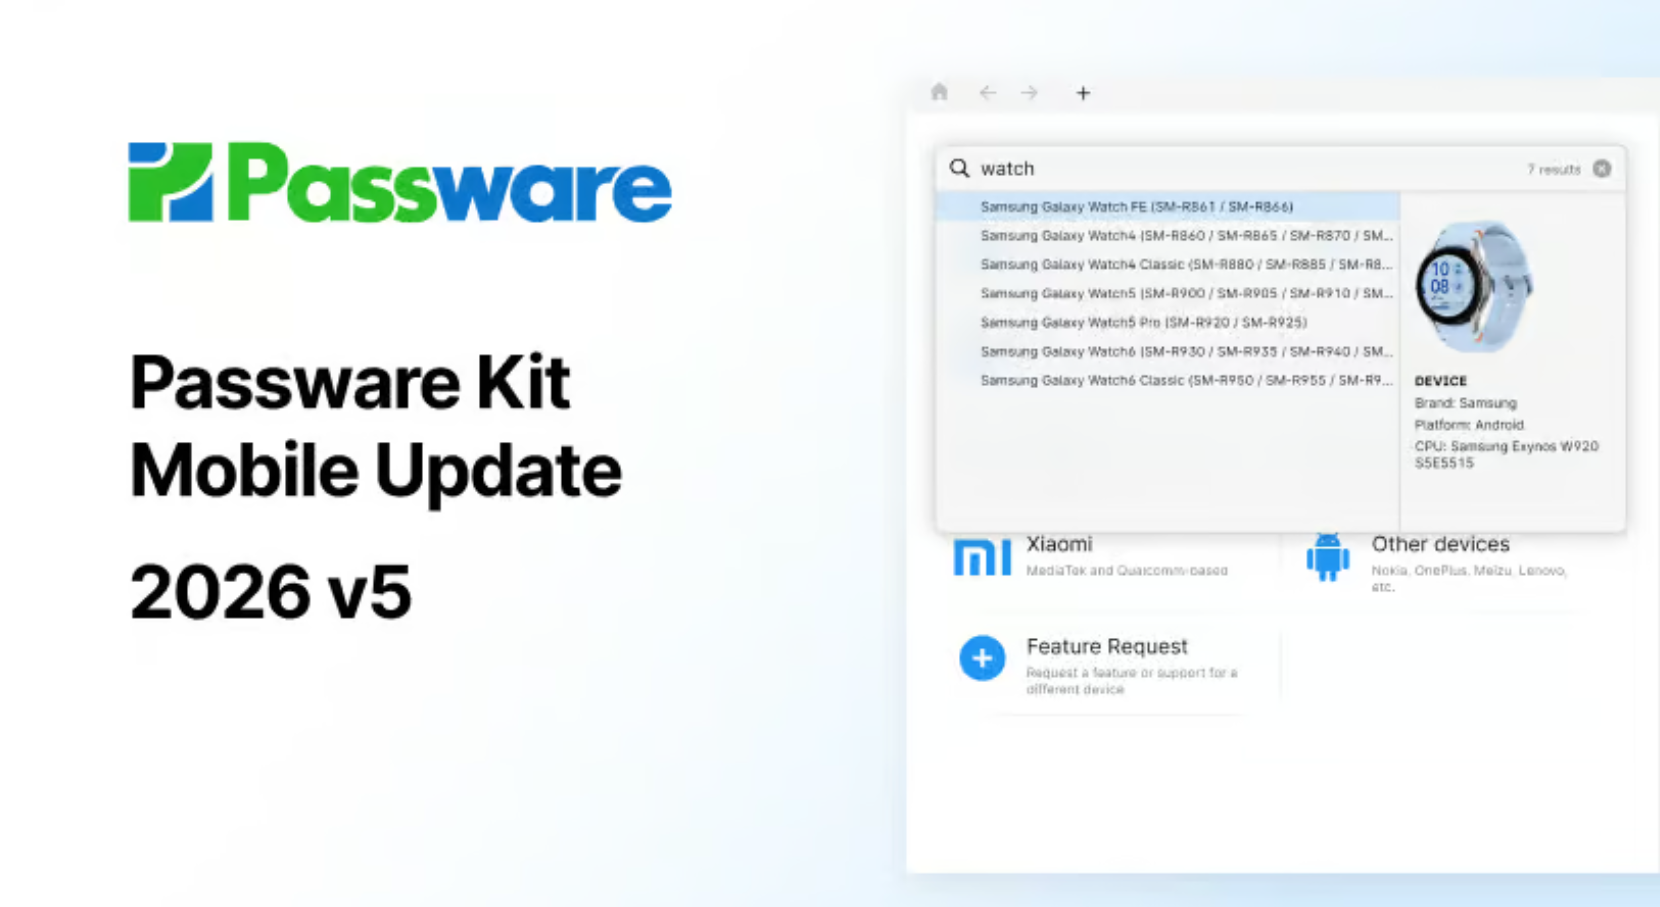
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 expands mobile forensics with Samsung Galaxy Watch 4/5/6 passcode recovery and data extraction, new Samsung and Unisoc device support, Enpass for Android decryption, and faster workflows with immediate passcode recovery....read more
Trust Is Not A Feature. It Is The Foundation.

Trust Is Not A Feature. It Is The Foundation.

Discover what agencies should expect from a digital forensics partner and how MSAB puts transparency, accountability and long-term commitment at the heart of its work....read more

Android Forensics Study of Password and Pattern Lock Protection

Posted by Oxygen Software "Let’s see what Pattern Lock is, how to access, determine or even get rid of it? We’ll also speak about Password Lock Protection and find out what it has in common with Pattern Lock. And finally

Skype in eDiscovery

by Stuart Clarke, 7Safe "The EDRM (Electronic Discovery Reference Model) is a widely accepted workflow, which guides those involved in eDiscovery. Typically, the identification and collection phases see email and common office documents harvested, but as technology moves forward is

Forensic Toolkit v3 Tips and Tricks – On a budget

Posted by Brian K. Glass "While researching FTK 3X and Oracle, you just recently discovered that the best configuration of your Oracle database would be on a solid state drive (SSD). Solid state drives give the maximum level of performance

Anonymous, what does it mean?

Posted by forens245 "Anonymous, a word which Merriam-Webster describes as: of unknown authorship or origin, not named or identified, or lacking individuality, distinction, or recognizability. There are some in this world that wish to remain anonymous, not named or identified.

CCL-Forensics offers “dunk!” for cookie files

CCL-Forensics has developed “dunk!”, a software utility which parses cookie files, and presents the investigator with the data they contain. A free trial version of dunk! is available at www.ccl-forensics.com/dunk which gives complete functionality for a limited time. Thereafter licences

GCHQ to offer British firms expertise in cybercrime

Some of the secret technologies created at the government’s giant eavesdropping centre GCHQ are to be offered to private industry as part of new cyber security strategy being unveiled by ministers on Friday. The idea is likely to be one

French Gendarmerie Nationale chooses Cellebrite’s UFED

The French Gendarmerie Nationale has equipped its national N-TECH force with Cellebrite’s Universal Forensic Extraction Device (UFED) for its mobile forensic investigations. The Gendarmerie Nationale, in charge of public safety in France, is using the UFED to extract information from

Paraben Releases P2 Commander v2.0

Paraben is pleased to announce the release of P2 Commander v2.0. Here are some feature highlights: * New memory dump parser* Added support for Exchange 2010 (.EDB)* Added support for Chrome history, cookies, auto fill items, keywords, and login analysis*

Forensic Toolkit v3 Tips and Tricks ― Not on a Budget

A couple of weeks ago, Brian Glass posted a very helpful comment, Forensic Toolkit v3 Tips and Tricks — on a Budget.  His comment focused on how to “get close to SSD performance on the cheap” and he discussed the

iPhone Tracking – from a forensic point of view

– Introduction – iPhoneTracking is sexy!!! Every mobile forensic suite, at least the ones dealing with iPhones, are providing it proudly. iPhoneTracking also has been a hot topic in the media all around the globe. People stated, that there is

Android Forensics Study of Password and Pattern Lock Protection

Let’s see what Pattern Lock is, how to access, determine or even get rid of it? We’ll also speak about Password Lock Protection and find out what it has in common with Pattern Lock. And finally we’ll try to understand 

Mike’s Forensic Tools – Cookie Cutter

A simple app to decode the data held within Google Analytics Cookies. The data can be identified by “__UTM” starting each section. The data holds: records, the number of visits to a website, the first, last and current visit dates;

Publishing articles at Forensic Focus

Forensic Focus is always keen to publish articles, papers or blog posts of interest to the digital forensics community. Articles are published not only online but also included in the monthly newsletter (sent to over 12,00 subscribers) and promoted via

SC Suite v4.4 Released.

A new version of SC Suite is available, version 4.4 now includes more tools to analyse and extract information from a variety of file types and utilities to assist in every day tasks. Continuing user feedback has resulted in the