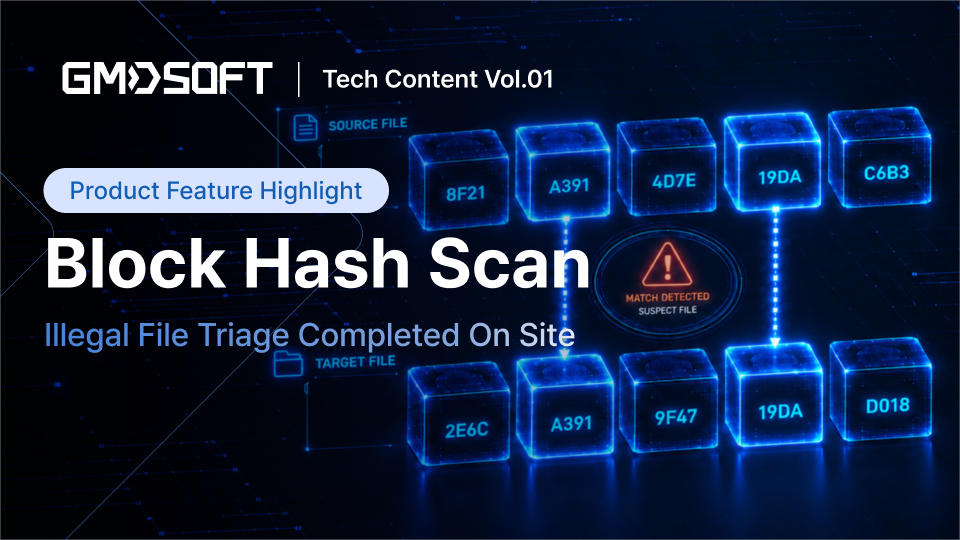
Block Hash Scan: Illegal File Triage Completed On Site

Hero Image

See how MD-LIVE’s Block Hash Scan helps investigators identify known target files on-site without reading every file in full, and what a zero-detection result really means....

Today's headlines 2 Oct 2026

Forensic Focus Digest, October 02 2026

Forensic Focus Digest, October 02 2026

Discover what’s new on Forensic Focus – explore the biggest challenges in mobile forensics with Magnet Forensics, discover faster investigative workflows with Cellebrite Genesis, meet Radim Motycka, founder of Proofsnap, and more....read more
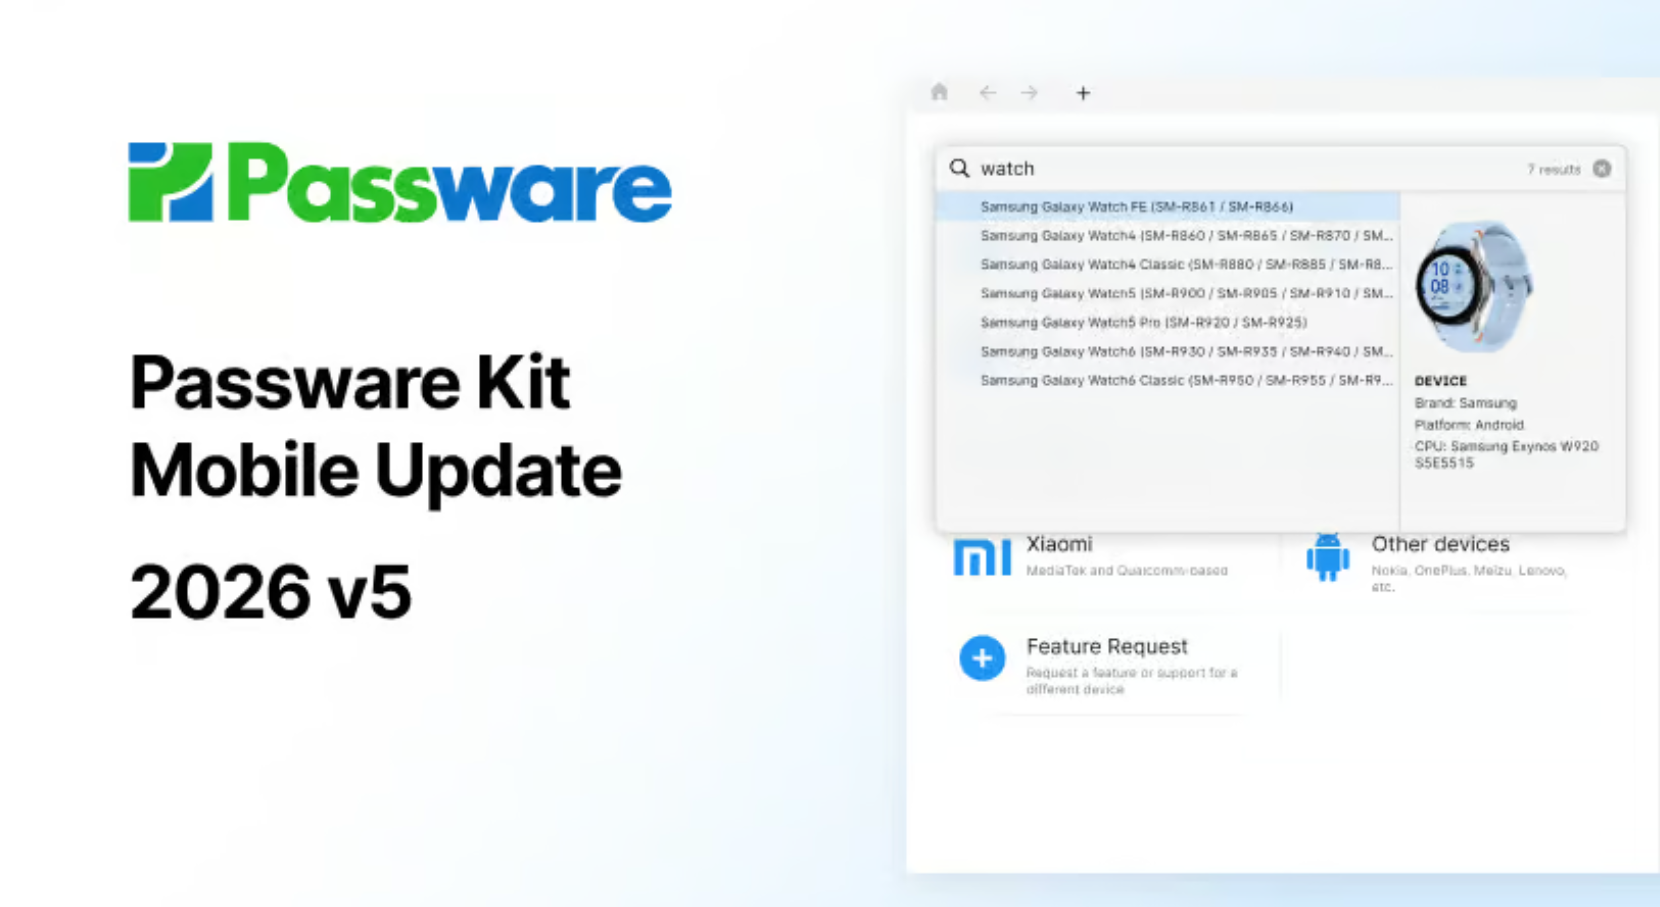
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 expands mobile forensics with Samsung Galaxy Watch 4/5/6 passcode recovery and data extraction, new Samsung and Unisoc device support, Enpass for Android decryption, and faster workflows with immediate passcode recovery....read more
Trust Is Not A Feature. It Is The Foundation.

Trust Is Not A Feature. It Is The Foundation.

Discover what agencies should expect from a digital forensics partner and how MSAB puts transparency, accountability and long-term commitment at the heart of its work....read more

Standard Units in Digital Forensics

by Dr Chris Hargreaves Lecturer at the Centre for Forensic Computing at Cranfield University in Shrivenham, UK. One of the earliest lectures in the MIT Openware programme in Physics begins with the lecture “Units and Dimensional Analysis”. Units of measurement

PitchLake – a tar pit for scanners

by Simon Biles Founder of Thinking Security Ltd., an Information Security and Risk Management consultancy firm based near Oxford in the UK. We’ve had two bank holidays in a row here in the UK – first off for Easter, then

How to Create an Open Source Network Forensics Appliance

By Ondrej Krehel Chief information security officer at Identity Theft 911 [email protected] IntroductionEncryption and anti-forensics attacker techniques are commonly encountered in incident response investigations, while the power of network forensics intelligence is often overlooked by busy IT and legal departments.

The Grid for Crime Prevention (G4CP) in Wales

by Sian Haynes and Stilianos Vidalis University of Wales, Newport Fujitsu is set to bring high-performance computing (HPC) to Wales. They will provide a distributed grid which is a project set over five-years costing up to £40 million. The grid

The End of Digital Forensics?

by Craig Ball When Microsoft introduced its Encrypting File System (EFS) in Windows 2000, the Cassandras of computer forensics peppered the listserves with predictions that the days of digital forensics were numbered. Ten years on and hundreds of systems acquired,

Evaluating Mobile Telephone Connection Behaviour – Part 2

The Basics of Evaluating Connection Records by Sam Raincock, IT and telecommunications expert witness Connection RecordsWithin the UK, details of past telephone connections are stored by the network providers. The minimum storage is advised by the Data Retention (EC Directive)

Biles’ Hierarchy of Disaster Recovery Needs

by Simon Biles Having failed to keep up with my New Year’s resolution of being more organised (the observant of you might have noticed the absence of a February column), it’s nice to be able to move into a new

The Question Of Cyber Terrorism

by Robert Murrill [email protected] Executive Summary This paper will take a look at Cyber terrorism and explaining what it is and what it isn’t by showing how closely related Cyber Terrorism and Cyber Warfare are. Although the affects of both

Personal Branding for Digital Forensics Jobseekers

by David Sullivan Looking at the job adverts here on Forensic Focus shows that after a really sluggish period the number of vacancies available in computer forensics and electronic disclosure is increasing. Many forensics professionals who would normally have changed

Geotags: Friend or Foe?

by David Benford Director, Blackstage Forensics I recently wrote a research paper, “Geotag Data: The Modification of Evidence on the Apple iPhone”, based around the possibility of modifying geotag evidence on the Apple iPhone. A test was performed as part

Is the NTSB a model for incident response?

by Sean McLinden Recently, the events surrounding the defacement of the HBGary Web site and publication of sensitive data were being bantered about on a number of forensic, security and incident response sites. As is typical for these kind of

I’m here! Now what?

by Ken Pryor Working for a small police department in a rural area, my opportunities to do digital forensic work on real cases are much fewer and farther between than those who work in large departments or in the private

Challenges of Smart Phone Forensics

by Rob Adams ACE, CDIA+ SALIX Mobile devices have become an essential component of our daily lives. These devices keep us connected and act as so much more than the cell phones and portable music players of the 1990’s. It

2010 report of digital forensic standards, processes and accuracy measurement

Joshua Isaac James, Pavel Gladyshev {Joshua.James, Pavel.Gladyshev}@UCD.ie Centre for Cybercrime Investigation University College Dublin Belfield, Dublin 4 Ireland 1. Introduction From December 7th 2010 to December 12th 2010 a survey on Digital Investigation Process and Accuracy was conducted in an