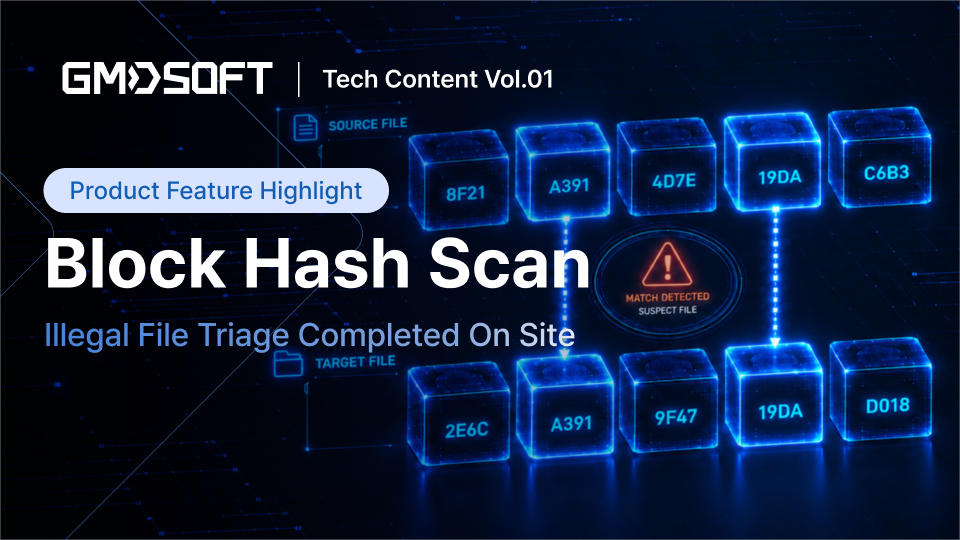
Block Hash Scan: Illegal File Triage Completed On Site

Hero Image

See how MD-LIVE’s Block Hash Scan helps investigators identify known target files on-site without reading every file in full, and what a zero-detection result really means....

Today's headlines 2 Oct 2026

Forensic Focus Digest, October 02 2026

Forensic Focus Digest, October 02 2026

Discover what’s new on Forensic Focus – explore the biggest challenges in mobile forensics with Magnet Forensics, discover faster investigative workflows with Cellebrite Genesis, meet Radim Motycka, founder of Proofsnap, and more....read more
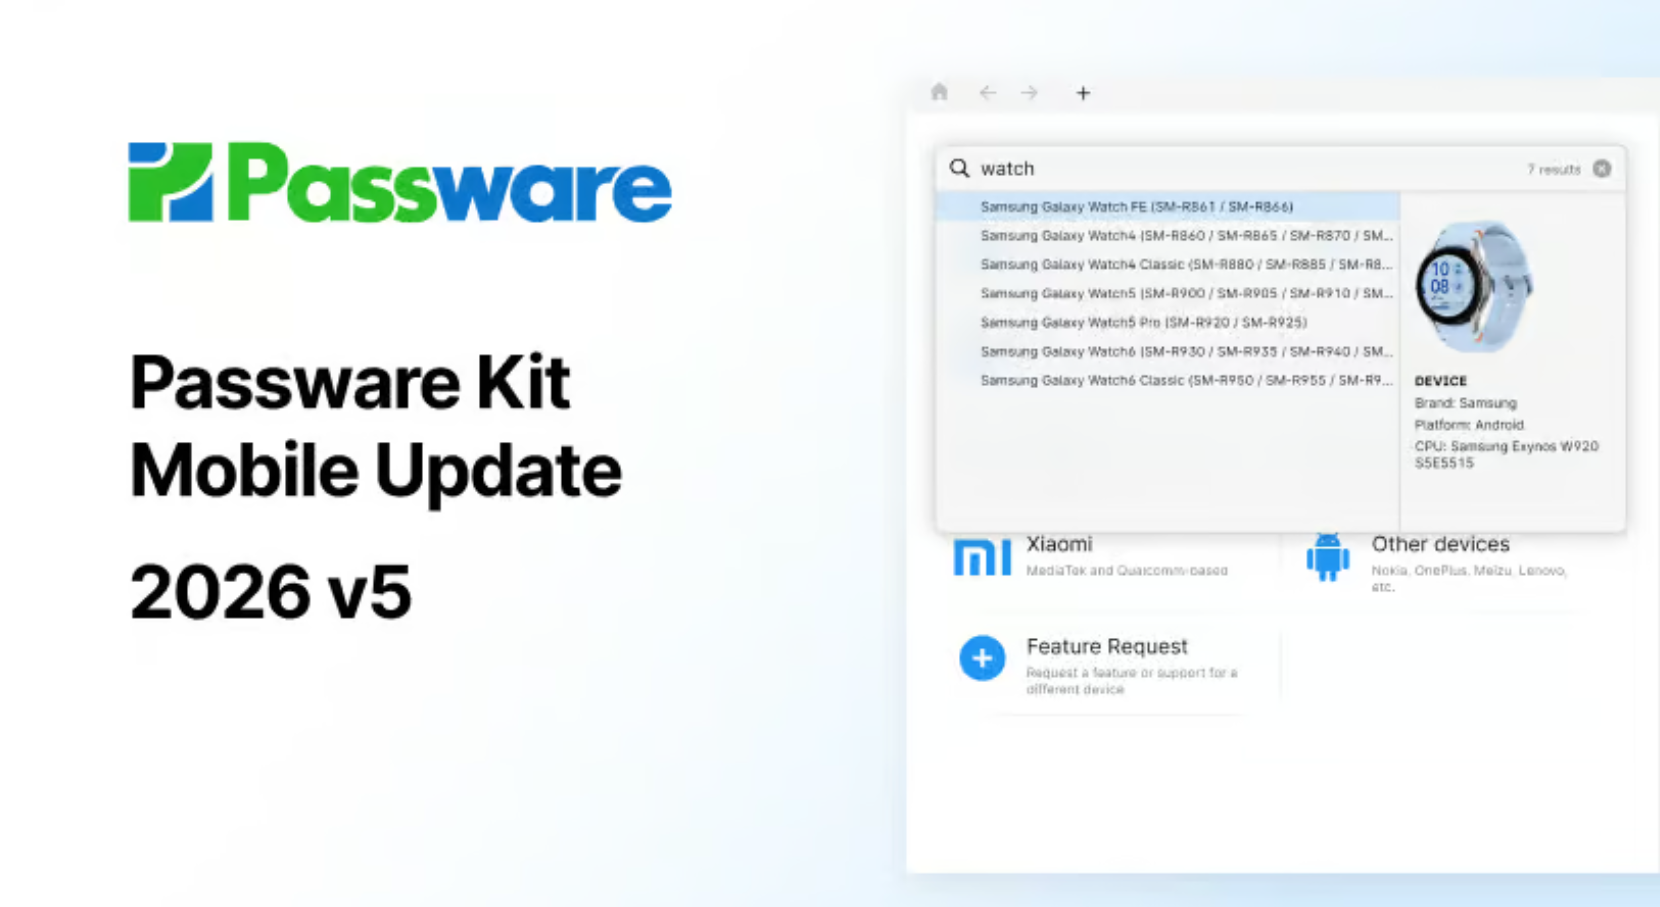
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 expands mobile forensics with Samsung Galaxy Watch 4/5/6 passcode recovery and data extraction, new Samsung and Unisoc device support, Enpass for Android decryption, and faster workflows with immediate passcode recovery....read more
Trust Is Not A Feature. It Is The Foundation.

Trust Is Not A Feature. It Is The Foundation.

Discover what agencies should expect from a digital forensics partner and how MSAB puts transparency, accountability and long-term commitment at the heart of its work....read more

Four arrested in the Netherlands in FBI cyber attack probe

Four people have been arrested in the Netherlands as part of an FBI-led investigation into computer hacking, according to US media reports. Sixteen people have been picked up in the US and one, aged 16, in Britain, the reports say.

My cat did it – honest, Guv!

and he did it via remote access… by Sam Raincock, IT and telecommunications expert witness When evaluating computer forensics cases the tricky part is often not just evaluating what is found but determining how it came to reside there. “It

Side channel attacks

by Simon Biles Founder of Thinking Security Ltd., an Information Security and Risk Management consultancy firm based near Oxford in the UK Forensics is all about evidence, but the trick is knowing where to find it! Locard’s exchange principle effectively

Digital Forensics and ‘self-tracking’

by Dr Chris Hargreaves, lecturer at the Centre for Forensic Computing at Cranfield University in Shrivenham, UK This month’s article is based very loosely around a recent 5-minute talk from Gary Wolf (link here) which explores the concept of ‘self-tracking’

It’s not always what you find…

by Sam Raincock, IT and telecommunications expert witness In digital forensics we are often asked to determine the presence of evidence. However, what happens when we do not find anything? How do we prove something wasn’t there? Proving something is

A cloud by any other name…

by Simon Biles Founder of Thinking Security Ltd., an Information Security and Risk Management consultancy firm based near Oxford in the UK. “You have to know the past to understand the present” – Dr. Carl SaganIf you have been kind

How to seduce your (potential) computer forensics employer

by David Sullivan We all over-complicate things and this is certainly true when seeking a new job. Essentially, to be successful at a Computer Forensics interview you just need to demonstrate two things:1. You have the technical skills needed to

Windows Search forensics

Analyzing the Windows (Desktop) Search Extensible Storage Engine database by Joachim Metz [email protected] Summary While some may curse Windows Vista for all its changes, for us forensic investigators it also introduced new interesting ‘features’. One is the integration of Windows

Sometimes it’s all about timing

First published June 2010 by Sam Raincock, IT and telecommunications expert witness When a crime happens, the time of the events may be critical to the legal case. However, how are these times established? Is it the time alleged by

Publication: an ethical dilemma for digital forensics research?

First published June 2010 by Dr Chris Hargreaves, lecturer at the Centre for Forensic Computing at Cranfield University in Shrivenham, UK Ethical issues in science are commonplace; examples such as cloning, climate change and genetic engineering are all subject to

Flash drives and acquisition

First published June 2010 by Dominik Weber, Senior Software Architect for Guidance Software, Inc. “Take a look at this”. It started simply with that.A co-worker was looking into some strange issue with an acquisition of a flash drive. It seemed

Unusual devices

First published June 2010 by Sean McLinden In 2007, New Jersey Governor Jon Corzine made the news twice for a single event. The first time was the report of a car accident on the Garden State Parkway in which he

Digital forensic sampling

The application of statistical sampling in digital forensics Authors: Robert-Jan Mora and Bas Kloet Company: Hoffmann Investigations, Almere, The Netherlands URL: http://en.hoffmannbv.nl Date: 27th March 2010 Version:1.0 Table of contents 1 Introduction 2 Sampling basics 2.1 The necessity for sampling

EnCase file copying and Windows Short File Names

First published May 2010 By Lee Hui Jing, EnCe Edited by Sarah Khadijah Taylor ABSTRACT A couple of months ago, one of my clients, an Investigating Officer from a Law Enforcement Agency, had requested me to extract some of the

The (Nearly) Perfect Forensic Boot CD – Windows Forensic Environment

by Brett Shavers   Introduction Figure 1: WWW.FORENSICS-INTL.COM As a quick introduction to the Windows Forensics Environment (WinFE); it is a bootable CD, based on the Windows Pre-Installed Environment (PE), with a few changes to create a forensically sound boot