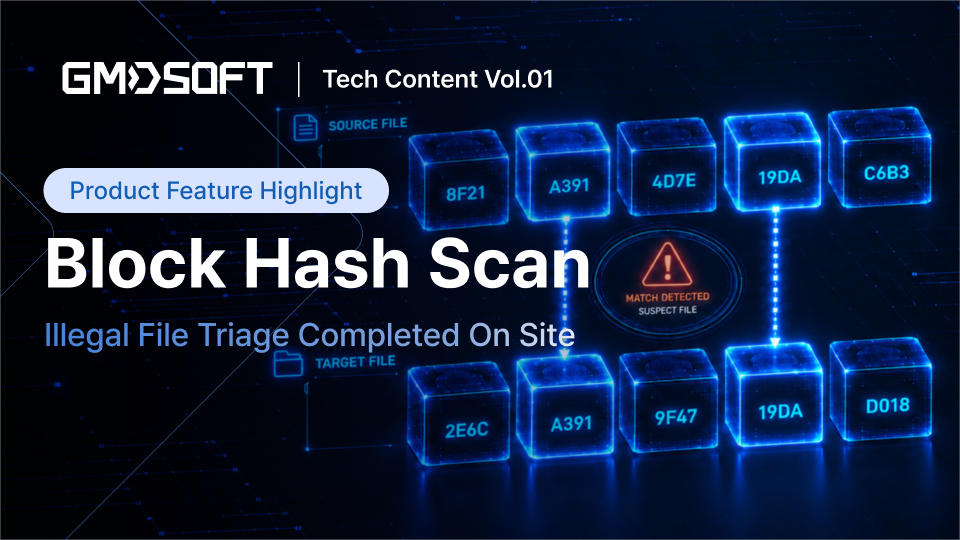
Block Hash Scan: Illegal File Triage Completed On Site

Hero Image

See how MD-LIVE’s Block Hash Scan helps investigators identify known target files on-site without reading every file in full, and what a zero-detection result really means....

Today's headlines 2 Oct 2026

Forensic Focus Digest, October 02 2026

Forensic Focus Digest, October 02 2026

Discover what’s new on Forensic Focus – explore the biggest challenges in mobile forensics with Magnet Forensics, discover faster investigative workflows with Cellebrite Genesis, meet Radim Motycka, founder of Proofsnap, and more....read more
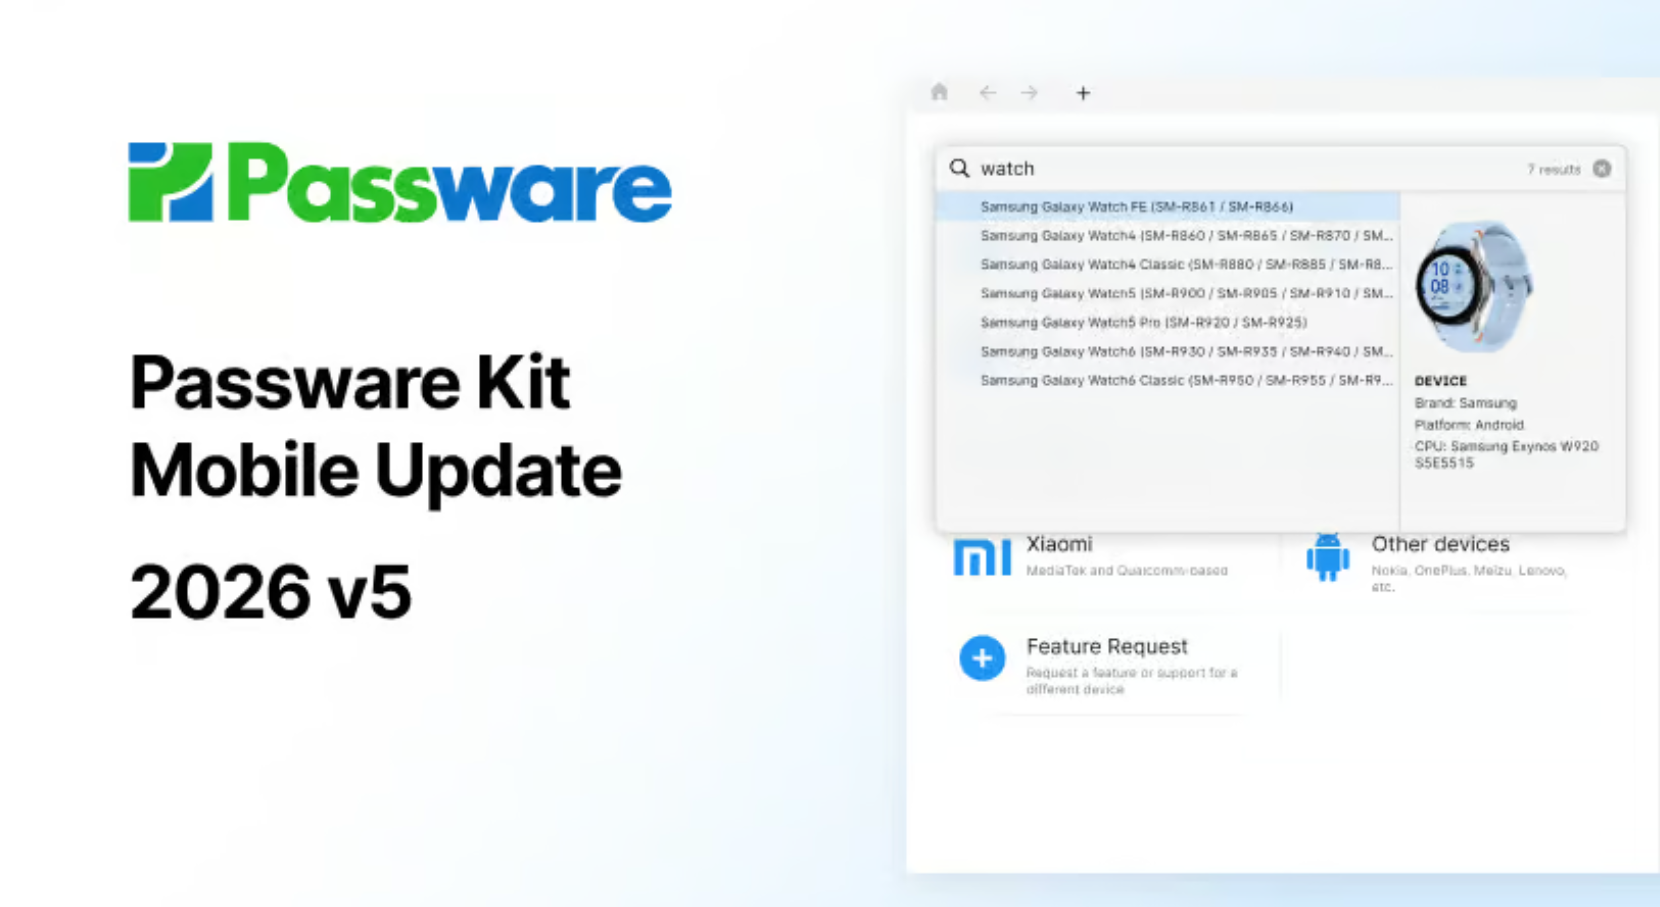
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 expands mobile forensics with Samsung Galaxy Watch 4/5/6 passcode recovery and data extraction, new Samsung and Unisoc device support, Enpass for Android decryption, and faster workflows with immediate passcode recovery....read more
Trust Is Not A Feature. It Is The Foundation.

Trust Is Not A Feature. It Is The Foundation.

Discover what agencies should expect from a digital forensics partner and how MSAB puts transparency, accountability and long-term commitment at the heart of its work....read more

Build Your Own Digital Evidence Collection Kit

First published June 2009 by David Kovar, NetCerto, Inc. Overview Collecting evidence accurately is clearly a foundational element for any ediscovery or forensics analysis project. The equipment required is important, but so are the supporting items – office supplies, forms,

Checking Masts – Cell Site Analysis (CSA)

First published March 2009 by Greg Smith Mobile Telephone Evidence & Forensics trewmte.blogspot.com Since linking with Jamie Morris at Forensic Focus to create a Mobile Forensics Discussion Forumto bring mobile telephone evidence to a wider audience, I have had several

Recording Telephone Calls

First published March 2009 by Greg Smith Mobile Telephone Evidence & Forensics trewmte.blogspot.com A question that often gets asked is “Can I record a telephone call?” and the answer to that is that you can (according to publicly available material),

Mobile Phone and GPS Forensics – Some Thoughts

First published February 2009 by Greg Smith Mobile Telephone Evidence & Forensics trewmte.blogspot.com Mobile telephones are the predominate wireless telecommunications device throughout the world and most certainly in the UK they predominate other technologies, where ownership has reached well over

Malicious Phone Call Legislation in the UK

First published February 2009 by Greg Smith Mobile Telephone Evidence & Forensics trewmte.blogspot.com It is being noted that there is an exponential growth in harassing and intimidating calls from financial companies, card companies and from outsource debt collection firms chasing

SonyEricsson Hidden Evidence

First published February 2009 by Greg Smith Mobile Telephone Evidence & Forensics trewmte.blogspot.com I have discovered that it is possible when manually examining some SonyEricssons (such as “K” range etc) that after a user has deleted the Last Number Dialled

TomTom GPS Device Forensics

First published January 2009 Written by Ben LeMere ([email protected]) & Andy Sayers ([email protected]) For more information visit GPSForensics.org Introduction: The sales of portable navigation devices are at an all time high. Last year, more than forty million portable GPS devices

Passive Network Security Analysis with NetworkMiner

First published January 2009 by Erik Hjelmvik networkminer.sourceforge.net It is disturbing how often networks are not properly documented in terms of IP plans, network segmentations and network security. Having a good view of the network is essential when performing a

A Discussion of Virtual Machines Related to Forensics Analysis

First published November 2008 by Brett Shavers (PDF version here) The Virtual Machine (VM)Description of the Virtual Machine The Virtual Machine Concept in Brief Virtual machines are not new and have been in use for well over a half century.

Email Evidence – Now You See it, Now You Don’t!

First published October 2008 By Sandy Boucher and Barry Kuang, Intelysis Corp. Background With the ever increasing role of computers and electronic communications in both our business and personal lives, emails have taken on a key evidentiary role in many

Linux ‘dd’ basics

First published March 2008 Linux dd can be a powerful and flexible tool to have in your box.You will find it installed by default on the majority of Linux distributions available today and it can be used for a multitude

The International Society of Forensic Computer Examiners (ISFCE)

by Joleyn Smithing, ISFCE The International Society of Forensic Computer Examiners (ISFCE)is dedicated to the advancement of the science of forensic computer examinations. Established in 2002, the ISFCE began as a result of the efforts of Mr. John Mellon. A