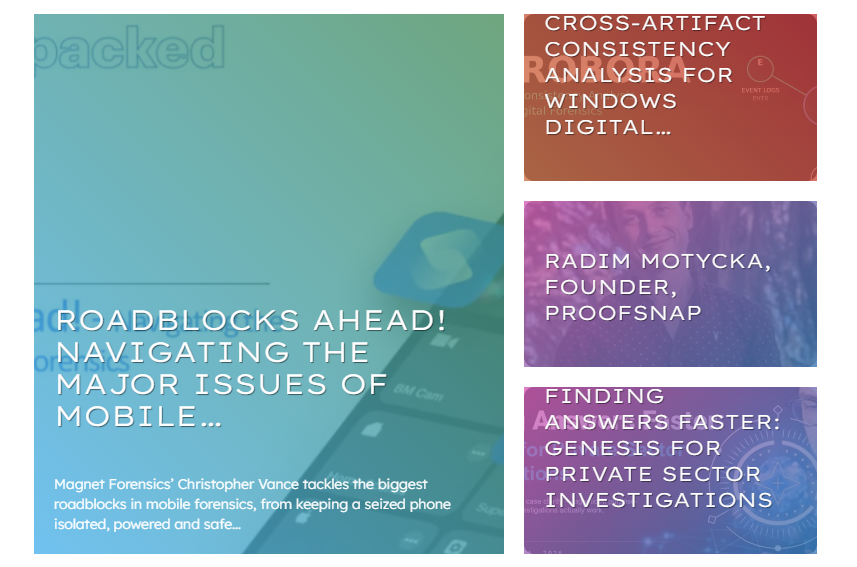
Block Hash Scan: Illegal File Triage Completed On Site

Hero Image

See how MD-LIVE’s Block Hash Scan helps investigators identify known target files on-site without reading every file in full, and what a zero-detection result really means....

Today's headlines 2 Oct 2026

Forensic Focus Digest, October 02 2026

Forensic Focus Digest, October 02 2026

Discover what’s new on Forensic Focus – explore the biggest challenges in mobile forensics with Magnet Forensics, discover faster investigative workflows with Cellebrite Genesis, meet Radim Motycka, founder of Proofsnap, and more....read more
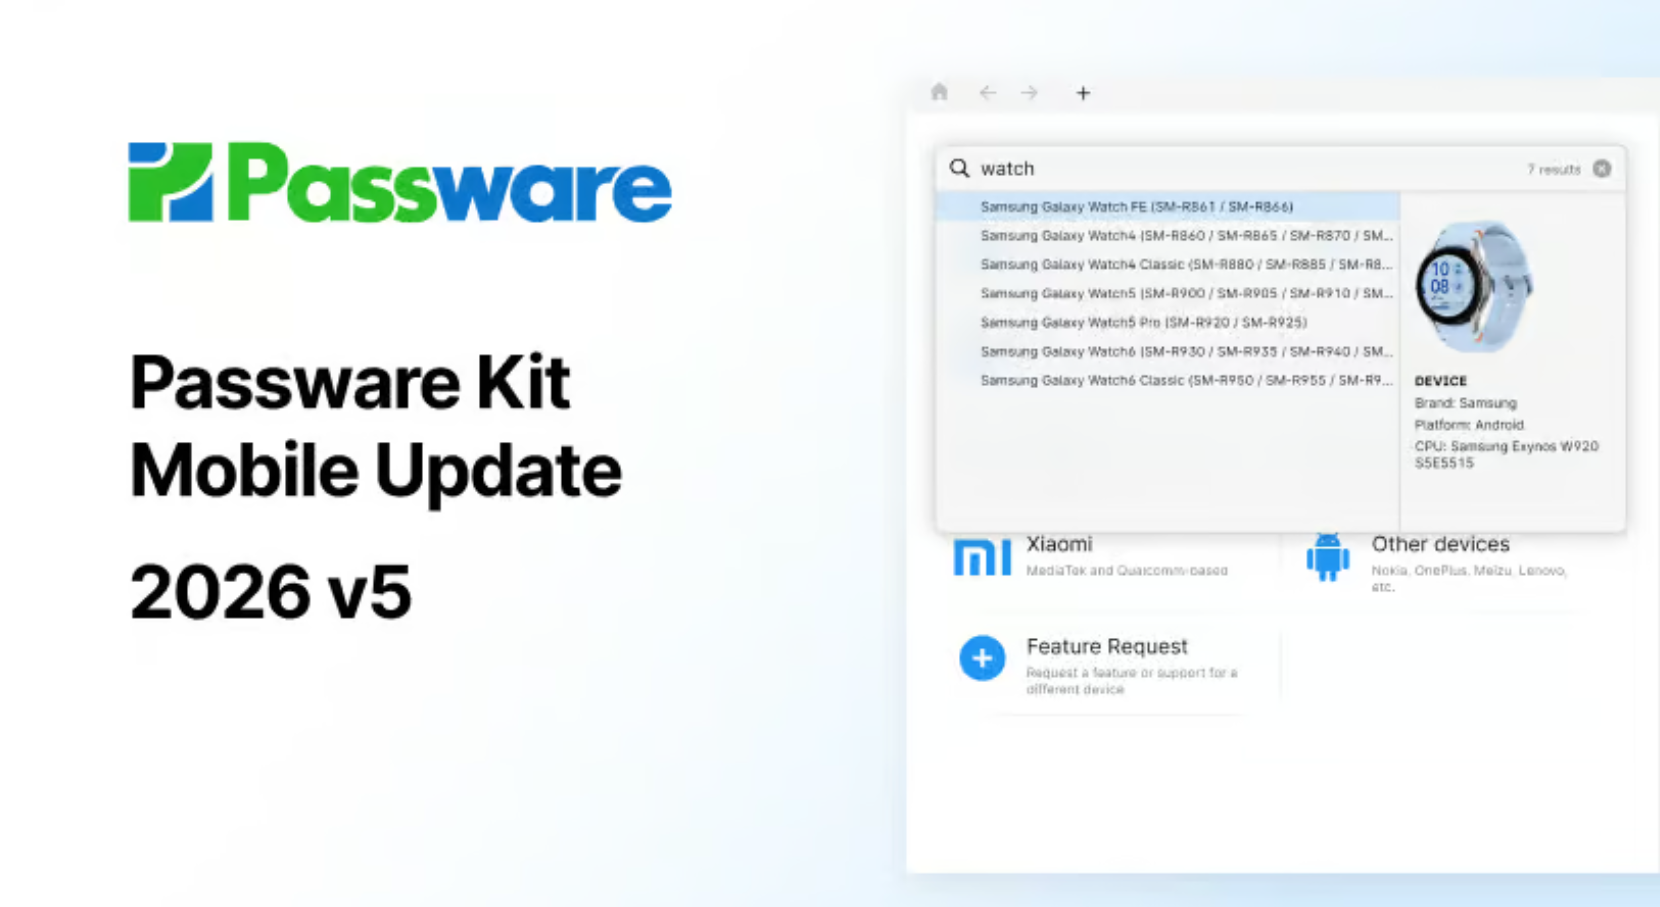
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 expands mobile forensics with Samsung Galaxy Watch 4/5/6 passcode recovery and data extraction, new Samsung and Unisoc device support, Enpass for Android decryption, and faster workflows with immediate passcode recovery....read more
Trust Is Not A Feature. It Is The Foundation.

Trust Is Not A Feature. It Is The Foundation.

Discover what agencies should expect from a digital forensics partner and how MSAB puts transparency, accountability and long-term commitment at the heart of its work....read more

Digital forensics of the physical memory

First published September 2005 Mariusz Burdach [email protected] Warsaw, March 2005 last update: July 11, 2005 Abstract This paper presents methods by which physical memory from a compromised machine can be analyzed. Through this methods, it is possible to extract useful

An Analytical Approach to Steganalysis

First published August 2005 by James E. Wingate, CISSP-ISSEP, CISM, IAM Director, Steganography Analysis & Research Center www.sarc-wv.com Chad W. Davis Computer Security Engineer Backbone Security.Com www.backbonesecurity.com Introduction Rapidly evolving computer and networking technology coupled with a dramatic expansion in

Smart Anti-Forensics

First published June 2005 by Steven McLeod steven mcleod@ozemail com au May 2005 EXECUTIVE SUMMARY This paper highlights an oversight in the current industry best practice procedure for forensically duplicating a hard disk. A discussion is provided which demonstrates that

Phone hacking: Police probe suspected deletion of emails by NI executive

Police are investigating evidence that a News International executive may have deleted millions of emails from an internal archive, in an apparent attempt to obstruct Scotland Yard’s inquiry into the phone-hacking scandal. The archive is believed to have reached back

Data: The Basics of Computer Forensics

First published June 2005 by Edward Pscheidt www.edwardpscheidt.com Everything is created on a computer. To be more precise, almost everything that is the subject of litigation was created on a computer. Be they letters, blueprints or company books, the vast

An Investigation Into Computer Forensic Tools

First published June 2005 K.K. Arthur & H.S. Venter Information and Computer Security Architectures (ICSA) Research Group Department of Computer Science University of Pretoria Pretoria This material is based upon work supported by Telkom, IST and the NRF through THRIP.

Developing A Framework For Evaluating Computer Forensic Tools

First published May 2005 by Colin Armstrong Curtin University of Technology School of Information Systems WA Australia Abstract Forensic science is the application of science to those criminal and civil laws that are enforced by police agencies in a criminal

The Forensic Chain of Evidence Model

First published May 2005 Improving the Process of Evidence Collection in Incident Handling Procedures by Atif Ahmad Department of Information Systems, University of Melbourne, Parkville, VIC 3010, Australia Abstract This paper suggests that administrators form a new way of conceptualizing

The Essentials Of Computer Discovery

First published May 2005 by Joan E. Feldman, President Computer Forensics Inc. www.forensics.com I. INTRODUCTION Chances are good that the date you scheduled, the letter you wrote, and the inter-office message you just read have all been recorded on magnetic

Description of the FAT fsstat Output

First published May 2005 by Brian Carrier reproduced with permission from The Sleuth Kit Informer, Issue 18 Overview The output of many TSK tools is relatively easy to understand because each tool has a specific focus. For example, the outut

SpyCloud: Intel Agencies Look to Keep Secrets in the Ether

Dropbox for files, Google for mail, iCloud for well, everything. Average citizens have all kinds of options for storing their information in the cloud. Now, spies want in. Soon, our nation’s secrets may take on a slightly more nebulous form.

Interview with Scott Burkeman, Warner Scott Recruitment

"The market has been up and down in recent years, which has been characterised by the state of the wider economy. With the government cuts in public spending, there has been much uncertainty within the public sector, which has resulted

MFP: The Mobile Forensic Platform

First published May 2005 Frank Adelstein Senior Principal Scientist, ATC-NY Abstract Digital forensics experts perform investigations of machines for “triage” to see if there is a problem, as well as to gather evidence and run analyses. When the machines to

Computer Forensics 101

First published May 2005 By Susan Steen and Johnette Hassell, Ph.D. Electronic Evidence Retrieval, LLC www.electronicevidenceretrieval.com Thirty years ago computers were colossal machines utilized only by government agencies and prodigious corporations. These early machines were so large and complex that