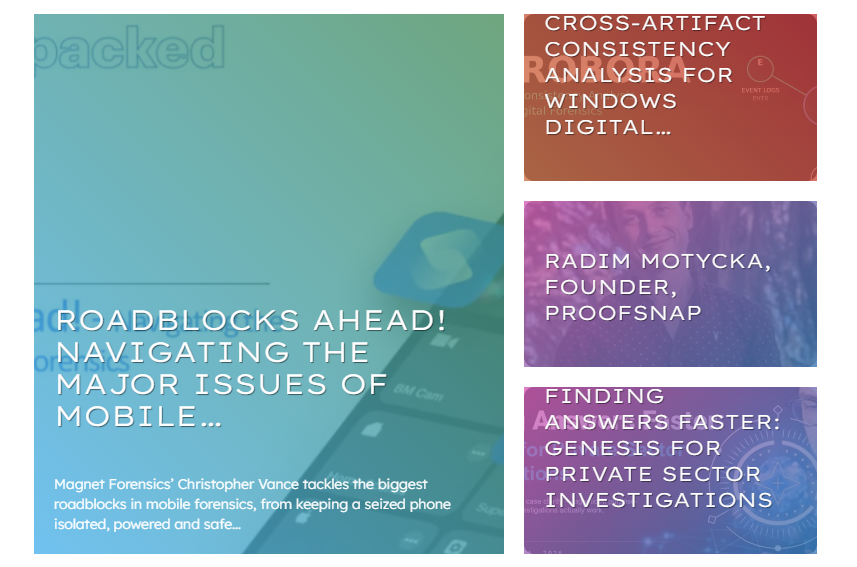
Block Hash Scan: Illegal File Triage Completed On Site

Hero Image

See how MD-LIVE’s Block Hash Scan helps investigators identify known target files on-site without reading every file in full, and what a zero-detection result really means....

Today's headlines 2 Oct 2026

Forensic Focus Digest, October 02 2026

Forensic Focus Digest, October 02 2026

Discover what’s new on Forensic Focus – explore the biggest challenges in mobile forensics with Magnet Forensics, discover faster investigative workflows with Cellebrite Genesis, meet Radim Motycka, founder of Proofsnap, and more....read more
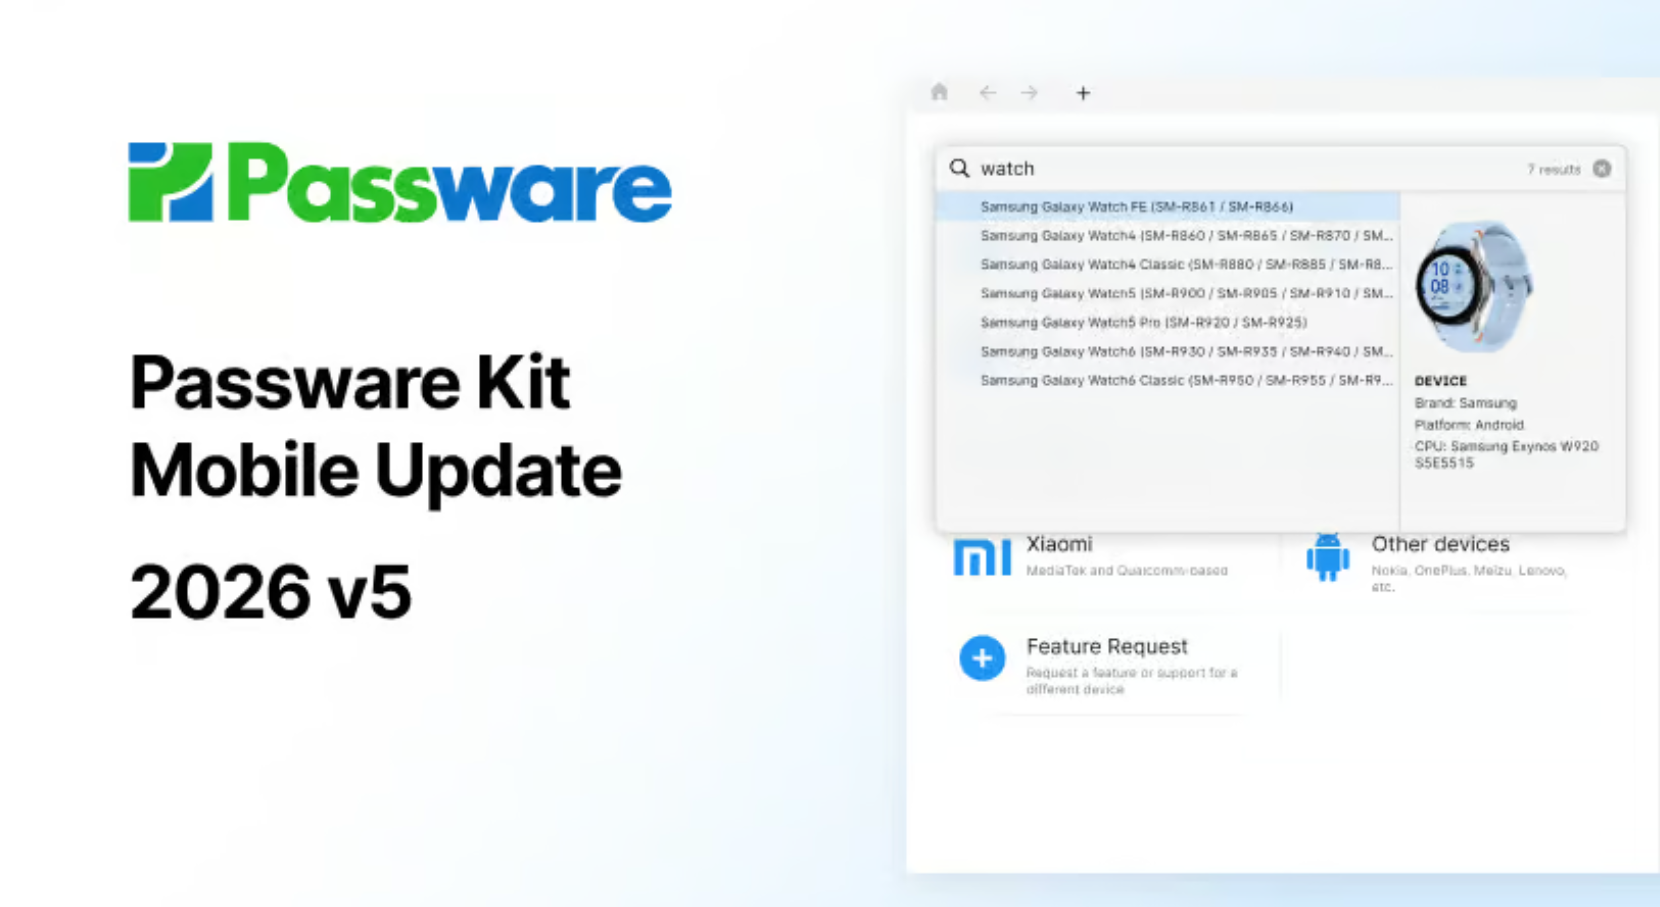
Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 Decrypts Samsung Galaxy Watch

Passware Kit Mobile 2026 v5 expands mobile forensics with Samsung Galaxy Watch 4/5/6 passcode recovery and data extraction, new Samsung and Unisoc device support, Enpass for Android decryption, and faster workflows with immediate passcode recovery....read more
Trust Is Not A Feature. It Is The Foundation.

Trust Is Not A Feature. It Is The Foundation.

Discover what agencies should expect from a digital forensics partner and how MSAB puts transparency, accountability and long-term commitment at the heart of its work....read more

Learning from Other’s Mistakes: Issues Arising from Electronic Discovery

First published May 2005 by Setec Investigations http://www.setecinvestigations.com Computer forensics and the associated electronic evidence and electronic discovery are relatively new to the litigation game. The use of such information is growing steadily and it has become impossible for legal

Collecting And Preserving Electronic Media

First published May 2005 by Joan E. Feldman, President Computer Forensics Inc. http://www.forensics.com The discovery process in civil litigation has always been a critical and sometimes confusing area for attorneys. Most attorneys have wondered, at one time or another, whether

Data Recovery Handling Tips & ESD Precaution

First published April 2005 by ActionFront Data Recovery Labs www.ActionFront.com Data Recovery Handling Tips & ESD Precaution Mishandling is a leading cause of hard disk drive failure. ESD (Electrostatic Discharge) A familiar form of Electrostatic Discharge, often called “static electricity”,

Beware Do-it-Yourself Data Recovery Solutions and Products

First published April 2005 by ActionFront Data Recovery Labs www.ActionFront.com Do-It-Yourself data recovery software may complicate your problems and diminish the prospects of a successful recovery. The object of many fix/doctor/repair programs is to try to make the drive, file-system

Is There a Need for Industry Control?

First published April 2005 by Nick Furneaux CSITech www.csitech.co.uk For many years if someone asked what I did for a living I would have to use an all-purpose description such as I worked in computer security or even worse I

Computer Forensics – A Business Tool

First published March 2005 by Andy Fox Director Audax Digital Forensics www.audaxuk.com March 2005 Computer forensics has become an increasingly important part of IT security. A 2003 survey carried out on 201 companies by the National High Tech Crime Unit

Electronic Evidence as the Smoking Gun

First published February 2005 by Henry J. Fasthoff, IV NOTE: THIS IS ARTICLE IS FOR INFORMATIONAL PURPOSES ONLY. IT IS NOT INTENDED TO BE CONSTRUED AS LEGAL ADVICE. Electronic communications–particularly email–may contain a treasure trove of evidence in commercial litigation

Hard Drive Crash? The Essential Data Recovery Report

First published January 2005 by Greg Duffield Your worst nightmare just became a horrifying reality. You keep hearing that little voice in your head mockingly shout “you should have backed that stuff up” The voice keeps echoing throughout your head

Using the Forensic Server Project

First published November 2004 The following is an extract from Chapter 8 of “Windows Forensics & Incident Recovery” by Harlan Carvey. Collecting data from a potentially compromised system is relatively simple. There are several methodologies for collecting data that an

Data Forensics – The smoking gun may be a click away

First published September 2004 By PAUL G. LEWIS Lewis is the founding partner of PG Lewis & Associates of Whitehouse Station, a data forensics firm. http://www.pglewis.com Enquiries to Rob Kleeger, [email protected] This article is reprinted with permission from the SEPTEMBER

Computer forensics software, an introduction

First published September 2004 by Jamie Morris, Forensic Focus In common with many other professions, the field of computer forensic investigation makes use of tools to allow practitioners to carry out their tasks effectively and efficiently. This article describes some

Free Dropbox Forensics Tool

Dropbox Reader is a set of Python scripts for forensic investigators. The scripts provide investigators with information about a particular Dropbox user’s account and activities, such as the registration e-mail, Dropbox identifier and most recently changed files. Dropbox Reader was