A round-up of today’s digital forensics news and views:
Forensic Focus News
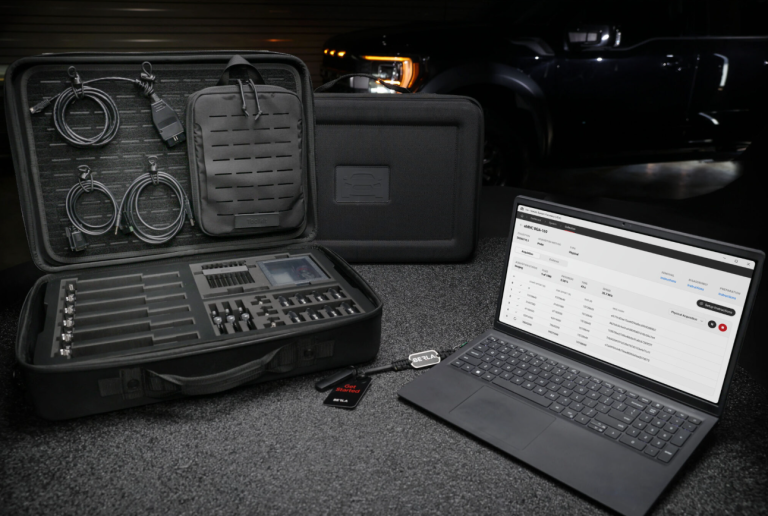
Belkasoft X For Mobile Forensics: Acquisition, Analysis, And Reporting
Belkasoft X supports mobile forensics across iOS and Android through layered acquisition methods, from iTunes backups and agent-based extraction to chipset-level physical imaging. iOS coverage spans checkm8-based full-file-system acquisition for A7–A11 devices, agent-based extraction across iOS 10.3.3 through 18.7.1, and optional passcode brute-force. Android acquisition ranges from ADB and agent backups to APK downgrade, rooted-device imaging, and chipset-specific methods for deeper extraction.
Industry News
SANS Releases Free Dynamic Incident Response Framework
Joshua Wright has published Dynamic Incident Response, a free 720-page Creative Commons framework representing the first major rebuild of the SANS IR model in 20 years. The framework addresses modern attacker persistence, where containment and recovery cycles repeat as adversaries return or new evidence reframes the incident scope. Contributed chapters cover cloud response, OT environments, and ransomware, with a hands-on session at the SANS AI Cybersecurity Summit on November 2-3.
Tools & Software
GLeapp Adds Image Similarity Detection to Mobile Triage
GLeapp, a new open-source image and video forensic triage toolkit, has been added to the Leapps collection and includes a feature that identifies media similar to a specified item of interest. Testing against a publicly available Cellebrite CTF extraction demonstrated the capability as a viable alternative when commercial tools fall short.
SQLite GUI Analyzer Adds Timestamp Conversion, Relationship Graph
SQLite GUI Analyzer has released a new version with dark mode, a table relationship graph, and right-click timestamp conversion supporting Unix, Chrome, FILETIME, and Mac time formats. It recovers deleted records from WAL files and freed pages, decodes BLOBs, and searches all tables simultaneously without modifying the source database. A Windows installer removes the Python setup requirement.
Research & Techniques
Dundee Team Launches Bias-Checking Tools for Forensic Reports
Researchers at the University of Dundee have released two tools, an AI-assisted Clarity Checker and an online lexicon, designed to reduce bias and inconsistent terminology in digital forensic reports used across European criminal justice systems. The Clarity Checker analyses written reports for language that could unintentionally skew interpretation of digital evidence before it enters the justice process. Both tools emerged from the Horizon Europe-funded Clarus Project, which studied digital forensic communication practices in Scotland, Finland, Greece, Czechia and Portugal.
Read more (deadlinenews.co.uk)
GenAI Risks and Epistemic Security in Cyber Investigations
Cyber investigators face longstanding epistemic risks including procedural gaps, tool bugs, and cognitive biases, and careless use of generative AI amplifies all three. Thoughtfully applied, AI can help examiners identify knowledge gaps and detect concealment activity, as illustrated by the Hugging Face incident.