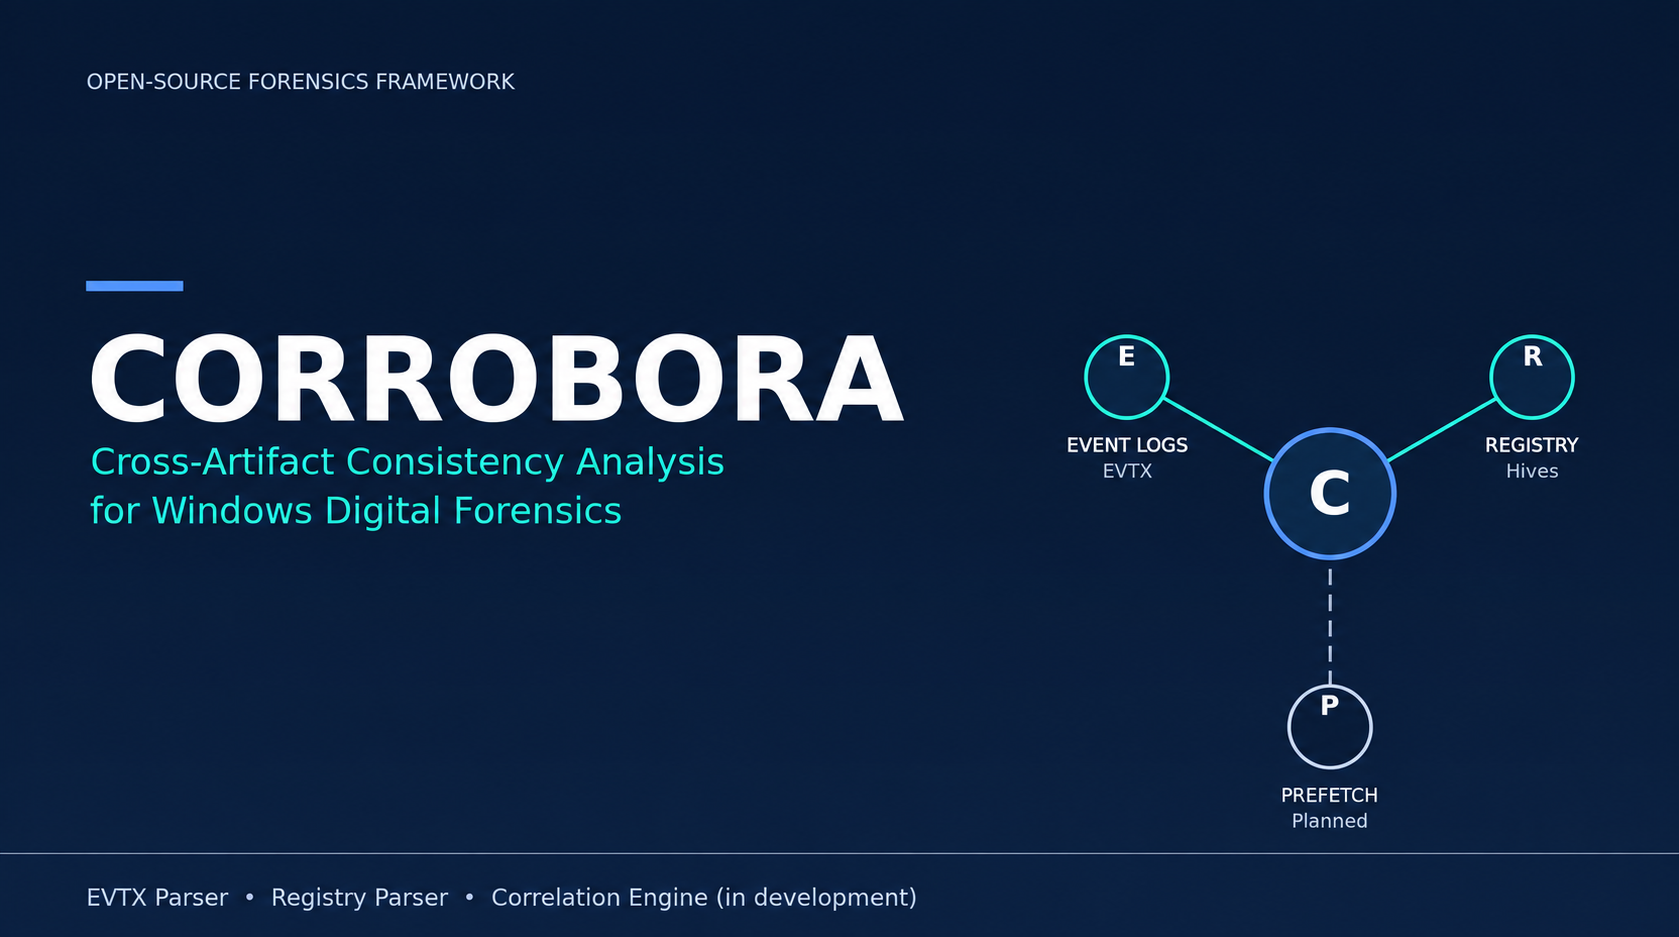
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

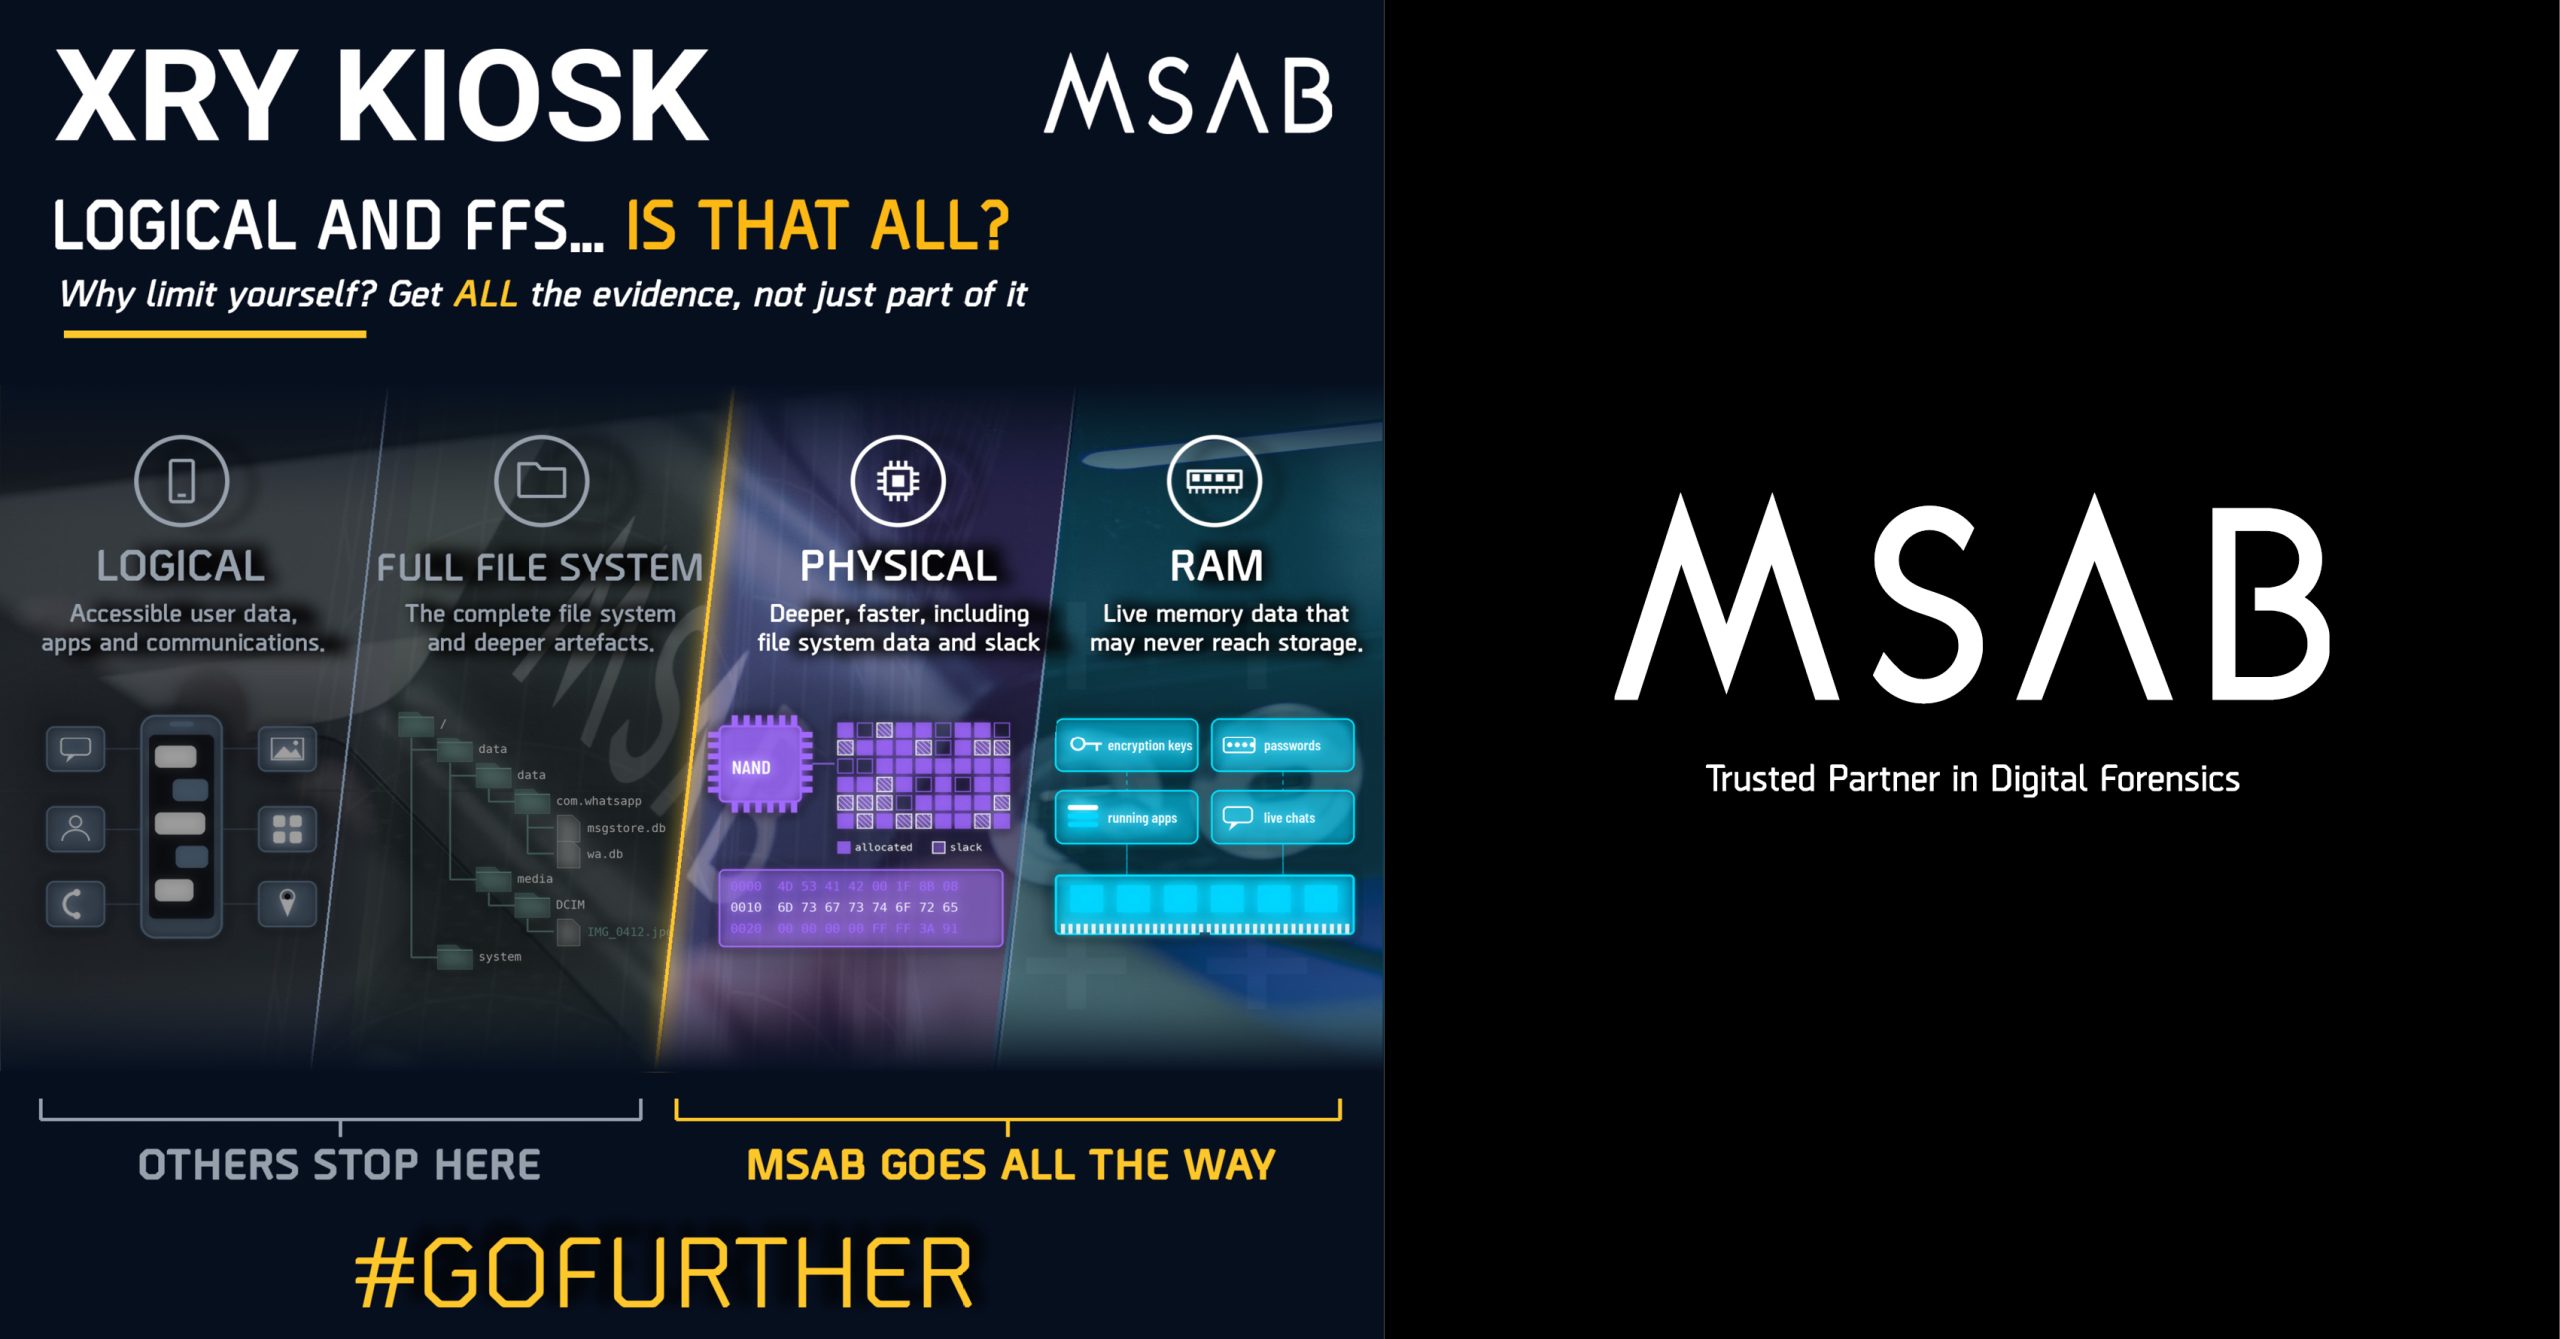
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Toward Exact And Inexact Approximate Matching Of Executable Binaries

Lorenz Liebler discusses his research at DFRWS EU 2019.The application of approximate matching (a.k.a. fuzzy hashing or similarity hashing) is often considered in the field of malware or binary analysis. Recent research showed major weaknesses of predominant fuzzy hashing techniques

Joe Sylve, Director Of Research And Development, BlackBag Technologies

Joe, your BlackBag profile describes how you "drive innovation and pursue emerging areas of research" as Director of Research & Development. Can you describe for us what your day-to-day looks like? Usually I’m managing shifting priorities, so there’s not always

Sarah Edwards On iOS Forensics And APOLLO

Christa: Hello and welcome to the Forensic Focus podcast. Monthly we interview experts from the digital forensics and incident response community on a host of topics ranging from technical aspects to career soft skills. I’m your host, Christa Miller. Today

Francis De Giorgio, Director Of Product Development, Susteen

Francis, tell us about your product development role. Where did you work previously, and what drew you to Susteen? I always enjoy a good David versus Goliath challenge and have had the privilege over the last 25 years to work

Everything You Ever Wanted To Ask About Checkm8 And Checkra1n

by Oxygen Forensics What’s Checkm8? Checkm8 is an exploit (program exploiting OS or hardware vulnerabilities) aimed at obtaining access to the execution of its own software code at the earliest stage of iOS device loading. What makes it stand out?

Everything You Ever Wanted To Ask About Checkm8 And Checkra1n

by Oxygen Forensics  What’s Checkm8? Checkm8 is an exploit (program exploiting OS or hardware vulnerabilities) aimed at obtaining access to the execution of its own software code at the earliest stage of iOS device loading. What makes it stand out?

BlackLight R3 From BlackBag

by Jade James BlackLight is a simple but smart investigation tool which allows examiners to quickly analyse computer systems and mobile devices. Searching is made easy with advanced filtering to sift through large data sets. The tool is aimed at

Forensic Tools For Investigating Child Sexual Abuse Material

Laura Sanchez discusses her research at DFRWS US 2019. Hello, I’m Laura Sanchez and I’m a graduate researcher at the University of New Haven. And I’ll be presenting the results of our survey that was conducted by my colleagues. Our

BlackLight R3 From BlackBag

by Jade James BlackLight is a simple but smart investigation tool which allows examiners to quickly analyse computer systems and mobile devices. Searching is made easy with advanced filtering to sift through large data sets. The tool is aimed at

What’s Happening In Forensics – Mar 03, 2020

13Cubed share a memory forensics challenge. Petr Stuchlík discusses SMB endpoint fingerprinting. DFRWS share presentations from last year’s US conference. Ryan Benson shares some digital forensics writing tips.

Chromium-Based Microsoft Edge From A Forensic Point Of View

by Oleg Skulkin & Svetlana Ostrovskaya Recently Microsoft finally released the Chromium-based version of Edge Browser, so it seems we’ll miss ESE databases soon (not). Of course, it may have a similar set of forensic artifacts to Chromium or Chrome,