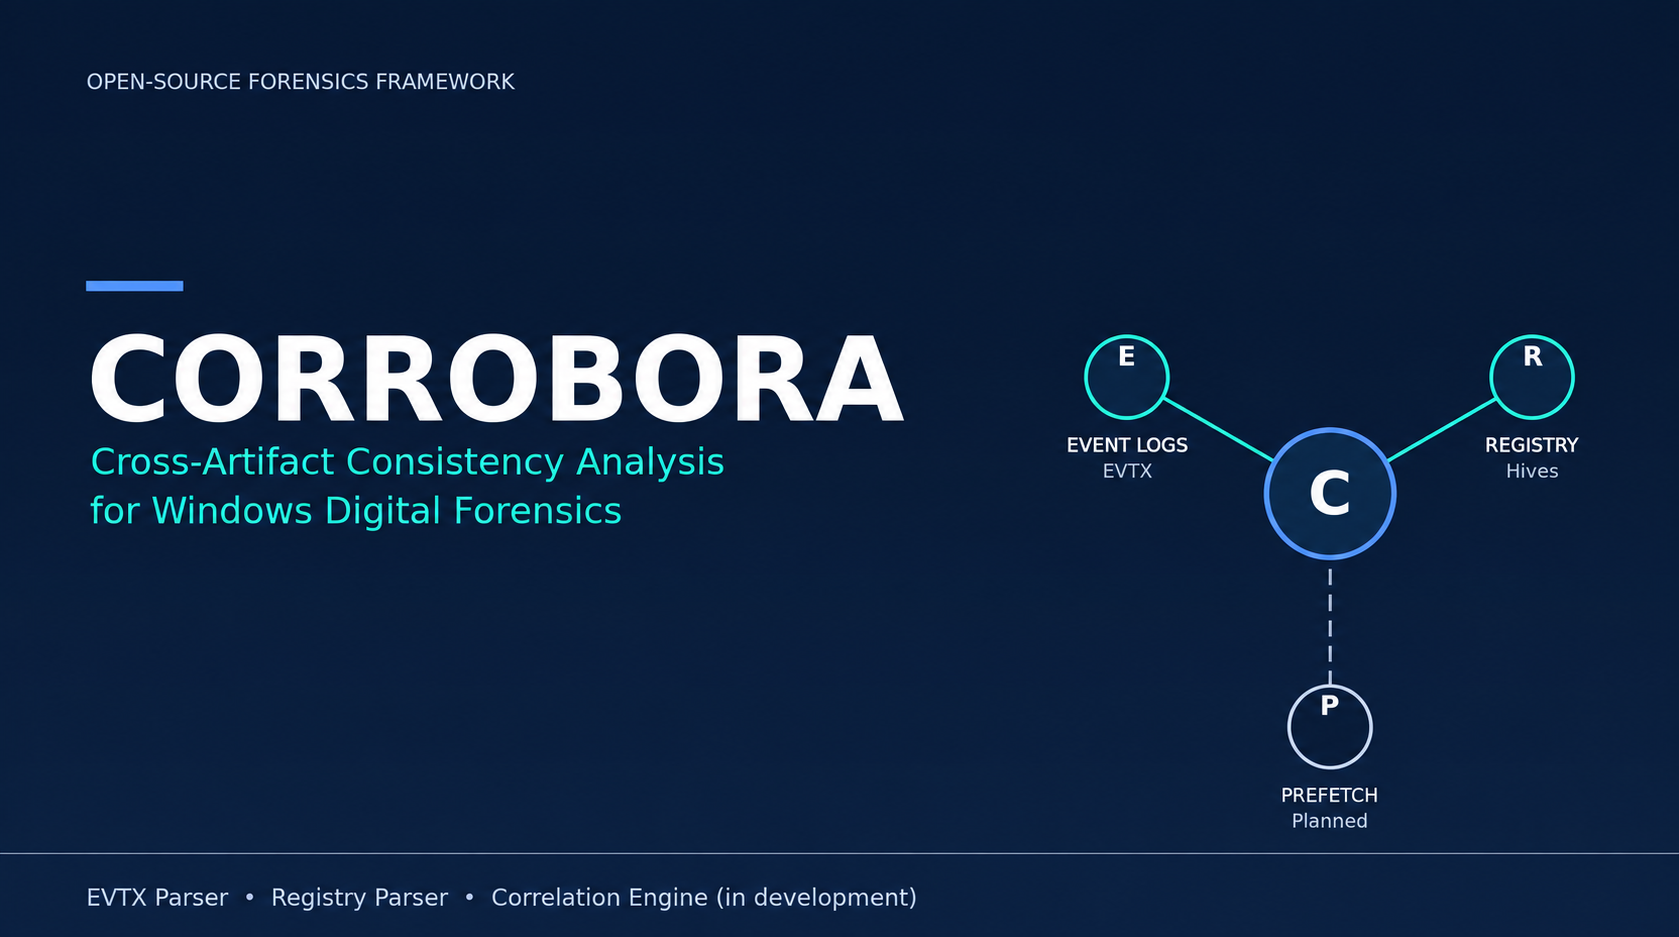
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

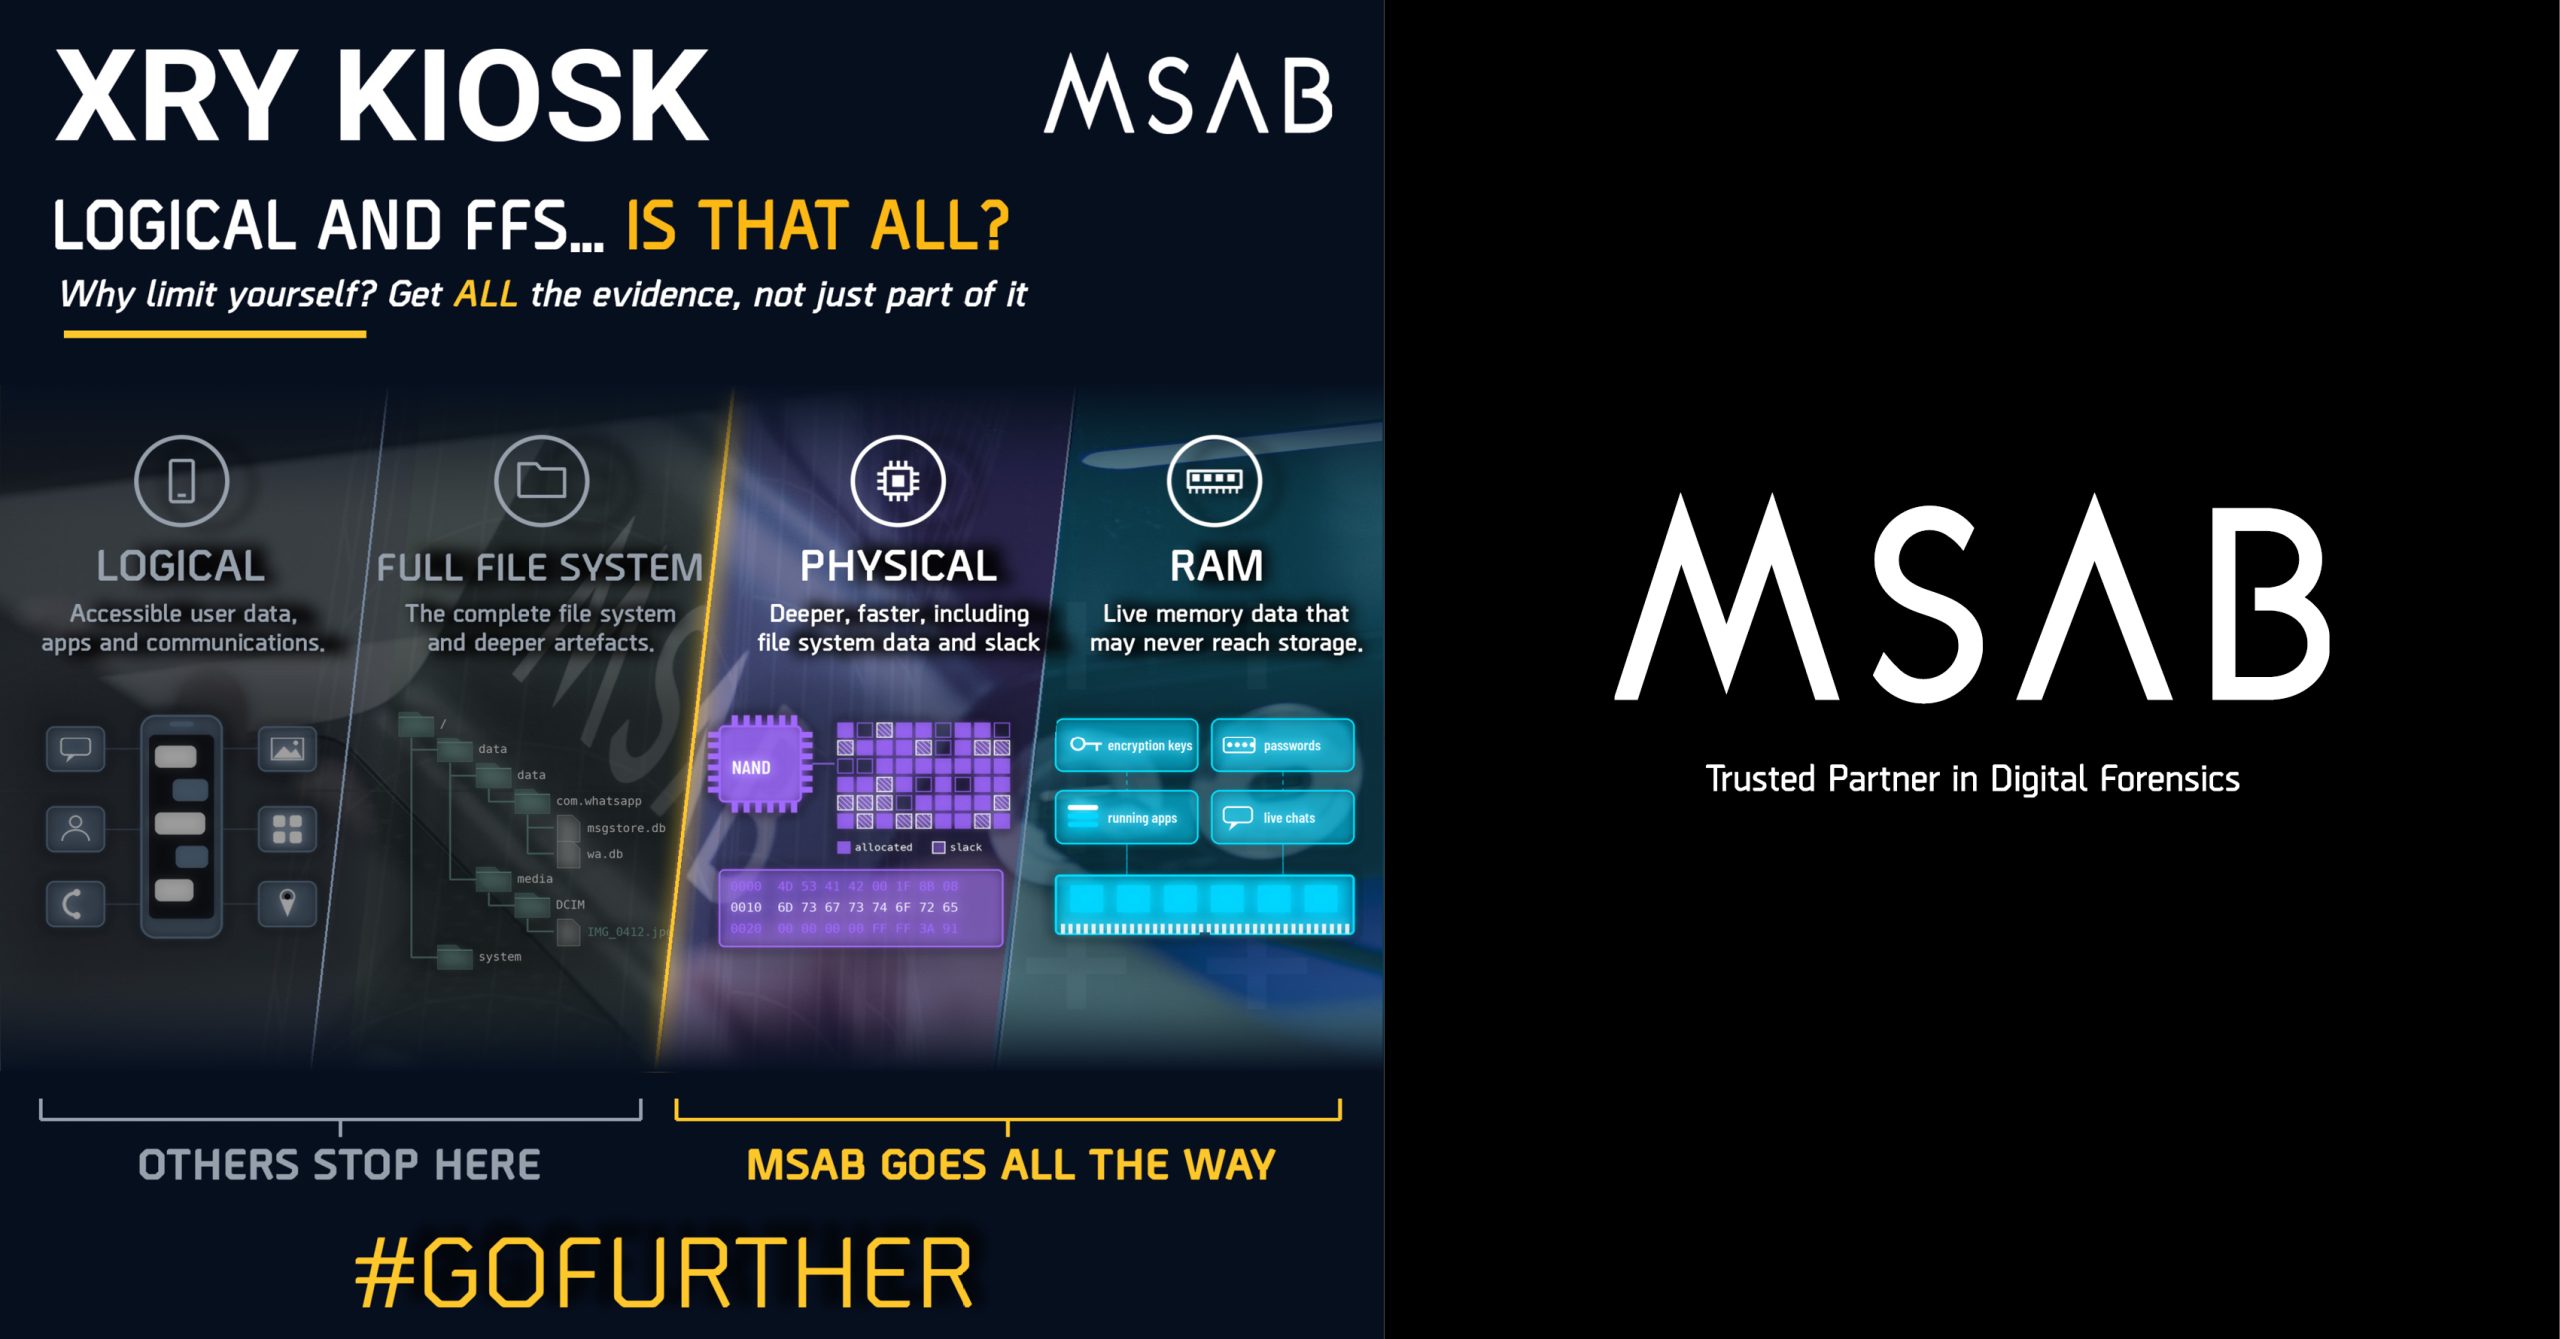
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
What’s Happening In Forensics – Jan 6, 2020

Didier Stevens analyses some unusual zip files. Andrew Case will be presenting “Volatility 3 Public Beta: A Peek into the Future of Memory Forensics” at the Art into Science conference in Austin TX on Jan 15. Phil Stokes shares some

How To Analyze Call Data Records In Oxygen Forensic Detective

Hi, this is Amanda Mangan with Oxygen Forensics. In this video, we’re going to go over Oxygen Forensics’ Call Data Expert. The first thing we’ll discuss is, what exactly is a CDR? A CDR is a call data record, and

How To Analyze Call Data Records In Oxygen Forensic Detective

Hi, this is Amanda Mangan with Oxygen Forensics. In this video, we’re going to go over Oxygen Forensics’ Call Data Expert. The first thing we’ll discuss is, what exactly is a CDR? A CDR is a call data record, and

Forensic Focus Legal Update December 2019 – Part II: Search And Seizure

by Christa Miller In cooperation with the National White Collar Crime Center (NW3C) and SEARCH, The National Consortium for Justice Information and Statistics, Forensic Focus offers a quarterly roundup of the latest legal developments around digital forensic evidence. Comprising major

Forensic Focus Legal Update December 2019 – Part II: Search And Seizure

by Christa Miller In cooperation with the National White Collar Crime Center (NW3C) and SEARCH, The National Consortium for Justice Information and Statistics, Forensic Focus offers a quarterly roundup of the latest legal developments around digital forensic evidence. Comprising major

Interview With Martin Westman, Product Specialist, MSAB

Martin, you've worked for MSAB for 15 years. What changes in mobile forensics stand out to you from that time? The most important one during this 15-year period would be the introduction of actual smartphones, because they were the biggest

Martin Westman, Product Specialist, MSAB

Martin, you've worked for MSAB for 15 years. What changes in mobile forensics stand out to you from that time? The most important one during this 15-year period would be the introduction of actual smartphones, because they were the biggest

Robert O’Leary, Head Of Investigations For USG & Corporate, Nuix

Robert, your career in digital forensics began in the industry's infancy. What first brought you to high tech crimes with the New Jersey State Police? I worked undercover narcotics investigations and I worked in a narcotic trafficking interdiction unit in

Passware Kit 2020v1: Dictionary Manager and Support for VeraCrypt GPT

Passware Kit 2020 v1 introduces a built-in Dictionary Manager, support for VeraCrypt GPT system encryption, and optimized decryption process for hard drives. The new version also extracts passwords from Windows 10/8 standalone systems protected with Windows Hello: PIN and Picture

Forensic Focus Forum Round-Up

Welcome to this month’s round-up of recent posts to the Forensic Focus forums. How would you recover a $J file from a UsnJrnl file in a shadow copy? Forum members discuss containing and recovering a malware infected server. Share your

How To Parse AirDrop Artifacts In Magnet AXIOM

Hey everyone, Trey Amick from Magnet Forensics here. Today we’re going to be looking at a new set of artifacts specific to Mac investigations, which will be released as part of the AXIOM 3.8 release. Today we’re going to be

How To Parse AirDrop Artifacts In Magnet AXIOM

Hey everyone, Trey Amick from Magnet Forensics here. Today we’re going to be looking at a new set of artifacts specific to Mac investigations, which will be released as part of the AXIOM 3.8 release. Today we’re going to be