Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

Investigating WMI Permanent Event Subscription Persistence

Hero Image

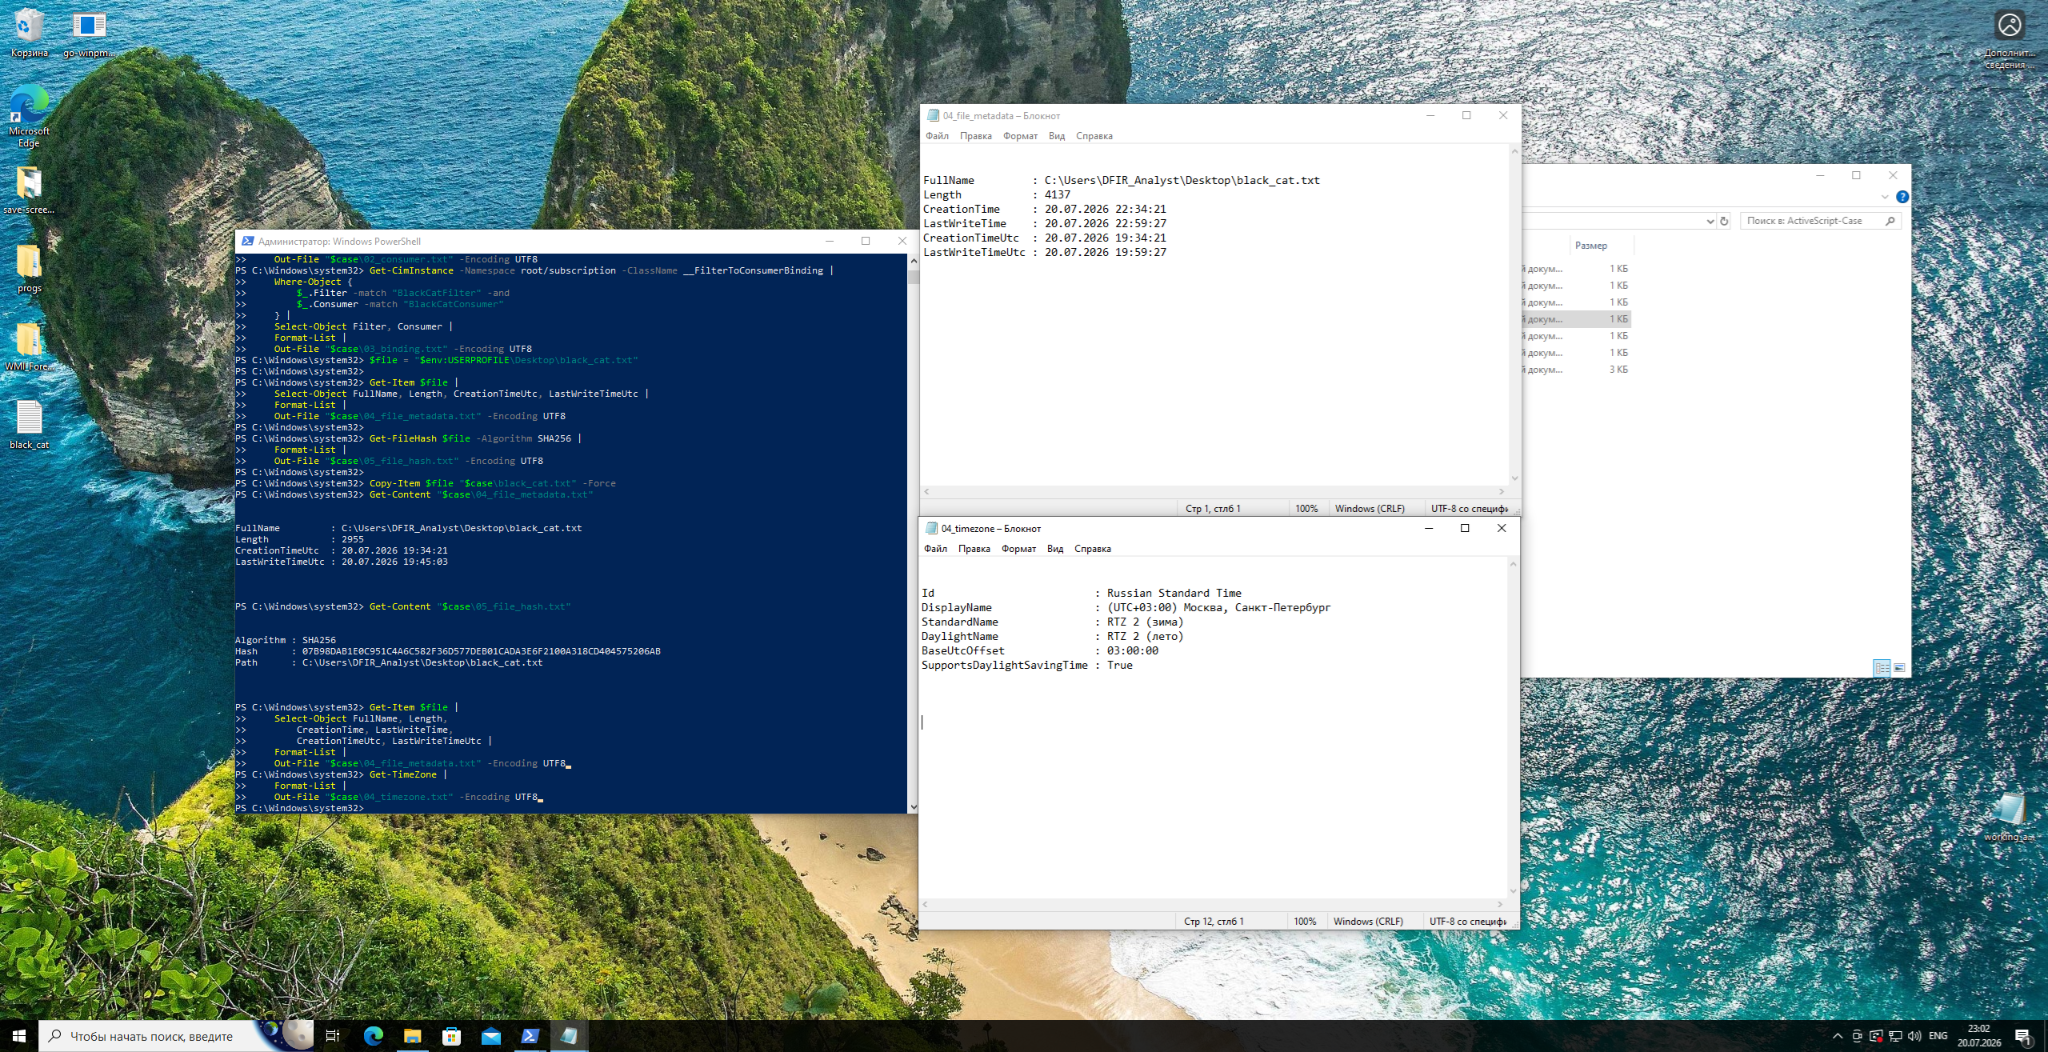
Vitalii offers a hands-on DFIR deep dive into WMI ActiveScriptEventConsumer persistence, from registration and execution to memory artifacts, Sigma detection, and cleanup....
Today's headlines 20 Oct 2026

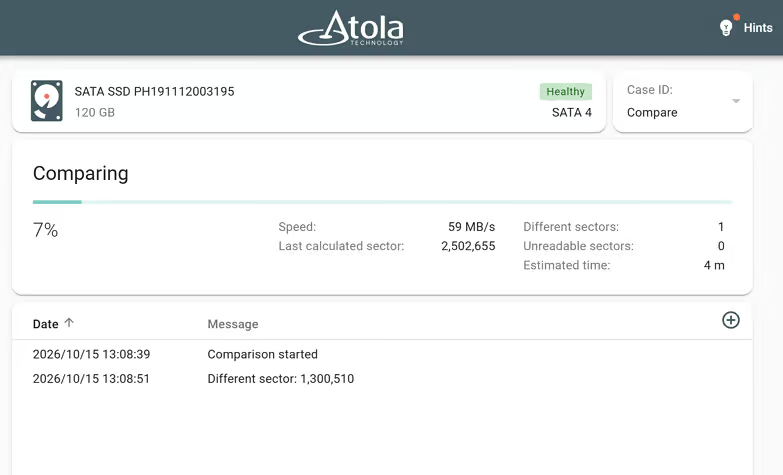
Atola TaskForce Gets A Massive Update Including A New Compare Module

Atola TaskForce Gets A Massive Update Including A New Compare Module

Meet Atola TaskForce firmware 2026.10, featuring a brand-new sector-by-sector Compare module, detection of used-drive fraud on Seagate devices, enhanced Web API automation, and 30+ improvements across forensic imaging workflows....read more
Forensic Focus Digest, 16 Oct 2026

Forensic Focus Digest, 16 Oct 2026

Discover what’s new on Forensic Focus: explore how the City of Johannesburg uses Detego Global to accelerate investigations, see how MD-LIVE takes investigators from first connection to a court-ready report, learn how iVe analyzes vehicle data to reveal driver behavior, and more....read more
The Forensic Focus State Of DFIR Survey Is Now Open

The Forensic Focus State Of DFIR Survey Is Now Open

Caseloads, AI, tools, hiring and careers: tell us what DFIR work looks like today. About 8 minutes, anonymous, with early access to the report...read more
Wickr Messenger Extraction And Decryption In Oxygen Forensic Detective

Wickr Messenger allows users to exchange end-to-end encrypted and content-expiring messages, and make end-to-end encrypted video conference calls. Wickr is regularly mentioned in various Internet sources as a secure messaging app. Let’s have a look at these secure features and

Walkthrough: Quin-C Social Analyzer Widget From AccessData

Hello. This is Sven from the technical team here at AccessData. This video will feature the Social Analyzer widget. So let’s get started. Go to Quin-C and open the grid, just to see how many items we have in our

Walkthrough: Quin-C Social Analyzer Widget From AccessData

Hello. This is Sven from the technical team here at AccessData. This video will feature the Social Analyzer widget. So let’s get started. Go to Quin-C and open the grid, just to see how many items we have in our

How To Conduct A Live Forensic Scan Of A Windows Computer

Learn how to conduct a Windows live scan with ADF Solutions Digital Evidence Investigator. Two USB ports are required to complete a scan, one for the Collection Key and one for the Authentication Key, once the scan has started the

How To Conduct A Live Forensic Scan Of A Windows Computer

Learn how to conduct a Windows live scan with ADF Solutions Digital Evidence Investigator.  Two USB ports are required to complete a scan, one for the Collection Key and one for the Authentication Key, once the scan has started the Authentication

Forensic Focus Forum Round-Up

Welcome to this month’s round-up of recent posts to the Forensic Focus forums. Forum members advise on producing E01 images in reverse sector order. How would you convert an AD1 image to a dd? Can you help roncfluey to image

How To Use The Griffeye Intelligence Database

Beginning with version 19, Griffeye Analyze DI Pro and Core will start using the new Griffeye Intelligence Database, or GID, to replace the legacy intelligence manager. In this video, we’re going to discuss the changes that the GID brings to

How To Use The Griffeye Intelligence Database

Beginning with version 19, Griffeye Analyze DI Pro and Core will start using the new Griffeye Intelligence Database, or GID, to replace the legacy intelligence manager. In this video, we’re going to discuss the changes that the GID brings to

Hunting For Attackers’ Tactics And Techniques With Prefetch Files

by Oleg Skulkin Windows Prefetch files were introduced in Windows XP, and since that time they have helped digital forensics analysts and incident responders to find evidence of execution. These files are stored under %SystemRoot%\Prefetch, and are designed to speed

How To Decrypt BitLocker Volumes With Passware

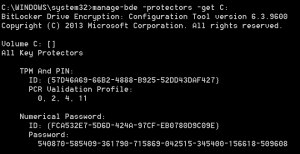
Decrypting BitLocker volumes or images is challenging due to the various encryption options offered by BitLocker that require different information for decryption. This article explains BitLocker protectors and talks about the best ways to get the data decrypted, even for

Hunting For Attackers’ Tactics And Techniques With Prefetch Files

by Oleg Skulkin Windows Prefetch files were introduced in Windows XP, and since that time they have helped digital forensics analysts and incident responders to find evidence of execution.  These files are stored under %SystemRoot%\Prefetch, and are designed to speed

How To Decrypt BitLocker Volumes With Passware

Decrypting BitLocker volumes or images is challenging due to the various encryption options offered by BitLocker that require different information for decryption. This article explains BitLocker protectors and talks about the best ways to get the data decrypted, even for

What’s Happening In Forensics – Nov 20, 2019

Oleg Afonin talks about the forensic analysis of Synology NAS devices. Alexis Brignoni shares a realm database storage primer for digital forensic examiners. Amped show how to resize images with Amped Replay. Passware announce a new partnership with BlackBag. OpenText