Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

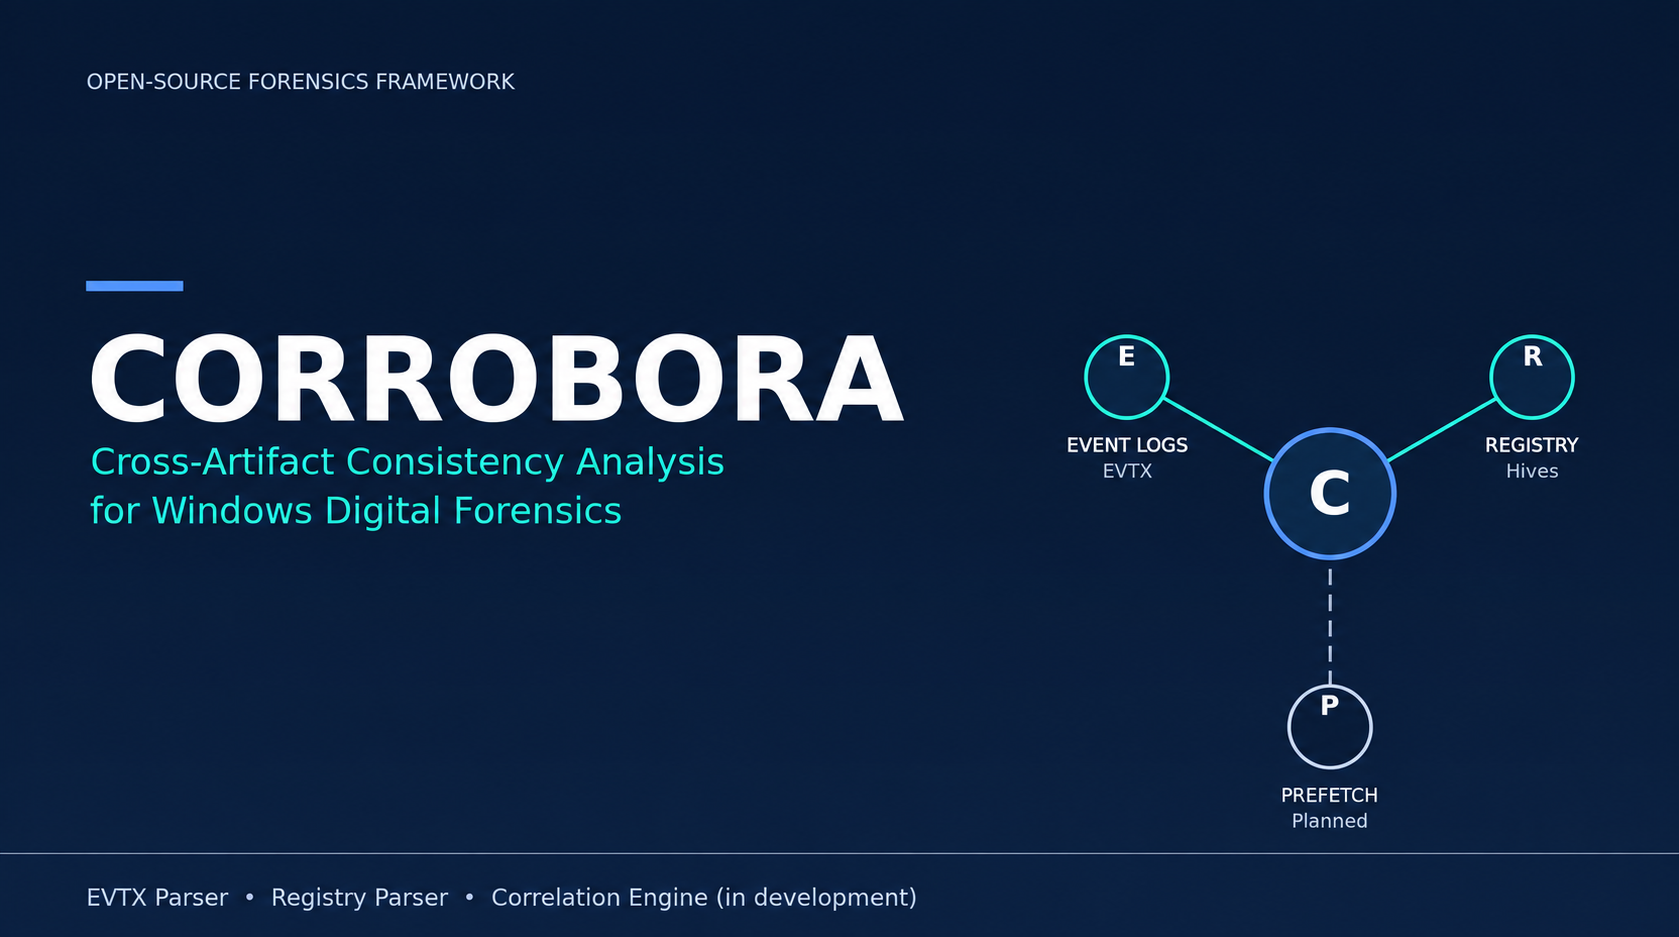
Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

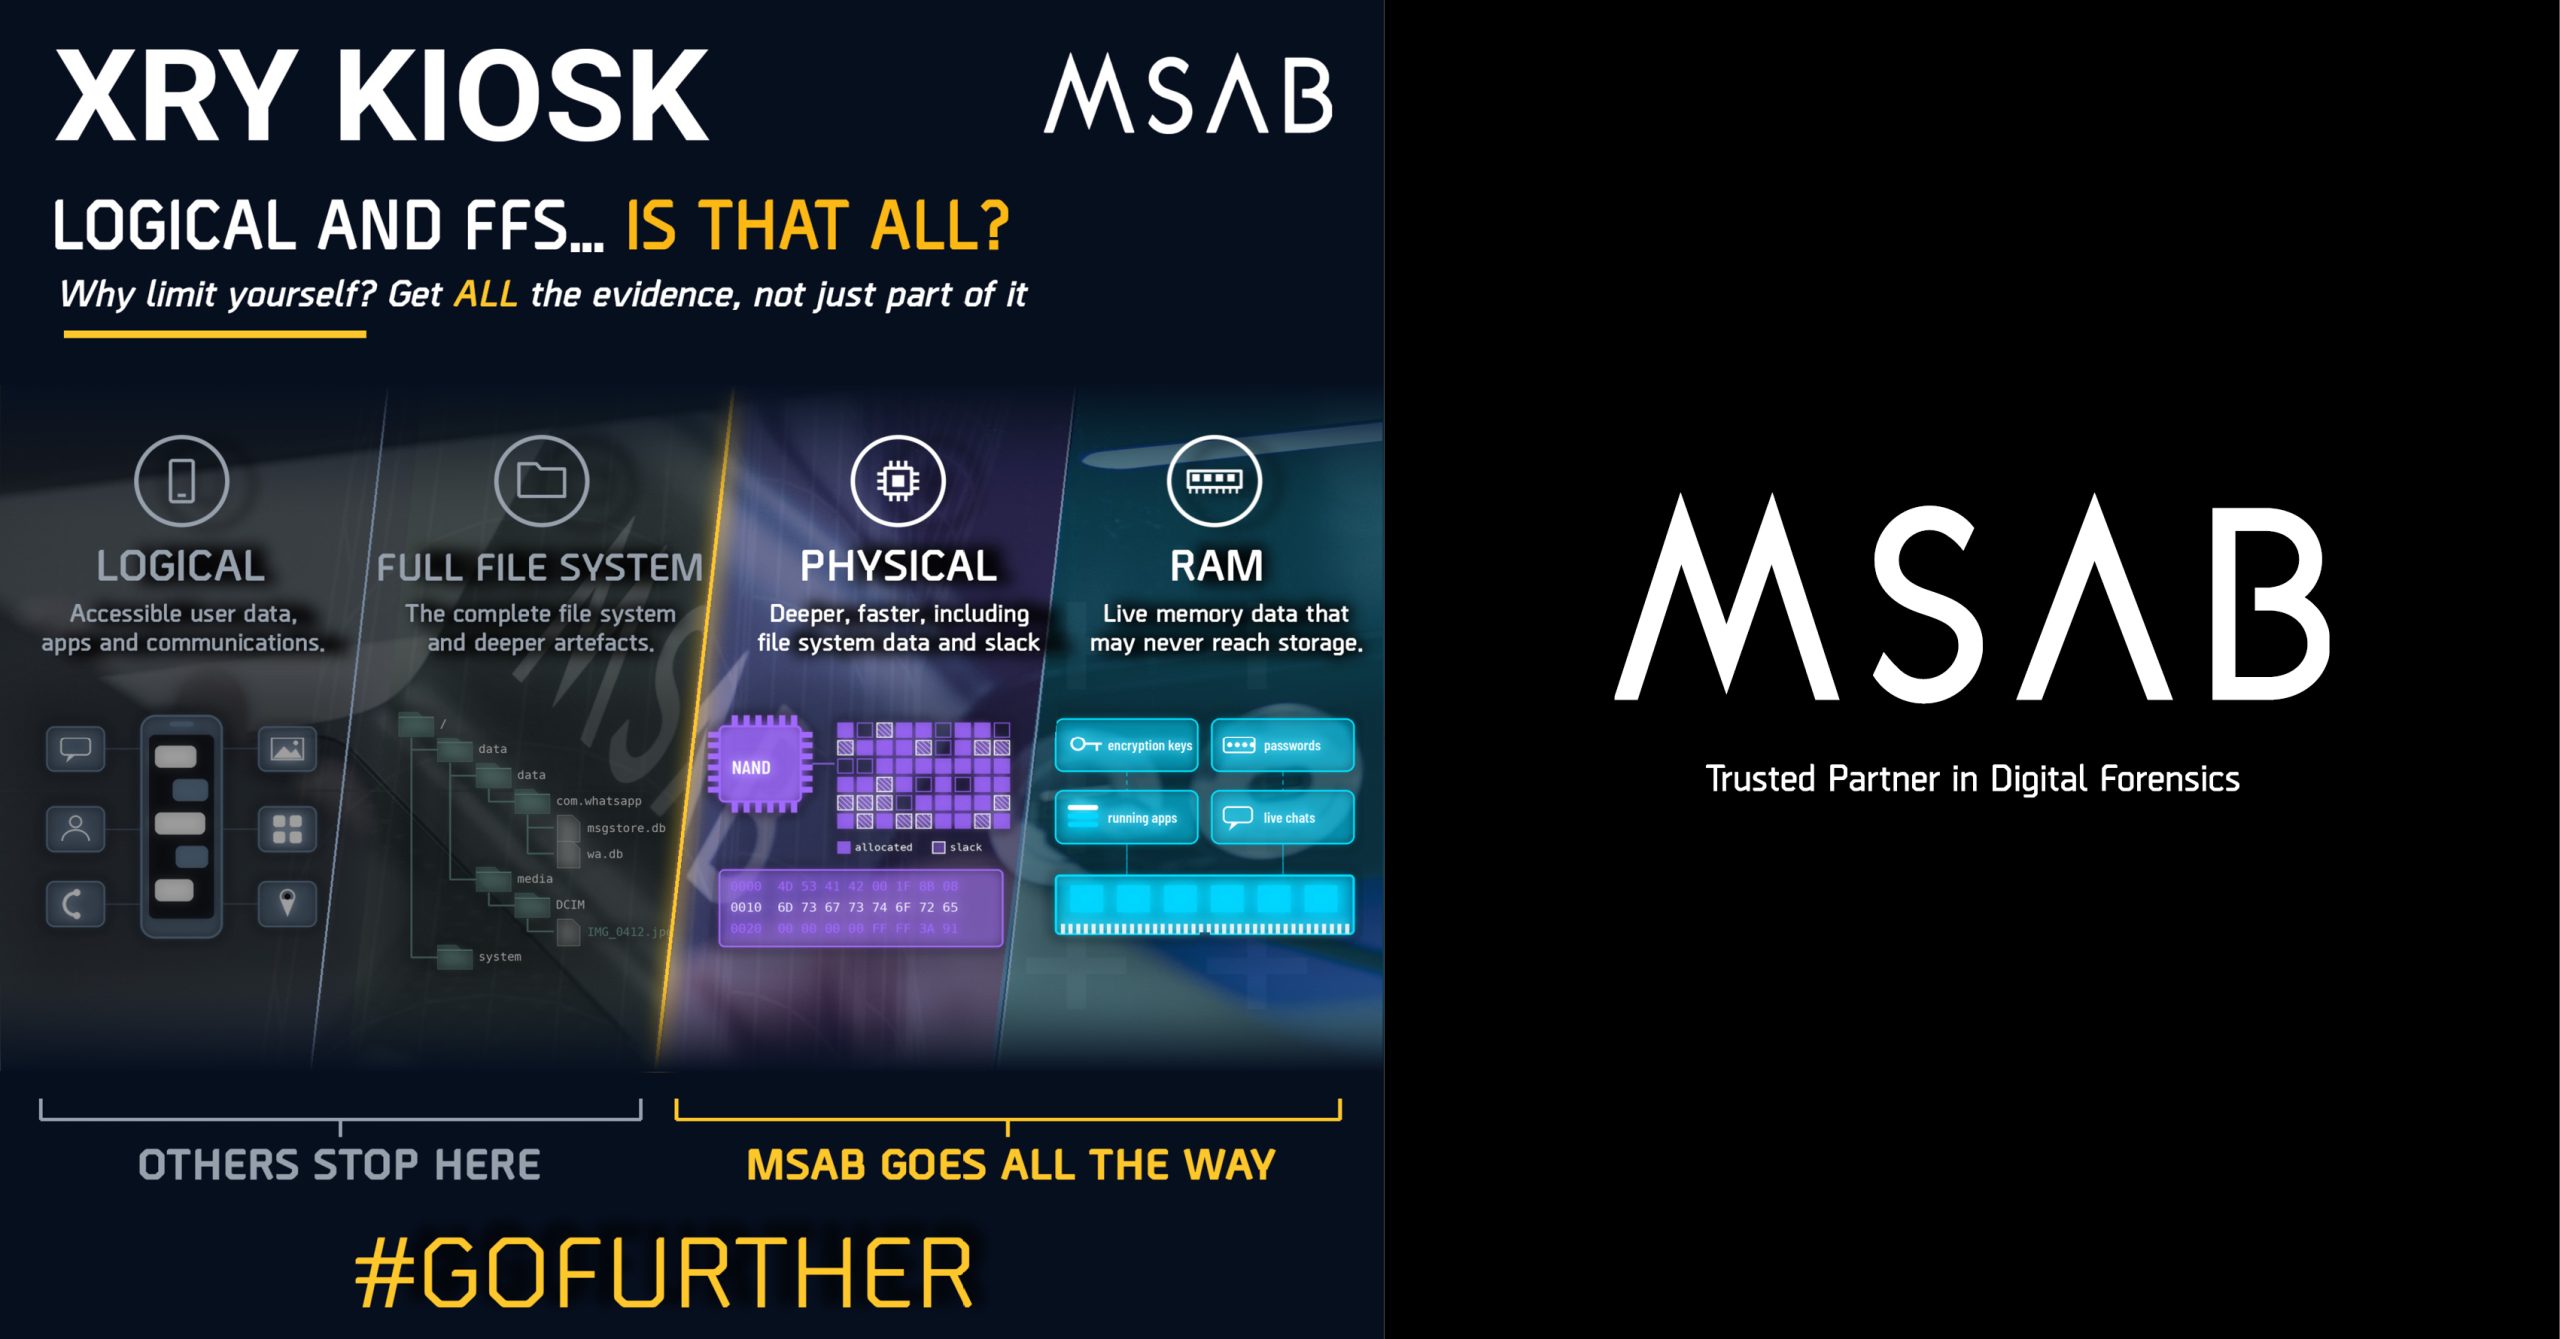
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
Hunting For Attackers’ Tactics And Techniques With Prefetch Files

by Oleg Skulkin Windows Prefetch files were introduced in Windows XP, and since that time they have helped digital forensics analysts and incident responders to find evidence of execution. These files are stored under %SystemRoot%\Prefetch, and are designed to speed

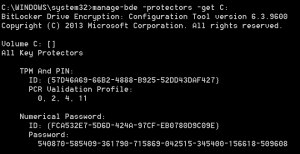
How To Decrypt BitLocker Volumes With Passware

Decrypting BitLocker volumes or images is challenging due to the various encryption options offered by BitLocker that require different information for decryption. This article explains BitLocker protectors and talks about the best ways to get the data decrypted, even for

Hunting For Attackers’ Tactics And Techniques With Prefetch Files

by Oleg Skulkin Windows Prefetch files were introduced in Windows XP, and since that time they have helped digital forensics analysts and incident responders to find evidence of execution.  These files are stored under %SystemRoot%\Prefetch, and are designed to speed

How To Decrypt BitLocker Volumes With Passware

Decrypting BitLocker volumes or images is challenging due to the various encryption options offered by BitLocker that require different information for decryption. This article explains BitLocker protectors and talks about the best ways to get the data decrypted, even for

What’s Happening In Forensics – Nov 20, 2019

Oleg Afonin talks about the forensic analysis of Synology NAS devices. Alexis Brignoni shares a realm database storage primer for digital forensic examiners. Amped show how to resize images with Amped Replay. Passware announce a new partnership with BlackBag. OpenText

How To Use Magnet AXIOM In Mac USB Investigations

Hey everyone, Trey Amick from Magnet Forensics here. Today we’re talking about Mac USB investigations, and what happens when we’ve been alerted that a USB has been inserted into an end point. Different organisations handle USB policies differently. Some have

How To Use Magnet AXIOM In Mac USB Investigations

Hey everyone, Trey Amick from Magnet Forensics here. Today we’re talking about Mac USB investigations, and what happens when we’ve been alerted that a USB has been inserted into an end point. Different organisations handle USB policies differently. Some have

Can Your Investigation Interpret Emoji?

by Christa Miller, Forensic Focus Emoji are everywhere — including in your evidence. Used across private-messaging apps and email, social media, and even in passwords and account names, emoji are pictographic representations of objects, moods, and words. They’re a convenient

Can Your Investigation Interpret Emoji?

by Christa Miller, Forensic Focus Emoji are everywhere — including in your evidence. Used across private-messaging apps and email, social media, and even in passwords and account names, emoji are pictographic representations of objects, moods, and words. They’re a convenient

Viber Messenger Extraction In Oxygen Forensic Detective

Viber is a cross-platform voice over IP and instant messaging software operated by Rakuten. The software app is provided as freeware for Android, Apple iOS, Microsoft Windows, macOS and Linux platforms. Initially the messenger was developed in 2010 by the

French Agency Uses Chip-Off Technique To Solve A Critical Case

By: Christophe Gabay, MSAB Area Sales Manager Recovering data from mobile devices continues to bring new challenges to investigators, and using “chip-off” and Joint Test Action Group (JTAG) methods have become topics of growing interest in the law enforcement community.

What’s Happening In Forensics – Nov 19, 2019

NirSoft release a new tool, MobileFileSearch, allowing users to search files on a mobile device attached to their computer. Arman Gungor shares some updates to Forensic Email Collector. DFRWS has a brand new website – take a look and register

Walkthrough: XRY Photon Manual

XRY Photon is a solution designed for recovering smartphone app data that’s inaccessible through normal extraction techniques. Now the power of XRY Photon has been expanded to cover hundreds of additional apps, with a new manual option. Before using XRY

How To Use Griffeye Brain – Artificial Intelligence

The Griffeye Brain in Analyze DI Pro version 19.2 brings the power of machine learning and artificial intelligence to help you quickly locate and identify child sex abuse material within your investigations.In addition, the Griffeye Brain now has improved object

Walkthrough: XRY Photon Manual

XRY Photon is a solution designed for recovering smartphone app data that’s inaccessible through normal extraction techniques. Now the power of XRY Photon has been expanded to cover hundreds of additional apps, with a new manual option. Before using XRY