Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

How Semantics 21 Is Changing The Way Investigators Work With Digital Evidence

Hero Image

Digital evidence has evolved, but have your investigative workflows kept pace? Discover how Semantics 21 is helping investigators reduce manual effort, prioritise critical evidence and work smarter with modern forensic intelligence tools....
Today's headlines 21 Oct 2026

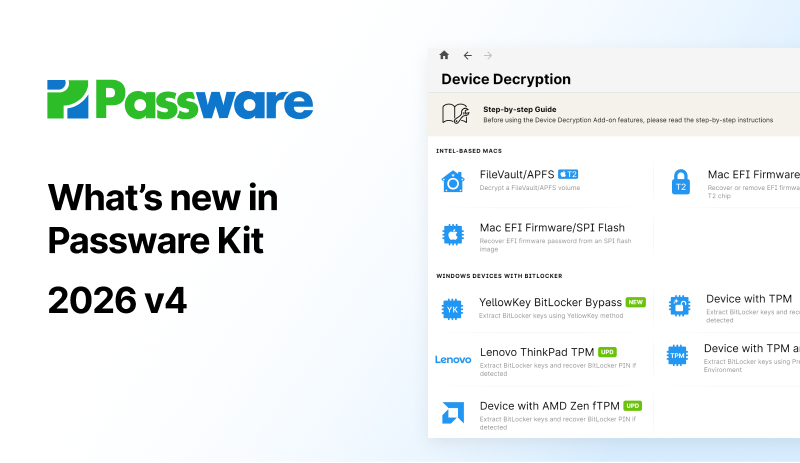
Passware Kit 2026 v4 Simplifies BitLocker Decryption And Adds E01 Export

Passware Kit 2026 v4 Simplifies BitLocker Decryption And Adds E01 Export

Passware Kit 2026 v4 is here with expanded BitLocker decryption support for AMD and Lenovo devices, the new YellowKey method, Linux eCryptfs decryption, E01 export, and enhanced Apple support....read more
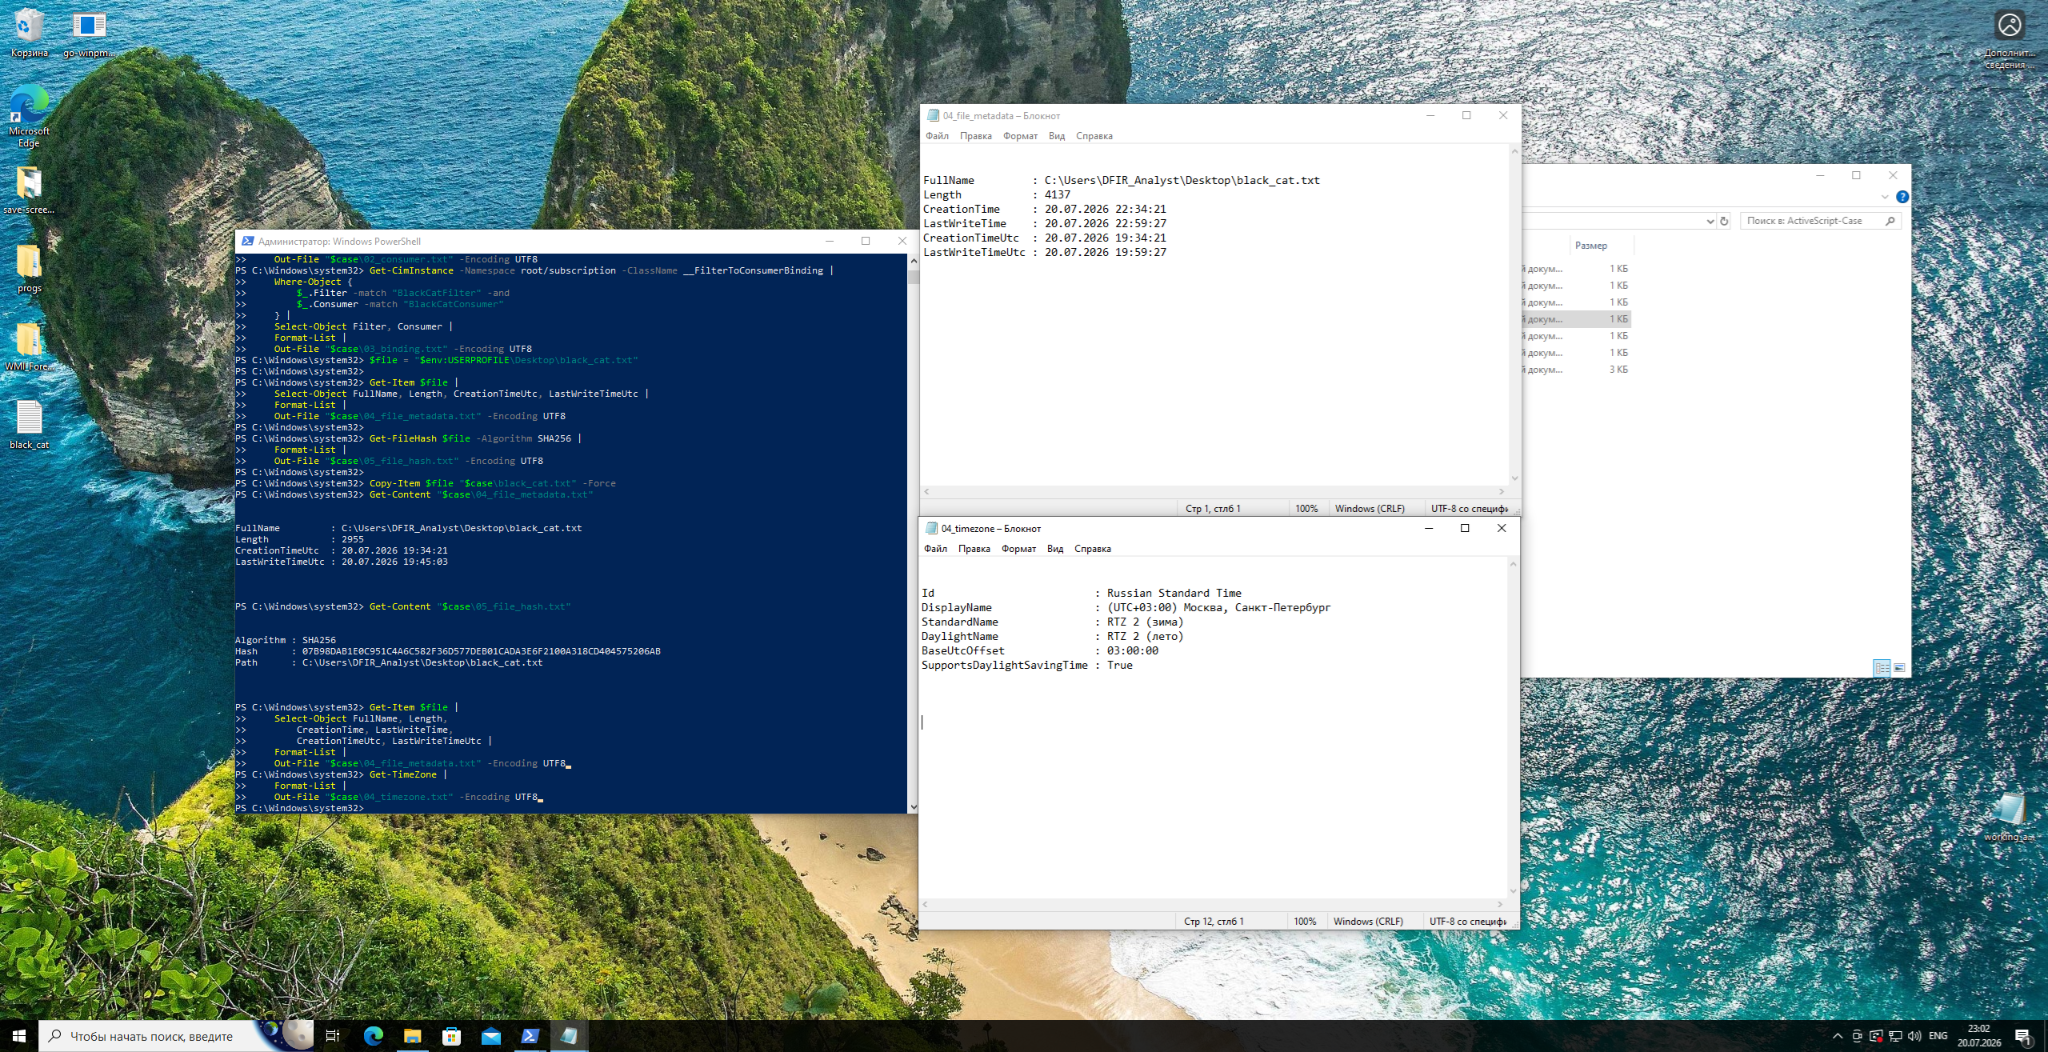
Investigating WMI Permanent Event Subscription Persistence

Investigating WMI Permanent Event Subscription Persistence

Vitalii offers a hands-on DFIR deep dive into WMI ActiveScriptEventConsumer persistence, from registration and execution to memory artifacts, Sigma detection, and cleanup....read more
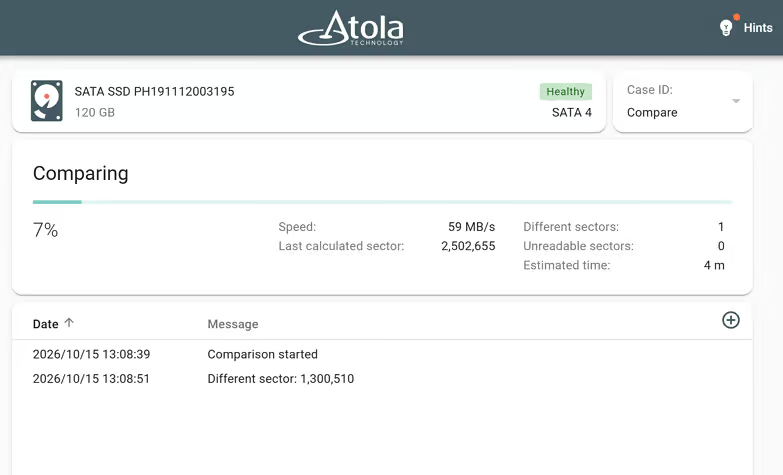
Atola TaskForce Gets A Massive Update Including A New Compare Module

Atola TaskForce Gets A Massive Update Including A New Compare Module

Meet Atola TaskForce firmware 2026.10, featuring a brand-new sector-by-sector Compare module, detection of used-drive fraud on Seagate devices, enhanced Web API automation, and 30+ improvements across forensic imaging workflows....read more
How To Use Text Analytics With Rosoka Integration

Hi, I’m Rich Frawley and I’m the Digital Forensic Specialist with ADF Solutions. Today we are going to explore the text analytics capabilities built into ADF’s digital forensic software with the integration of Rosoka. Rosoka brings the power of automated

How To Use Text Analytics With Rosoka Integration

Hi, I’m Rich Frawley and I’m the Digital Forensic Specialist with ADF Solutions. Today we are going to explore the text analytics capabilities built into ADF’s digital forensic software with the integration of Rosoka.  Rosoka brings the power of automated

What’s Happening In Forensics – Sep 18, 2019

Liam Barry shares his experience of the Magnet User Summit. Arman Gungor talks about how to uncover timestamps in forensic email examination. Ewen O’Brien, writing in Digital Forensics Magazine, talks about how stress and burnout are two huge security and

Sneak Peak Of New Belkasoft Evidence Center 2020

Belkasoft announces the upcoming release of its Belkasoft Evidence Center 2020 v.9.7. The new version significantly expands the mobile forensics and remote acquisition. Among new features are acquisition of MTK based devices; acquisition via MTP/PTP protocols; iTunes backups support for

What’s Happening In Forensics – Sep 16, 2019

Craig Hinkley talks about preventing burnout for cybersecurity and digital forensics professionals. Cellebrite’s UFED Chinex Kit can now extract data from non-standard Chinese phones.

MSAB Launches Mobile Forensics Blog

MSAB believes that knowledge is a powerful tool to help make the world a safer place. That is why we are so happy to announce the launch of our Mobile forensics blog. This forensic and evidence-centered blog focuses on news,

Four Critical Success Factors In Mobile Forensics

by Mike Dickinson, Deputy Executive Officer at MSAB The purpose of this paper is to encourage mobile forensic practitioners to consider a wider number of critical factors surrounding their choice and use of mobile forensic tools. Specifically, the quality of

What’s Happening In Forensics – Sep 13, 2019

Josh Hickman discusses the challenges of extracting data from the Wickr messaging app. Andrea Fortuna talks about browser fingerprinting. Adam Harrison shares his unofficial write-up of the Defcon DFIR CTF. Criminals have managed to use artificial intelligence to replicate the

How To Acquire Data From A Mac Using MacQuisition

Depending on the digital forensic imaging tool you have available, creating a forensic image of a Mac computer can be either an anxiety-creating situation, or as easy as “1-2-3-START”. There are several things you must identify ahead of attempting a

How To Acquire Data From A Mac Using MacQuisition

Written by: Justin Matsuhara, Solutions Engineer, BlackBag Technologies Stephanie Thompson, Solutions Engineer, BlackBag Technologies Depending on the digital forensic imaging tool you have available, creating a forensic image of a Mac computer can be either an anxiety-creating situation, or as

Chrome Nuts And Bolts: ChromeOS / Chromebook Forensics

Jessica Hyde discusses her research on Google Chrome at DFRWS EU 2019. Jessica: Hey, everyone. Good morning. So we’re going to be talking about forensics of Chromebooks, as Hans just mentioned. Just a little bit about me, I work as

Chrome Nuts And Bolts: ChromeOS / Chromebook Forensics

Jessica Hyde discusses her research on Google Chrome at DFRWS EU 2019. Jessica: Hey, everyone. Good morning. So we’re going to be talking about forensics of Chromebooks, as Hans just mentioned. Just a little bit about me, I work as

Register For Webinar: Griffeye Brain In Analyze DI Pro

Join us for this highly anticipated webinar and learn about Griffeye’s new and advanced AI technology: Griffeye Brain. When dealing with masses of previously unseen images and videos, investigators are often forced to work in the dark without really knowing

What’s Happening In Forensics – Sep 10, 2019

Craig Ball talks about how career changes can bring about personal existential doubts. Oxygen Forensics show how to use KeyScout, a utility which uncovers and extracts user data and passwords. Harlan Carvey provides a brief history of DFIR time and