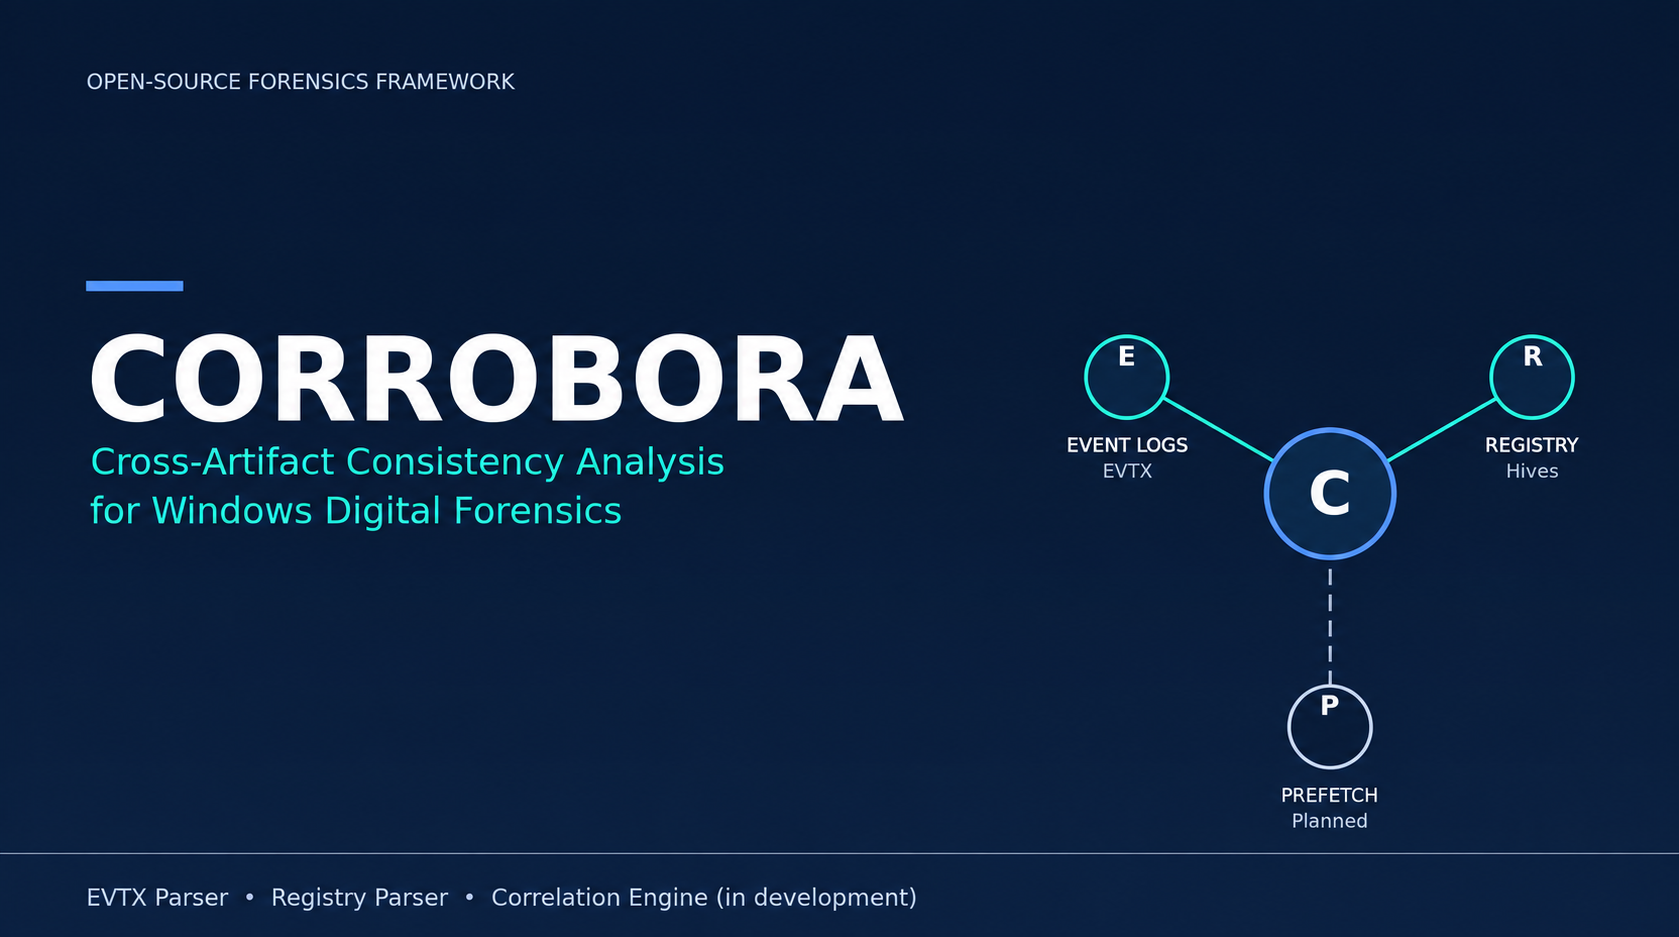
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 28 Sep 2026

ADF Solutions Named A Major Player In IDC MarketScape For Worldwide Digital Forensics Platforms 2026 Vendor Assessment

ADF Solutions Named A Major Player In IDC MarketScape For Worldwide Digital Forensics Platforms 2026 Vendor Assessment

ADF Solutions has been named a Major Player in the IDC MarketScape: Worldwide Digital Forensics Platforms 2026 Vendor Assessment, recognizing the company's continued focus on intelligent triage, automation, and AI-driven digital investigations....read more
Go Beyond The Basics With XRY Kiosk From MSAB

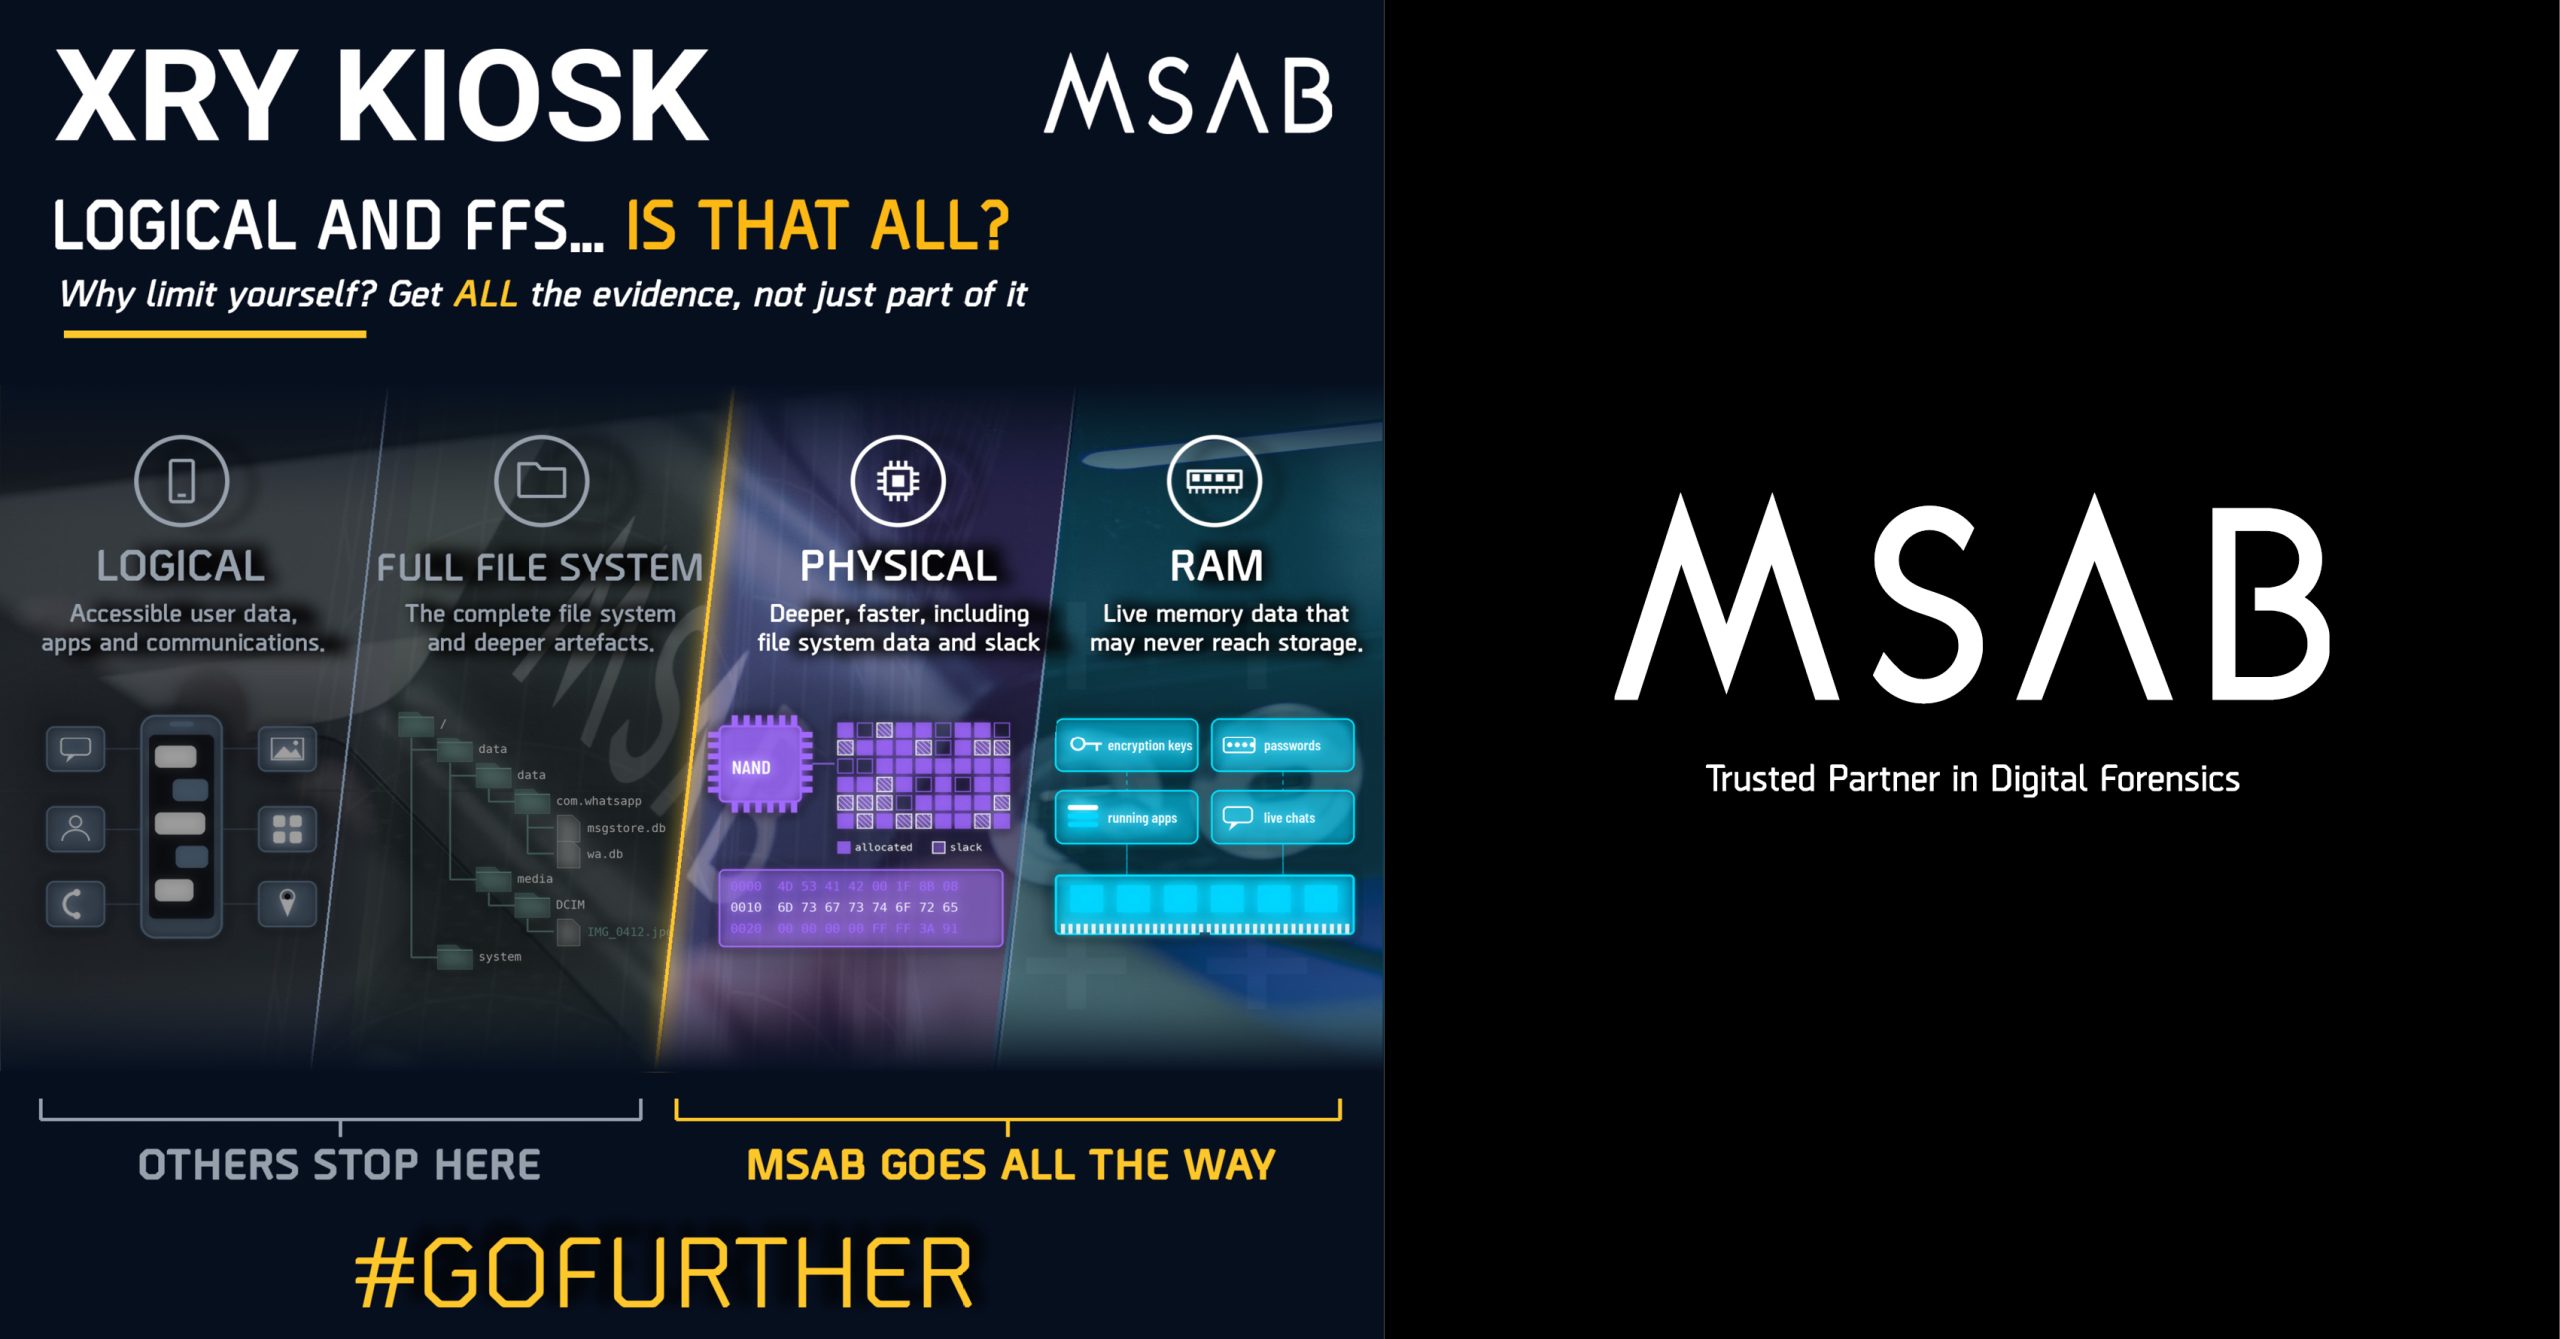
Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
MPE+ Android Malware Detection webinar now online

A recorded version of Lee Reiber’s recent webinar “MPE+ Android Malware Detection” can now be viewed here. Please use this forum topic for discussion of the webinar and for asking Lee any questions, thank you.

Mobile Forensics: MPE+ Android Malware Detection

Presenter: Lee Reiber, Global Director of Mobile Forensics, AccessData Join the forum discussion here.View the webinar on YouTube here.Read a full transcript of the webinar here. Transcript Lee Reiber: Good morning! Or afternoon, or wherever you guys might be. I

IntaForensics Announces Lima Lite 20% Pre-Launch offer!

IntaForensics Announces Lima Lite entry level Forensic Case Management for £695.00 + local taxes (less 20% pre-launch offer) including support and all updates for 1 year. A leap forward for sole digital forensic practitioners, incident response, cyber security teams, small

Forensic Control Reviews Latest Version of Internet Evidence Finder (IEF)

Internet Evidence Finder (IEF), the industry-leading forensic software from Magnet Forensics that recovers existing and deleted data from 220+ Internet-related artifacts has been reviewed by Jonathan Krause of Forensic Control. To read the full report and learn more about IEF’s

Article: Mobile Device Geotags & Armed Forces

In recent years it has been noticeable that the amount of people carrying a smart phone has increased exponentially. This is down to their low price and availability; even children as young as 12 have a smart phone. However, most

Why Use IEF to Search for Internet-Related Artifacts? Efficiency!

[Republished from the Magnet Forensics blog by Lance Mueller, Director of Forensics – Magnet Forensics (formerly JADsoftware).]Well, it’s day two for me at Magnet Forensics, and I thought I would take the opportunity to say “hello” to everyone and briefly

Article: Interpretation of NTFS Timestamps

File and directory timestamps are one of the resources forensic analysts use for determining when something happened, or in what particular order a sequence of events took place. As these timestamps usually are stored in some internal format, additional software

Nuix upgrades philanthropic product Proof Finder

Nuix has released Proof Finder 4.2, delivering advanced new features for eDiscovery and investigation professionals. This upgrade extends Nuix’s partnership with Room to Read, a global non-profit organization that seeks to transform the lives of children in Asia and Africa

Mobile Device Geotags & Armed Forces

In recent years it has been noticeable that the amount of people carrying a smart phone has increased exponentially. This is down to their low price and availability; even children as young as 12 have a smart phone. However, most

Industry Veteran & Thought Leader Lance Mueller Joins Magnet Forensics Team

With a strong commitment to helping thousands of its customers in the world’s top law enforcement, military, government and corporate organizations recover data from a broad range of Internet-related communications, Magnet Forensics (formerly JADsoftware) has brought industry veteran and thought

Webinar (Mobile Forensics): MPE+ Android Malware Detection

Malware on computers can infect, transmit and “sell” personal data. Malware can also be used to “blame” and cast doubt on collected evidence in a computer examination. If this is the case, why aren’t these items being scanned when conducting

Interpretation of NTFS Timestamps

Introduction File and directory timestamps are one of the resources forensic analysts use for determining when something happened, or in what particular order a sequence of events took place. As these timestamps usually are stored in some internal format, additional

The ticking time bomb known as cloud forensics

We’ve seen the news reports with carloads of FBI agents, windbreakers and all, rushing into a business to seize paper records and servers. The evidence is analyzed later to prove a crime using computer forensics. However, the more likely use