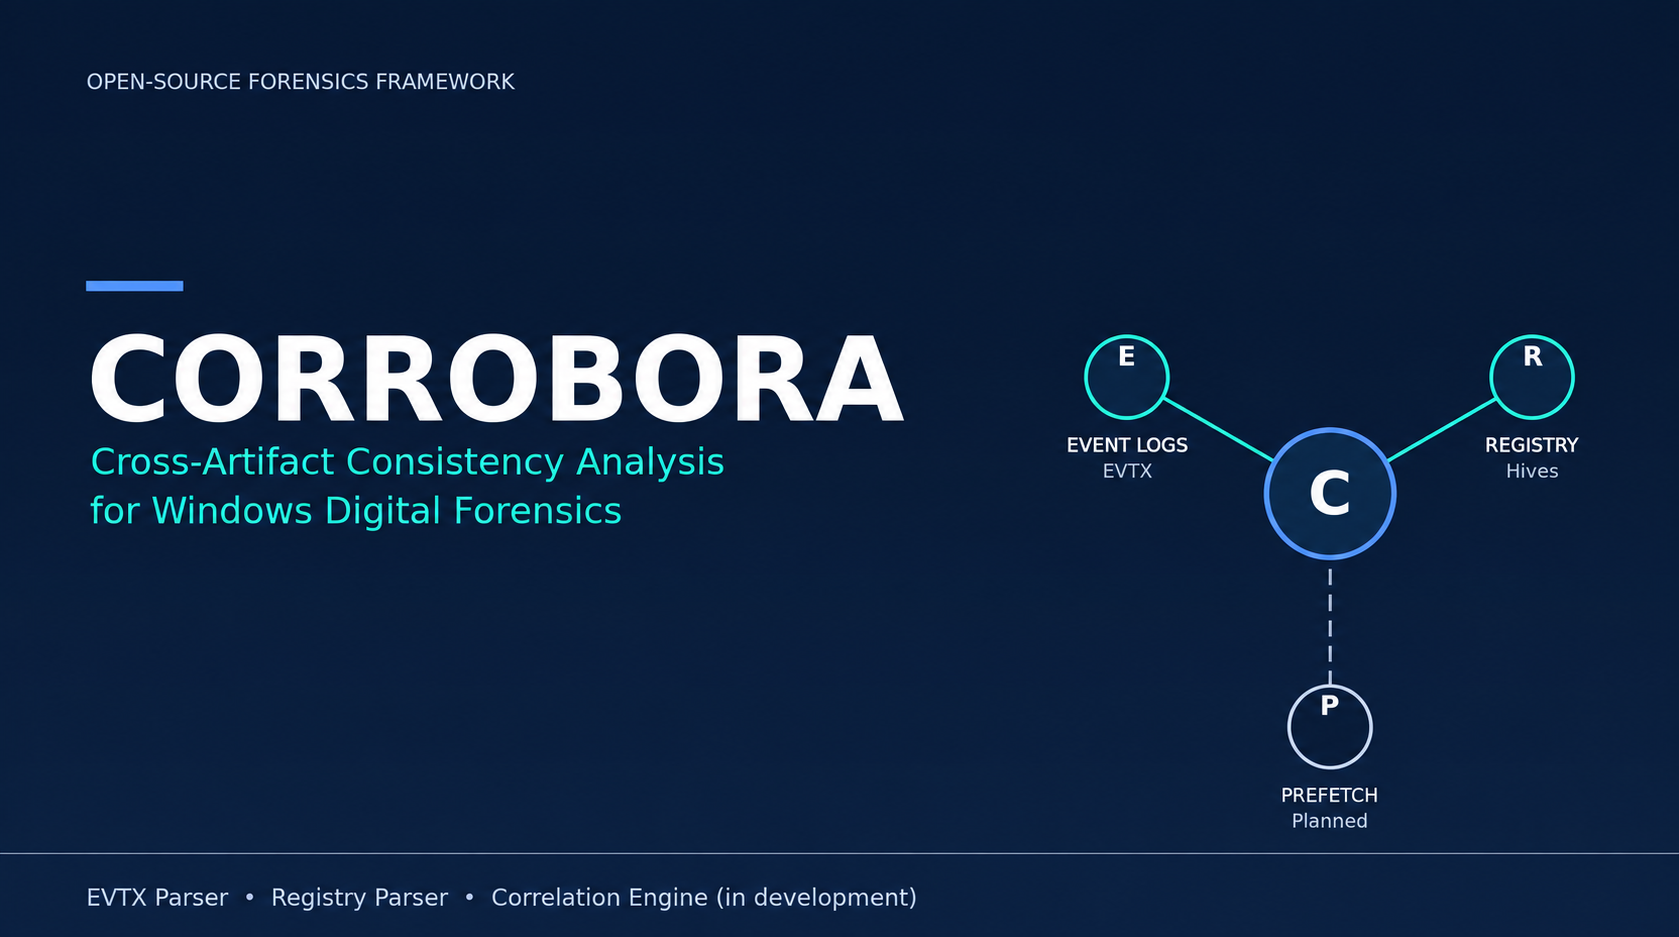
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 28 Sep 2026

ADF Solutions Named A Major Player In IDC MarketScape For Worldwide Digital Forensics Platforms 2026 Vendor Assessment

ADF Solutions Named A Major Player In IDC MarketScape For Worldwide Digital Forensics Platforms 2026 Vendor Assessment

ADF Solutions has been named a Major Player in the IDC MarketScape: Worldwide Digital Forensics Platforms 2026 Vendor Assessment, recognizing the company's continued focus on intelligent triage, automation, and AI-driven digital investigations....read more
Go Beyond The Basics With XRY Kiosk From MSAB

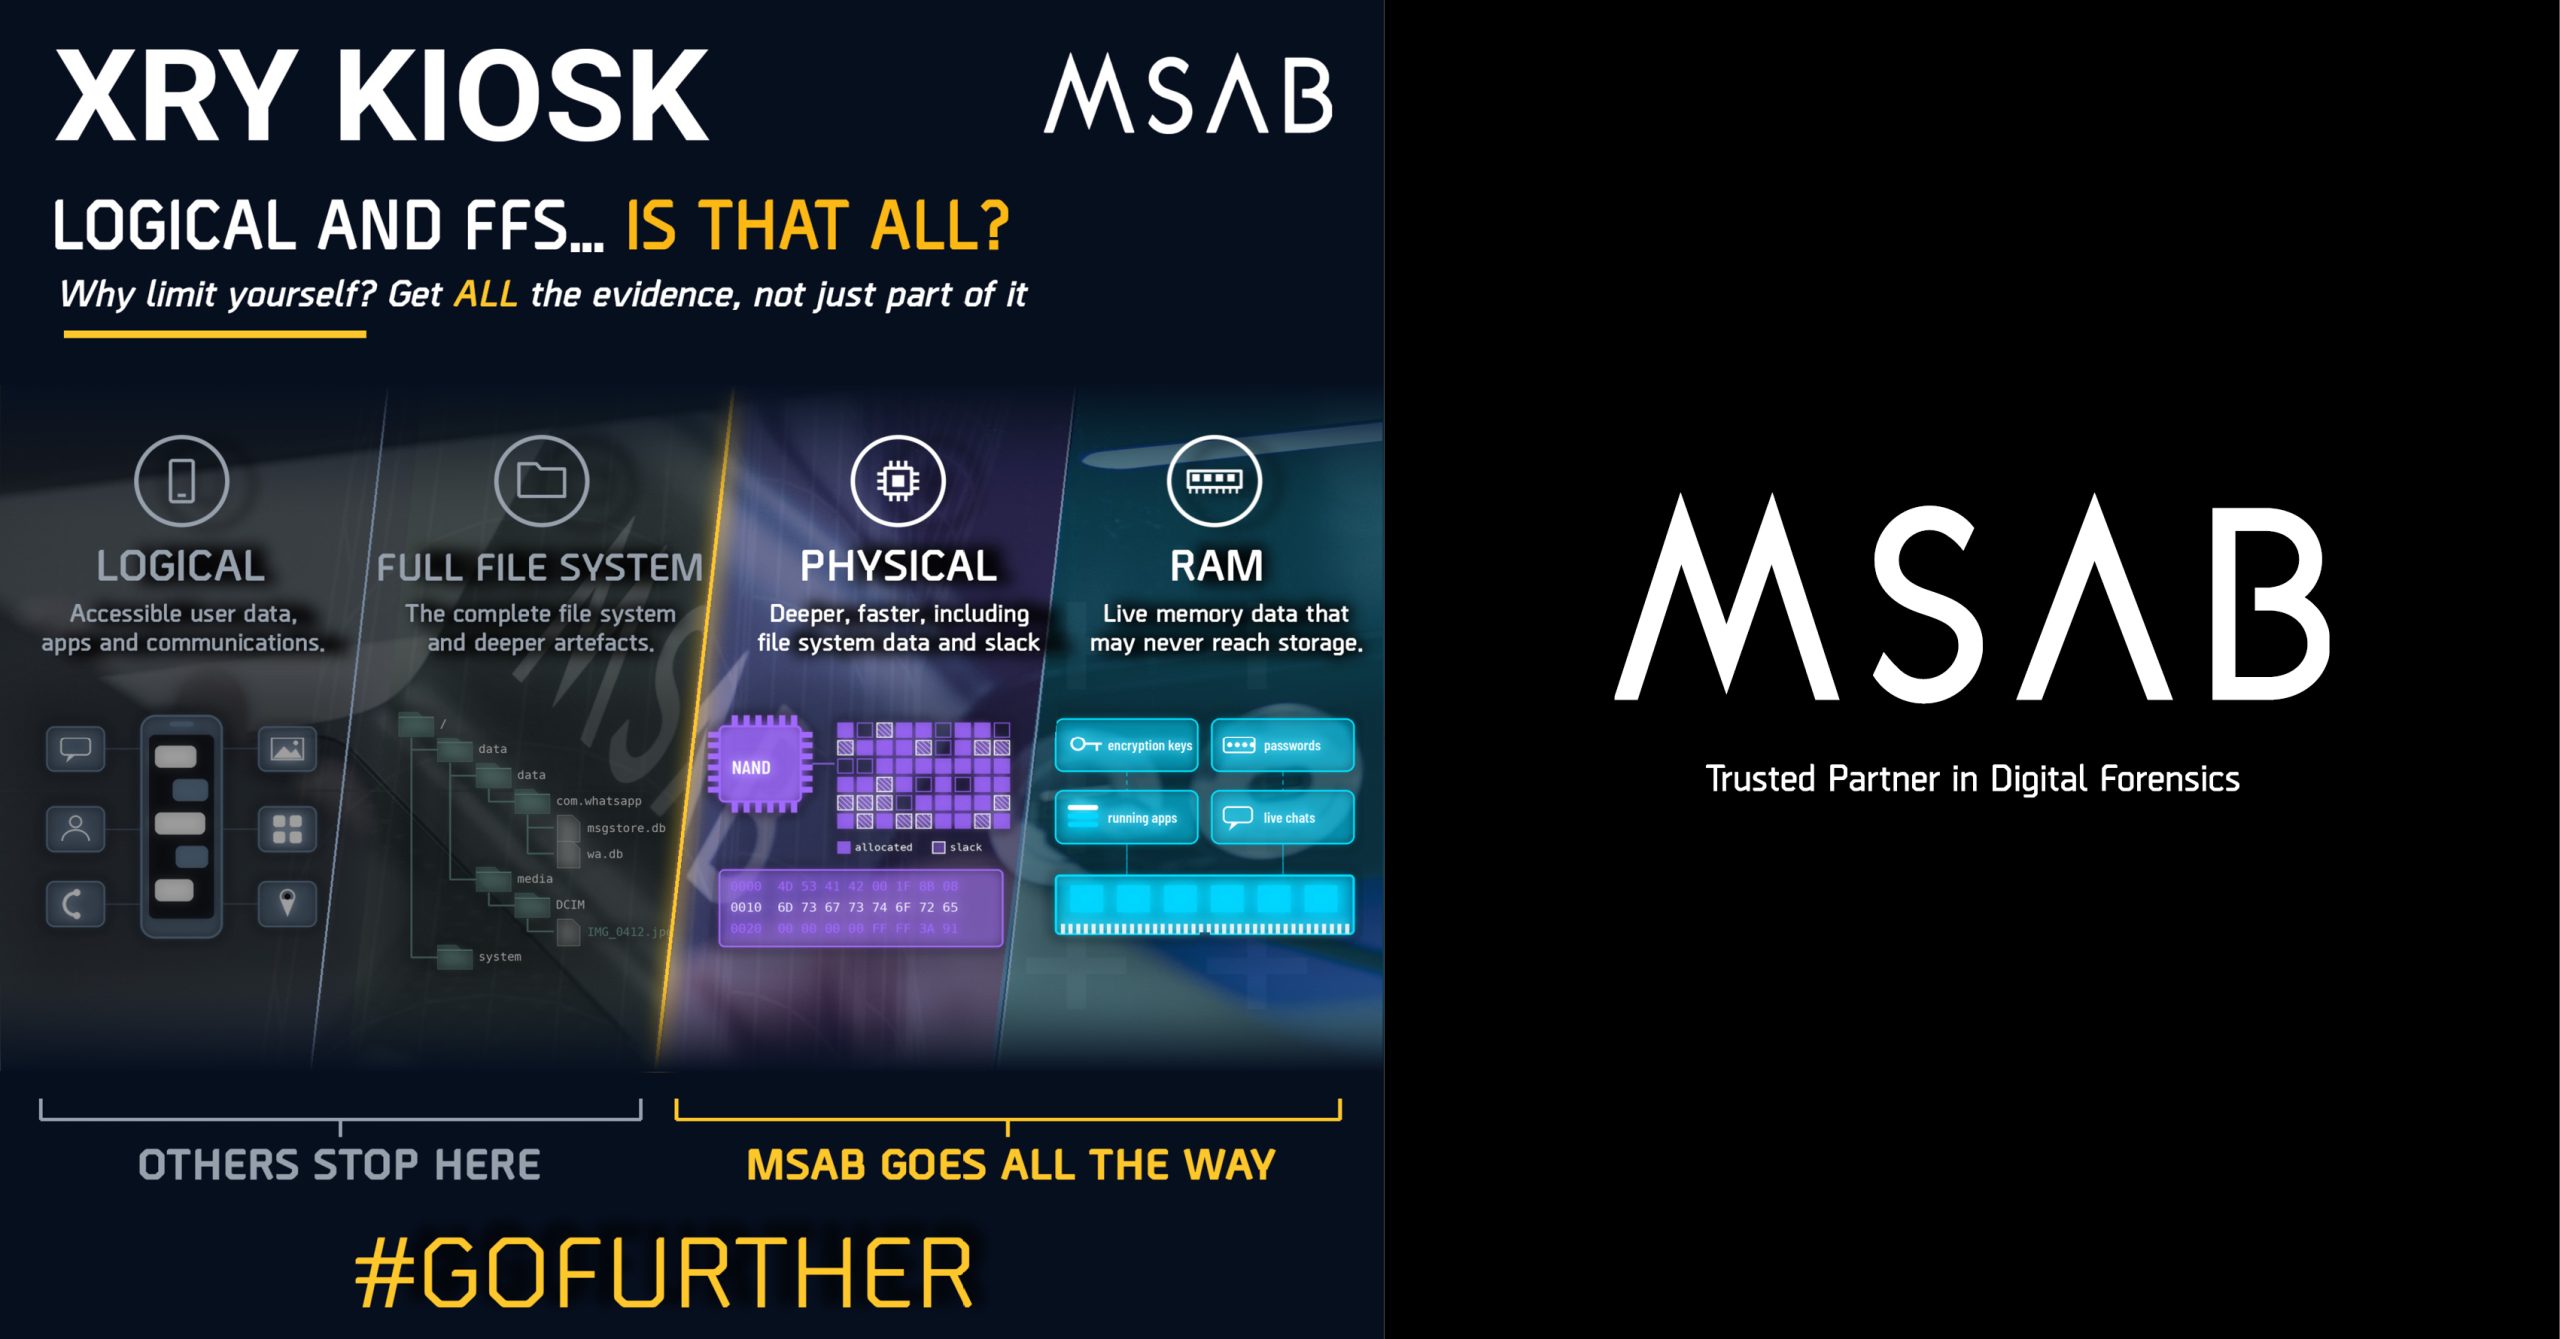
Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more

Lee Reiber, Global Director of Mobile Forensics, AccessData

Lee, you previously worked in law enforcement and were the CEO of a prominent mobile phone training company. Can you tell us more about your background and how you came to work for AccessData? I worked in law enforcement for

Forensics Europe Expo Announce Free to Attend Workshop Programme for Visitors

Forensics Europe Expo, 24 – 25 April 2013, Olympia, London, sponsored by LGC Forensics, in Collaboration with Forensic Science Society and organised in partnership with The Investigator has been designed as the premier international forum for sourcing forensics products, equipment

INTERNET EVIDENCE FINDER Adds Mac OS X File System Support & Timeline Feature

With a strong commitment to helping thousands of its customers in the world’s top law enforcement, military, government and corporate organizations recover data from a broad range of Internet-related communications, Magnet Forensics (formerly JADsoftware) has launched v6.0 of its industry-leading

Belkasoft Releases Free Kernel-Mode Live RAM Capturing Tool

Belkasoft has released a new kernel-mode forensic tool to capture the content of the computer’s volatile memory. Belkasoft RAM Capturer offers forensic specialists the ability to take snapshots of the computer’s volatile memory (“memory dumps”) even if an anti-dumping protection

EuroForensics 2013: 4th International Forensic Sciences Conference & Exhibition

Euroforensics 2013: 4th International Forensic Sciences, Cyber Security and Surveillance Technologies Conference & Exhibition takes place in Harbiye Military Museum Istanbul, Turkey 27-29 March 2013. The 4th Euroforensics has been designed as the primary international conference and exhibition for sourcing

BlackBag Technologies Announces BlackLight(R) 2013 R1 Forensic Software Release

BlackBag Technologies, Inc. has announced the immediate availability of BlackLight 2013 R1, a comprehensive iPhone, iPad, and Mac OS X forensic analysis tool. This latest release includes a timeline feature that displays device usage and communications chronologically, and adds Windows

Nuix 4.2 upgrade delivers toolset for large-scale digital investigations

Nuix has released version 4.2 of its investigation software. New digital forensics capabilities in this release round out Nuix’s investigative feature set, making it an essential tool for any government or private-sector organization needing to complete large-scale investigations efficiently and

Phones Can Be Searched If No Password Lock: Ontario Court

Ontario’s highest court has signalled that the right of police officers to look through someone’s phone depends on whether there’s a password. The Court of Appeal for Ontario says it’s all right for police to have a cursory look through

Reconnoitre from Sanderson Forensics updated

Sanderson Forensics are pleased to announce an update to our most recent software tool Reconnoitre. Reconnoitre allows the forensic investigator to quickly and easily investigate images containing volume shadow copies, without the need to run VSSAdmin. This latest version adds

New Free Tool: Decrypting the Dropbox filecache.dbx file

Republished from the MagnetForensics.com blog by Jad Saliba, Founder & CTO of Magnet Forensics (formerly JADsoftware) I would like to introduce a new free tool we’ve just released to the forensics community called Dropbox® Decryptor. But first, some background. Dropbox