Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

Preparing Digital Multimedia Evidence For Court: What To Consider Before Presentation

Hero Image

Effective courtroom presentation starts with careful preparation - discover how Amped Replay helps forensic professionals prepare clear, accurate and properly documented digital multimedia evidence for court....
Today's headlines 29 Oct 2026

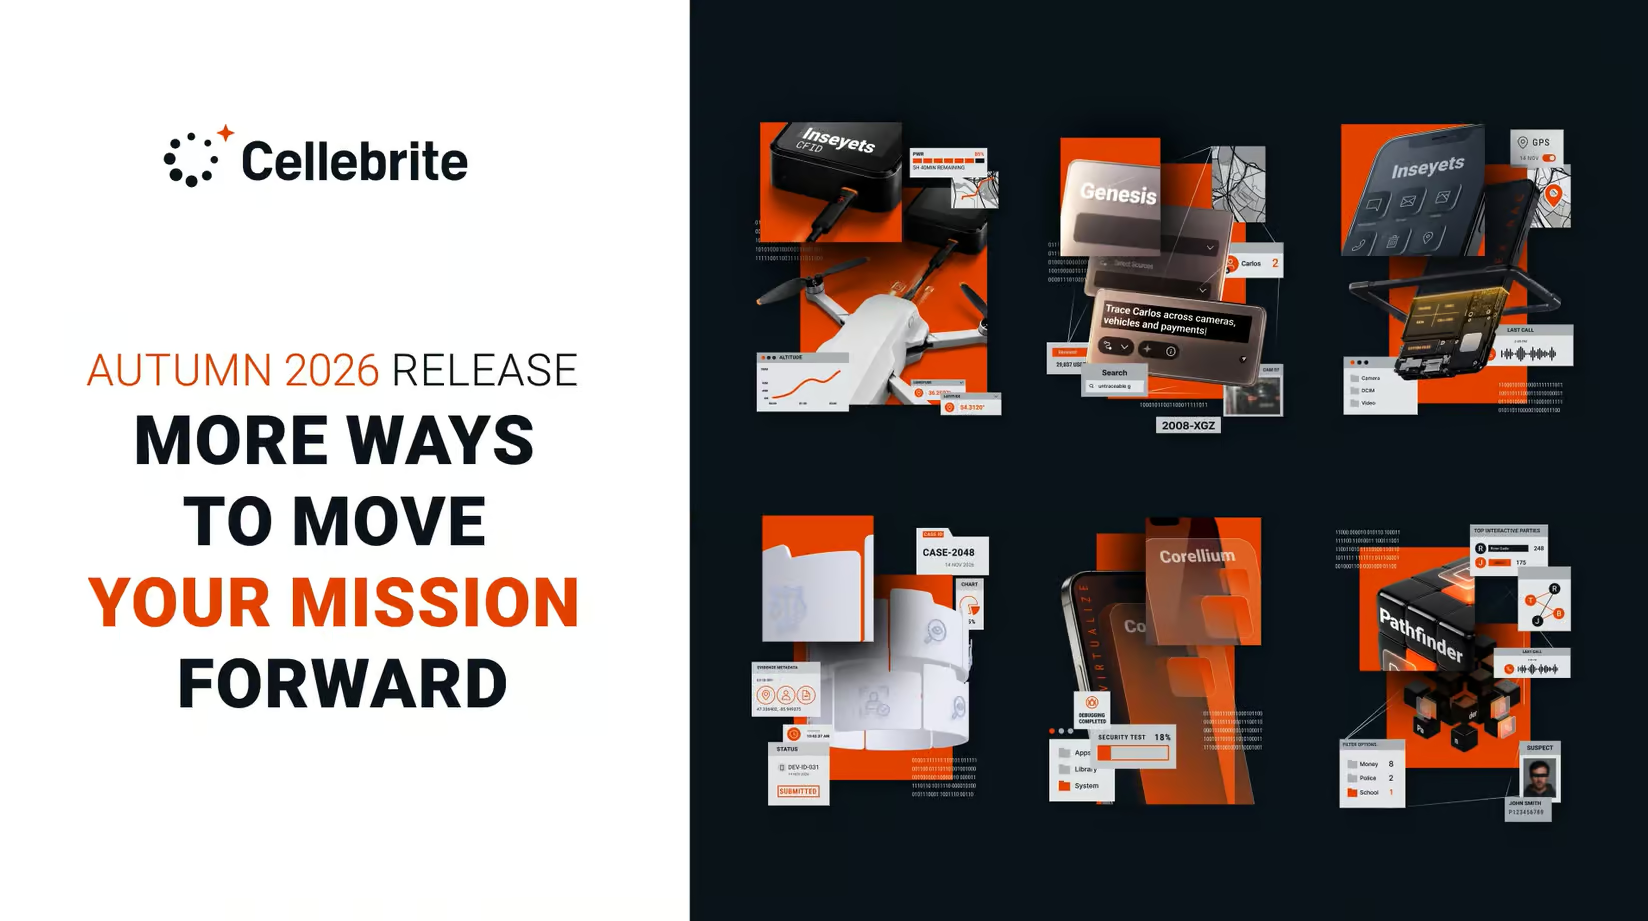
Explore Cellebrite’s Autumn 2026 Release: Discover What’s New

Explore Cellebrite’s Autumn 2026 Release: Discover What’s New

Discover how the Cellebrite Autumn 2026 Release is transforming digital investigations with faster access to evidence, AI-powered insights and seamless collaboration....read more
Agentic AI For Digital Investigations: Matt Goeckel Introduces Cellebrite Genesis

Agentic AI For Digital Investigations: Matt Goeckel Introduces Cellebrite Genesis

Cellebrite’s Matt Goeckel joins the Forensic Focus Podcast to talk about Genesis, an AI tool that lets investigators ask questions of their evidence, decode raw databases and stay within the scope of a warrant, while examiners stay in control....read more
End-To-End Digital Investigations: From First Access To Final Verdict

End-To-End Digital Investigations: From First Access To Final Verdict

Discover how Magnet Forensics’ integrated platform, from Graykey and Axiom to Automate, Review and Verify, helps agencies cut backlogs, collaborate in real time and build defensible cases from first access to final verdict....read more
Geo-tagging and Photo Tracking on iOS

As you may already know, Apple has always been criticized for using their extremely popular devices to track users and use this information to expand their own databases. This tutorial assumes that you have already jailbroken your device and you

Geo-tagging & Photo Tracking On iOS

As you may already know, Apple has always been criticized for using their extremely popular devices to track users and use this information to expand their own databases. This tutorial assumes that you have already jailbroken your device and you know how to

KS – an open source bash script for indexing data

This is a keywords searching tool working on the allocated, unallocated data and the slackspace, using an indexer software and a database storage. Often during a computer forensics analysis we need to have all the keywords indexed into a database

Belkasoft Evidence Center 5.3: New Tool to Share Collected Evidence

Belkasoft announces a major update to its flagship forensic product, Belkasoft Evidence Center 2013. Version 5.3 introduces Evidence Reader, an all-new free tool allowing Belkasoft users to pass along evidence collected with the main product. Over 12 other enhancements are

KS – an open source bash script for indexing data

KS – an open source bash script for indexing data ABSTRACT:  This is a keywords searching tool working on the allocated, unallocated data and the slackspace, using an indexer software and a database storage . Often during a computer forensics

MPE+ Android Malware Detection webinar now online

A recorded version of Lee Reiber’s recent webinar “MPE+ Android Malware Detection” can now be viewed here. Please use this forum topic for discussion of the webinar and for asking Lee any questions, thank you.

Mobile Forensics: MPE+ Android Malware Detection

Presenter: Lee Reiber, Global Director of Mobile Forensics, AccessData Join the forum discussion here.View the webinar on YouTube here.Read a full transcript of the webinar here. Transcript Lee Reiber: Good morning! Or afternoon, or wherever you guys might be. I

IntaForensics Announces Lima Lite 20% Pre-Launch offer!

IntaForensics Announces Lima Lite entry level Forensic Case Management for £695.00 + local taxes (less 20% pre-launch offer) including support and all updates for 1 year. A leap forward for sole digital forensic practitioners, incident response, cyber security teams, small

Forensic Control Reviews Latest Version of Internet Evidence Finder (IEF)

Internet Evidence Finder (IEF), the industry-leading forensic software from Magnet Forensics that recovers existing and deleted data from 220+ Internet-related artifacts has been reviewed by Jonathan Krause of Forensic Control. To read the full report and learn more about IEF’s

Article: Mobile Device Geotags & Armed Forces

In recent years it has been noticeable that the amount of people carrying a smart phone has increased exponentially. This is down to their low price and availability; even children as young as 12 have a smart phone. However, most

Why Use IEF to Search for Internet-Related Artifacts? Efficiency!

[Republished from the Magnet Forensics blog by Lance Mueller, Director of Forensics – Magnet Forensics (formerly JADsoftware).]Well, it’s day two for me at Magnet Forensics, and I thought I would take the opportunity to say “hello” to everyone and briefly

Article: Interpretation of NTFS Timestamps

File and directory timestamps are one of the resources forensic analysts use for determining when something happened, or in what particular order a sequence of events took place. As these timestamps usually are stored in some internal format, additional software

Nuix upgrades philanthropic product Proof Finder

Nuix has released Proof Finder 4.2, delivering advanced new features for eDiscovery and investigation professionals. This upgrade extends Nuix’s partnership with Room to Read, a global non-profit organization that seeks to transform the lives of children in Asia and Africa