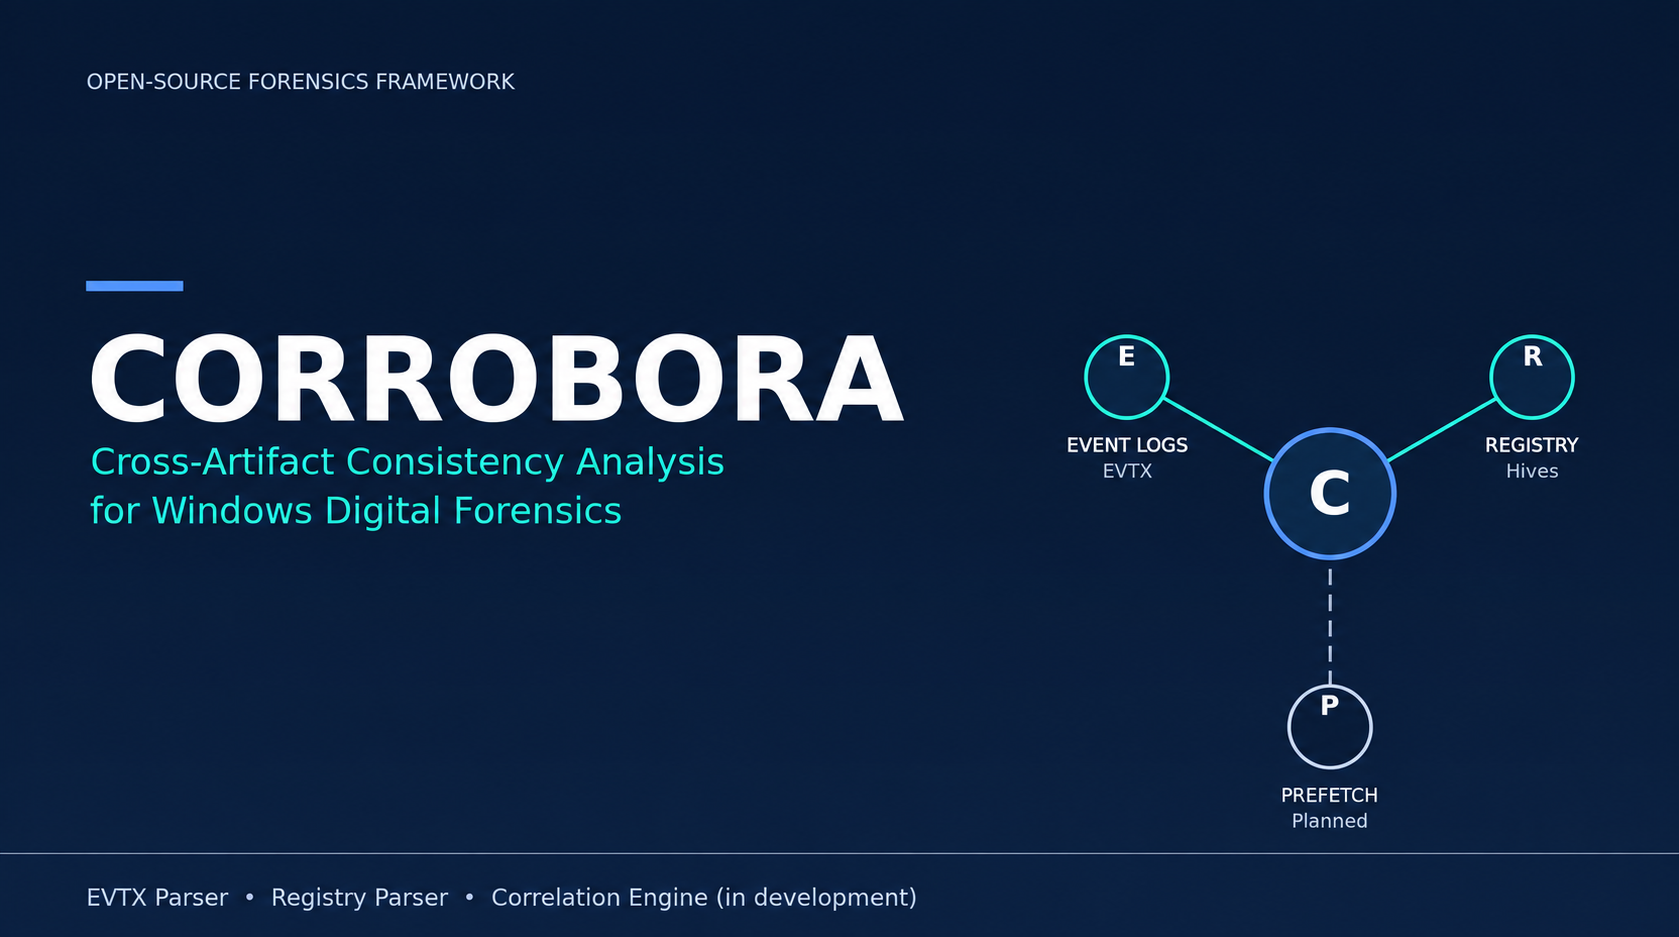
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

Today's headlines 25 Sep 2026

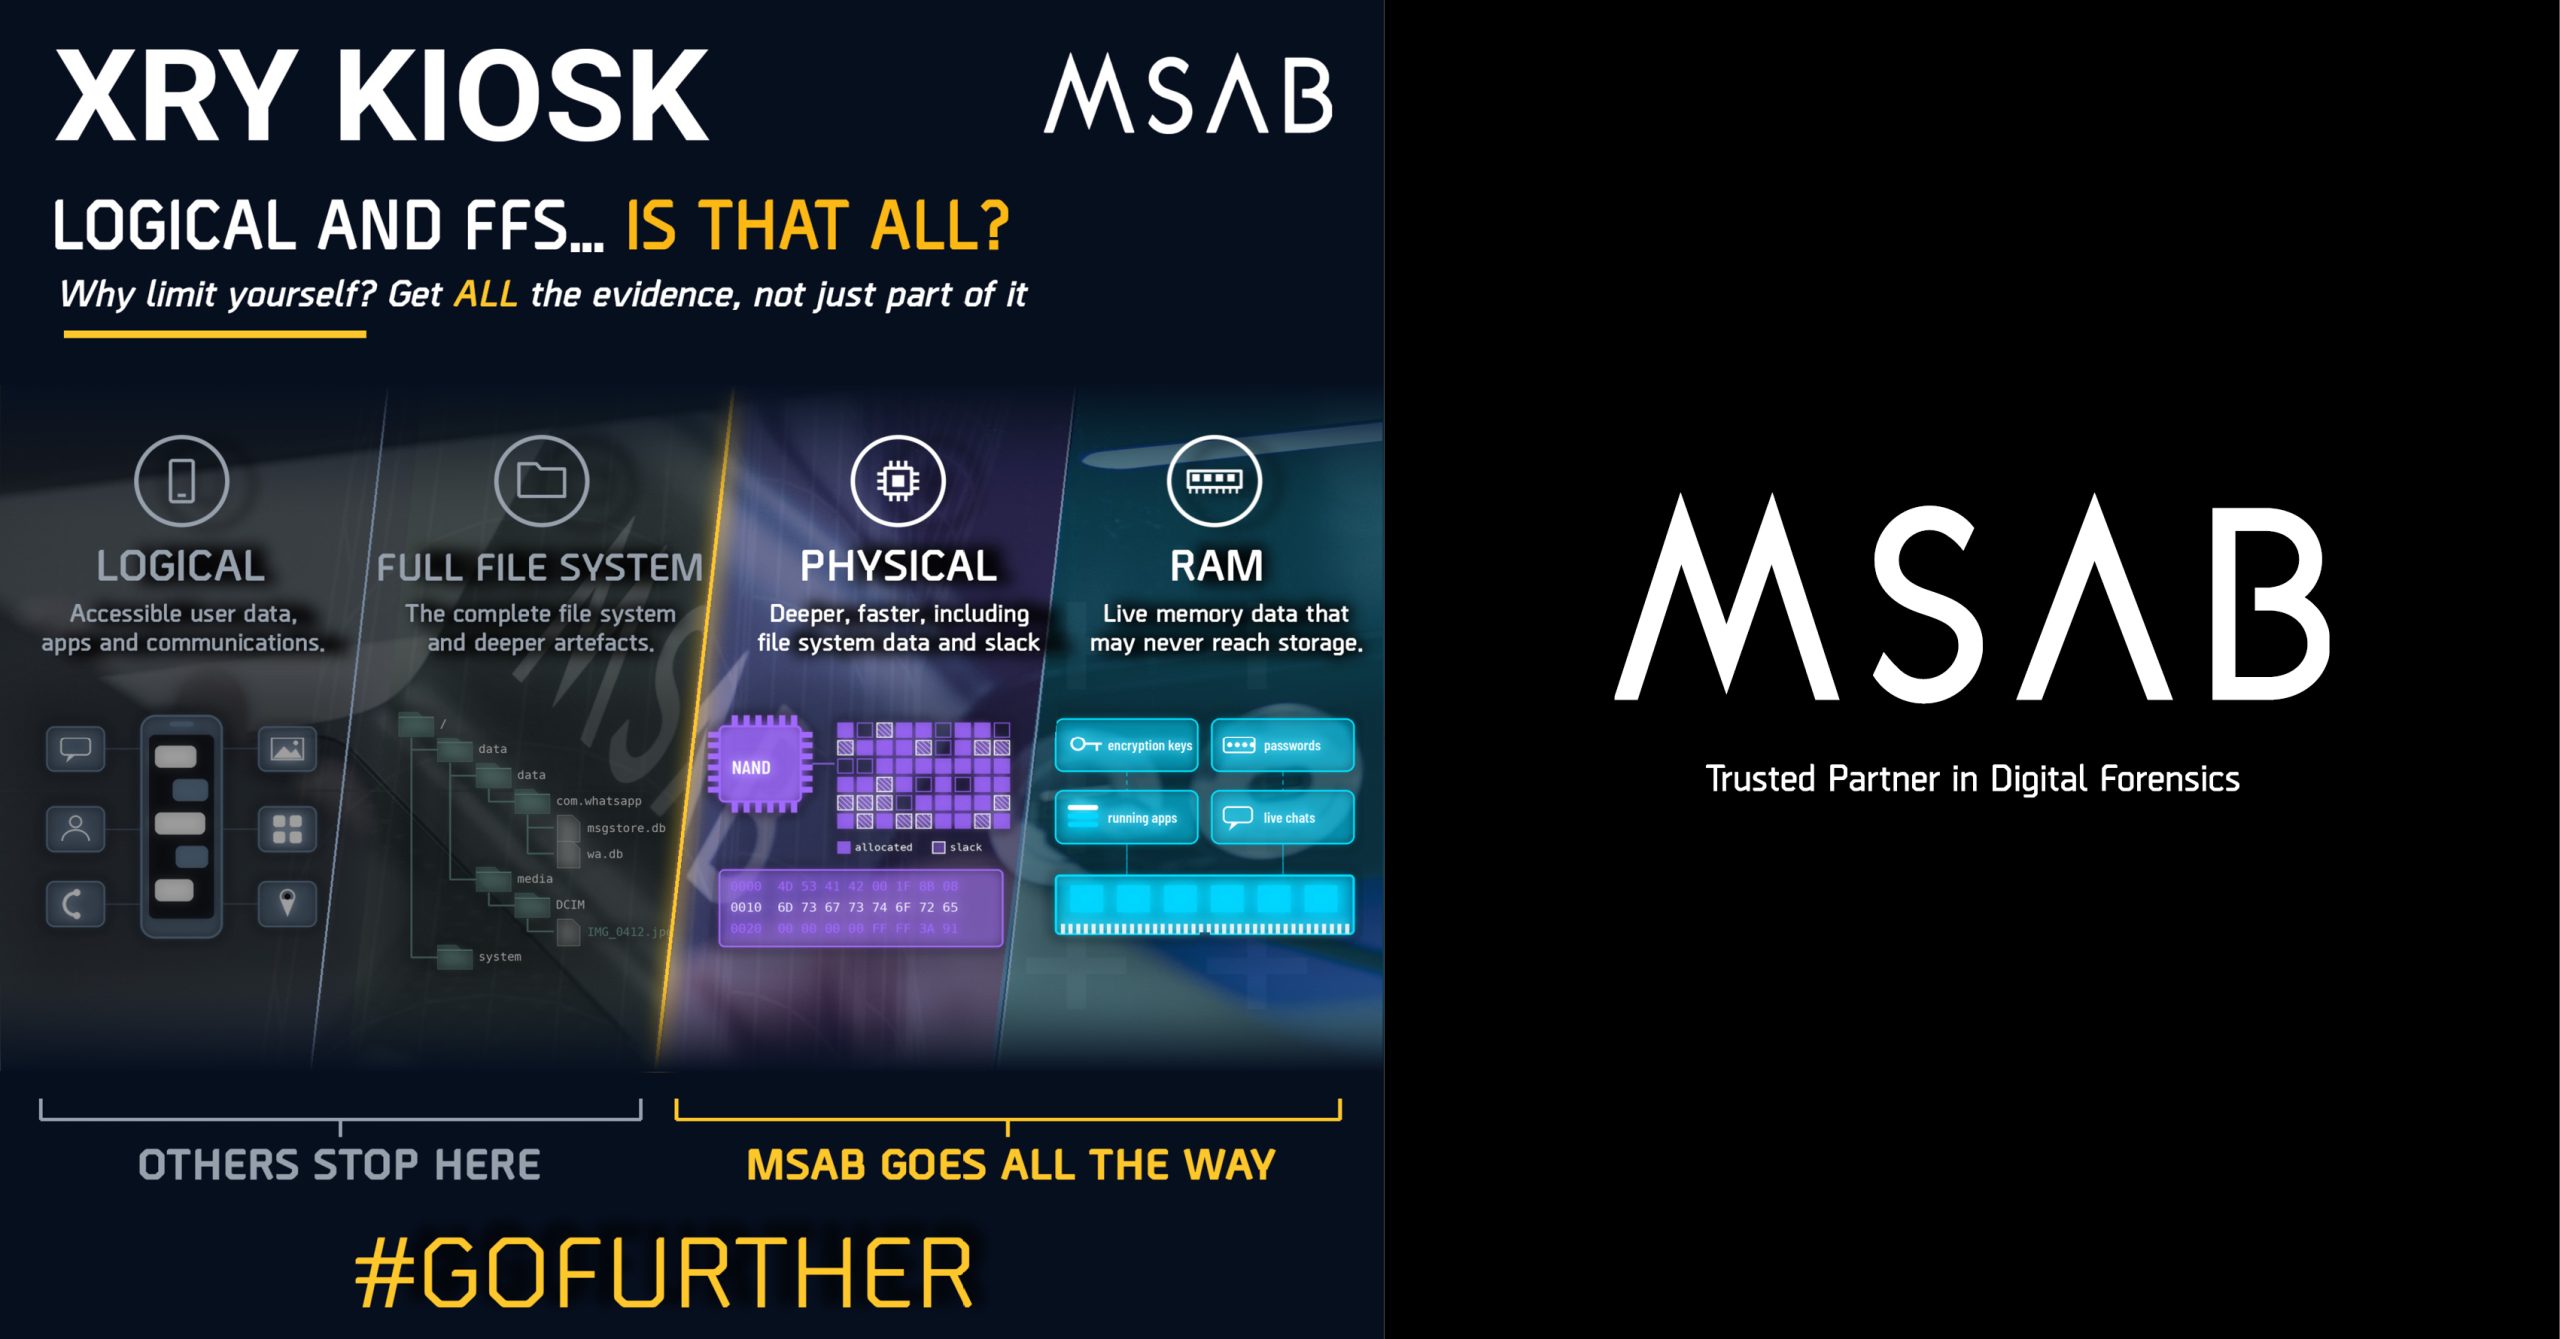
Go Beyond The Basics With XRY Kiosk From MSAB

Go Beyond The Basics With XRY Kiosk From MSAB

Go beyond the basics with XRY Kiosk - extract logical, full file system, physical and RAM data through controlled, compliant workflows built for fast frontline forensics....read more
How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more

Paraben Releases P2 Commander v2.0

Paraben is pleased to announce the release of P2 Commander v2.0. This new version is a major update offering many new features: What’s New: * Data triage (a snapshot of important sources of evidence such as e-mail databases, chat databases,

Malaysian Forensics Expert recovers data from waterlogged Blackberry

A mobile phone, believed to have been owned by one of four murder victims, including cosmetics millionairess Datuk Sosilawati Lawiya, had received a call from one ‘Datuk Pathma 2’, several hours before they were allegedly killed, the High Court here

EnCase® Certified Examiner program turns 10 this month

Guidance Software, Inc. is celebrating a decade of industry-leading computer forensic industry education and certification, as its EnCase® Certified Examiner (EnCE®) program turns 10 this month. More than 3,300 forensic examiners have earned the EnCE designation worldwide in those 10

Forensic Toolkit v3 Tips and Tricks ― Not on a Budget

by Sean L. Harrington "A couple of weeks ago, Brian Glass posted a very helpful comment, Forensic Toolkit v3 Tips and Tricks — on a Budget. His comment focused on how to “get close to SSD performance on the cheap”

iPhone Tracking – from a forensic point of view

Posted by 4rensiker "iPhoneTracking is sexy! Every mobile forensic suite, at least the ones dealing with iPhones, are providing it proudly. iPhoneTracking also has been a hot topic in the media all around the globe. People stated that there is

Android Forensics Study of Password and Pattern Lock Protection

Posted by Oxygen Software "Let’s see what Pattern Lock is, how to access, determine or even get rid of it? We’ll also speak about Password Lock Protection and find out what it has in common with Pattern Lock. And finally

Skype in eDiscovery

by Stuart Clarke, 7Safe "The EDRM (Electronic Discovery Reference Model) is a widely accepted workflow, which guides those involved in eDiscovery. Typically, the identification and collection phases see email and common office documents harvested, but as technology moves forward is

Forensic Toolkit v3 Tips and Tricks – On a budget

Posted by Brian K. Glass "While researching FTK 3X and Oracle, you just recently discovered that the best configuration of your Oracle database would be on a solid state drive (SSD). Solid state drives give the maximum level of performance

Anonymous, what does it mean?

Posted by forens245 "Anonymous, a word which Merriam-Webster describes as: of unknown authorship or origin, not named or identified, or lacking individuality, distinction, or recognizability. There are some in this world that wish to remain anonymous, not named or identified.

CCL-Forensics offers “dunk!” for cookie files

CCL-Forensics has developed “dunk!”, a software utility which parses cookie files, and presents the investigator with the data they contain. A free trial version of dunk! is available at www.ccl-forensics.com/dunk which gives complete functionality for a limited time. Thereafter licences

GCHQ to offer British firms expertise in cybercrime

Some of the secret technologies created at the government’s giant eavesdropping centre GCHQ are to be offered to private industry as part of new cyber security strategy being unveiled by ministers on Friday. The idea is likely to be one

French Gendarmerie Nationale chooses Cellebrite’s UFED

The French Gendarmerie Nationale has equipped its national N-TECH force with Cellebrite’s Universal Forensic Extraction Device (UFED) for its mobile forensic investigations. The Gendarmerie Nationale, in charge of public safety in France, is using the UFED to extract information from

Paraben Releases P2 Commander v2.0

Paraben is pleased to announce the release of P2 Commander v2.0. Here are some feature highlights: * New memory dump parser* Added support for Exchange 2010 (.EDB)* Added support for Chrome history, cookies, auto fill items, keywords, and login analysis*

Forensic Toolkit v3 Tips and Tricks ― Not on a Budget

A couple of weeks ago, Brian Glass posted a very helpful comment, Forensic Toolkit v3 Tips and Tricks — on a Budget.  His comment focused on how to “get close to SSD performance on the cheap” and he discussed the