Identifying Interception Possibilities for WhatsApp Communication
Hello everybody. My name is Dennis Wijnberg, and together with Dr Nhien-An Le-Khac, I’m presenting about Alternative Methods for WhatsApp interception. This research project was part of my dissertation in partial fulfillment of my Master of Science degree for the

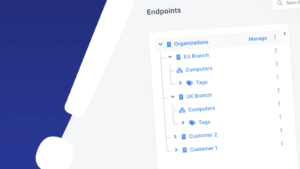
How to Automatically Tag Your Assets During an Investigation

Binalyze exclamation point logo with screenshot of list of endpoints
How many Web Servers, Mail Servers, Domain Controllers, and other critical assets do you have on your network or the network you have been asked to investigate? More often than not, nobody can answer this question quickly and this slows

Register For Webinar: AI Helping Good People Make This World Safer

Cyborg hand holding Cloud of justice and law icon bubble
Modern devices allow users to store a tremendous amount of data, including thousands of photos and videos. AI is one of the solutions that might significantly facilitate the investigator’s job and reduce the time they spend on manually analyzing significant

Your Car Is Recording: Metadata-Driven Dashcam Analysis System

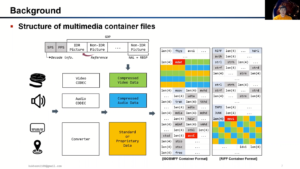
Hello everyone. Thank you for being at this presentation. My name is Kukheon Lee from Digital Forensic Research Center at Korea University. It is an honor to present. Thank you to the DFRWS committee for inviting us here. My presentation

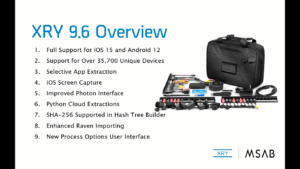
What’s New in XRY 9.6 and XAMN 6.2

Greg Masterson: Good afternoon, everybody. We’re going to get started here in a minute. We’re going to be introducing Kevin Kyono, a Technical Sales Engineer with MSAB to discuss the release of 9.6 of XRY and 6.2 of XAMN, and

Android File System Extraction With Oxygen Forensic Detective

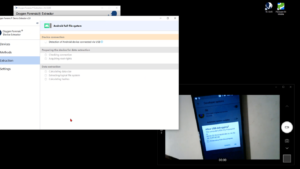
A screenshot of Oxygen Forensic Detective overlaid with video of an Android phone extraction process
Hey everyone, Keith Lockhart here from Oxygen Forensics Training. This video is a short look at the Android file system extractor. This option here in our Android extraction section of our forensic extractor for our devices. So, I’ve got the

Teaching the Next Generation of Cyber Sleuths

A cartoon graphic of a young Black girl in jeans, a t-shirt and jacket besides words describing the Cyber Sleuth Science Lab's mission
Hello, I’m Darryl Pfeif and I’m going to talk to you about our research project — ‘Introducing Digital Forensics in Secondary School’. This project was recorded with funding from the national science foundation and wouldn’t have been possible without the

Forensic Analysis of ReFS Journaling

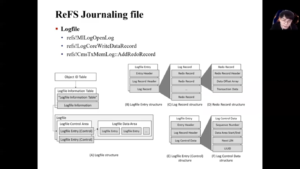
Hello, I am Seonho Lee from the Affiliated Institute of ETRI. Today, I talk about the forensic analysis of ReFS Journaling. Before everything, let me just briefly explain the two key topics of the presentation. I’m going to explain what

Capturing the Low Hanging Fruit: Analysis Phase

Holly: Hi everyone. My name is Holly Hagene, welcome to today’s webcast. We’ll get started in just a minute. First, a few reminders: all the lines have been muted to reduce background noise. We also encourage you to submit questions