A round-up of today’s digital forensics news and views:
Forensic Focus News
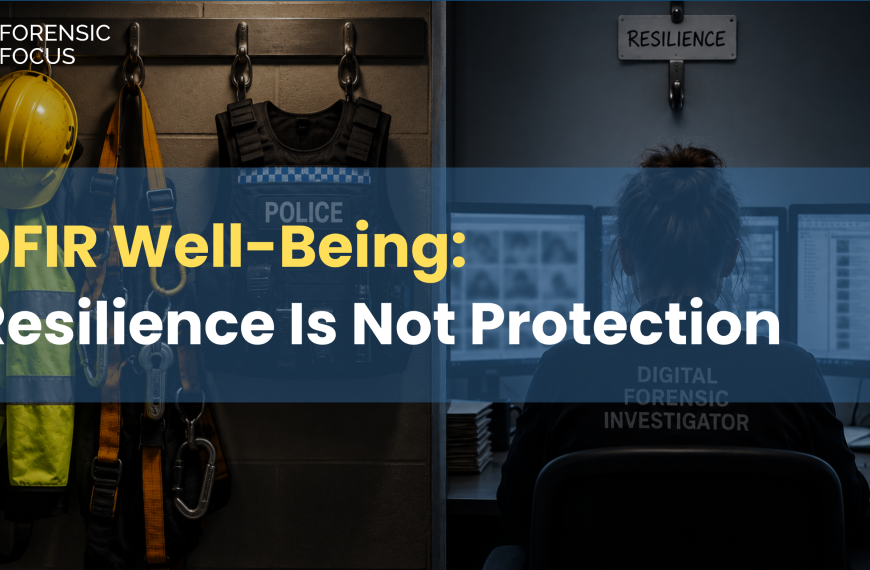
A Stab Vest Is Protection. DFIR “Resilience” Is Not.
We would never tell a police officer to face a blade with “resilience” instead of body armour, so why do we expect digital forensic investigators to face repeated trauma with little more than resilience to protect them?
Research & Techniques
SANS Releases Free 720-Page IR Framework
Joshua Wright has released Dynamic Incident Response (DAIR), a free 720-page framework available in all digital formats under Creative Commons, rebuilding SANS’s foundational incident response model for the first time in two decades. DAIR replaces the linear prepare-identify-contain-eradicate-recover model with an iterative, evidence-led approach that reflects how real incidents unfold, including contributions on ransomware, cloud, and OT environments.
Read more (dynamicincidentresponse.com)
zsh Modules Create macOS Forensic Blind Spots
macOS’s default shell, zsh, ships with loadable modules that enable TCP networking, file manipulation, and extended-attribute access entirely within the existing shell process, leaving no child-process telemetry for analysts to find. Attackers using zsh/net/tcp can retrieve and execute remote scripts without spawning curl, wget, or nc, while zsh/attr allows extended-attribute modification without xattr. DFIR practitioners hunting macOS compromises must look beyond process execution logs to network socket activity and filesystem metadata changes attributed to /bin/zsh itself.
Legal & Policy
Safe Cloud Storage Act Passes House
The U.S. House passed the Safe Cloud Storage Act by voice vote, removing a legal barrier that prevented law enforcement from using cloud providers to store and process digital evidence in child exploitation cases. Approved vendors operating under law enforcement contracts gain limited liability protection, subject to encryption requirements, cybersecurity safeguards, and restricted access controls. The bill now heads to the President after a return to the Senate for minor language changes.
Tools & Software
Volatility 3 2.28.2 Adds Linux Malfind Dumping
Volatility Foundation has released version 2.28.2 of its open-source memory forensics framework, introducing several practitioner-relevant changes. Linux analysts gain the ability to dump enumerated VMAs and pages via the Malfind plugin, while Windows Intel memory layers now include translation-based verification checks. macOS analysis support receives a deprecation warning, signalling reduced future support for that platform.
DFRWS Relaunches AFF4 Forensic Storage Working Group
DFRWS has reformed its working group on a common forensic storage format, anchored by AFF4 and AFF4-L, a scalable logical evidence container now under DFRWS stewardship. The AFF4-L draft standard specification has been publicly released, alongside two new implementations: the Gemini container-hashing tool built by a United Nations researcher and a Rust-based AFF4 library from Aletheian Labs.