Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

Investigating WMI Permanent Event Subscription Persistence

Hero Image

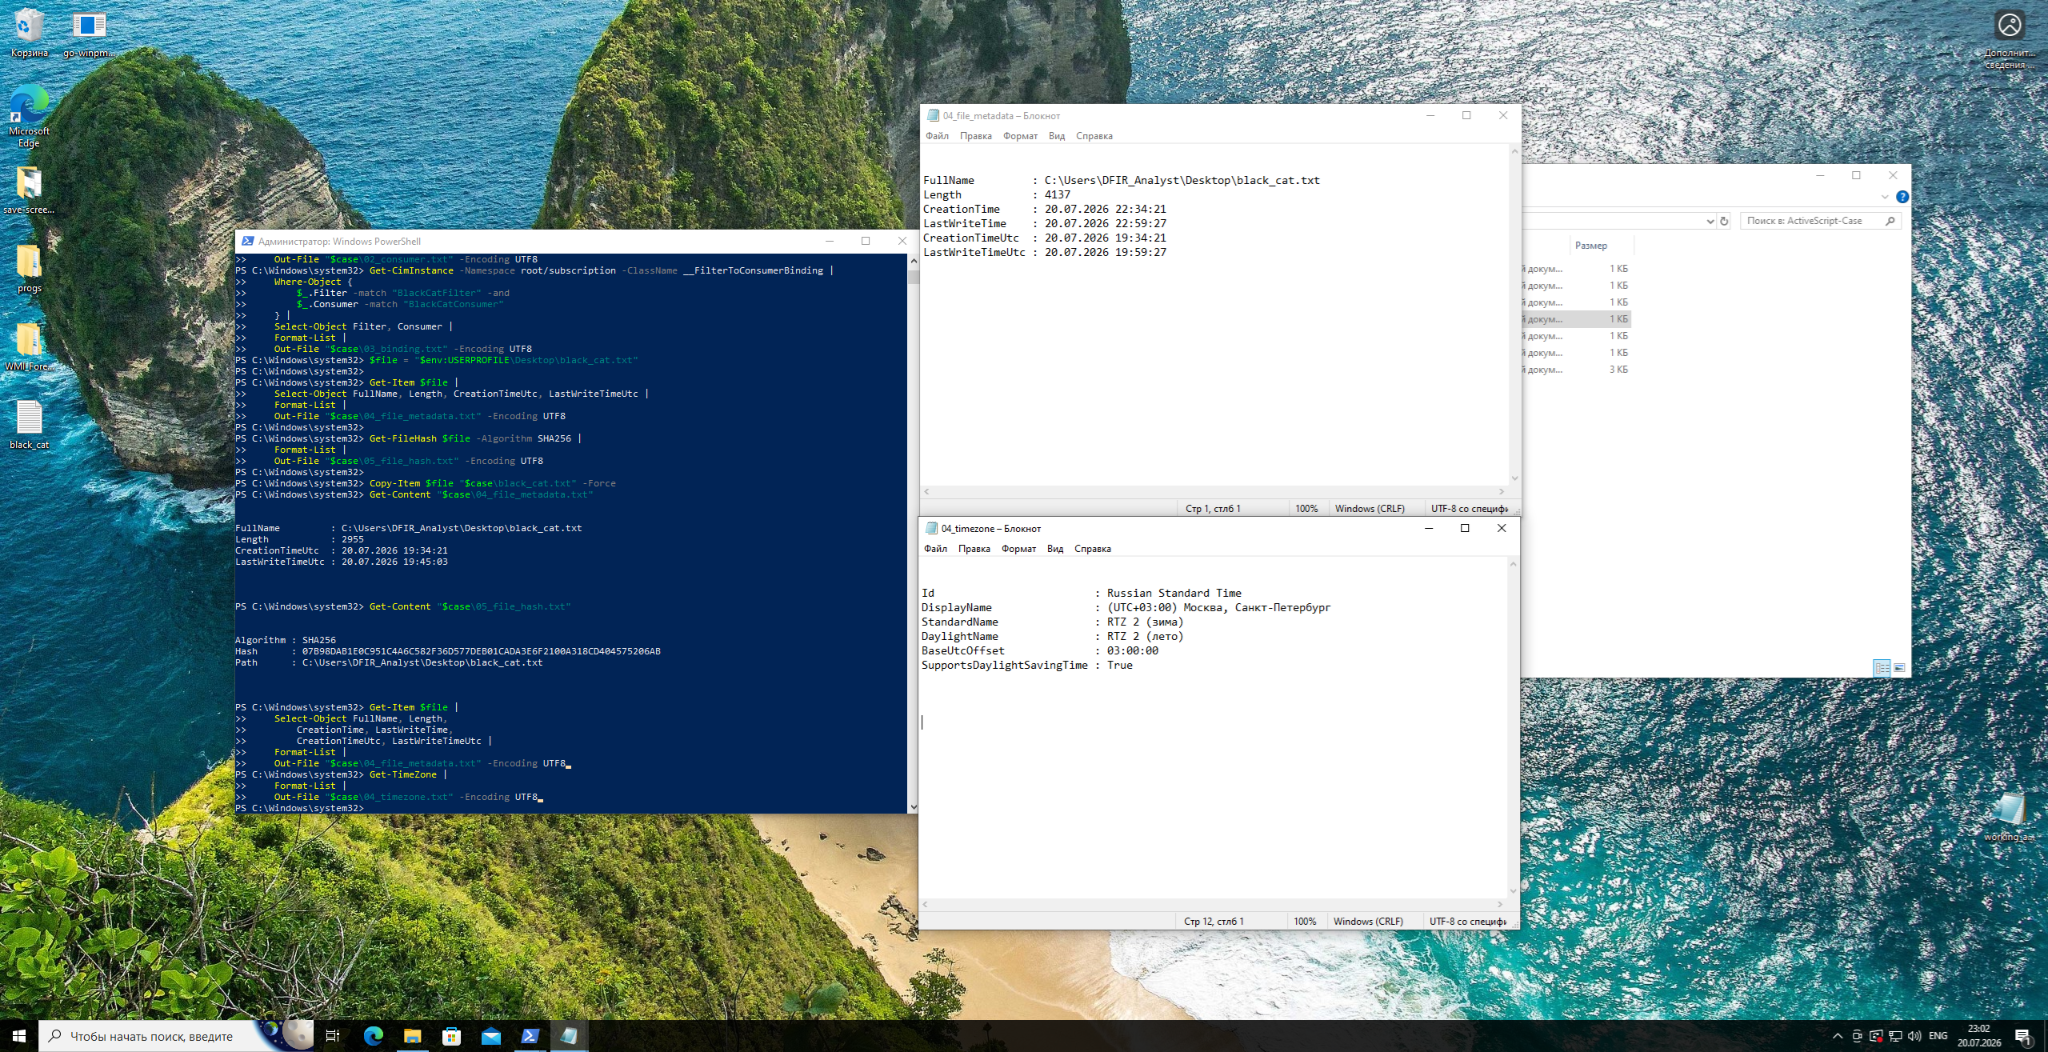
Vitalii offers a hands-on DFIR deep dive into WMI ActiveScriptEventConsumer persistence, from registration and execution to memory artifacts, Sigma detection, and cleanup....
Today's headlines 20 Oct 2026

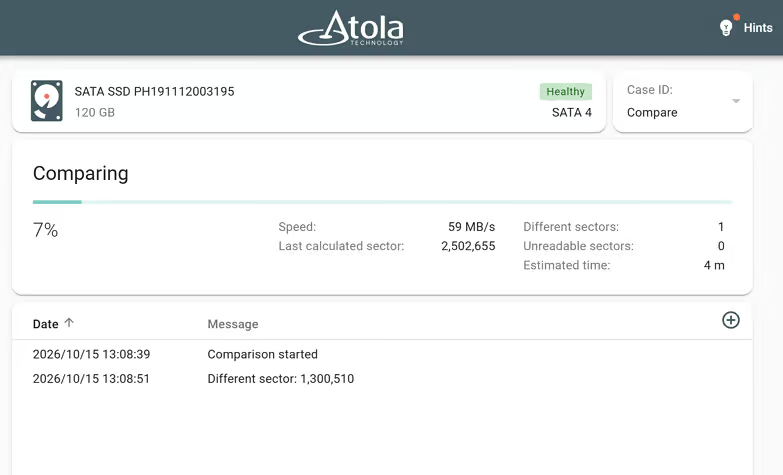
Atola TaskForce Gets A Massive Update Including A New Compare Module

Atola TaskForce Gets A Massive Update Including A New Compare Module

Meet Atola TaskForce firmware 2026.10, featuring a brand-new sector-by-sector Compare module, detection of used-drive fraud on Seagate devices, enhanced Web API automation, and 30+ improvements across forensic imaging workflows....read more
Forensic Focus Digest, 16 Oct 2026

Forensic Focus Digest, 16 Oct 2026

Discover what’s new on Forensic Focus: explore how the City of Johannesburg uses Detego Global to accelerate investigations, see how MD-LIVE takes investigators from first connection to a court-ready report, learn how iVe analyzes vehicle data to reveal driver behavior, and more....read more
The Forensic Focus State Of DFIR Survey Is Now Open

The Forensic Focus State Of DFIR Survey Is Now Open

Caseloads, AI, tools, hiring and careers: tell us what DFIR work looks like today. About 8 minutes, anonymous, with early access to the report...read more
Review: MacQuisition From BlackBag

by Jade James MacQuisition is an effective 3-in-1 tool which provides the facility to acquire data live from a running system, as well as offering targeted data collection and forensic imaging. MacQuisition runs on Mac OS X and safely boots

MacQuisition From BlackBag

by Jade James MacQuisition is an effective 3-in-1 tool which provides the facility to acquire data live from a running system, as well as offering targeted data collection and forensic imaging. MacQuisition runs on Mac OS X and safely boots

Joe Walsh On Private Browsing Data And Teaching Digital Forensics Online

Christa: Hello and welcome to the Forensic Focus podcast. Monthly we interview experts from the digital forensics and incident response community on a host of topics ranging from technical aspects to career soft skills. I’m your host, Christa Miller. Today

Webinar: New Triage Capabilities In BlackLight

Quickly triage systems with new BlackLight features in this upcoming webinar with BlackBag Technologies and Passware, Inc.Register for BlackBag and Passware’s upcoming webinar to learn how the latest improvements to BlackLight allow examiners to more quickly triage systems. In this

How To Save Time With XAMN’s Dynamic Artifact Count Feature

At MSAB, we’re always looking to improve our software and make every product more user-friendly, intuitive, and valuable; and to help save you time. We’ve recently improved the way that XAMN displays and counts artifacts. Let’s take a look at

How To Integrate LACE Carver With Griffeye Analyze DI Pro

Let’s talk about the exciting new LACE Carver integration with Analyze DI Pro. Once you have the proper license, you can head over to your Downloads page on MyGriffeye.com and go to the LACE Carver download. Once the app package

How To Use AXIOM In Malware Investigations: Part II

Hey everyone, Tara Nelson here with Magnet Forensics. Today I’m going to give a little insight into how AXIOM can help with some of your day-to-day investigations. In this video we’re going to talk a little bit about malware investigations.

How To Use AXIOM In Malware Investigations: Part II

Hey everyone, Tara Nelson here with Magnet Forensics. Today I’m going to give a little insight into how AXIOM can help with some of your day-to-day investigations. In this video we’re going to talk a little bit about malware investigations.

How To Boot Scan A Microsoft Surface Pro

Hi, I’m Rich Frawley, and I’m the Digital Forensic Specialist with ADF Solutions. Today we’re going to conduct a boot scan of a Microsoft Surface Pro with BitLocker activated.At this point you have decided on a search profile, or search

How To Boot Scan A Microsoft Surface Pro

Hi, I’m Rich Frawley, and I’m the Digital Forensic Specialist with ADF Solutions. Today we’re going to conduct a boot scan of a Microsoft Surface Pro with BitLocker activated. At this point you have decided on a search profile, or

What Changes Do We Need To See In eDiscovery? Part VI

by Harold Burt-Gerrans Several years ago, we hosted what I believe was the first true single-language review of multi-lingual documents. At that time, Google search could only find one eDiscovery or processing software vendor that included bulk/mass machine language translation

What Changes Do We Need To See In eDiscovery? Part VI

by Harold Burt-Gerrans Welcome to Part 6, the last in this series. In case you’re joining late, the previous parts are available as follows: Standards Standards and De-Duplication Levels New Approach to Managing Duplicative Documents Family Level Coding Recursive De-Duplication