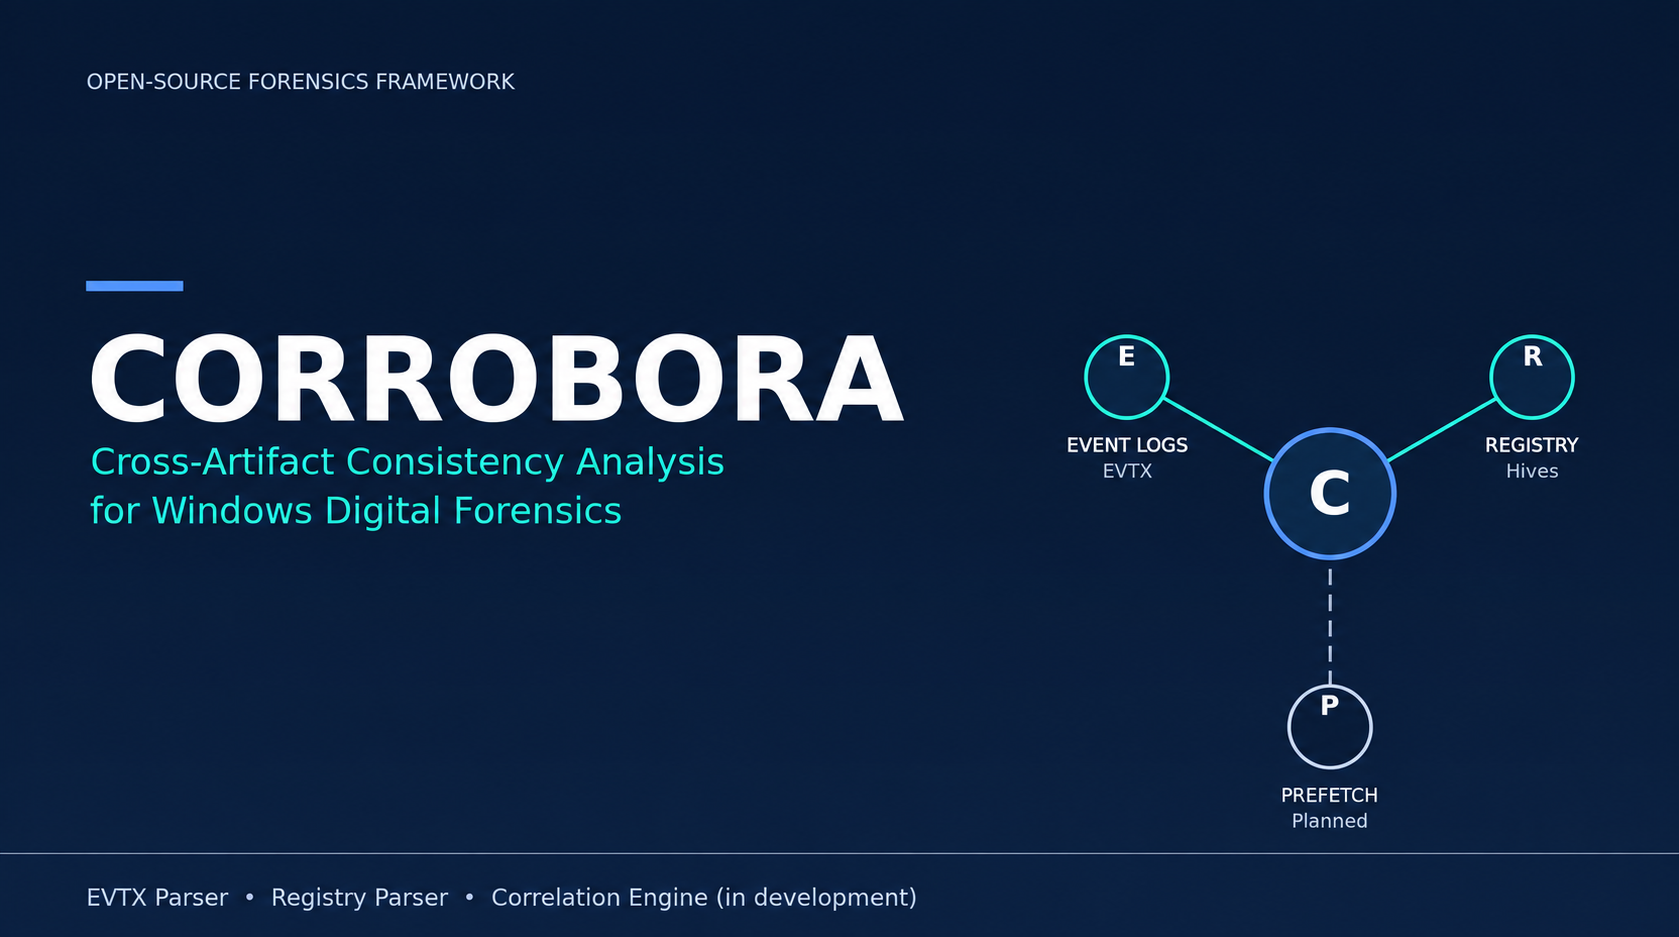
Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldnโ€™t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
Radim Motycka, Founder, Proofsnap

Radim Motycka, Founder, Proofsnap

Why screenshots alone may not be enough: ProofSnap founder Radim Motycka explains how hashes, timestamps, WARC, network artefacts and independent verification can strengthen the preservation of web evidence....read more

Digital Forensics Round-Up, June 29 2023

A round-up of this weekโ€™s digital forensics news and views: โ€˜The audio gets to youโ€™: What it takes for Singapore police to investigate child sexual abuse material For a few hours every day, Assistant Superintendent of Police (ASP) Jane Chen

Types Of Devices Examined In Digital Forensics Investigations

Today, digital forensic investigators must be adept at extracting evidence from an array of devices, each with unique structures, operating systems, storage capabilities, and security features. A case involving a desktop computer, for example, may require an understanding of operating

Mitre Att&ck Scanning And Mapping Added To DRONE

The DFIR Lab team at Binalyze have their finger on the pulse of the cybersecurity ecosystem to ensure that our DRONE assisted compromise assessment module within AIR always includes the latest IOCs. In addition they are always working on an

Digital Forensics Round-Up, June 22 2023

A round-up of this weekโ€™s digital forensics news and views: UK National Crime Agency Head Calls for Hacking Law Updates A British cyber law that criminalizes hacking and other intrusion activities is outdated, often hindering law enforcement action against cyber

The Power Of Auto Asset Tagging In DFIR

When a breach occurs one of the first questions the investigating team leader will want answered is, โ€˜how many of our assets could this potentially impact or has it already impacted?โ€™ To best answer that question youโ€™ll need to know

Digital Forensics Round-Up, June 08 2023

A round-up of this weekโ€™s digital forensics news and views: Digital Forensics Training Strengthens Ukrainian Investigative Capabilities Last week, EU Advisory Mission (EUAM) Ukraine and the Austrian National Criminal Intelligence Service organized an intensive training in Vienna on digital forensics…

Presentation On Video Evidence Principles At The European Parliament

Images and videos are among the most significant forms of evidence used to solve crimes. However, the challenges that surround video evidence are often overlooked or not fully understood during investigations. To promote greater awareness among practitioners and institutions on

Cellebriteโ€™s Solutions To Current eDiscovery Challenges

Si: Welcome friends and enemies to the Forensic Focus podcast. Today we have Monica with us from Cellebrite, and we are going to have a reasonably wide-ranging discussion, touching on SaaS and workflows and a number of other things. Monica,