Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

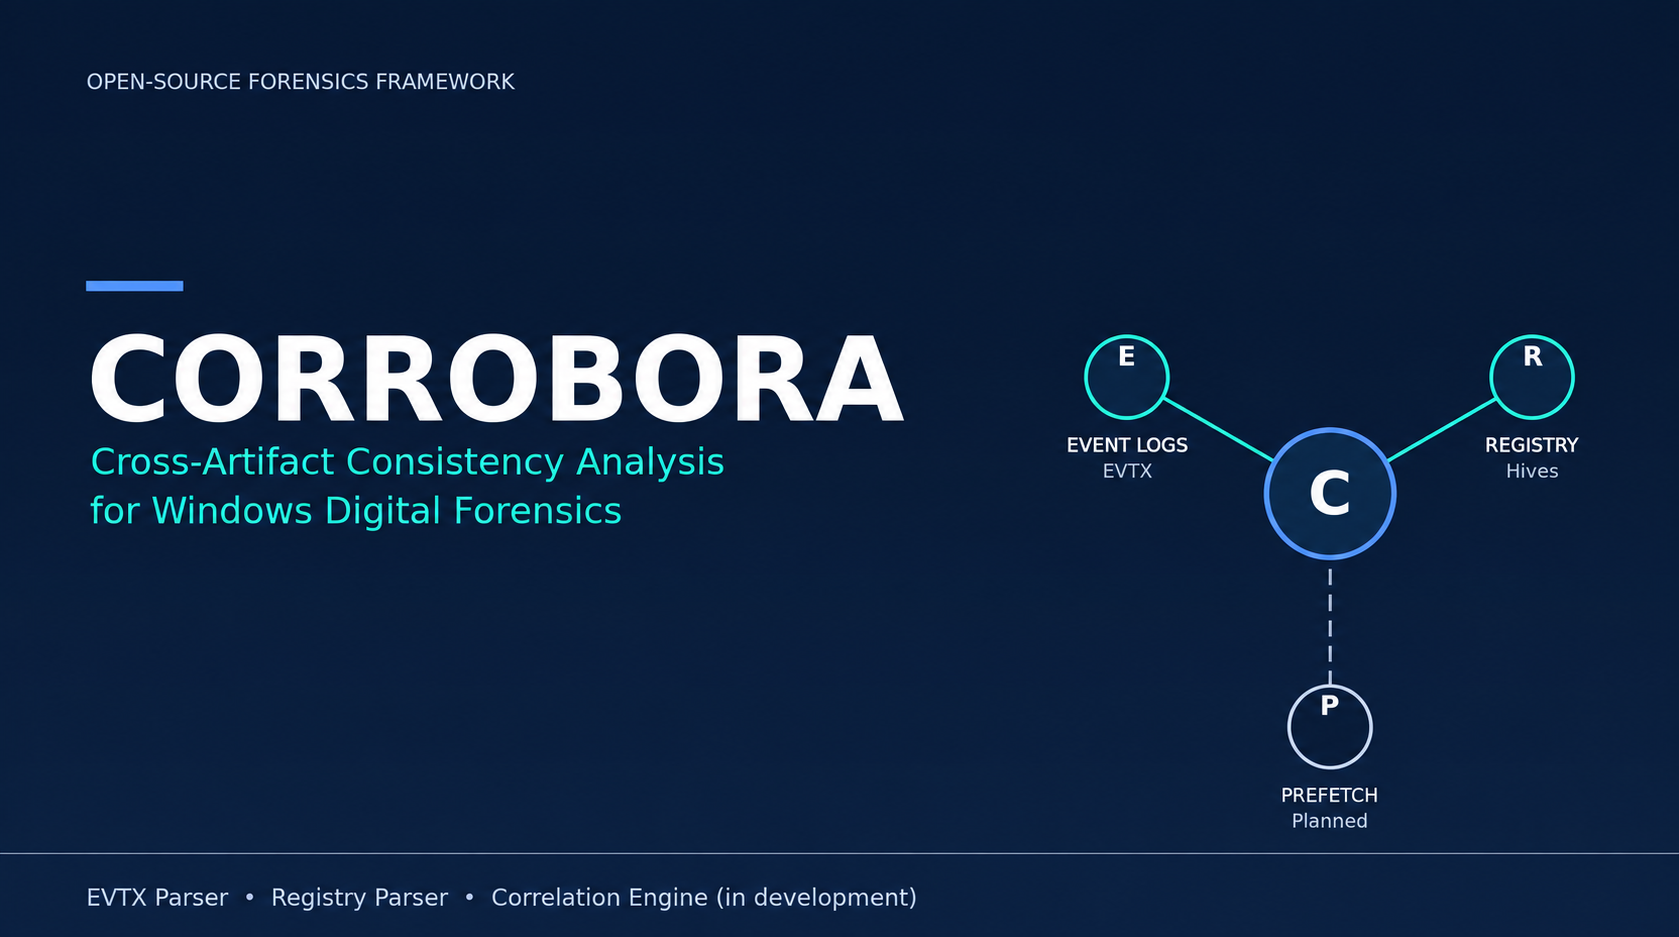
Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
Radim Motycka, Founder, Proofsnap

Radim Motycka, Founder, Proofsnap

Why screenshots alone may not be enough: ProofSnap founder Radim Motycka explains how hashes, timestamps, WARC, network artefacts and independent verification can strengthen the preservation of web evidence....read more

A Survey on the State of Video Forensics In 2022

Amped Software launches a new survey to understand what are the trends with video evidence and what is the state of video forensics in 2022. The survey is open to anyone working on image and video evidence (even occasionally) and

Deep dive into ‘METADATA’

Deep dive into ‘METADATA’ Hancom is glad to release a new whitepaper of ‘Metadata’, and hope this can help you to improve your forensic investigation skills. This whitepaper focuses on the research of Metadata. We will use MD-RED and analyze

Distant Traces and Their Use in Crime Scene Investigation

Starting with a physical crime scene – a fire – Manon Fischer describes how IoT devices such as “smart” plugs and thermostats store “distant traces” remotely, and could be used to help reconstruct a fire’s origin, cause, and timeline. Session

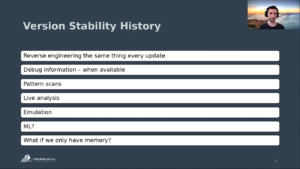
The Wisdom of the Heap: Mesh It up by Weaving Data Structures

In this short presentation, Trufflepig Forensics’ Aaron Hartel and Christian Müller present some early stage research about the volatility of data in memory as data structures change version to version. Session Chair: We’re now going over to memory forensics and

Oxygen Forensics Introduces User-Focused Advancements In Latest Release

Oxygen Forensics has released the latest version of the all-in-one digital forensic solution, Oxygen Forensic® Detective v.14.6. This version adds support for multiple new backups, continues to improve the iOS Agent extractor, and introduces a new analytic feature. Brute-force for

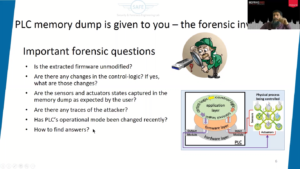
Toward Graph-Based Network Traffic Analysis and Incident Investigation

At DFRWS-EU 2022, Milan Cermak describes the need to create data associations for use during network traffic analysis and incident investigation. The focus is on robust graph data visualization of the kind that’s commonly used in criminal investigation, allowing analysts

2022 2Q MD-Series Release Note Highlights

Find out the major features in MD-Series that are supported in 2Q 2022.  MD-NEXT v1.91.4–v1.91.9 Supports new 2,428 models, updated 783 Models. Android Full filesystem extraction method added Samsung Galaxy S22 Qualcomm Series. Supports iOS Checkm8 Full Filesystem (iOS 15.0∼15.2.1

Get Ready for the Next Big Reveal From Grayshift

Grayshift continues to extend its strength in lawful access and extraction capabilities As a leader in cell phone forensics, Grayshift, has been hard at work developing new features for law enforcement partners like you. We strive to provide law enforcement