Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

How Semantics 21 Is Changing The Way Investigators Work With Digital Evidence

Hero Image

Digital evidence has evolved, but have your investigative workflows kept pace? Discover how Semantics 21 is helping investigators reduce manual effort, prioritise critical evidence and work smarter with modern forensic intelligence tools....
Today's headlines 21 Oct 2026

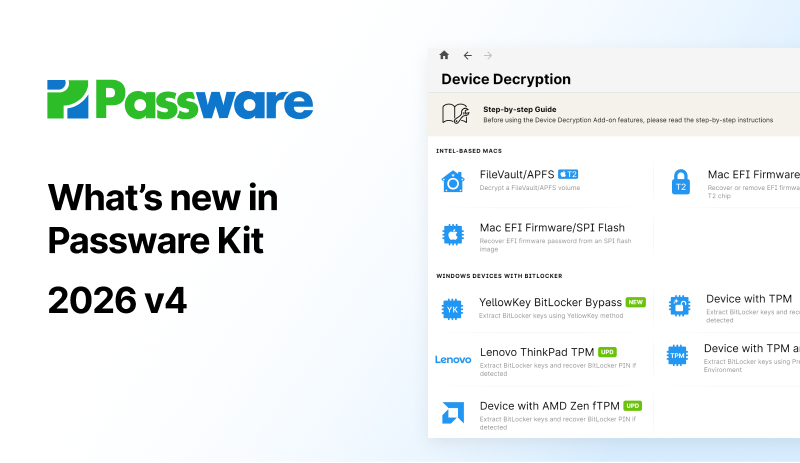
Passware Kit 2026 v4 Simplifies BitLocker Decryption And Adds E01 Export

Passware Kit 2026 v4 Simplifies BitLocker Decryption And Adds E01 Export

Passware Kit 2026 v4 is here with expanded BitLocker decryption support for AMD and Lenovo devices, the new YellowKey method, Linux eCryptfs decryption, E01 export, and enhanced Apple support....read more
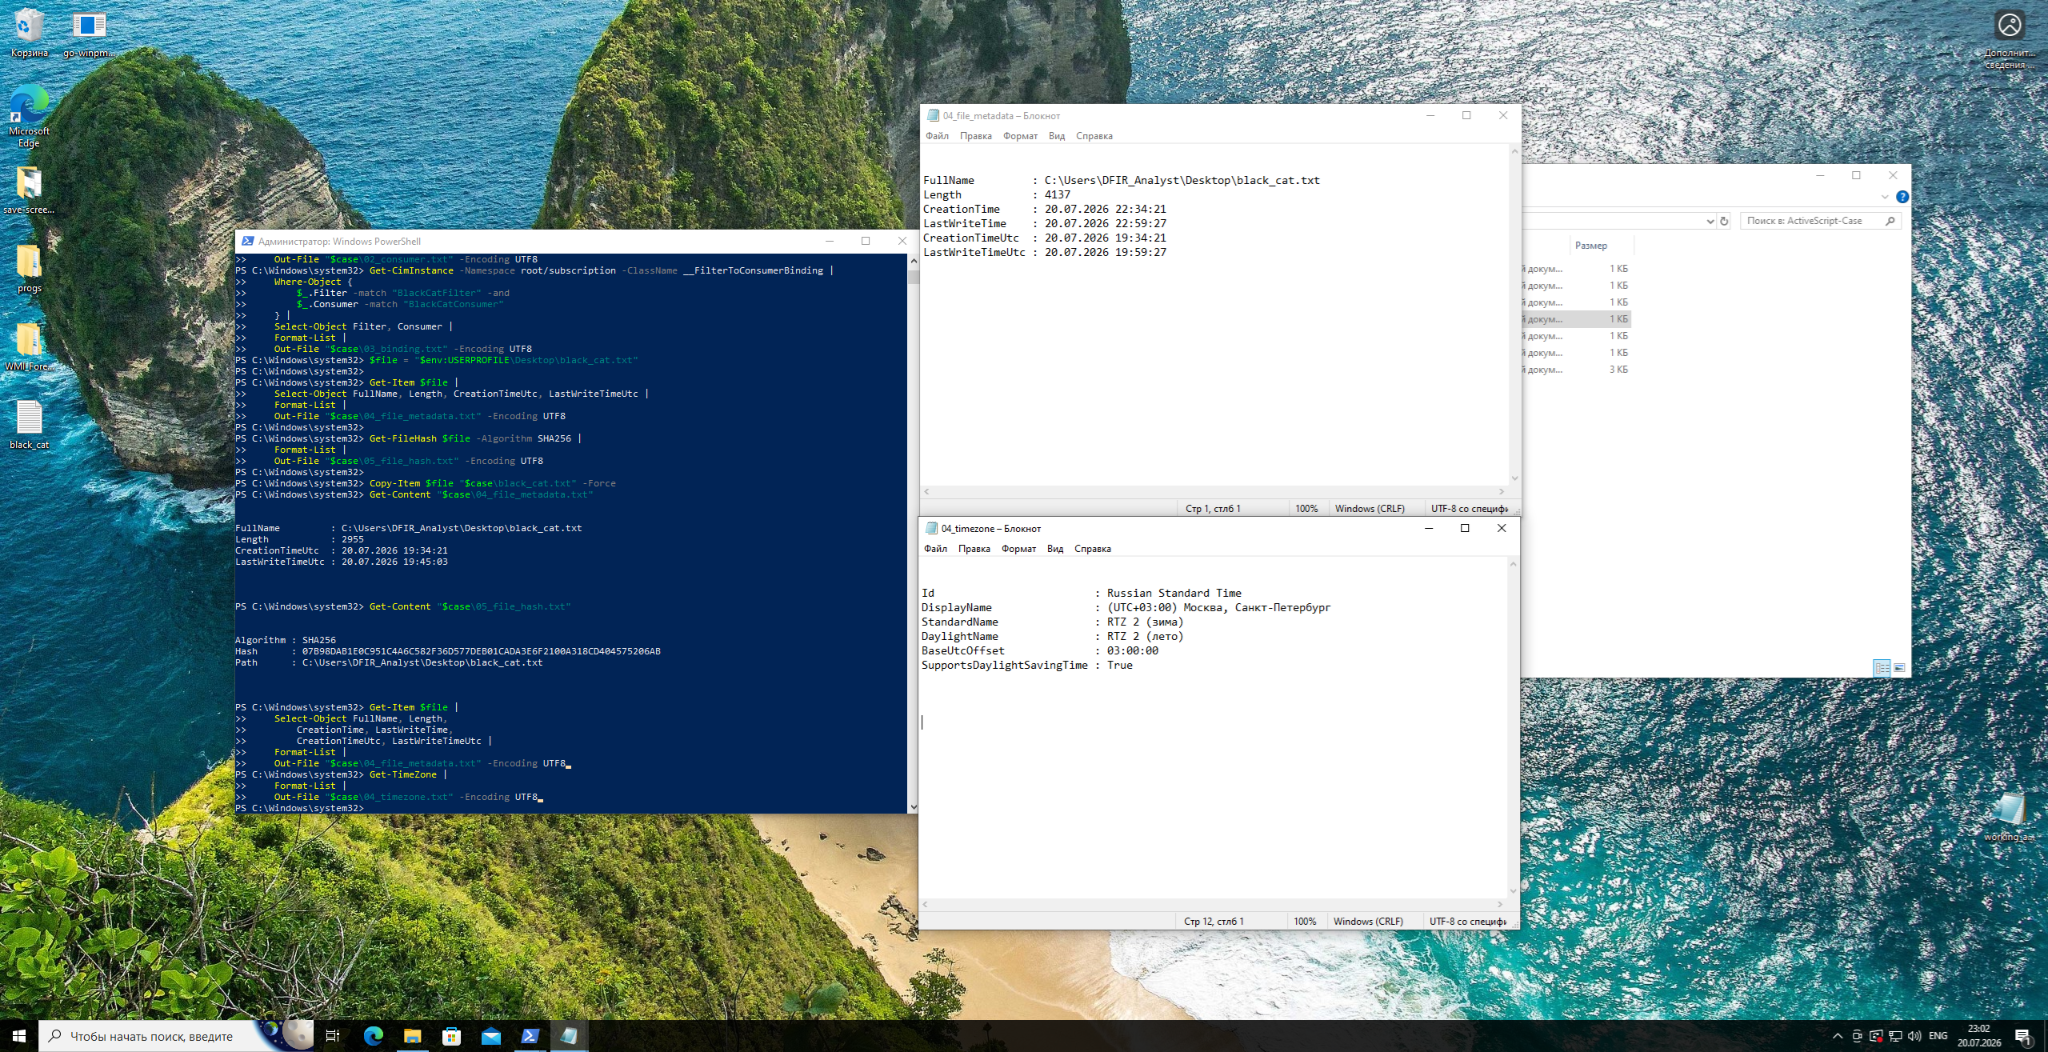
Investigating WMI Permanent Event Subscription Persistence

Investigating WMI Permanent Event Subscription Persistence

Vitalii offers a hands-on DFIR deep dive into WMI ActiveScriptEventConsumer persistence, from registration and execution to memory artifacts, Sigma detection, and cleanup....read more
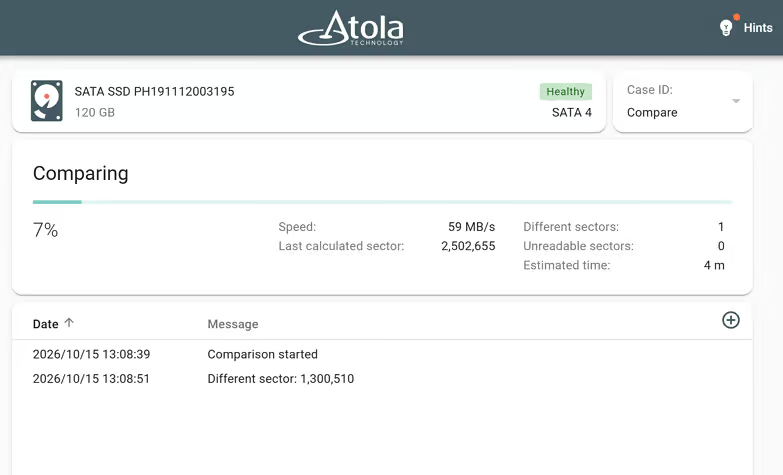
Atola TaskForce Gets A Massive Update Including A New Compare Module

Atola TaskForce Gets A Massive Update Including A New Compare Module

Meet Atola TaskForce firmware 2026.10, featuring a brand-new sector-by-sector Compare module, detection of used-drive fraud on Seagate devices, enhanced Web API automation, and 30+ improvements across forensic imaging workflows....read more
GID – A Big Step For Intelligence Sharing And Collaboration

Collaboration has always been a cornerstone of everything we do at Griffeye. We simply believe that humans are better when working together. That is why the Analyze platform is built to interconnect and reach out to other forensic tools, platforms

How To Analyze Windows 10 Timeline With Belkasoft Evidence Center

Temporal analysis of events (Timeline) can be beneficial when you want to reconstruct events related to computer incidents, data breaches, or virus attacks taking place on a victim’s computer. Historically, digital forensic timeline analysis has been broken down into two

How To Analyze Windows 10 Timeline With Belkasoft Evidence Center

Temporal analysis of events (Timeline) can be beneficial when you want to reconstruct events related to computer incidents, data breaches, or virus attacks taking place on a victim’s computer.  Historically, digital forensic timeline analysis has been broken down into two

What’s Happening In Forensics – Jul 8, 2019

Amped will be holding a User Day in Denver, CO, on October 6th – register to attend here. DME Forensics have released DVR Examiner 2.7, feauturing a new way to visually review clips. Brett Shavers announces some upcoming additions to

Belkasoft Evidence Center 9.6 — Fresh Update With Brand New Features

A fresh version of Belkasoft‘s flagship digital forensics product Belkasoft Evidence Center has recently been released. The 9.6 version combines an affordable price with a range of timely updates based on the most important industry developments. More details on what’s

Industry Roundup: Image Recognition And Categorization

by Christa Miller, Forensic Focus The need for image recognition and categorization has never been more in demand thanks to the spread of extremist propaganda, child sexual abuse material (CSAM), and other illicit activity across the internet. Because of the

Amped Software Partners With The University Of Colorado Denver

Education is important for raising the value of video and image forensics. The more practitioners understand the correct way to process and clarify the evidence they receive, the better the probative value that evidence becomes. One group who has been

What’s Happening In Forensics 5th Jul 2019

DFRWS US 2019 is nearly upon us! There’s still time to register to join in Portland, OR from the 14th-17th July. The call for speakers for Enfuse 2019 in November is now live. Eurofins Scientific, a forensic services firm that

Fighting Crime With Data: Law Enforcement In The 21st Century

by Paul Hamrick, Nuix Law enforcement investigations have long been influenced by developments in technology; after all, new technologies create new ways for criminals to profit and new sources of evidence. Law enforcement needs to keep up with the times,

Fighting Crime With Data: Law Enforcement In The 21st Century

by Paul Hamrick, Nuix Executive Summary Law enforcement investigations have long been influenced by developments in technology; after all, new technologies create new ways for criminals to profit and new sources of evidence. Law enforcement needs to keep up with

What’s Happening In Forensics 4th Jul 2019

Andrea Fortuna shows how to convert a Windows SFS (Dynamic Disks) partition to regular partition for forensic analysis. Harlan Carvey shares a review of his book Investigating Windows Systems. Xavier Mertens rounds up news from Pass-The-Salt 2019. Kristian Lars Larsen

Webinar: Mobile Device Investigator For Android & iOS

A new webinar, Mobile Device Investigator For Android & iOS, is available to view here. Join the forum discussion here.View the webinar on YouTube here.Read a full transcript of the webinar here. Read More

Mobile Device Investigator For Android & iOS

Join the forum discussion here.View the webinar on YouTube here.Read a full transcript of the webinar here.Rich: Good day, everyone. Thank you for taking the time out of your day to hear about Mobile Device Investigator. I’ll be conducting a

What’s Happening In Forensics 3rd Jul 2019

Atola Insight Forensic 4.13 has been released, with NVMe support. Andrew Case talks about building the next generation of memory forensics practitioners. Didier Stevens reminds himself (and us) how to set a nslookup type via the command-line. Salt4n6 talks about