Take the State of DFIR Survey

Caseloads, AI, tools and careers. 8 minutes, anonymous, early access to the report.

Take the survey →

How Semantics 21 Is Changing The Way Investigators Work With Digital Evidence

Hero Image

Digital evidence has evolved, but have your investigative workflows kept pace? Discover how Semantics 21 is helping investigators reduce manual effort, prioritise critical evidence and work smarter with modern forensic intelligence tools....
Today's headlines 21 Oct 2026

Passware Kit 2026 v4 Simplifies BitLocker Decryption And Adds E01 Export

Passware Kit 2026 v4 Simplifies BitLocker Decryption And Adds E01 Export

Passware Kit 2026 v4 is here with expanded BitLocker decryption support for AMD and Lenovo devices, the new YellowKey method, Linux eCryptfs decryption, E01 export, and enhanced Apple support....read more
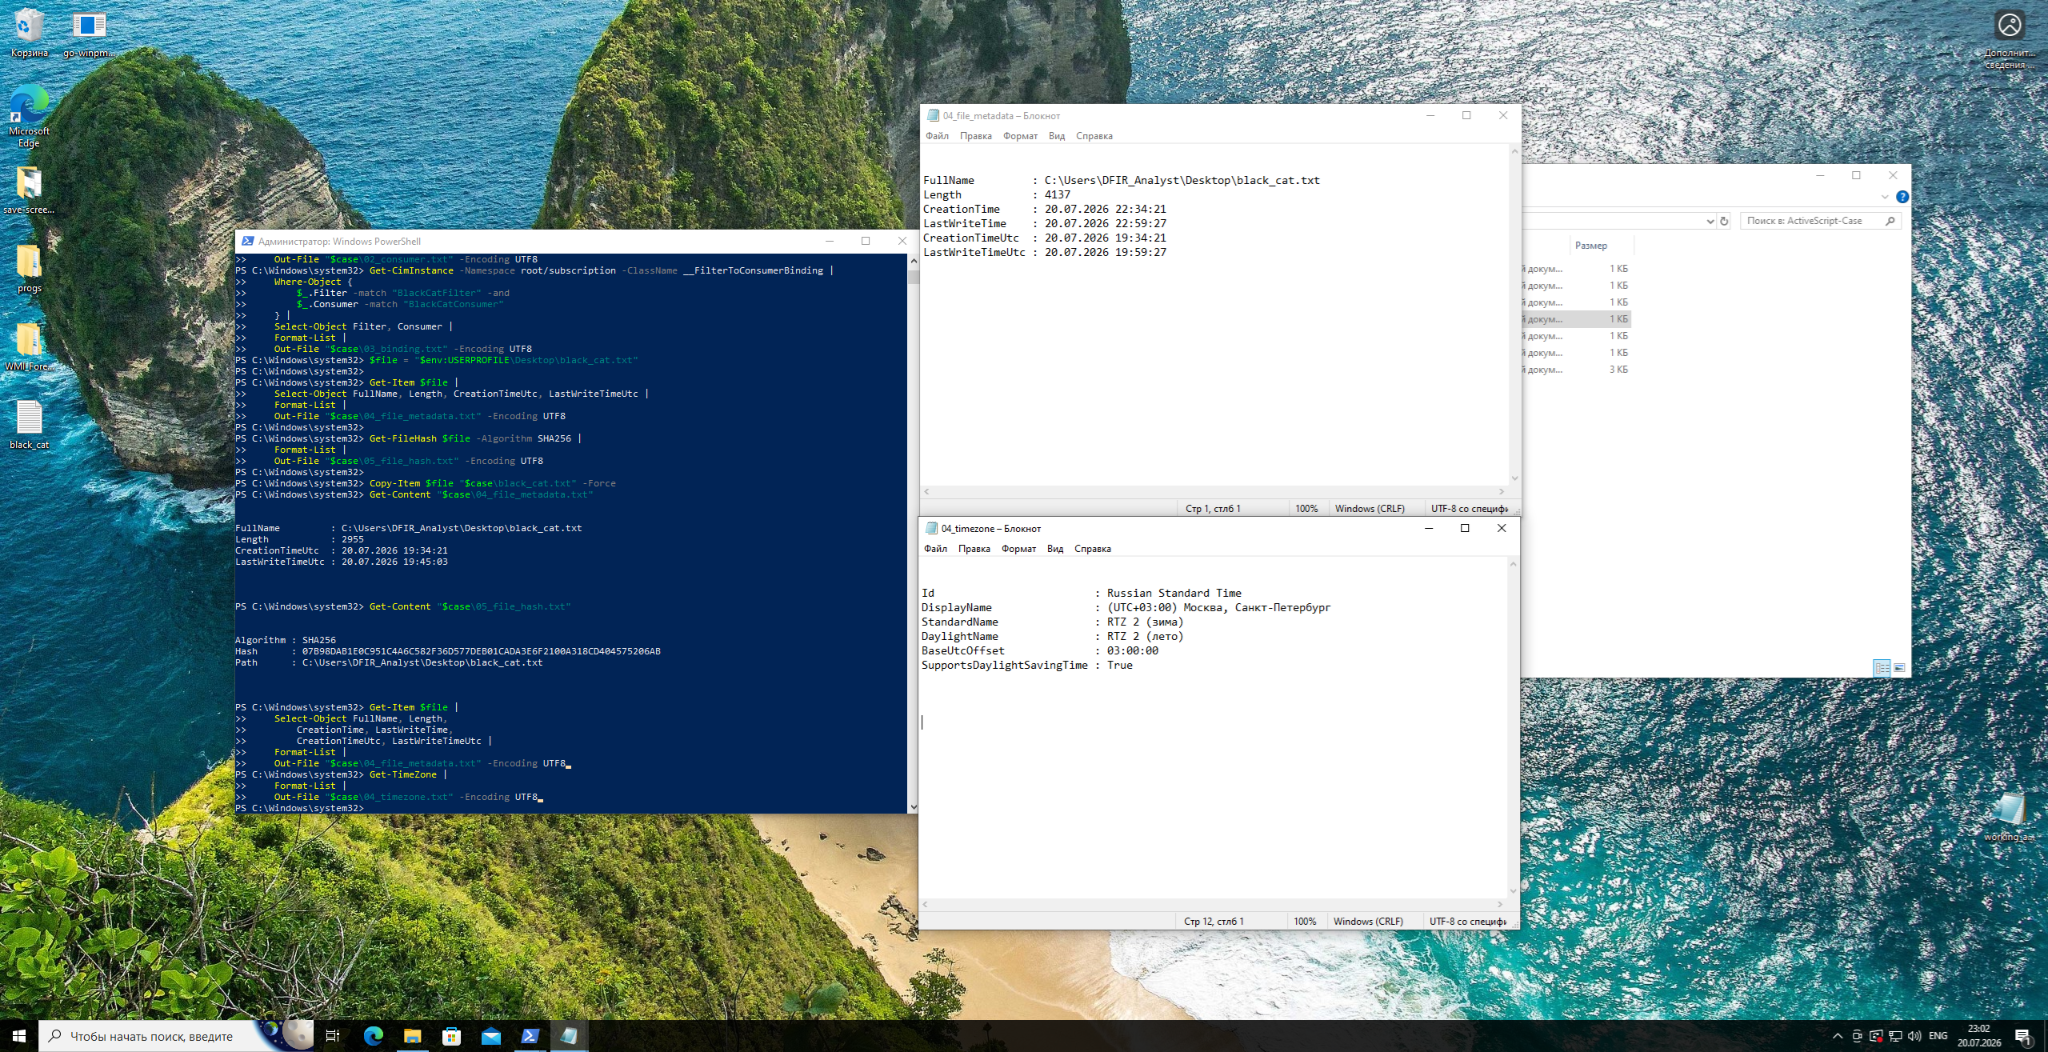
Investigating WMI Permanent Event Subscription Persistence

Investigating WMI Permanent Event Subscription Persistence

Vitalii offers a hands-on DFIR deep dive into WMI ActiveScriptEventConsumer persistence, from registration and execution to memory artifacts, Sigma detection, and cleanup....read more
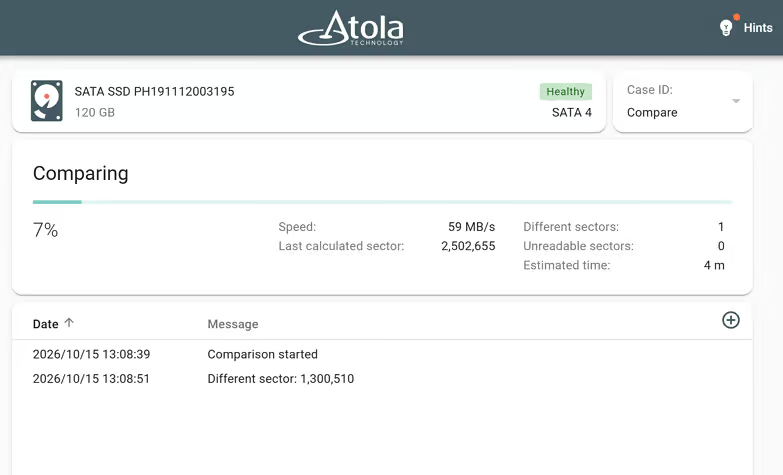
Atola TaskForce Gets A Massive Update Including A New Compare Module

Atola TaskForce Gets A Massive Update Including A New Compare Module

Meet Atola TaskForce firmware 2026.10, featuring a brand-new sector-by-sector Compare module, detection of used-drive fraud on Seagate devices, enhanced Web API automation, and 30+ improvements across forensic imaging workflows....read more
Unreal Steganography: Using A VR Application As A Steganography Carrier

by Stuart Wilson This report focuses on the use of virtual reality as a potential steganography carrier file to avoid detection of forensic analysis applications commonly used within law enforcement. The goal is to show how a virtual reality game/environment

What’s Happening In Forensics Jul 12, 2019

Matt talks about how to derive intelligence from LNK files. Oleg Skulkin demonstrates how to use MITRE ATT&CK for forensics. DFRWS US 2019 has begun – follow their Twitter feed for updates.

MD5 Are Excited To Announce The Launch Of VFC5 On The 15th July 2019

MD5 Ltd first launched VFC to the forensic community in 2007. As well as being the original virtualisation solution for the forensic investigator, over the last 12 years, VFC has saved crucial time and provided crucial intelligence & evidence for

Finding And Interpreting Windows Firewall Rules

by Joakim Kävrestad Determining with whom and in what way a computer has communicated can be important and interesting in several types of examinations. Communications can be an important part of analyzing if and how a computer has been remote

Finding And Interpreting Windows Firewall Rules

by Joakim Kävrestad Determining with whom and in what way a computer has communicated can be important and interesting in several types of examinations. Communications can be an important part of analyzing if and how a computer has been remote

What’s Happening In Forensics – Jul 12, 2019

The UK home secretary has announced a new technology to help combat the distribution of child abuse content online. Bryan Ambrose demonstrates how to extract pcap from a memory image. The Cybercrime Centre at the University of Cambridge is looking

BlackBag Technologies Announces New Windows® Forensic Investigations Course

BlackBag reaffirms its commitment to Windows forensics with a specialized Windows investigative course.BlackBag offers digital forensic training to meet the needs of law enforcement, military and private sector examiners. BlackBag’s courses are designed to address realistic scenarios, simulating the daily

What’s Happening In Forensics – Jul 11, 2019

Atola announce TaskForce 2019.7. F-Response V8 has been released, with improved Dropbox collection. Amped talk about why it’s important to get the order right when you’re filtering.

What’s Happening In Forensics – Jul 10, 2019

John Patzakis talks about key evidence in social media statements and what might count as an exception to the hearsay rule. The Nuix User Exchange will be taking place in September – register here. Amped have updated DVRConv. What app

6 Month Checkup At Oxygen Forensics

Hard to believe that half the year is already up! Not only has our company been growing month after month but so has our software! Let’s take a look at the fantastic innovations brought to you in Oxygen Forensic® Detective

Review: Mobile Device Investigator From ADF

by Jade James ADF Solutions is a leading provider of intelligent digital forensic and media exploitation software. ADF’s tools are used for the processing and analysis of computers, external drives, mobile devices and other media storage such as USBs and

Mobile Device Investigator From ADF

Reviewed by Jade James ADF Solutions is a leading provider of intelligent digital forensic and media exploitation software. ADF’s tools are used for the processing and analysis of computers, external drives, mobile devices and other media storage such as USBs

What’s Happening In Forensics – Jul 9, 2019

OpenText demonstrate how to identify private browsing and wearable data activity with Encase. Kali Linux has been made available for the Raspberry Pi 4. ElcomSoft discuss the art of iPhone acquisition. Oxygen Forensics round up what they’ve done so far