Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

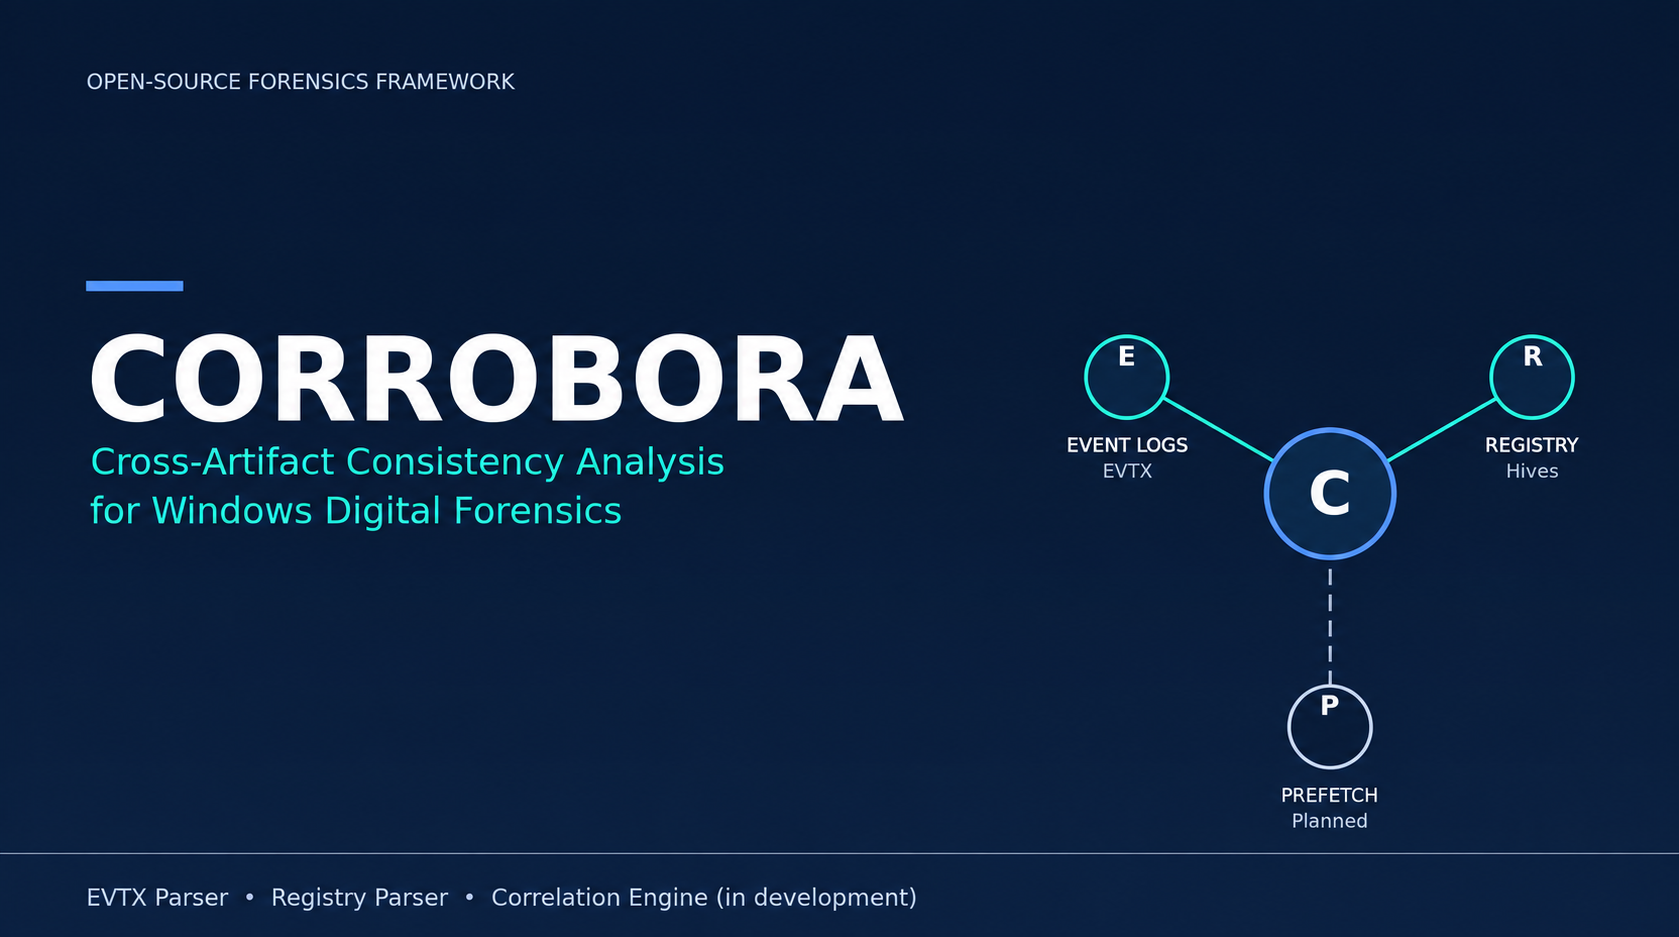
Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
Radim Motycka, Founder, Proofsnap

Radim Motycka, Founder, Proofsnap

Why screenshots alone may not be enough: ProofSnap founder Radim Motycka explains how hashes, timestamps, WARC, network artefacts and independent verification can strengthen the preservation of web evidence....read more

MSAB’s Simon Crawley on the Importance of Frontline Forensics

Christa: Time is of the essence when field extractions of mobile devices are needed, but so are forensically sound extractions as strong links along the chain of custody. Today the Forensic Focus podcast welcomes Simon Crawley, a senior consultant with

Forging Trust in Digital Forensics as Technology Evolves

A person holding a tablet with brightly lit icons representing law, trust, compliance
February’s publications continued a trending topic in recent research: establishing reliability in forensic science as a whole, and digital forensics particularly. Even as some works explored the decryption of encrypted data, and the use of “hacked” data from encrypted devices,

Leveraging Intel DCI for Memory Forensics

A small circuit board is connected to a larger circuit board via cabling
Hello, and welcome to my DFRWS US 2021 talk about leveraging Intel DCI for memory forensics. My name is Tobias Latzo and I’m in the security research group of the Friedrich-Alexander University Erlangen-Nürnberg in Germany, which is led by Felix

Finding Important Artifacts in Recycle Bin

A green recycle logo with white circuit board lines depicting data recycling
Recycle Bin can become an important clue to the case. It might provide the trace of a trial to hide or to conceal a clue. This whitepaper focuses on the research of deleted files from various types of apps in

Malware Family Classification Via Efficient Huffman Features

Hello everyone. My name is Steven O’Shaughnessy, and I’m a lecturer from the Technological University in Dublin. And on behalf of my colleague, Frank Breitinger from the University of Lausanne and myself, I am presenting our paper entitled malware family

AI-Based Video Recognition in FTK

Holli: Actually, it looks like everybody’s in here, so we can go ahead and get started. Hi everyone, my name is Holli Hagene. Welcome to today’s webcast. A few reminders: all of the lines have been muted to reduce background

Techno Security Returns to Myrtle Beach – One Month Early

The Marriott Resort at Grande Dunes in Myrtle Beach, South Carolina, USA will host the 23rd edition of the Techno Security & Digital Forensics Conference flagship event, May 9-12 – nearly one month sooner than its accustomed kickoff the Sunday

Checkm8 Acquisition Method in Oxygen Forensic Detective 14.3

We first added checkm8 acquisition from iOS devices in Oxygen Forensic® Detective v.12.6 in July of 2020. Not surprisingly, many things have changed since then. That being the case, we updated our tool several times over the last few months

Dealing With Multiple Data Sources: A Panel Discussion

The inaugural E-Crimes Symposium: Cutting Edge Topics in Digital Forensics — offered on February 28th by the Henry C. Lee Institute of Forensic Science at the University of New Haven — brought together experts in a range of digital forensics

Computer Forensic Reference Data Sets For Digital Evidence

Rick: Good morning. My name is Rick Ayres, I’m the project lead for the Computer Forensics Tool Testing project at NIST. My talk today is going to provide an overview on updates to our Computer Forensics Reference Data Sets project,

New Challenge of Drone Forensics, MD-DRONE

Empower Your Investigation With Drone Forensic Solution, MD-DRONE. MD–DRONE is a forensic software for extracting and analyzing data from the various data sources of unmanned aerial vehicles (UAV)/Drones from global manufacturers such as DJI, Parrot, and PixHawk. Data can be

Emiliano Polito, Trainer, Amped Software

Emiliano, congratulations on your new role! Your journey to Amped Software has been colorful — what first interested you about multimedia engineering as a career? Hi and thank you! My journey to Amped Software has been an eventful one for