Corrobora – Cross-Artifact Consistency Analysis For Windows Digital Forensics

Hero Image

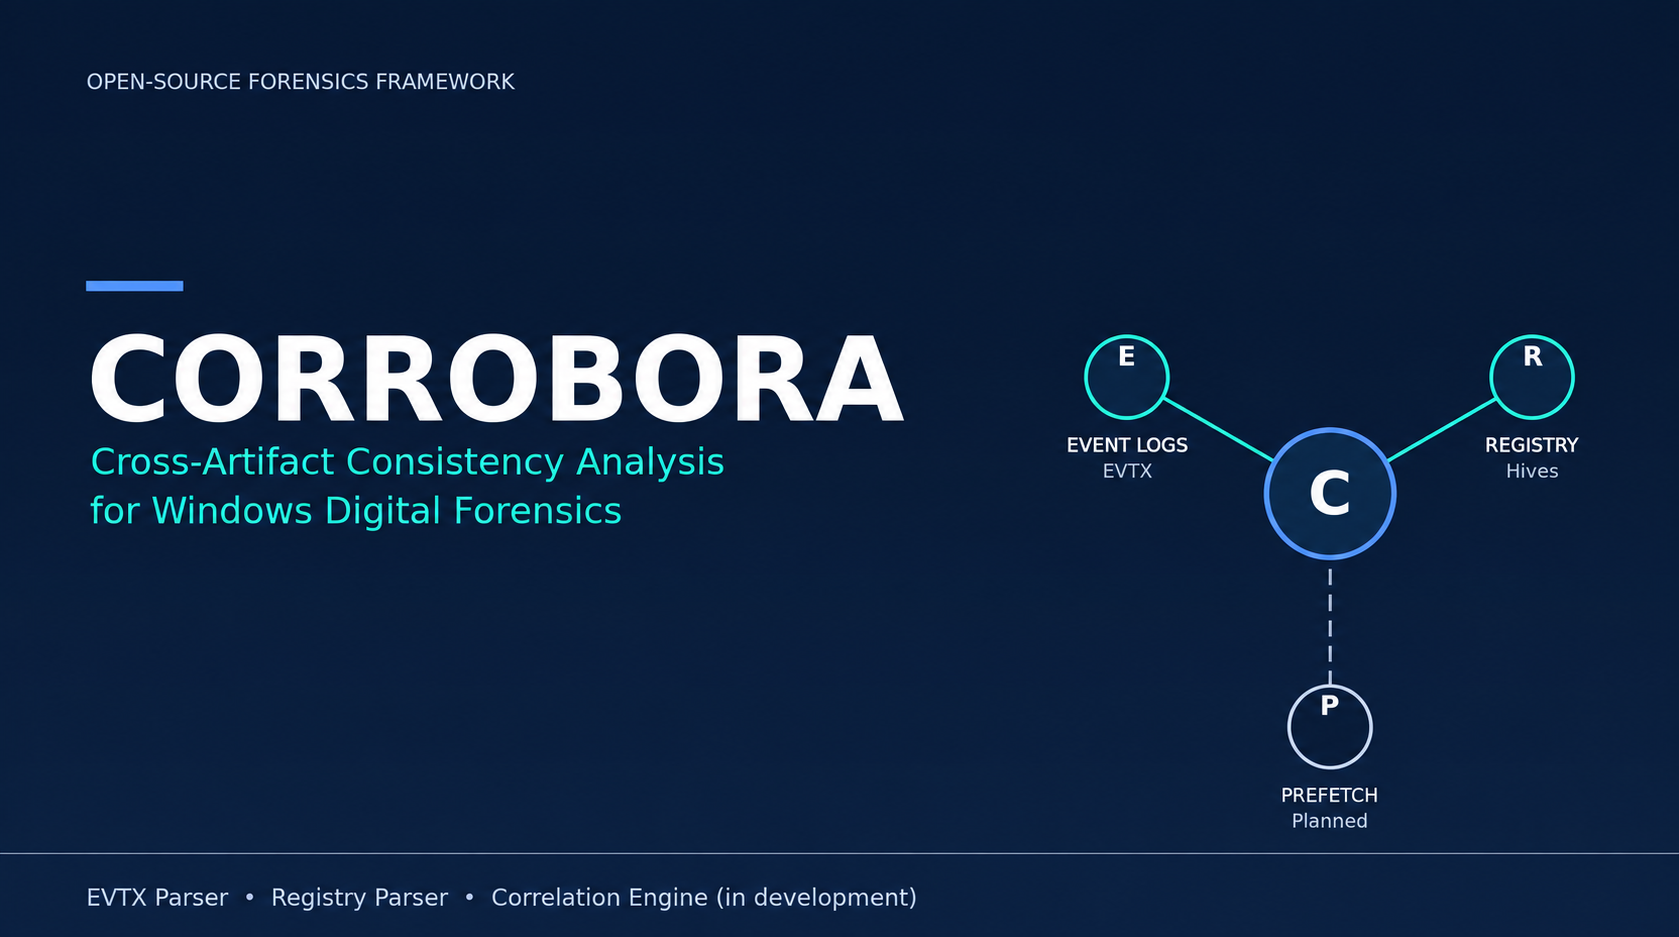
Dielle De Noon explores the development and validation of two key components of her open-source Windows digital forensics framework and how they lay the foundation for future cross-artifact correlation....

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

How Semantics 21 Is Calling Time On Add-On Culture In Digital Forensics

Investigative capability shouldn’t be split across licences, modules and bolt-ons - S21 VisionX brings visual review, prioritisation and victim identification into one intelligence-led platform....read more
Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Magnet Forensics Expands Collaboration With NCMEC To Strengthen Victim Identification

Coming soon to Magnet Griffeye: new capabilities will enable investigators to securely share CSAM-related files, hashes and investigative information directly with NCMEC, helping streamline workflows and support faster child victim identification....read more
Radim Motycka, Founder, Proofsnap

Radim Motycka, Founder, Proofsnap

Why screenshots alone may not be enough: ProofSnap founder Radim Motycka explains how hashes, timestamps, WARC, network artefacts and independent verification can strengthen the preservation of web evidence....read more
Using Network Capture with Binalyze AIR

Steve: Good afternoon, everyone, and welcome to our “Network Capture Using Binalyze AIR” workshop. We have two people on the call today, so we have Emre who I guess you’re all pretty familiar with, who’s the founder and CEO of

Customizing Password Attacks in Oxygen Forensic Detective

Device screen locks and encryption are some of the most significant challenges law enforcement faces in acquiring data for investigations. With Oxygen Forensic® Detective, however, investigators can bypass screen locks to extract and decrypt crucial evidence from Android devices based

XRY Generic Profiles Explained

Hello, my name is Wil Hernandez and I’m a tech sales engineer with MSAB and welcome to XRY in 5. In today’s XRY in 5, we’re going to talk about the generic profiles. How do you get to the generic

The AFF4 Evidence Container: Why and What’s Next

Well, good day. My name is Bradley Schatz, I’m from Evimetry. Today I’m here, it’s my distinct pleasure to be here at the Magnet Virtual Summit to talk about the Advanced Forensic Format Container version four. That’s an evidence container

AIR From Binalyze

Modern forensic data acquisition in enterprise environments requires constant evaluation of approach, methods, tools and tactics. Multiple different ways of acquiring both logical and physical images from remote sources in corporate environments have been developed throughout the years, from deployment

Register For Webinar: Binalyze AIR-DRONE Integration

Binalyze AIR now comes with DRONE integrated for assisted compromise assessment and threat hunting capabilities, all in one place! During this 1 hour webinar, we will make a full demonstration of Binalyze AIR, including the new DRONE integration which makes

New in Binalyze AIR v1.8.0: Multi-organization support

Binalyze AIR v1.8.0 is now available with multi-organization support. One of the most requested features we received from our customers was the ability to manage multiple organizations from a single AIR console. For enterprise customers, this was important to align

Android App Downgrade in Oxygen Forensic Detective

The Android ADB backup is one of the methods that is used to acquire evidence from unlocked Android devices. However, with this approach, investigators cannot extract applications of the latest version because their data is not included in the backup